

CVE-2025-24659
 dottak/cve-2025-24659
PoC of CVE-2025-24659
code-analysisexploitationpenetration-testing+2
dottak/cve-2025-24659PoC of CVE-2025-24659
 zcrosman/cve-2024-32651
changedetection rce though ssti
 randomrobbiebf/cve-2020-12077
MapPress Maps Pro < 2.53.9 - Remote Code Execution (RCE) due to Incorrect Access Control in AJAX Actions
 kailing0220/cve-2022-26134
在受影响的Confluence Server 和Data Center 版本中,存在一个OGNL 注入漏洞,该漏洞允许未经身份验证的攻击者在Confluence Server 或Data Center 服务器上执行任意代码。
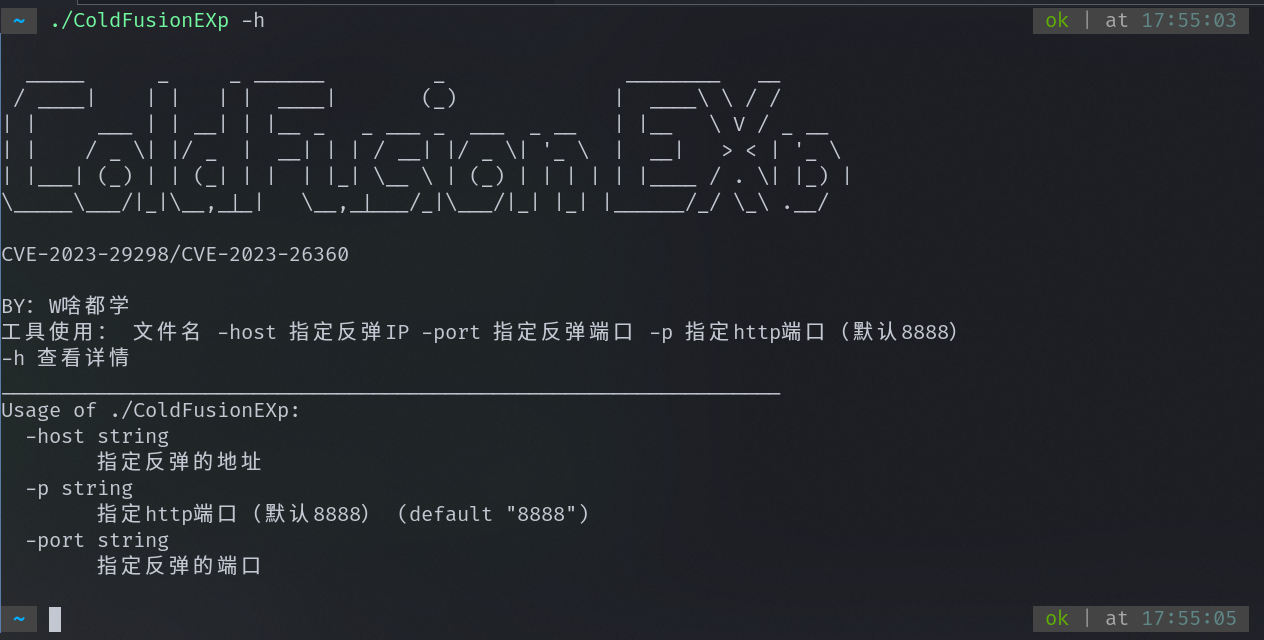 curiouslearnerdev/coldfusion_exp
Adobe ColdFusion CVE-2023-26360/CVE-2023-29298 自动化实现反弹
 ptrstr/cve-2025-4524
CVE-2025-4524 - Unauthenticated madara-core Wordpress theme LFI
 danielhemmati/cve-2016-2098-my-first-exploit
This exploit is remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data
 vulnmachines/zf3_cve-2021-3007
ZendFramework_CVE-2021-3007 PoC
 cymulateresearch/react2shell-scanner
React2Shell Scanner (CVE-2025-55182 & CVE-2025-66478)
 secpool2000/cve-2020-17530
Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts于2020年12月08日披露 S2-061 Struts 远程代码执行漏洞(CVE-2020-17530),在使用某些tag等情况下可能存在OGNL表达式注入漏洞,从而造成远程代码执行,风…
 izxci/cve-2026-9691
CVE-2026-9691: Integration for ActiveCampaign and Contact Form 7, WPForms, Elementor, Ninja Forms <= 1.1.1 Unauthenticated PHP Object Injection PoC,…
 sanupl/cve-2021-46078
CVE-2021-46078 - An Unrestricted File Upload vulnerability exists in Sourcecodester Vehicle Service Management System 1.0. A remote attacker can…
 sanupl/cve-2021-46076
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 izxci/cve-2026-49085
PHP Object Injection exploit for WP Insightly (CVE-2026-49085). Provides proof-of-concept code to demonstrate and test the vulnerability in affected…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
 netvanguard-cmd/cve-2025-59536
PoC exploit for CVE-2025-59536, a high-severity code injection vulnerability in Claude Code's startup trust dialog, enabling remote exploitation of…
 some-1hing/cve-2018-16763
Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.