
CVE-2018-11235-DEMO
 chybeta/cve-2018-11235-demo
Demonstrates exploitation of CVE-2018-11235, a Git submodule RCE vulnerability, with build script and analysis for educational purposes.
code-analysiseducationexploitation+2
14
chybeta/cve-2018-11235-demoDemonstrates exploitation of CVE-2018-11235, a Git submodule RCE vulnerability, with build script and analysis for educational purposes.
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
 gmh5225/cve-2022-35737
Proof-of-concept exploit code and technical analysis for CVE-2022-35737, an integer overflow in SQLite3's sqlite3_str_vappendf function enabling…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
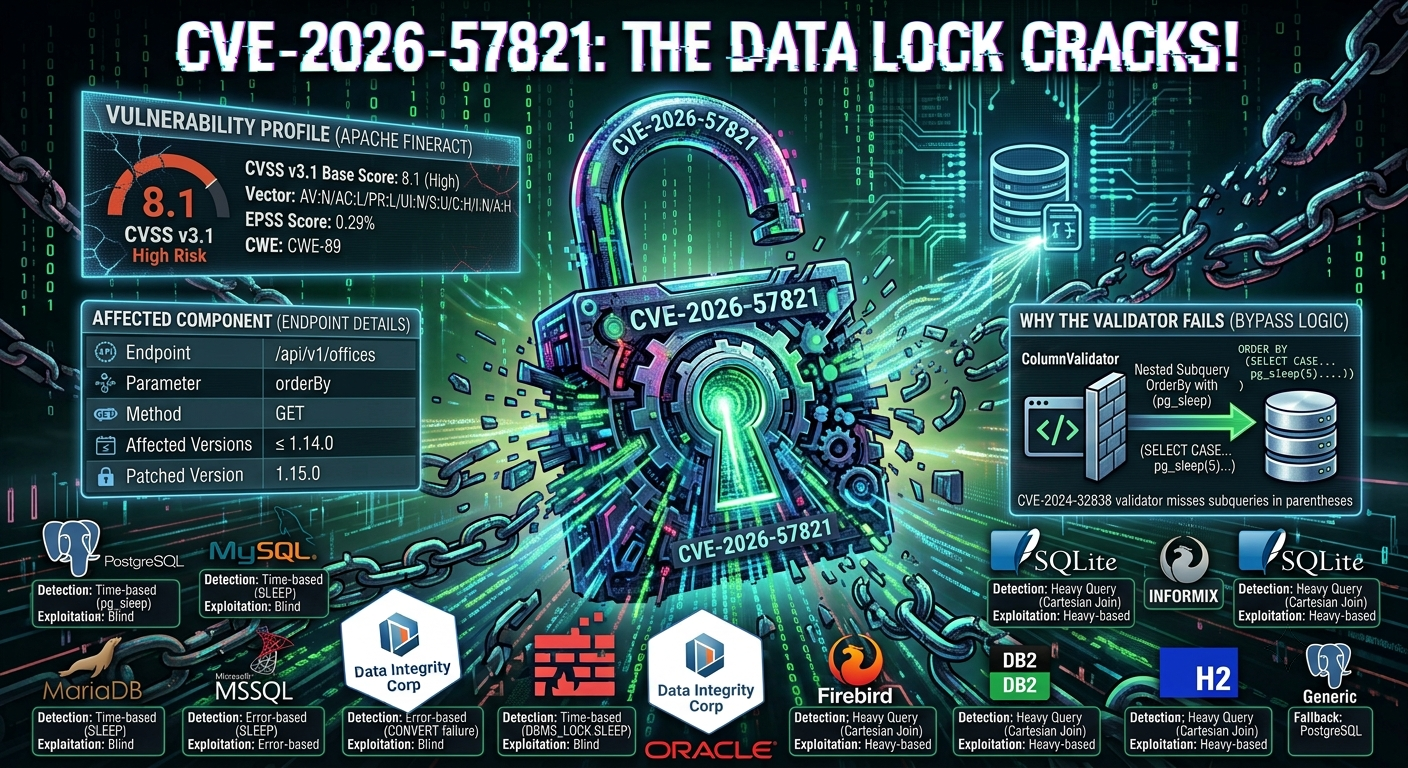 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 elevenpaths/atomshields-cli
CLI for AtomShields static analysis scanner. Install, uninstall, and run checkers and reports to detect vulnerabilities in source code projects.
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496: terminal escape-sequence injection into Boa web server logs — source review, patch analysis and reproducible…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.
 carlosalbertotuma/advisory
Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
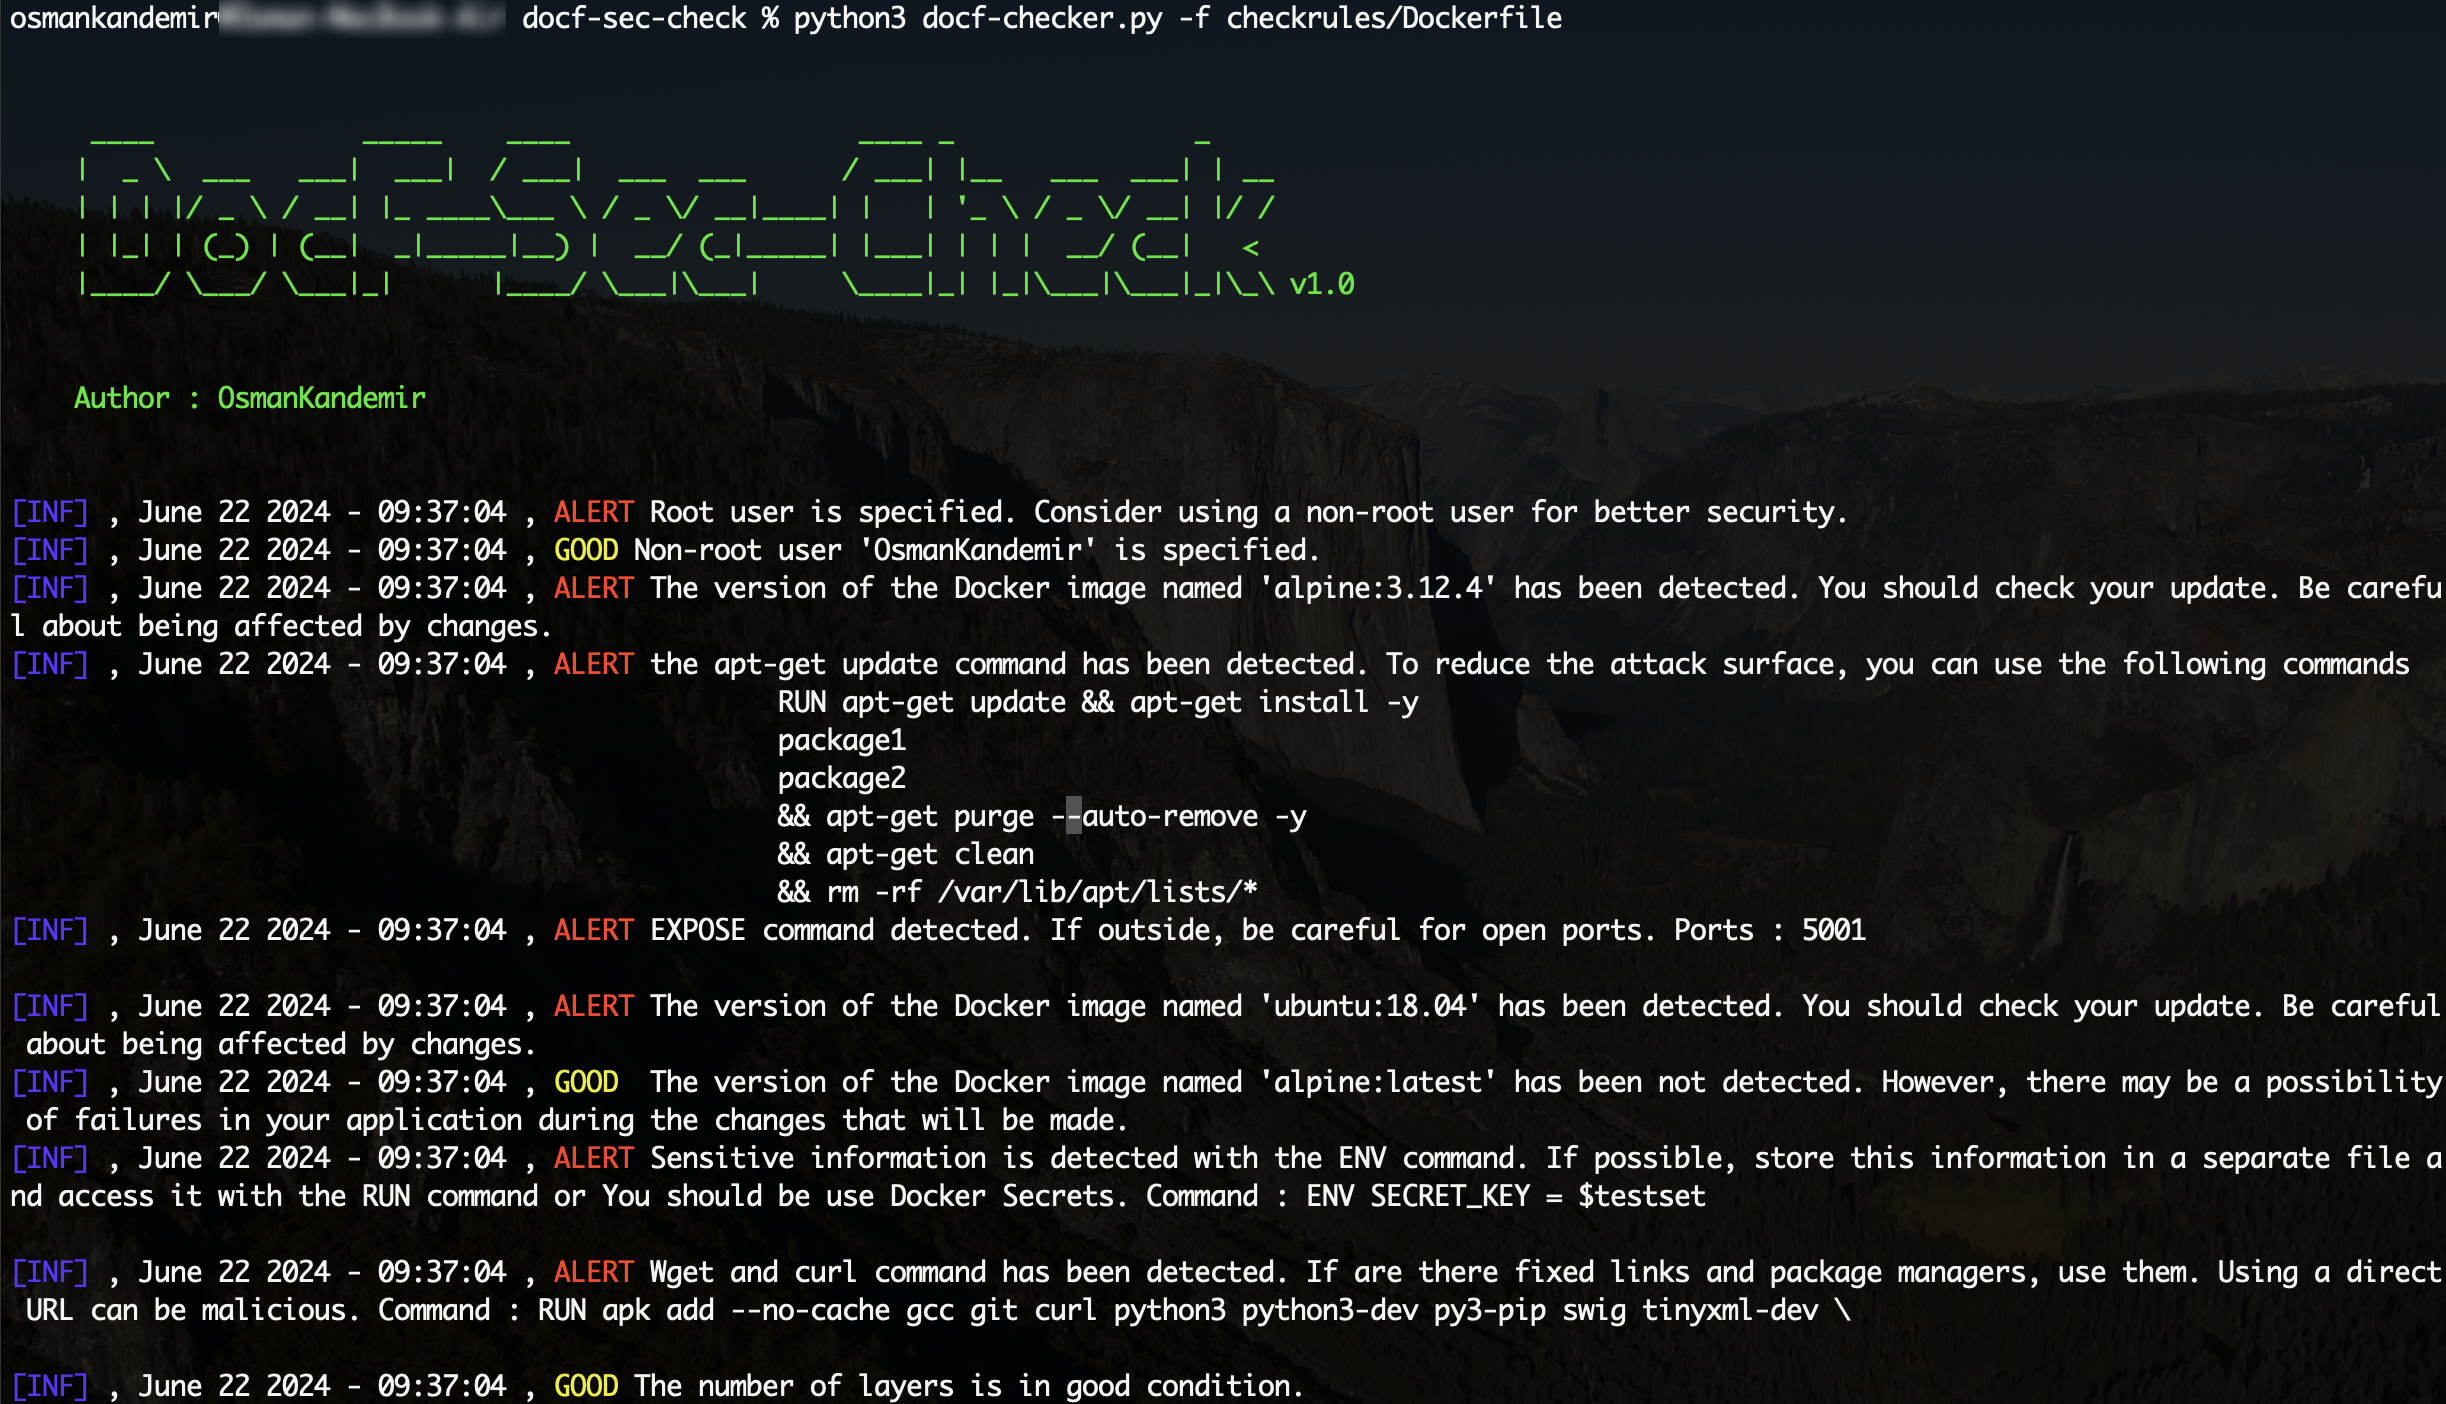 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 thestingr/reactoops-writeup
Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…