
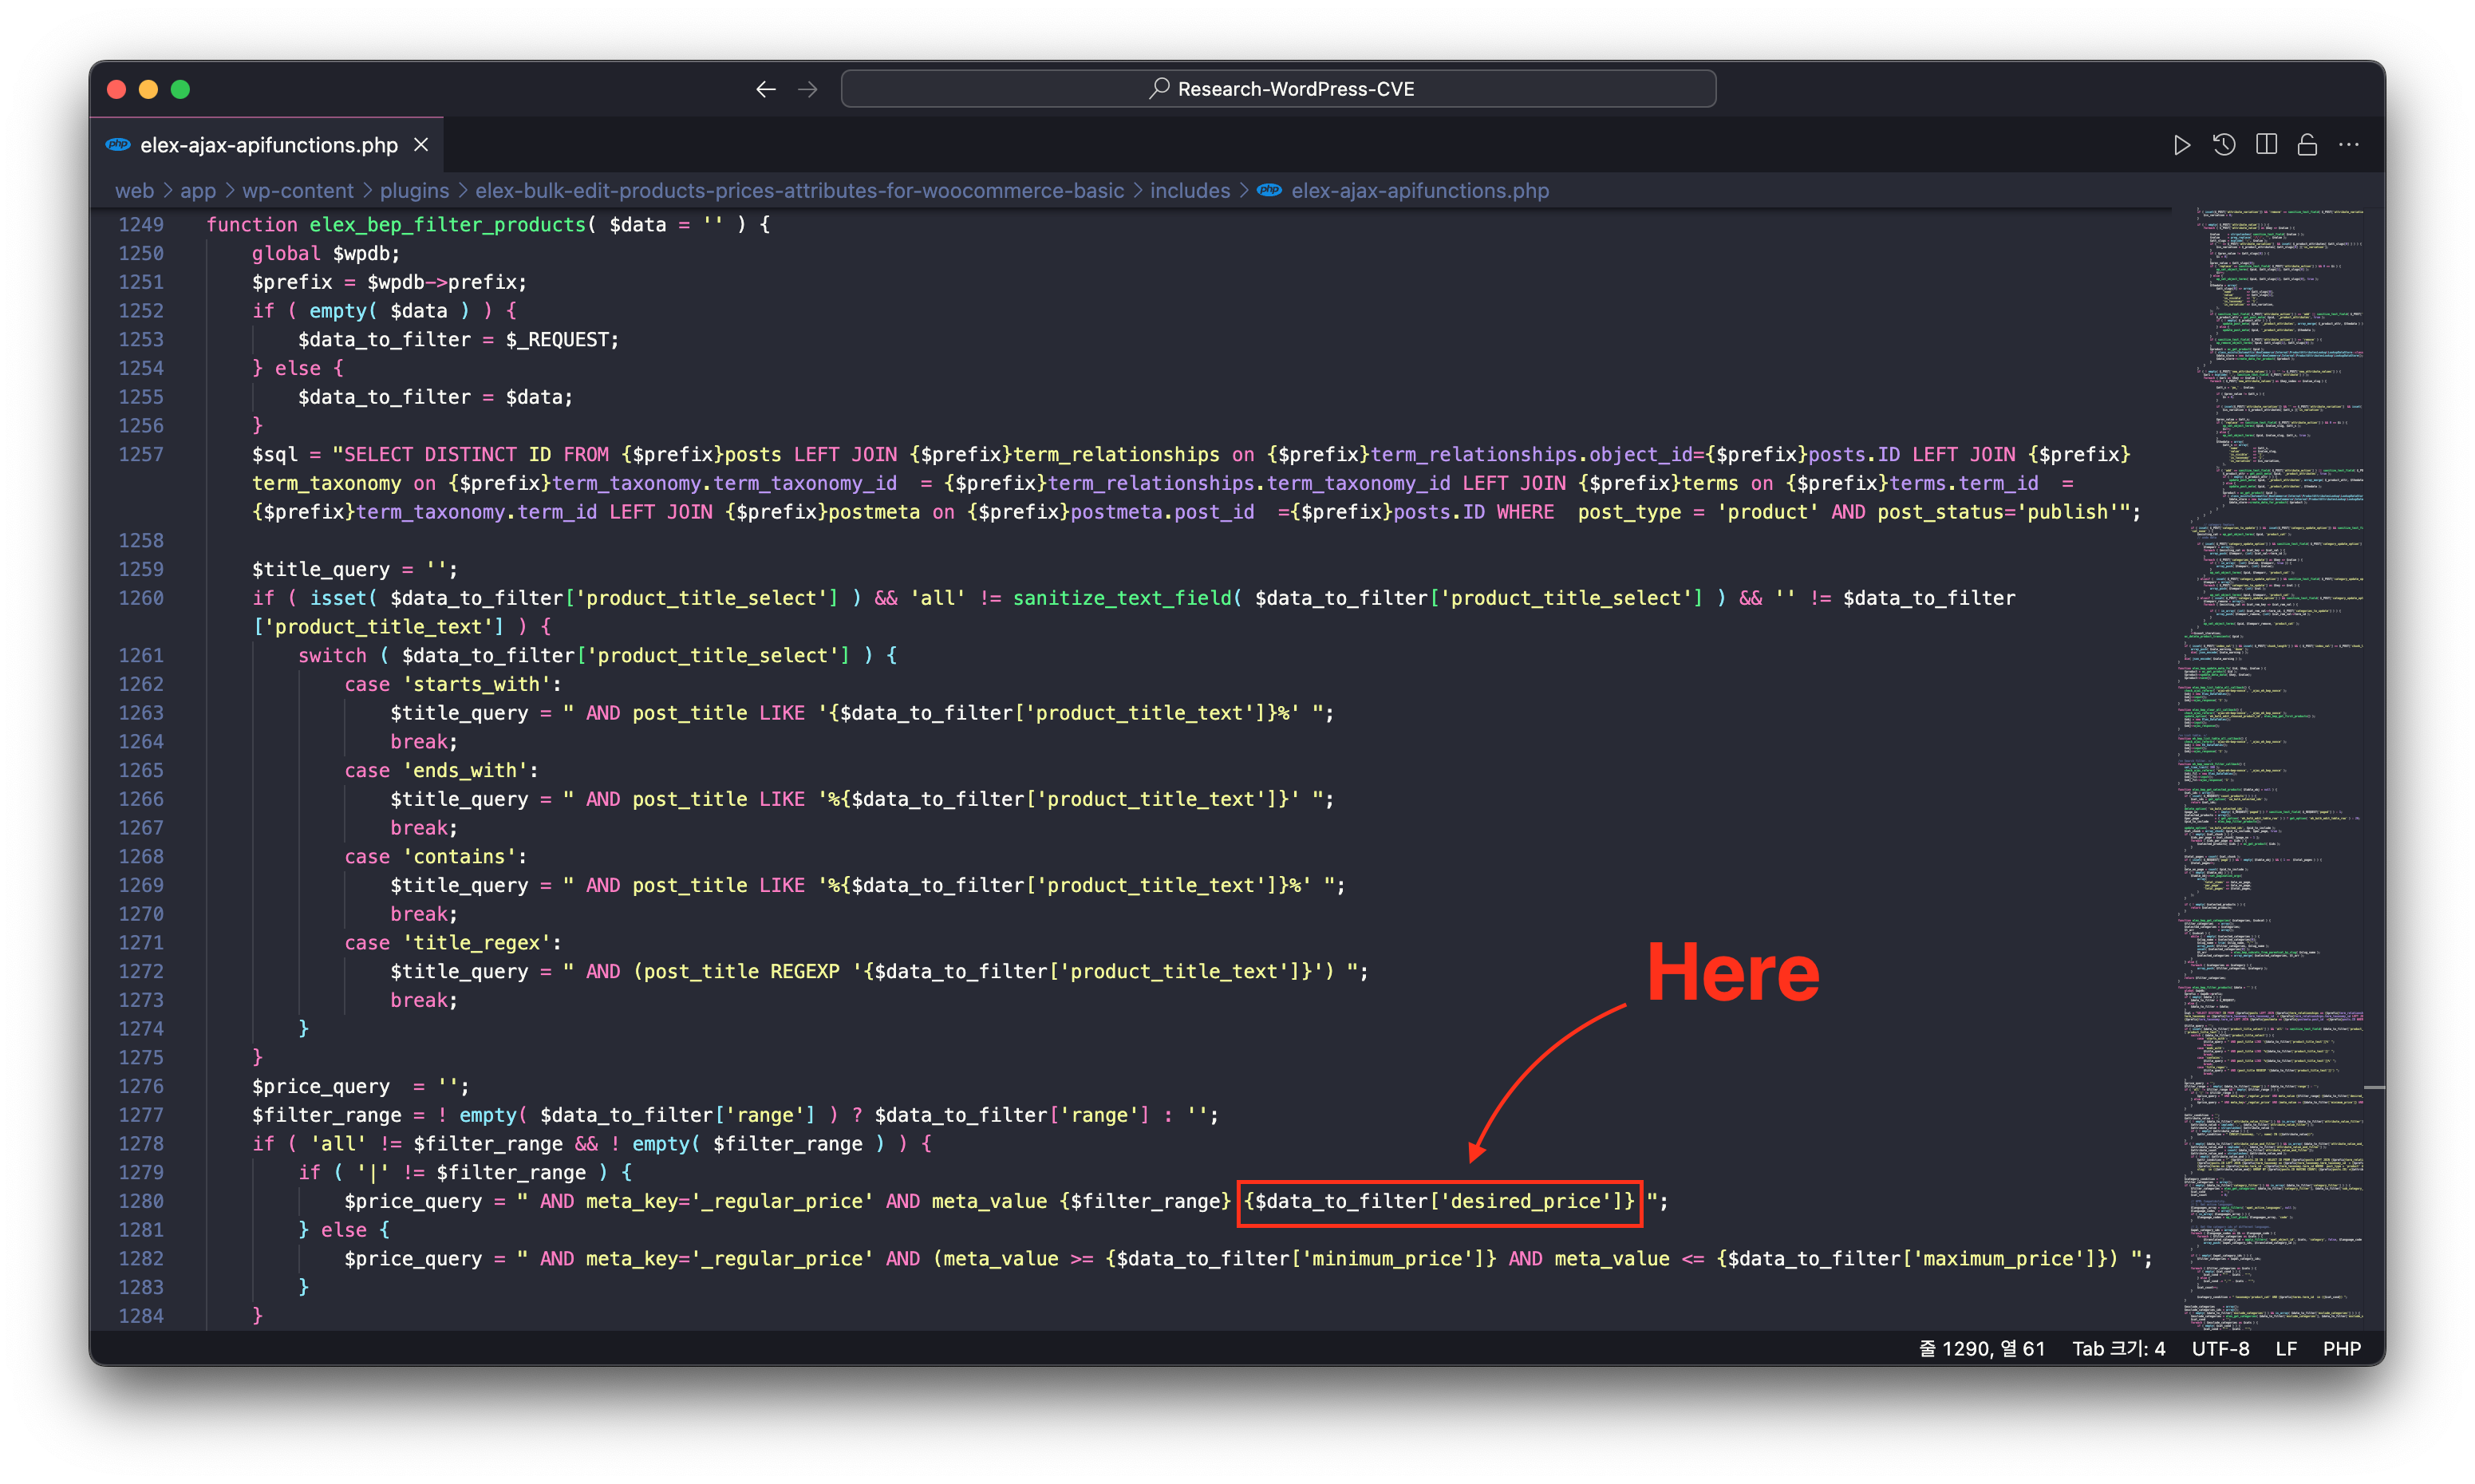
CVE-2025-22352
 dottak/cve-2025-22352
PoC of CVE-2025-22352
code-analysisexploitationpenetration-testing+2
dottak/cve-2025-22352PoC of CVE-2025-22352
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
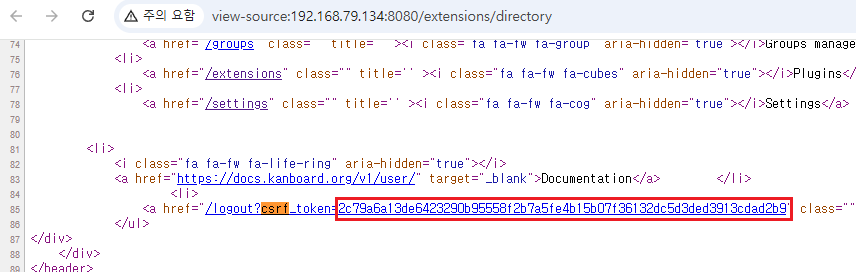 drkim-dev/cve-2026-25924
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…
 jinxia62/oracle-identity-manager-cve-2025-61757
Oracle Identity Manager 远程代码执行漏洞CVE-2025-61757
 vpn28/cve-2021-34481
Check patch for CVE-2021-34481
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
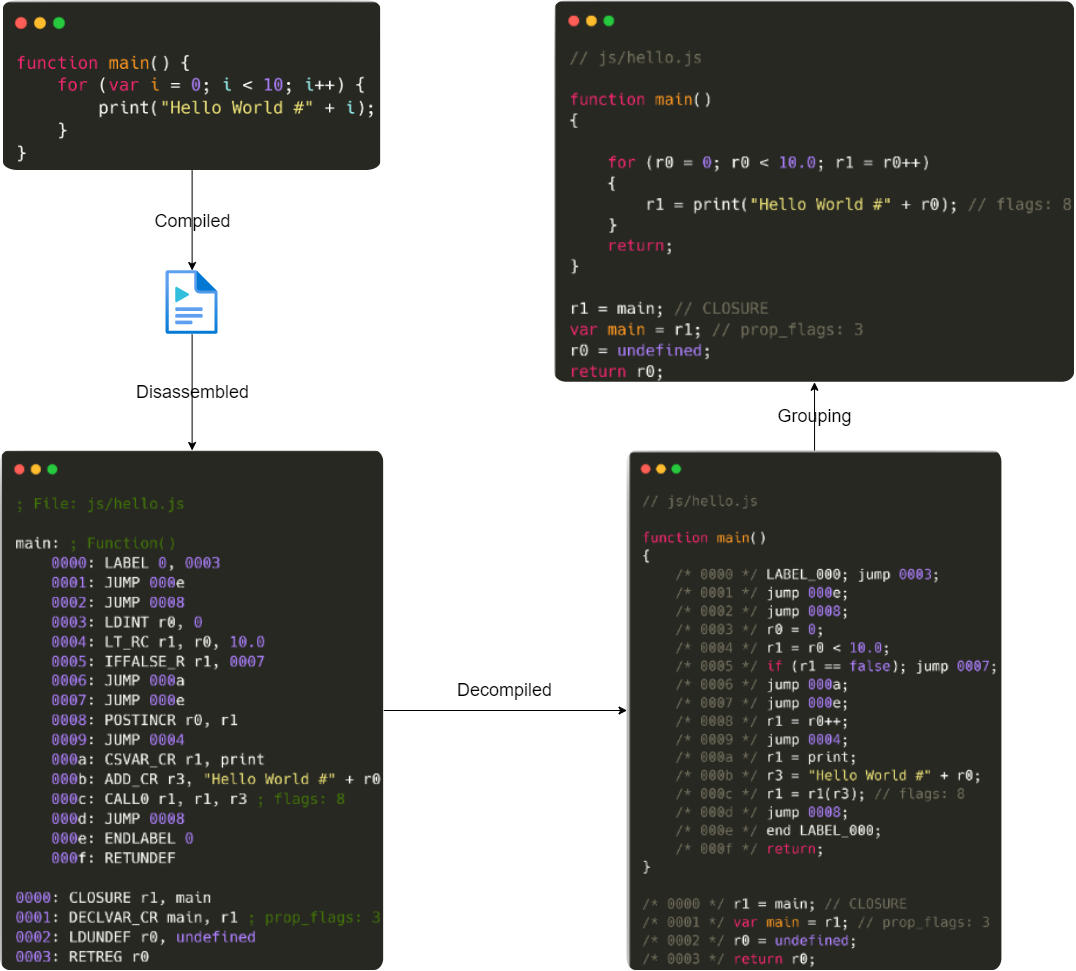 nccgroup/detaped
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 gguaiker/trend_micro_poc
CVE-2018-3608 Trend_Micro_CVE
 rat-c/cve-2024-1512
PoC for CVE-2024-1512 in MasterStudy LMS WordPress Plugin.
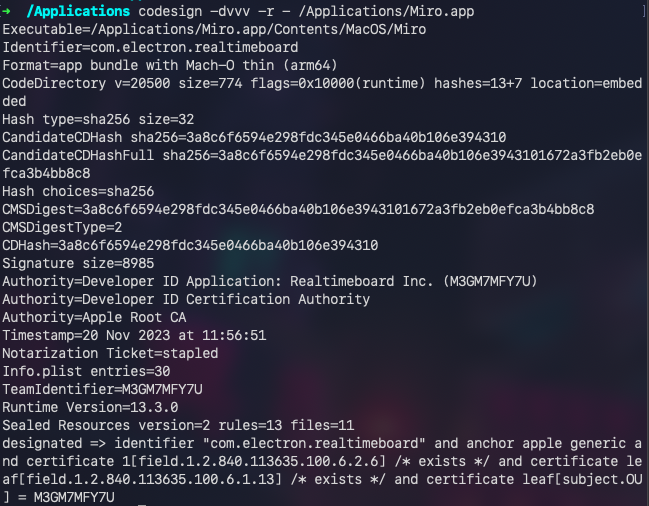 louiselalanne/cve-2024-23746
Miro Desktop 0.8.18 on macOS allows Electron code injection.
 mhtsec/cve-2026-84645
Jenkins PersistenceRoot Deserialization RCE (SECURITY-3972) — PoC & analysis. Requires Item/Configure; affects weekly <= 2.579 / LTS <= 2.568.2
 azilrababe/cve-2025-68613
Technical analysis of CVE-2025-68613, a critical Expression Injection vulnerability in n8n that allows authenticated attackers to achieve Remote Code…
 nmurilo/cve-2008-4687-exploit
Python exploit for CVE-2008-4687 targeting remote code execution in MantisBT via crafted sort parameter in manage_proj_page.php.
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 alexb616/sessionreaper-cve-2025-54236
PoC Magento Session Reaper - CVE-2025-54236