
CVE-2026-13157
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
code-analysisexploitationpayload-development+4
minhhk68/cve-2026-13157Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 p4x1s/cve-2023-33829-poc
SCM Manager XSS
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
 oscerd/cve-2026-46591
Reproducer for CVE-2026-46591: Apache Camel camel-neo4j Cypher injection via property names in CamelNeo4jMatchProperties, enabling authorization…
 izxci/cve-2026-9691
CVE-2026-9691: Integration for ActiveCampaign and Contact Form 7, WPForms, Elementor, Ninja Forms <= 1.1.1 Unauthenticated PHP Object Injection PoC,…
 kxisxr/bash-script-cve-2018-16763
FUEL CMS 1.4.1 allows PHP Code Evaluation via the pages/select/ filter parameter or the preview/ data parameter. This can lead to Pre-Auth Remote…
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
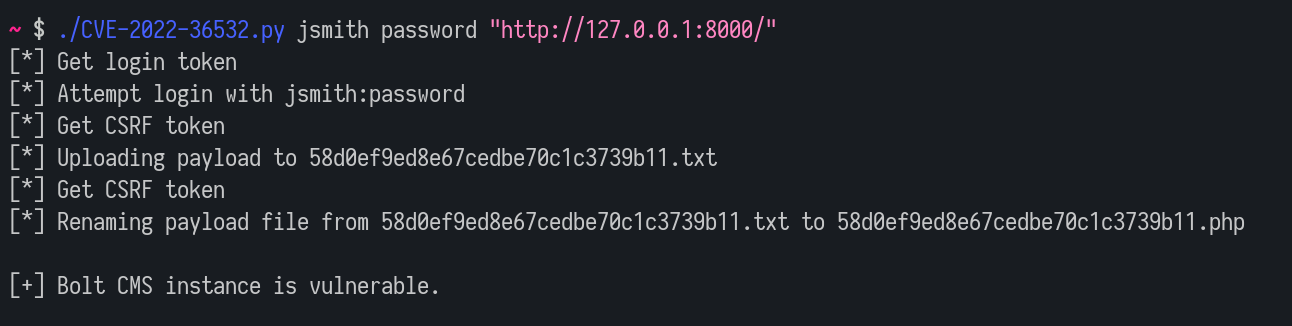 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 r00t4dm/jenkins-cve-2017-1000353
Proof-of-concept exploit for Jenkins CVE-2017-1000353, a remote code execution vulnerability via unsafe deserialization in the CLI interface.
 dottak/cve-2025-22783
PoC of CVE-2025-22783
 geraldoalcantara/cve-2023-50071
Multiple SQL injection vulnerabilities in /customer_support/ajax.php?action=save_department in Customer Support System 1.0 allow authenticated…
 breadsquad/ediop3php
A PHP CVE-2025-1219 SCANNER. In bash no root.
 e-corp-demo/cve-2026-44788
Proof-of-concept exploit for CVE-2026-44788, demonstrating vulnerability exploitation in C# for security testing and validation.
 dddo0/cve-2018-1000533
Proof-of-concept exploit for CVE-2018-1000533, a remote code execution vulnerability in GitList 0.6.0 via unsanitized input in the search function,…
 awusan125/test_for6387
test code for cve-2024-6387
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 oscerd/cve-2026-33454
Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec