
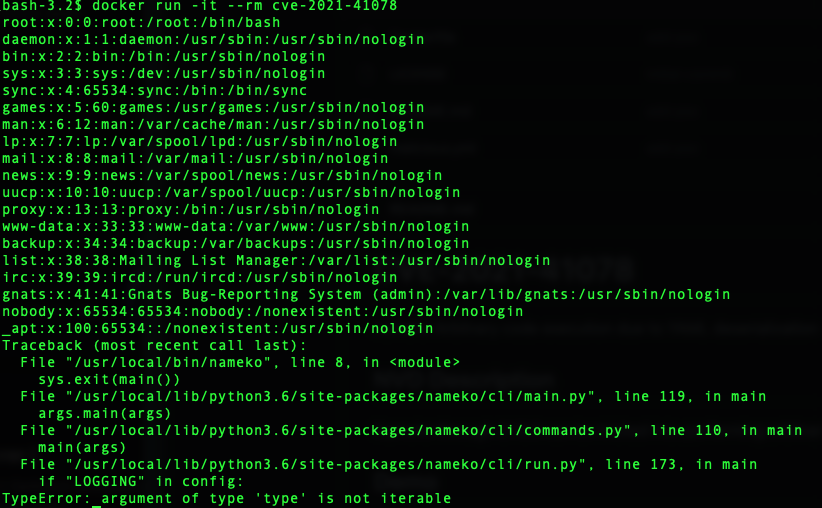
CVE-2021-41078
 s-index/cve-2021-41078
nameko Arbitrary code execution due to YAML deserialization
code-analysisexploitationmisconfiguration+3
s-index/cve-2021-41078nameko Arbitrary code execution due to YAML deserialization
 cyberharsh/groovy-scripting-engine-cve-2015-1427
Docker-based lab environment for CVE-2015-1427 ElasticSearch Groovy sandbox bypass and remote code execution, demonstrating two POC methods with Java…
 cyberharsh/php-unit-cve-2017-9841
Docker-based lab to reproduce CVE-2017-9841, a remote code execution vulnerability in PHPUnit's eval-stdin.php when installed under a web root.
 snorlyd/https-nj.gov---cve-2018-14042
Vulnearability Report of the New Jersey official site
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 jvoisin/php-malware-finder
Detect potentially malicious PHP files
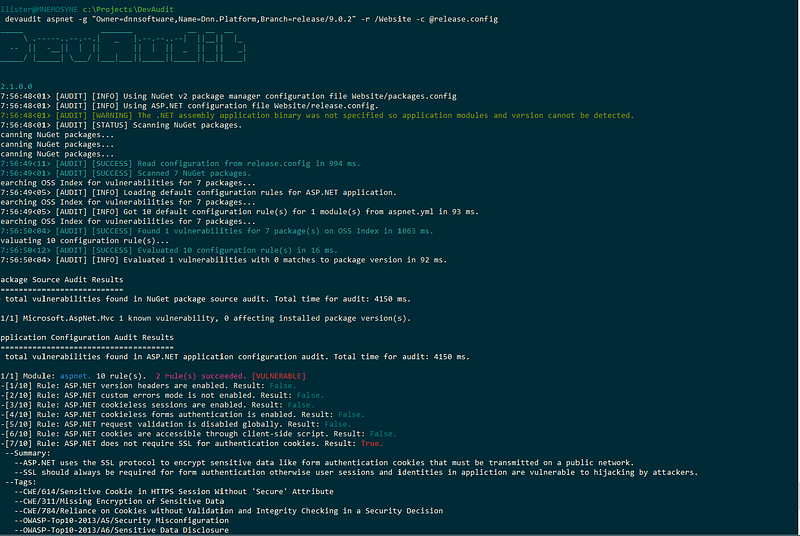 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 praetorian-inc/gokart
A static analysis tool for securing Go code
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.