
CVE-2024-21546
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
code-analysisexploitationpayload-development+4
digitalsurgn/cve-2024-21546Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
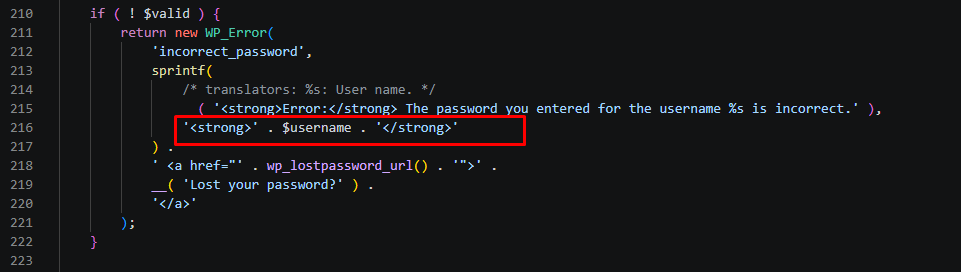 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 hosch3n/fastjsonvulns
Exploit for Fastjson 1.2.80 CVE-2022-25845 enabling AspectJ file read and Groovy remote class loading for RCE.
 matesz44/cve-2025-64512
CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads
 tokyohunter/cve-2019-9978-social-warfare-wordpress-rce
A complete walkthrough and exploit for CVE-2019-9978 - Unauthenticated Remote Code Execution in Social Warfare WordPress plugin ≤ 3.5.2. Includes…
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 oscerd/cve-2026-33454
Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec
 alexb616/sessionreaper-cve-2025-54236
PoC Magento Session Reaper - CVE-2025-54236
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 lirantal/safer-eval-cve-cve-2019-10760
Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version
 nixon-h/cve-2025-68147-ospos-stored-xss
PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…
 adamshaikhma/cve-2026-3300
Exploit for CVE-2026-3300, an unauthenticated stored XSS leading to RCE in Everest Forms Pro WordPress plugin, with a Python script to generate a…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…