
phpstan
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
code-analysisstatic-code-analysis
phpstan/phpstanPHP Static Analysis Tool - discover bugs in your code without running it!
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
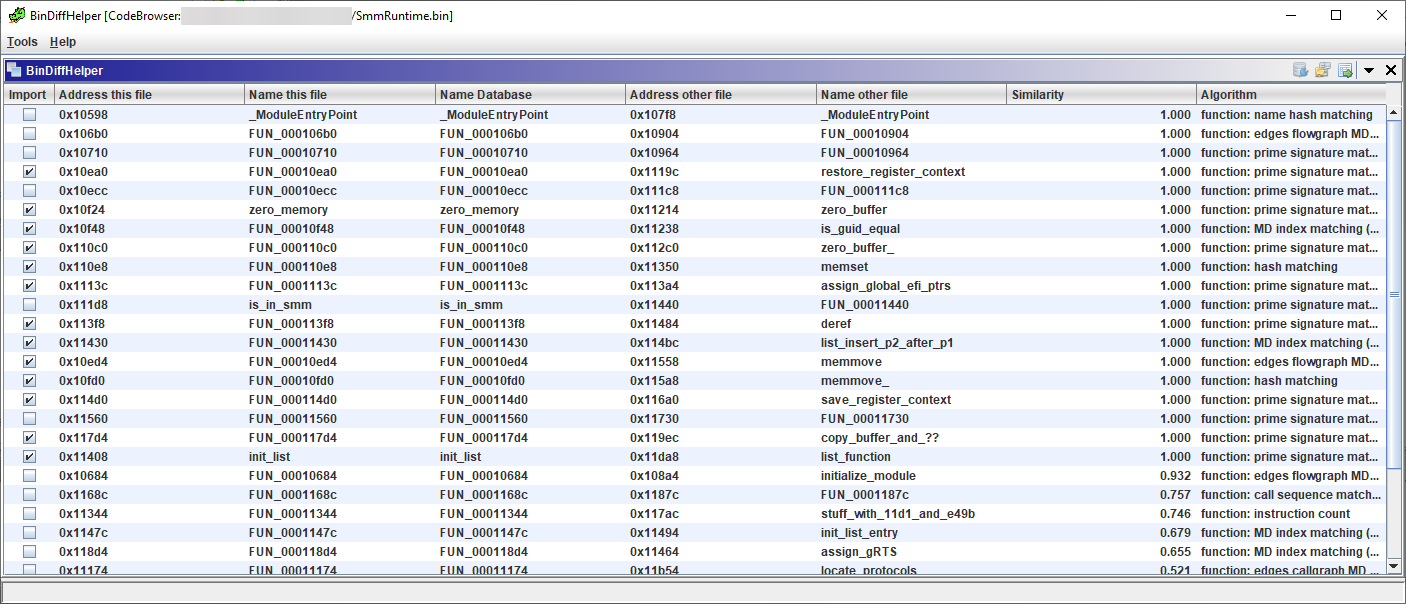 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
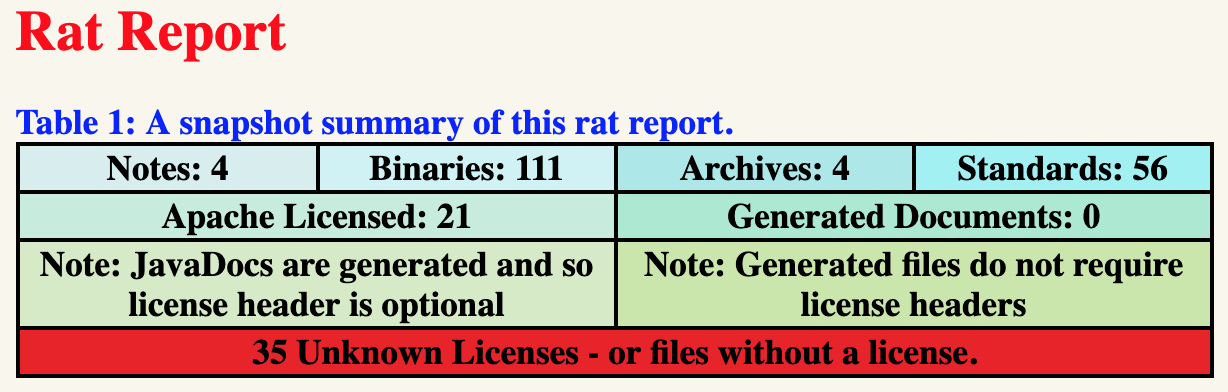 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 shoucheng3/testng-team__testng_cve-2022-4065_7-5
Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.
 falconkei/snakeyaml_cve_poc
SnakeYAML-CVE-2022-1471-POC
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
 bor8/cve-2022-34169
https://nvd.nist.gov/vuln/detail/CVE-2022-34169
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 mhaskar/bughound
Static code analysis tool based on Elasticsearch