CVE-2025-55182-Scanner

🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.

🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Collection of Solidity snippets and Foundry scripts for smart contract security audits

Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.

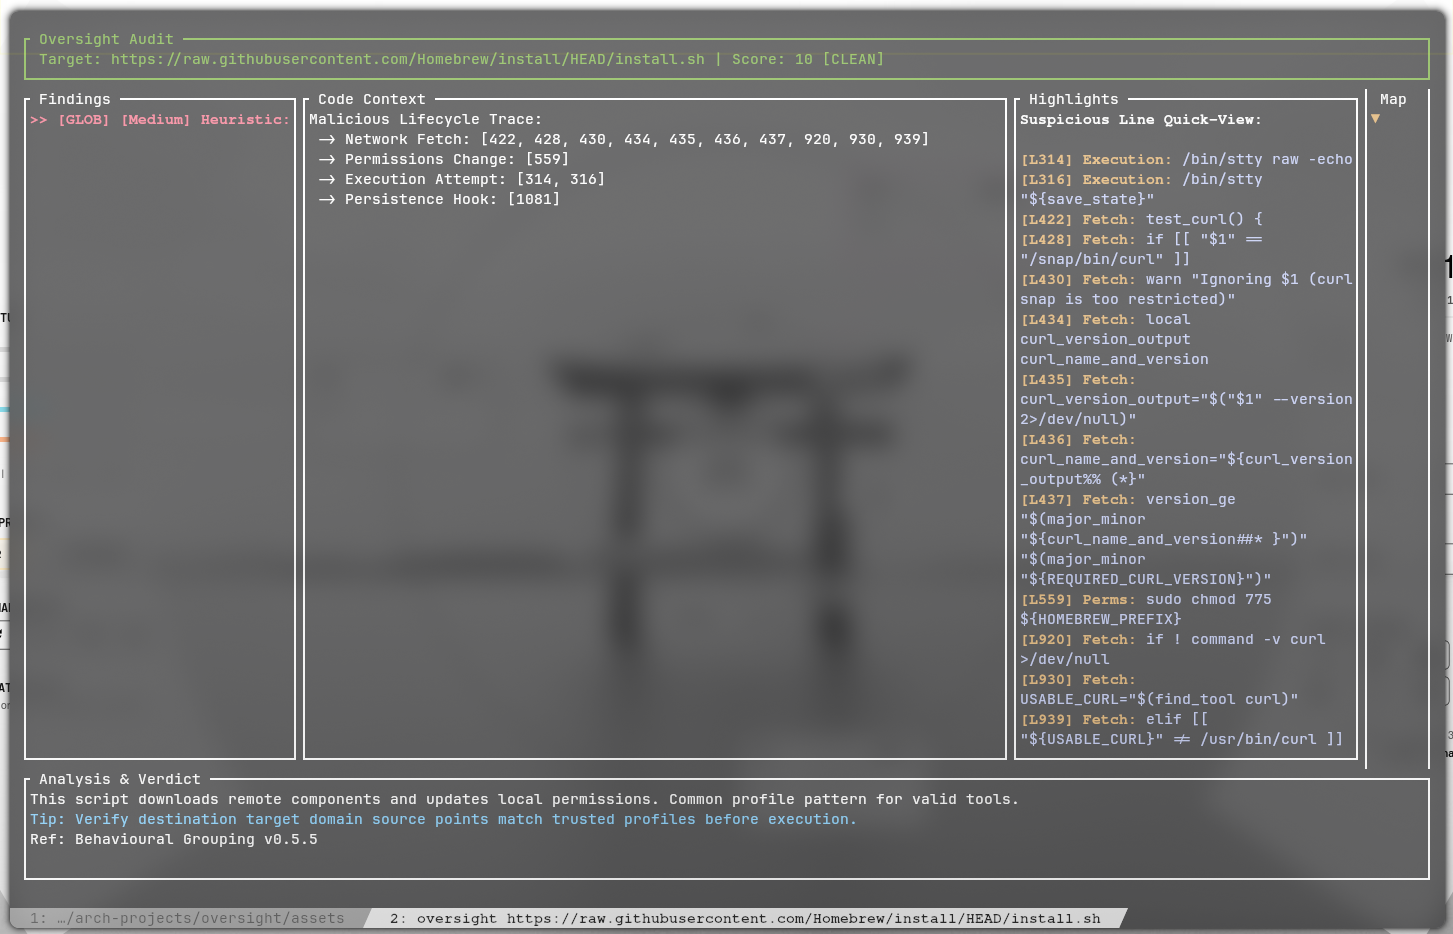
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)

Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…

JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…

WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)

Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)

Laravel 5 POP chain exploit for CVE-2021-43503, demonstrating a personally discovered deserialization vulnerability with proof-of-concept code.

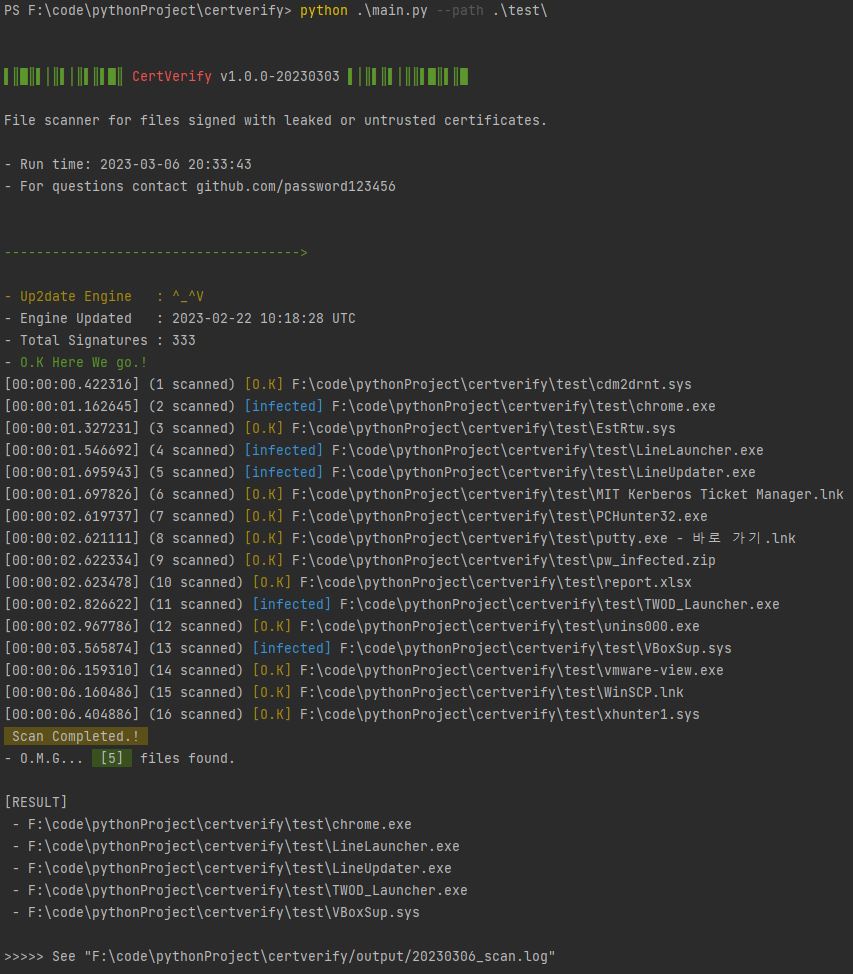
A scanner that files with compromised or untrusted code signing certificates written in python.

Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…

Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…