
Tai-e
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
android-securitycode-analysiseducation+2
1.8k5h 17m ago
pascal-lab/tai-eAn easy-to-learn/use static analysis framework for Java and Android
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
 zerowang030221/quantum-algorithm-for-elliptic-curve-discrete-logarithms-with-space-efficient-point-addition
Qiskit-based resource estimation framework for space-efficient quantum modular inversion and affine point-addition circuits used in elliptic-curve…
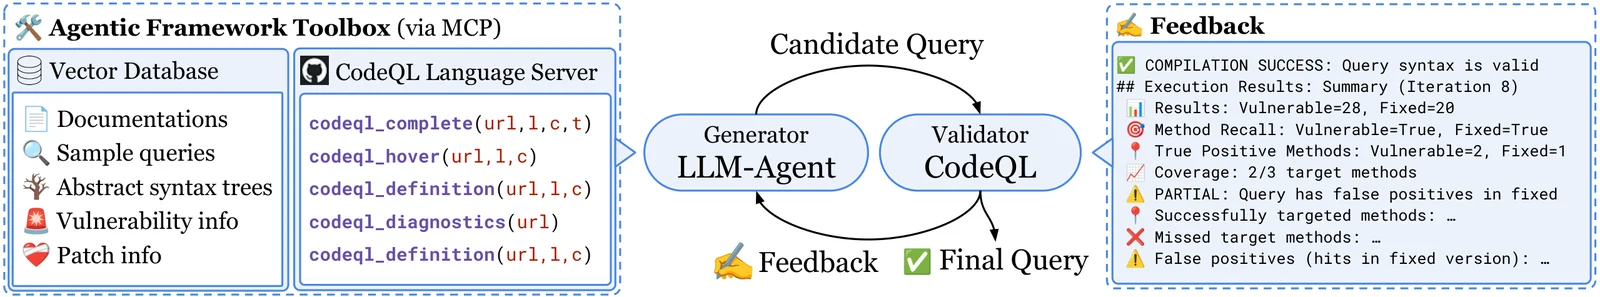 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 crytic/slither
Static Analyzer for Solidity and Vyper
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 colton1skees/dna
LLVM based static binary analysis framework
 renweimeng/vlun-agent-x
VulnAgent-X: A Layered Agentic Framework for Repository-Level Vulnerability Detection
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…