
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
openlore-PoC preview

openlore-PoC

GitHubsqueeze440/openlore-poc

PoC — path traversal via unsanitized LLM-derived domain field in OpenLore (GHSA-5j8x-q7q6-58j5, CVE-2026-87001, CVSS 4.7).
code-analysisexploitationpapers-research+3
1 month ago
CVE-2026-39902 preview

CVE-2026-39902

GitHubkx00007/cve-2026-39902

Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
code-analysisexploitationpenetration-testing+2
1 month ago
CVE-2026-52832-PoC-exploit-nuclio-dashboard preview

CVE-2026-52832-PoC-exploit-nuclio-dashboard

GitHubmdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard

Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
code-analysiscontainer-securityexploitation+3
2 months ago
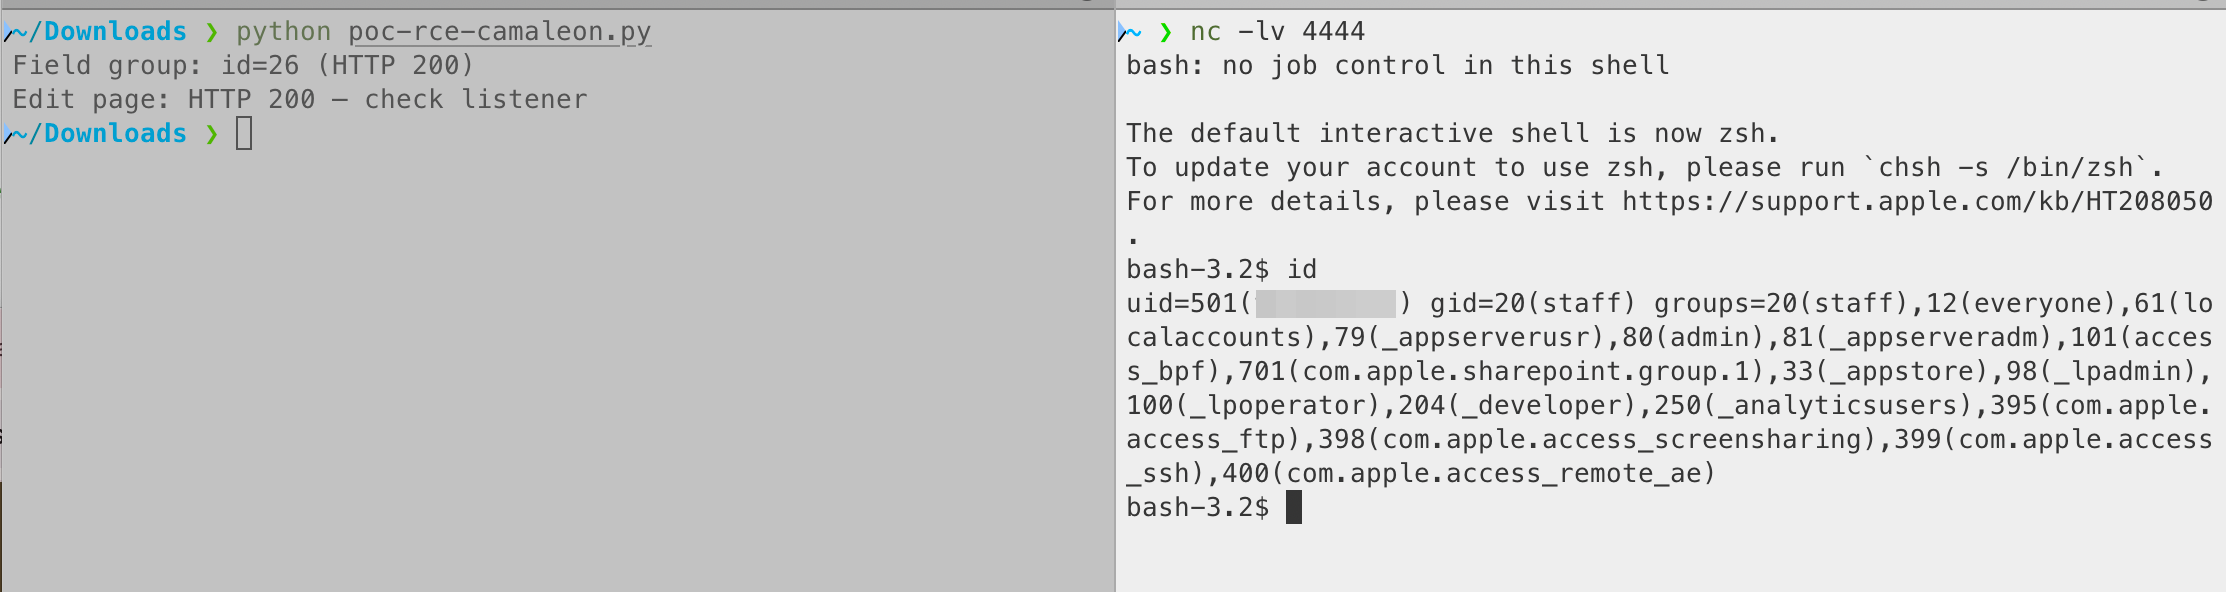
CVE-2026-66748-Camaleon-CMS---Authenticated-RCE-via-select_eval-Custom-Field preview

CVE-2026-66748-Camaleon-CMS---Authenticated-RCE-via-select_eval-Custom-Field

GitHubtheopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field

Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
code-analysisexploitationpapers-research+4
12 months ago
CVE-2026-12277 preview

CVE-2026-12277

GitHubmoritakaaz/cve-2026-12277

Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
code-analysisexploitationpayload-development+4
3 months ago
CVE-2026-39938 preview

CVE-2026-39938

GitHubkx00007/cve-2026-39938

Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
code-analysisexploitationinformation-gathering+3
4 months ago
cve-2026-25541-fuel-analysis preview

cve-2026-25541-fuel-analysis

GitHubtrajanox/cve-2026-25541-fuel-analysis

CVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
code-analysiscurated-resourceseducation+3
14 months ago
By-Poloss..-..CVE-2026-7515-PoC preview

By-Poloss..-..CVE-2026-7515-PoC

GitHubpolosss/by-poloss..-..cve-2026-7515-poc

Unauthenticated Local File Inclusion
code-analysiseducationexploitation+3
14 months ago
By-Poloss..-..CVE-2017-20251 preview

By-Poloss..-..CVE-2017-20251

GitHubpolosss/by-poloss..-..cve-2017-20251

Insert PHP Plugin PHP Code Injection
code-analysiseducationexploitation+4
14 months ago
CVE-2026-48030 preview

CVE-2026-48030

GitHubmuslimbek-0x/cve-2026-48030

Proof-of-concept exploit for CVE-2026-48030, a critical OS command injection in Pheditor 2.0.1-2.0.3. Includes vulnerable code analysis, PoC script,…
code-analysiseducationexploitation+3
4 months ago
CVE-2026-47102-PoC preview

CVE-2026-47102-PoC

GitHublearner202649/cve-2026-47102-poc

The code for personally reproducing the corresponding vulnerability
code-analysiseducationexploitation+5
5 months ago
CVE-2026-35196 preview

CVE-2026-35196

GitHubkx00007/cve-2026-35196

Second CVE still Remote Code Execution
code-analysiseducationexploitation+3
5 months ago
CVE-2026-11344-RCE preview

CVE-2026-11344-RCE

GitHubxmyronn/cve-2026-11344-rce

Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
code-analysisexploitationinformation-gathering+5
5 months ago
CVE-2026-7393-RCE preview

CVE-2026-7393-RCE

GitHubxmyronn/cve-2026-7393-rce

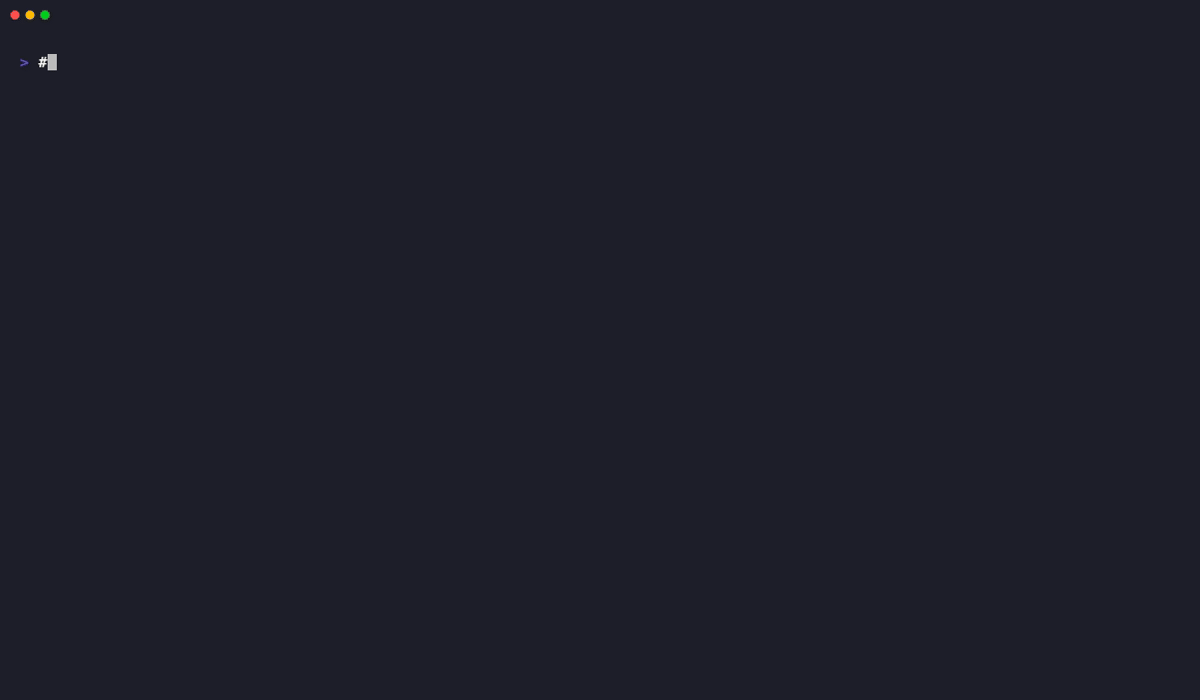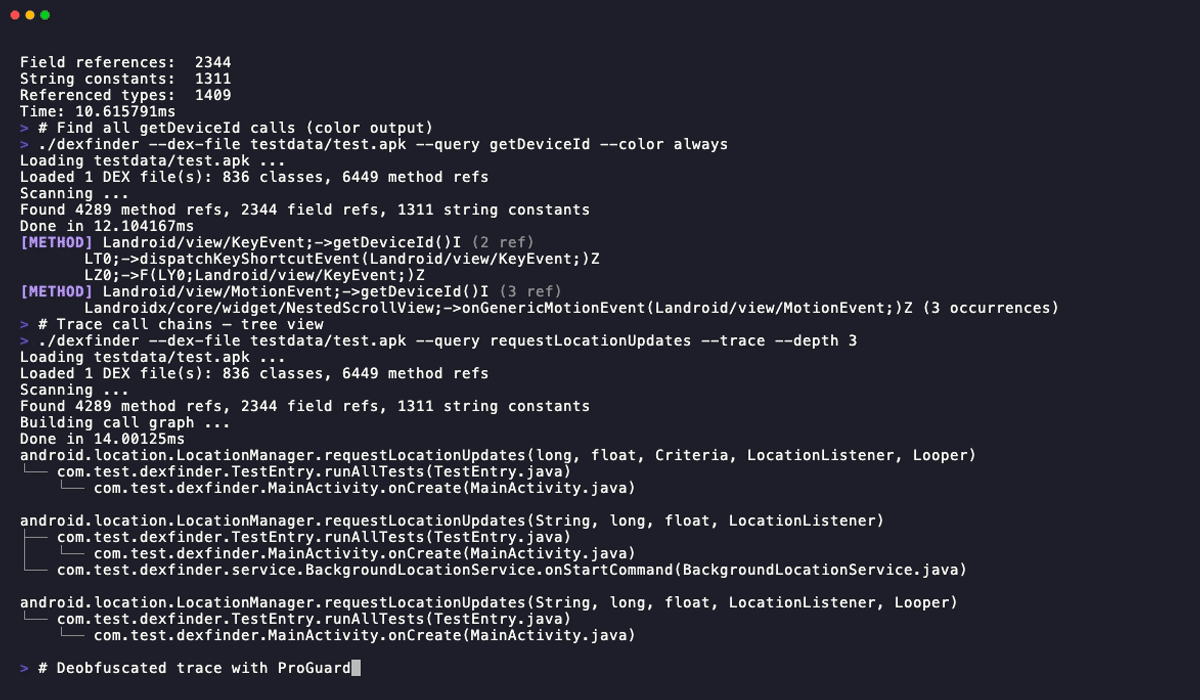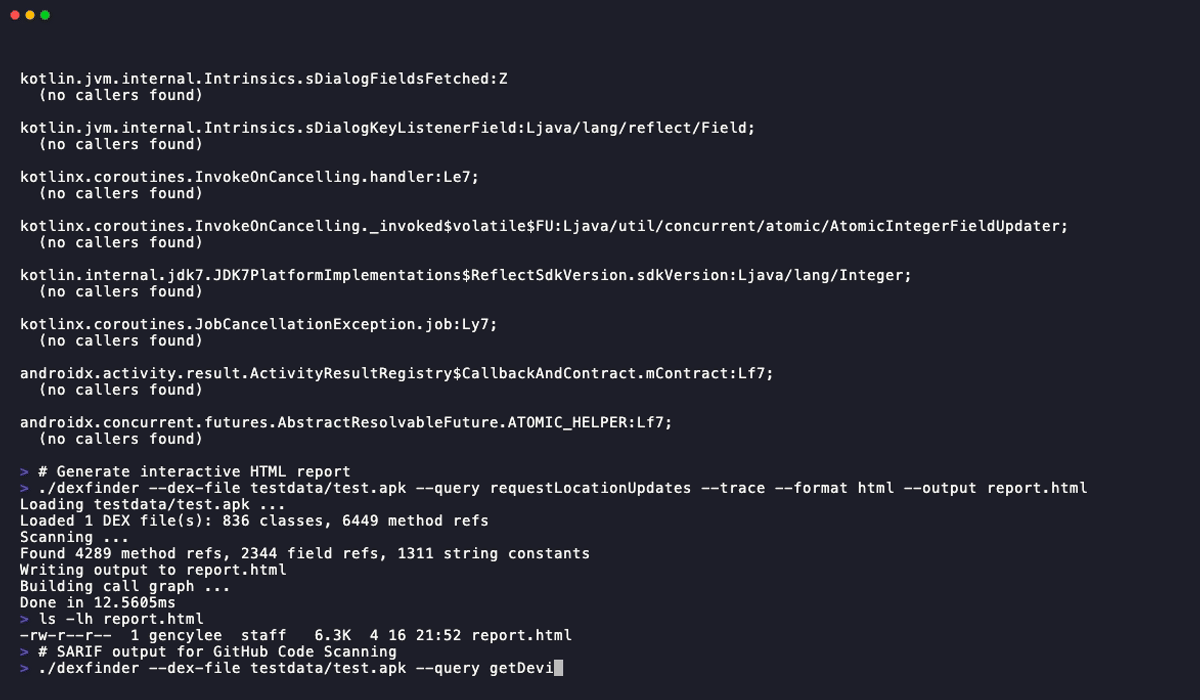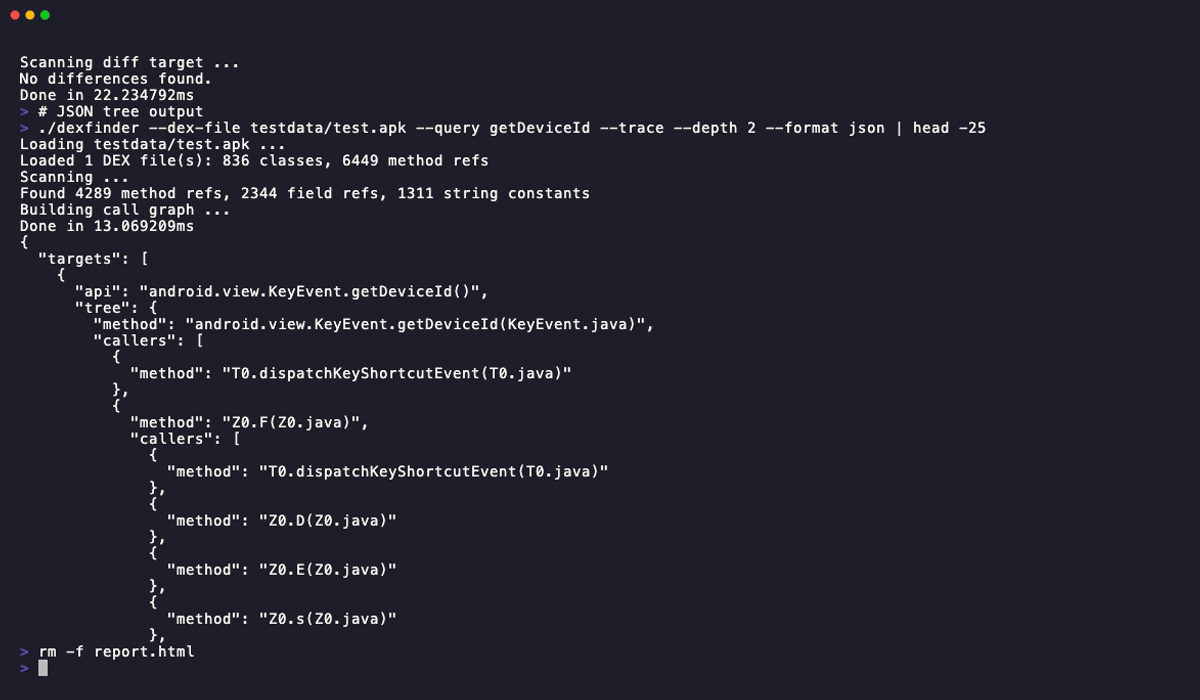
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
code-analysisexploitationpayload-generation+3
5 months ago
dexfinder preview

dexfinder

GitHubjunelegency/dexfinder

Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
android-securitybinary-analysiscode-analysis+6
1086 months ago
CVE-2025-49113-Roundcube-RCE preview

CVE-2025-49113-Roundcube-RCE

GitHubrippsec/cve-2025-49113-roundcube-rce

CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
code-analysisctfexploitation+4
6 months ago
CVE-2026-22692 preview

CVE-2026-22692

GitHublukasz-rybak/cve-2026-22692

CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
code-analysiseducationexploitation+3
6 months ago
CVE-2026-23498 preview

CVE-2026-23498

GitHublukasz-rybak/cve-2026-23498

CVE-2026-23498 - Shopware Has Improper Control of Generation of Code in Twig rendered views

code-analysiseducationpapers-research+2
6 months ago
Previous12Next