
preflight
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
code-analysisconfiguration-auditingdevsecops+8
62
preflightsh/preflightGo-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
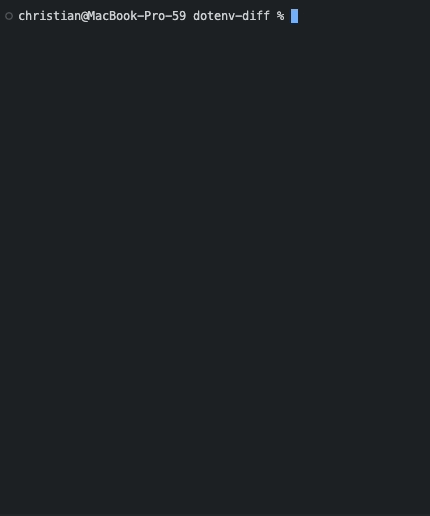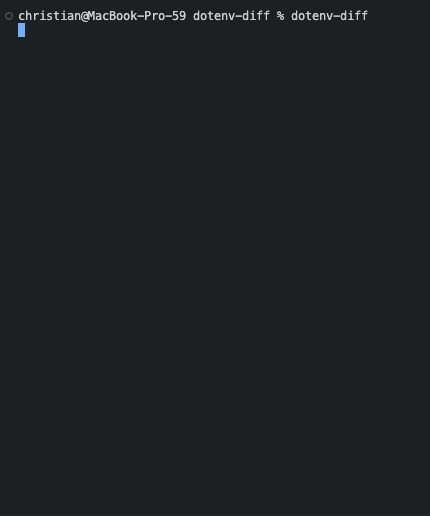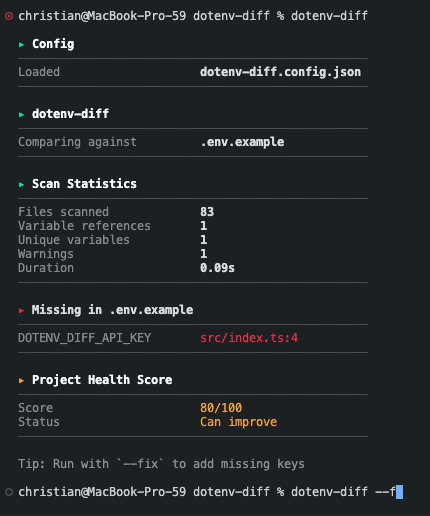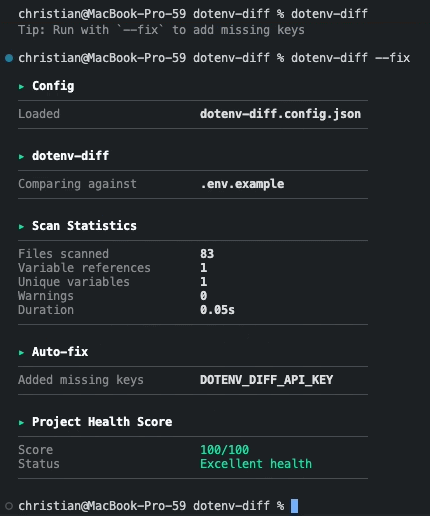 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
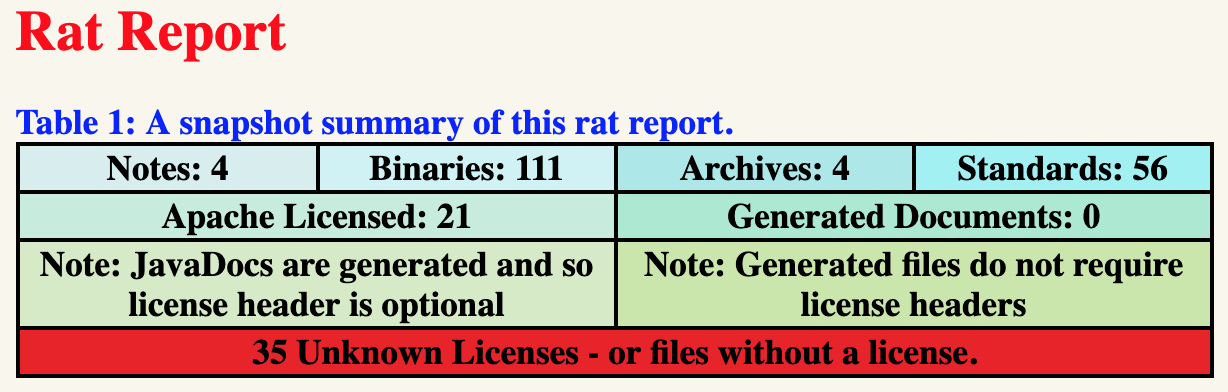 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 califio/ngxray
ngxray — nginx config security scanner
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
 surri/audit-axios
Scan local repos for vulnerable axios versions (CVE-2026-40175) and patch interactively