

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.2k21h 43m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
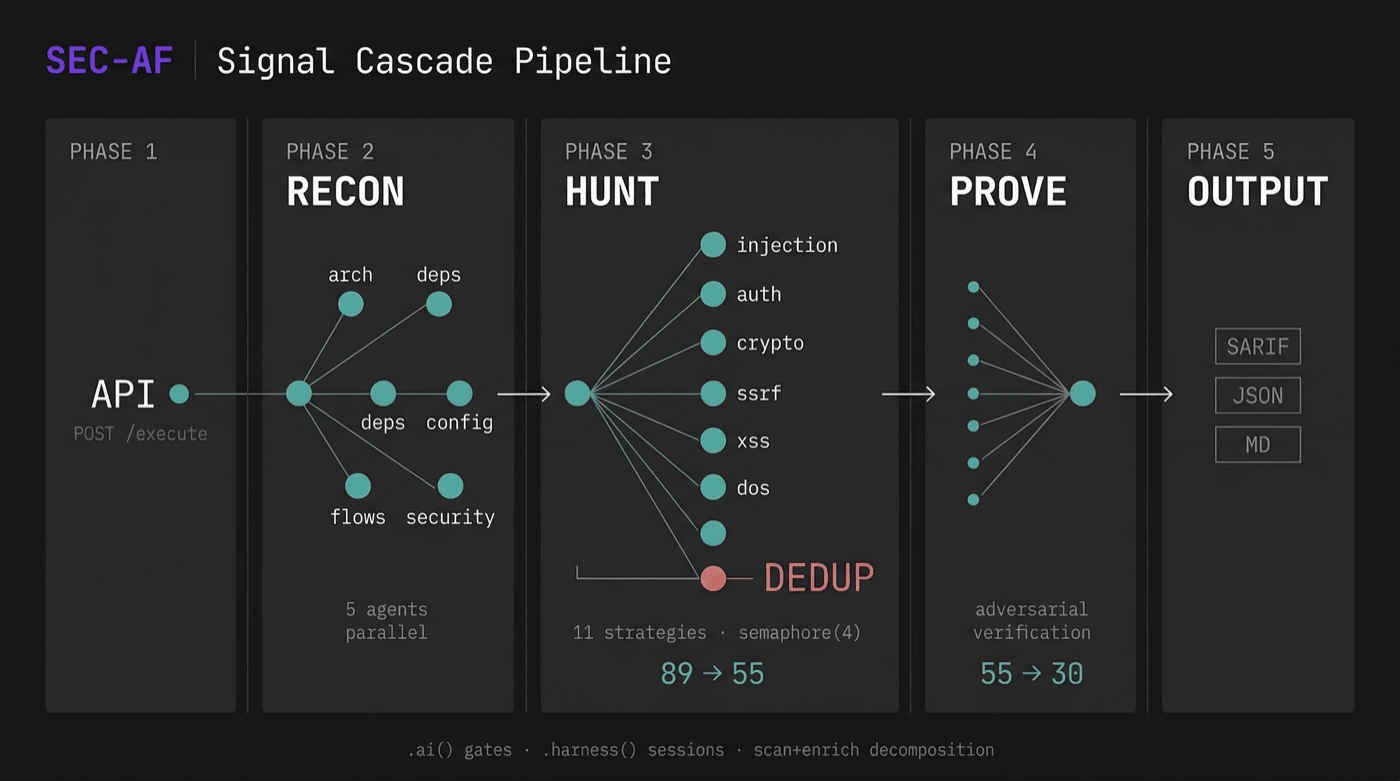 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 rat5ak/cve-2025-55182-react2shell-rce-poc
This repository documents research into deserialization behavior within Next.js React Server Components (RSC) using the Flight protocol. It focuses…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 lunixbochs/revsync
realtime cross-tool collaborative reverse engineering
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 otaviokr/log4j-2021-vulnerability-study
This is a showcase how the Log4J vulnerability (CVE-2021-44228) could be explored. This code is safe to run, but understand what it does and how it…
 chilit-nl/log4shell-example
The goal of this project is to demonstrate the log4j cve-2021-44228 exploit vulnerability in a spring-boot setup, and to show how to fix it.
 paolorabbito/internet-security-project---cve-2021-26814
Educational exploit demonstration for CVE-2021-26814 targeting Wazuh v4.0.3, with step-by-step exploitation and remediation code for university-level…
 exploitblizzard/cve-2020-0601-spoofkey
Proof-of-concept exploit for CVE-2020-0601 demonstrating spoofed cryptographic key generation and code signing using OpenSSL and Ruby.