
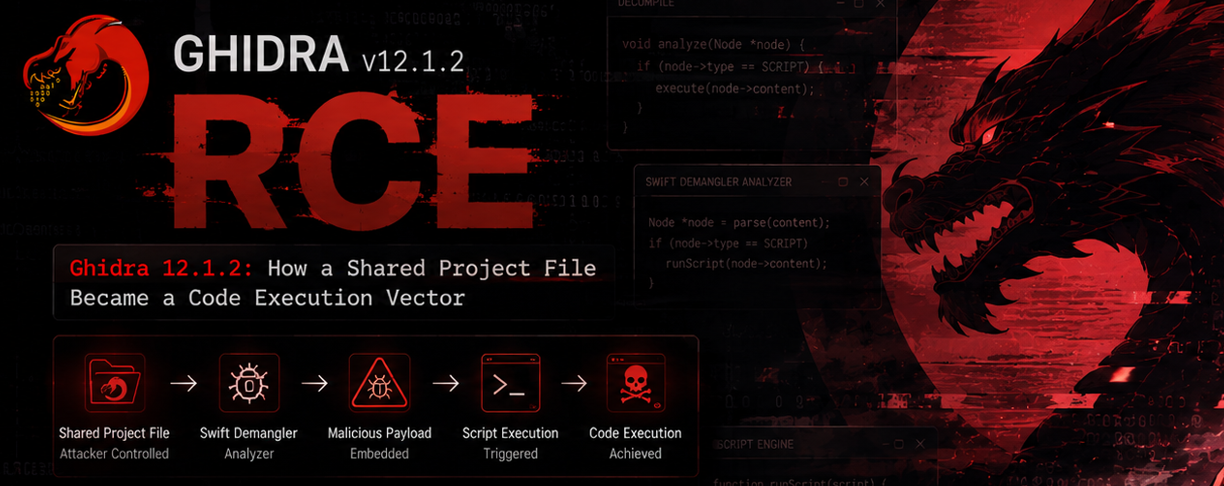
CVE-2026-18718
 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
code-analysisexploitationpayload-generation+2
1
sn0x-sharma/cve-2026-18718Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 crytic/slither
Static Analyzer for Solidity and Vyper
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
 matesz44/cve-2025-64512
CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 xxconi/cve-2026-27384
Automated scanner and exploit for CVE-2026-27384, an unauthenticated RCE in W3 Total Cache via mfunc/eval() injection. Features auto-detection, 48…
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 kerburenthusiasm/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132 enabling unauthenticated remote code execution in Pterodactyl Panel <= 1.11.10 via locale parameter…
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 dharan10/cve-2022-40471
Exploit code for Clinic patient management system v1 unauth rce cpms rce CVE-2022-40471
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…

 anothersec/cve-2025-6440
WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload
 d0n601/cve-2025-13595
CIBELES AI <= 1.10.8 - Unauthenticated Arbitrary File Upload