
ggshield
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
code-analysisdevsecopssecret-detection+1
2.0k
gitguardian/ggshieldDetect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
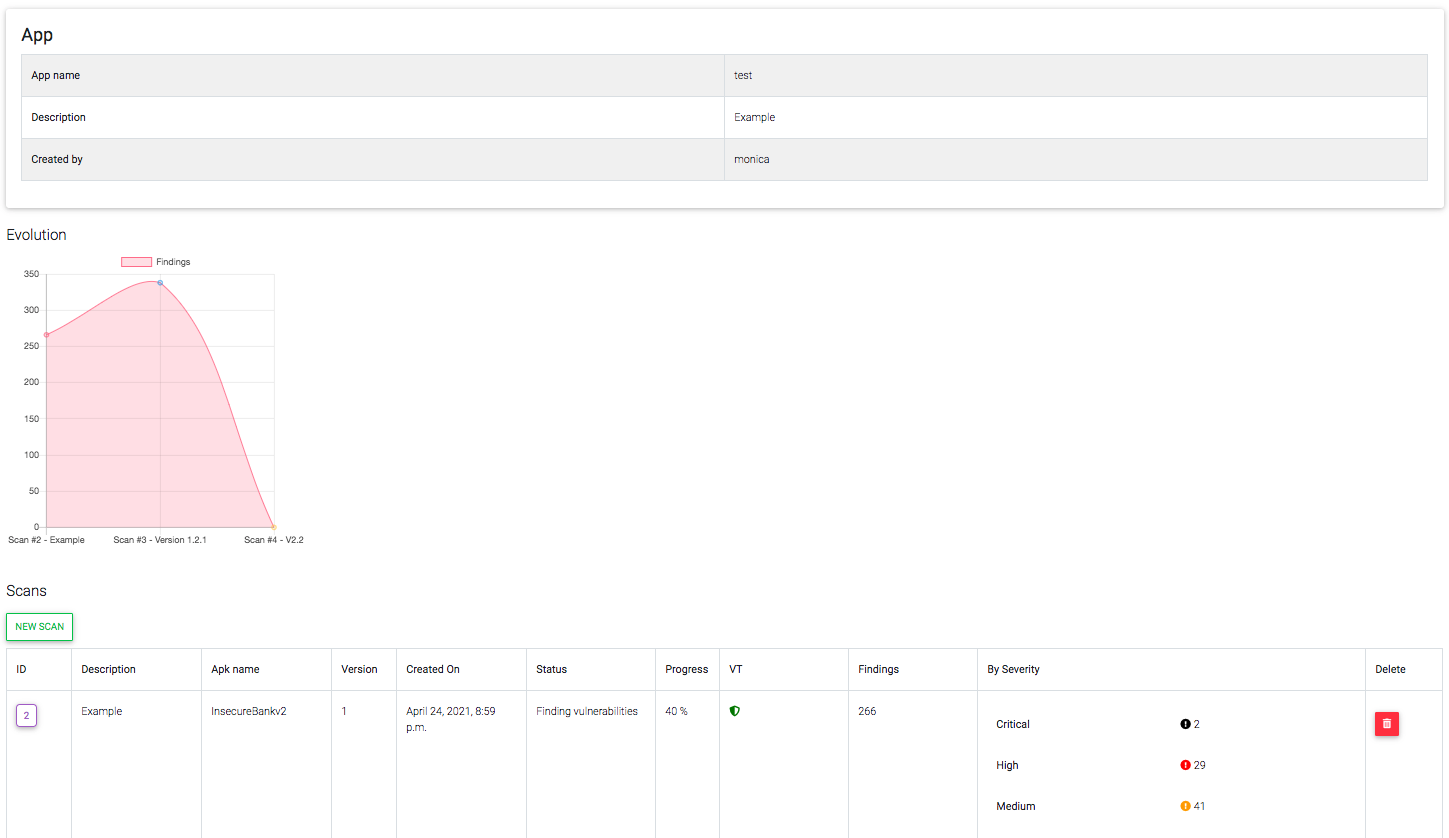 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 owasp/asvs
Application Security Verification Standard
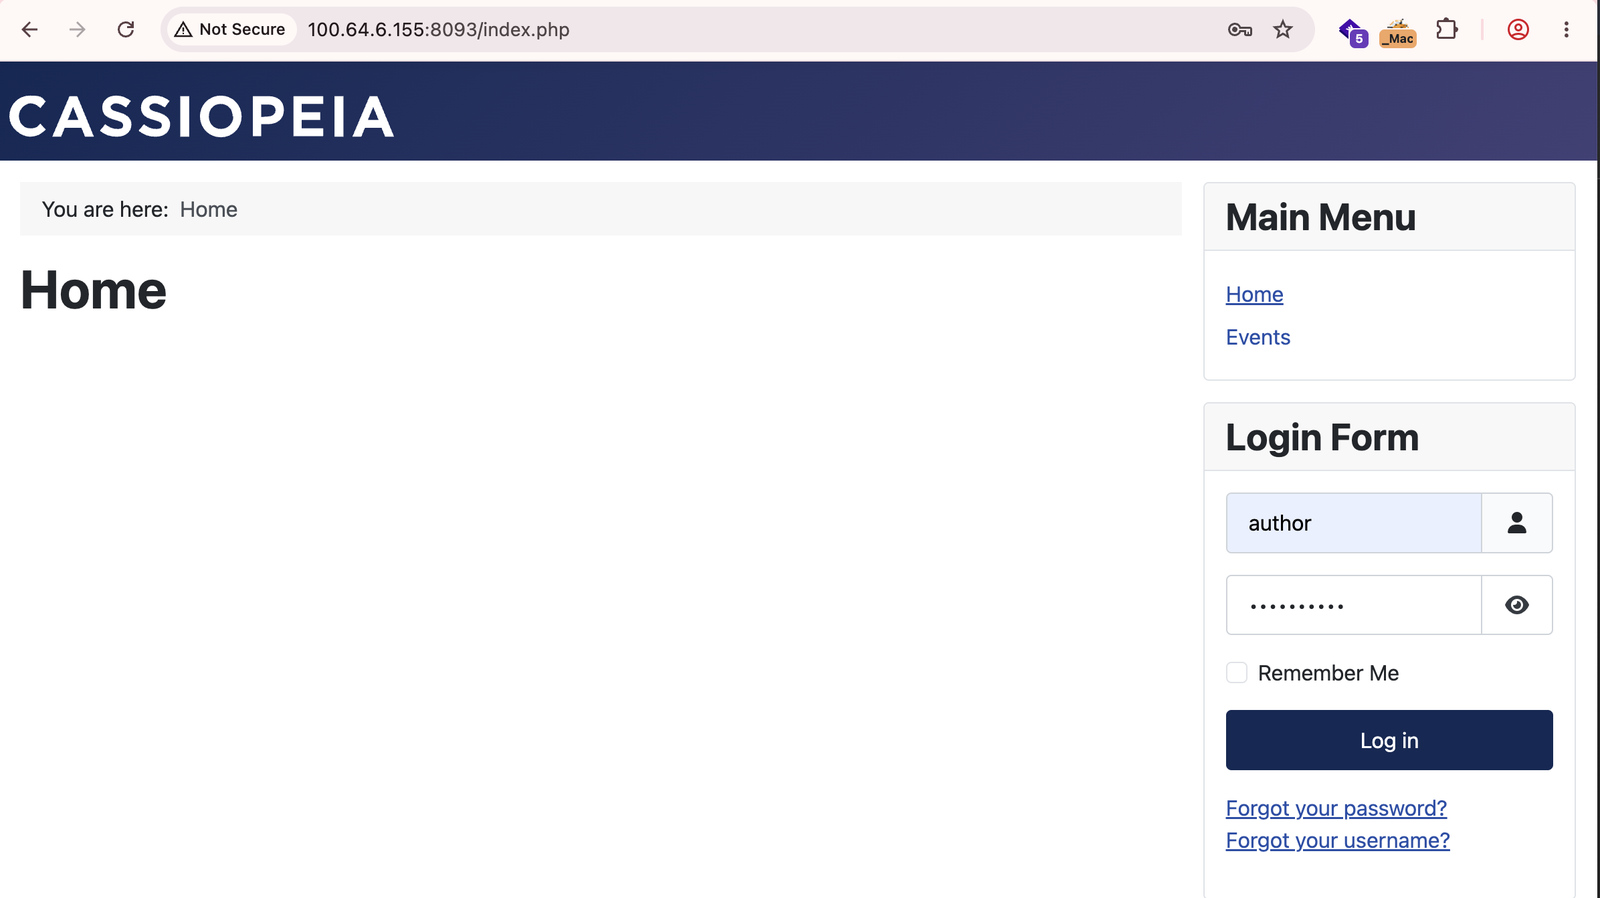 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 binsec/xyntia
Xyntia, the black-box deobfuscator
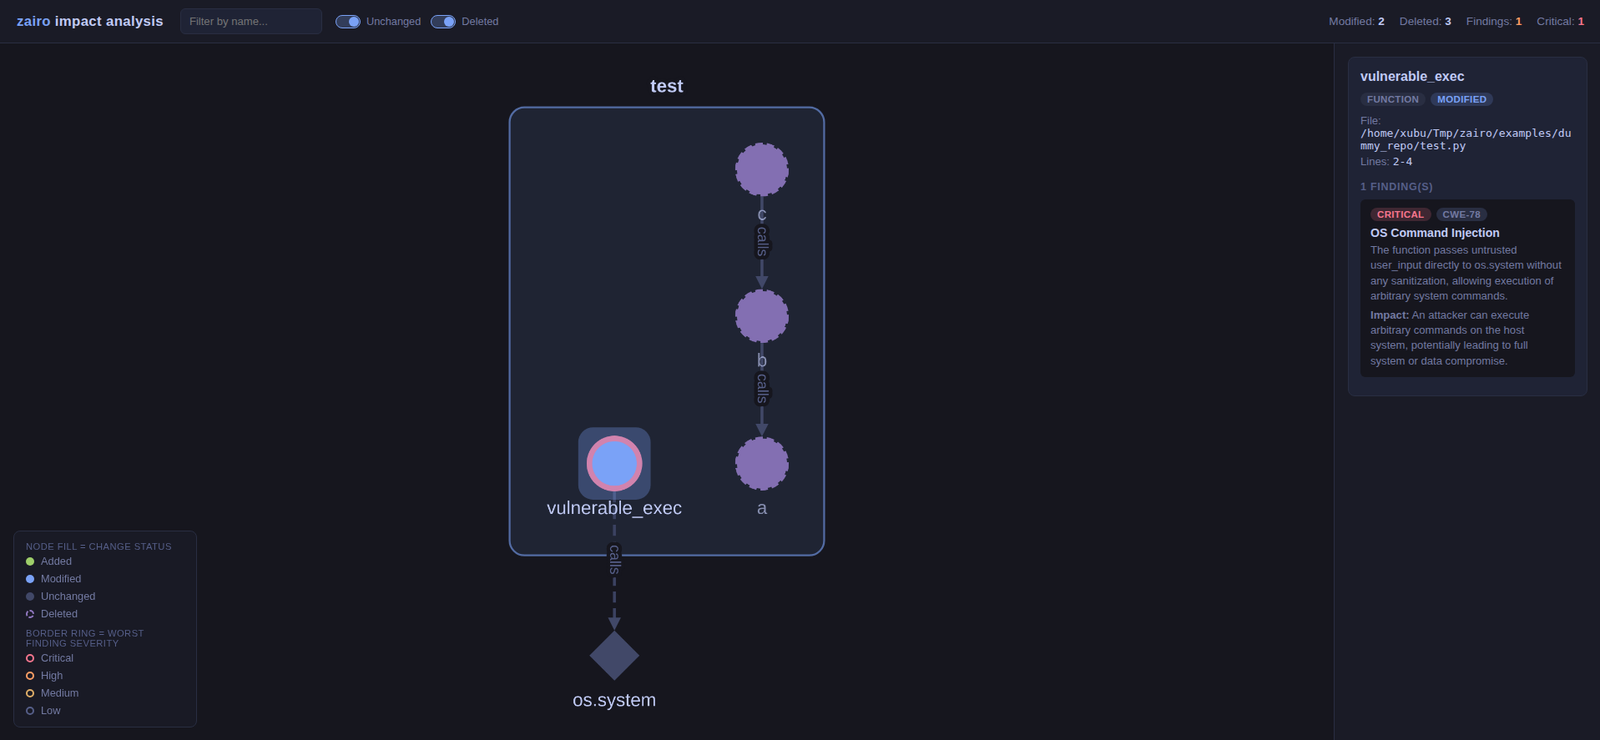 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)