vue-template-compiler-patched
 bio/vue-template-compiler-patched
Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506
code-analysisgeneral-purpose-utilitiesstatic-analysis+2
24
bio/vue-template-compiler-patchedPatched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 oscerd/cve-2026-25747
CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
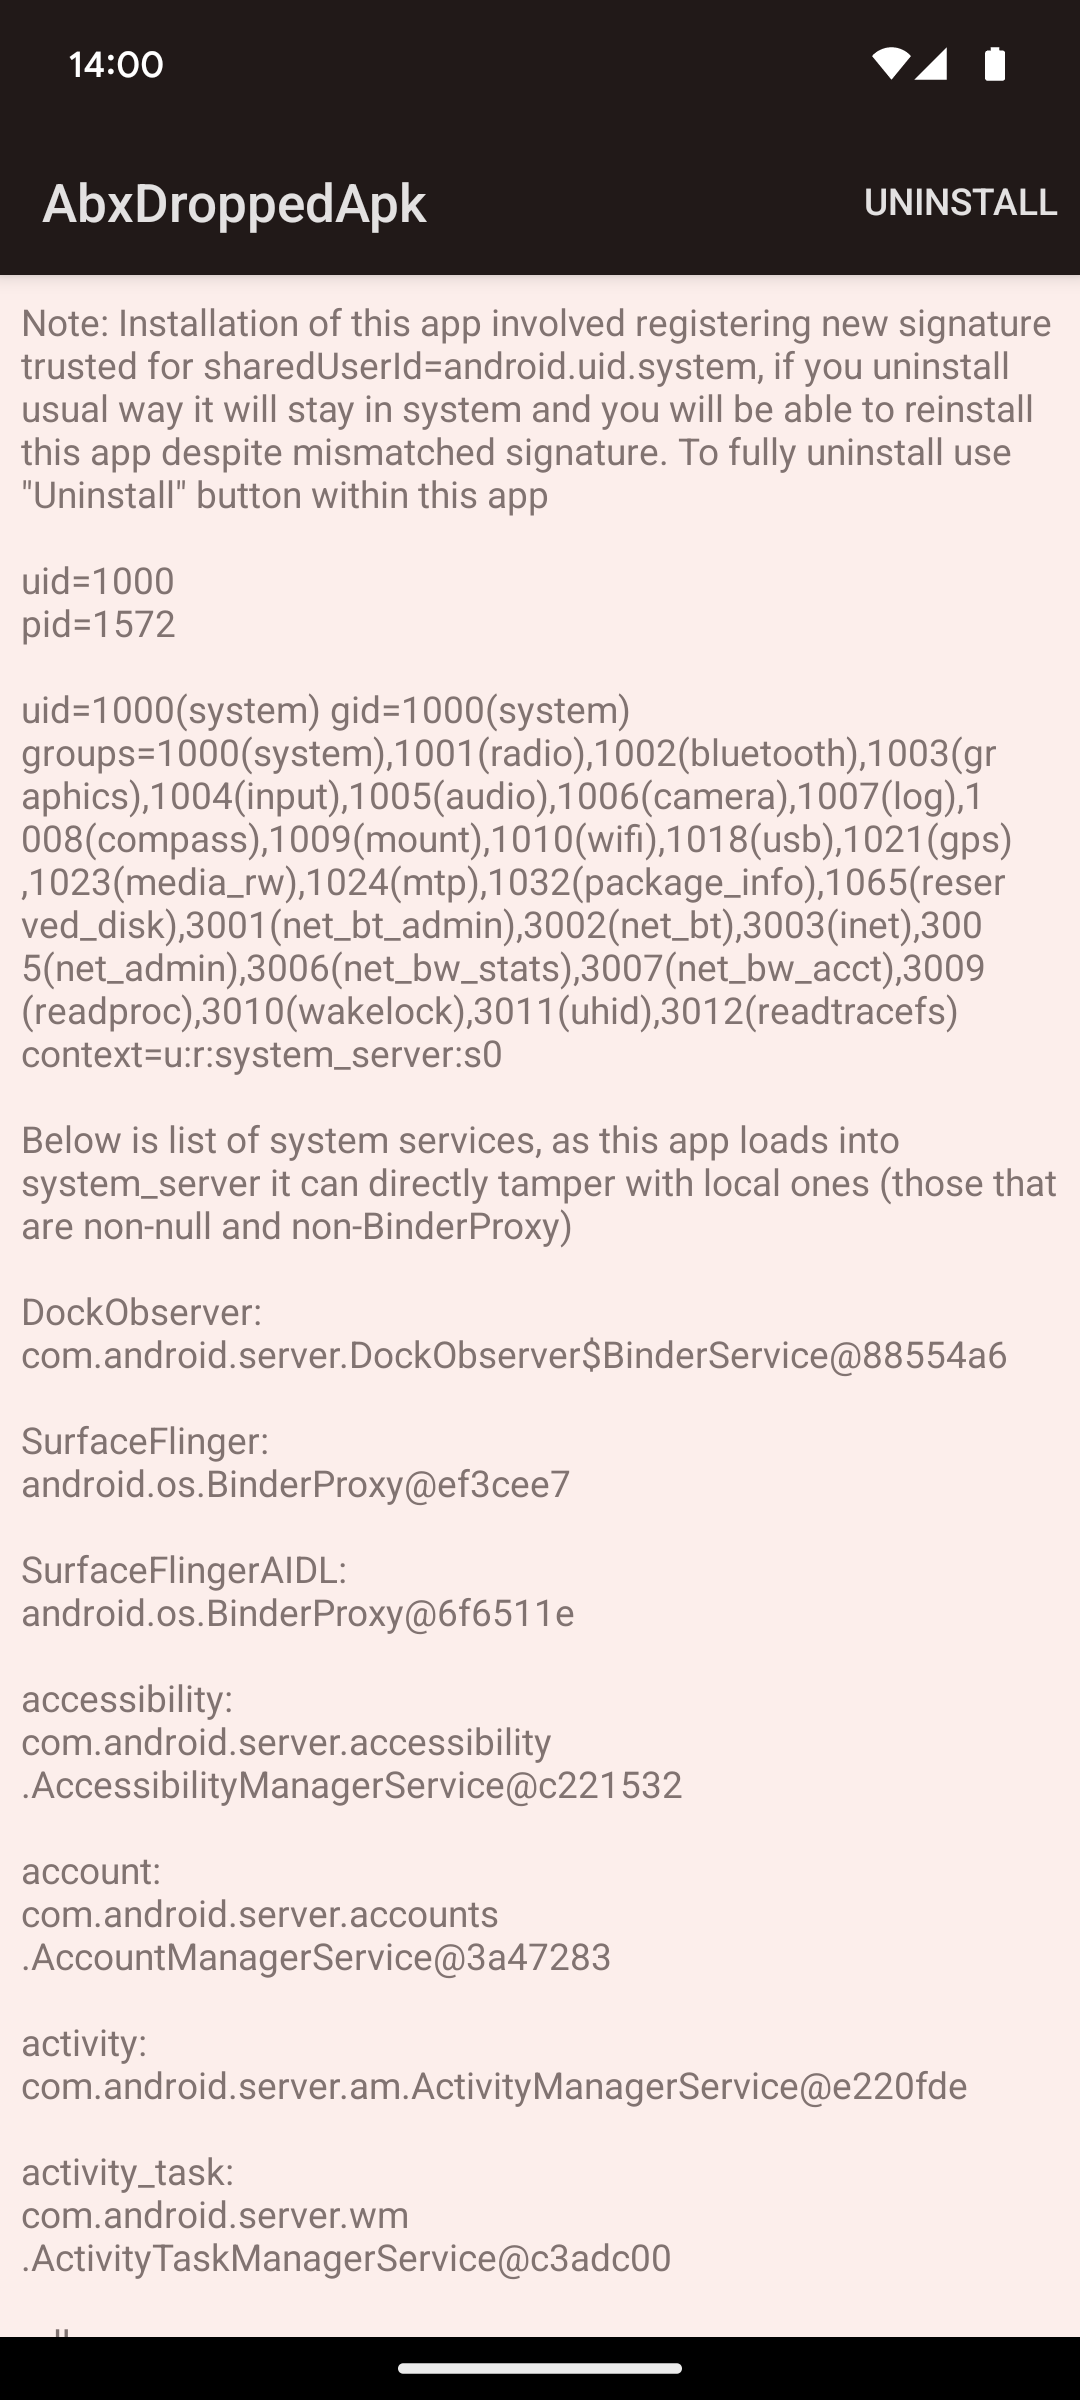 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 bhavyakcwestern/hacking-pdf.js-vulnerability
CVE-2024-4367
 taiyou-tw/cve-2024-40445_cve-2024-40446
This repository serves as the public reference for CVE-2024-40445 and CVE-2024-40446. Both vulnerabilities impact MimeTeX, an open-source software…
 ptrstr/cve-2024-32830-poc
PoC code to download files with CVE-2024-32830
 funcid/cve-2024-38828
PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…
 jaloon/spring-webmvc5
Fork spring-webmvc 5.3.39 to fix CVE-2024-38816, CVE-2024-38819