

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
81.3k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
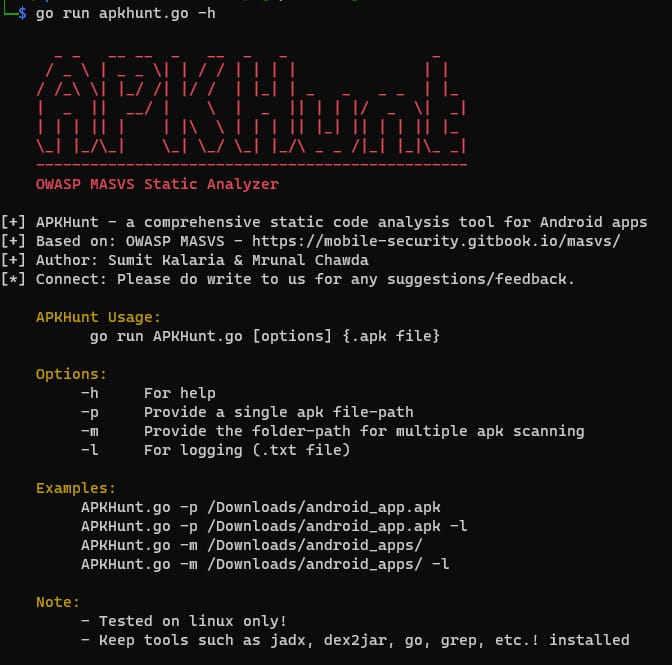 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 zerowang030221/quantum-algorithm-for-elliptic-curve-discrete-logarithms-with-space-efficient-point-addition
Qiskit-based resource estimation framework for space-efficient quantum modular inversion and affine point-addition circuits used in elliptic-curve…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 colton1skees/dna
LLVM based static binary analysis framework
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 trinadh465/frameworks_base_aosp10_r33_cve-2023-21284
Android framework patch for CVE-2023-21284, addressing a security vulnerability in AOSP 10.
 trinadh465/platform_frameworks_base_cve-2023-21288
Android platform framework repository containing a patch or analysis for CVE-2023-21288, a vulnerability in the Android framework.
 trinadh465/platform_frameworks_base_cve-2023-21281
Android platform framework patch for CVE-2023-21281, addressing a security vulnerability in the Android framework.
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…