nono
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
ai-securitycloud-securitycode-analysis+8
nolabs-ai/nonoagent runtime security - zero trust, zero setup, zero latency agent sandboxing
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 jaytarr-geo/nextjs-lodash-cve-2025-13465-repro
Reproduction environment for CVE-2025-13465, demonstrating a vulnerability in Next.js applications using Lodash. Provides a minimal setup to test and…
 mbanyamer/cve-2026-25546-godot-mcp-0.1.1-os-command-injection
Proof-of-concept exploit for CVE-2026-25546, demonstrating OS command injection in godot-mcp via malicious projectPath parameter, with Python PoC and…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
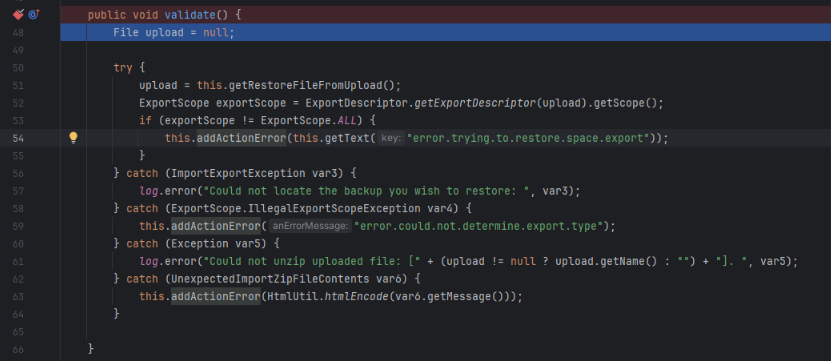 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
 chilit-nl/log4shell-example
The goal of this project is to demonstrate the log4j cve-2021-44228 exploit vulnerability in a spring-boot setup, and to show how to fix it.
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 fairyming/cve-2020-8840
PoC exploit for CVE-2020-8840: JNDI injection leading to remote code execution in FasterXML jackson-databind. Includes environment setup, exploit…