
r2ai
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
ai-assisted-reversingbinary-analysiscode-analysis+5
478
radareorg/r2aiRadare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 hakaioffsec/cve-2026-12191
PoC for CVE-2026-12191
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
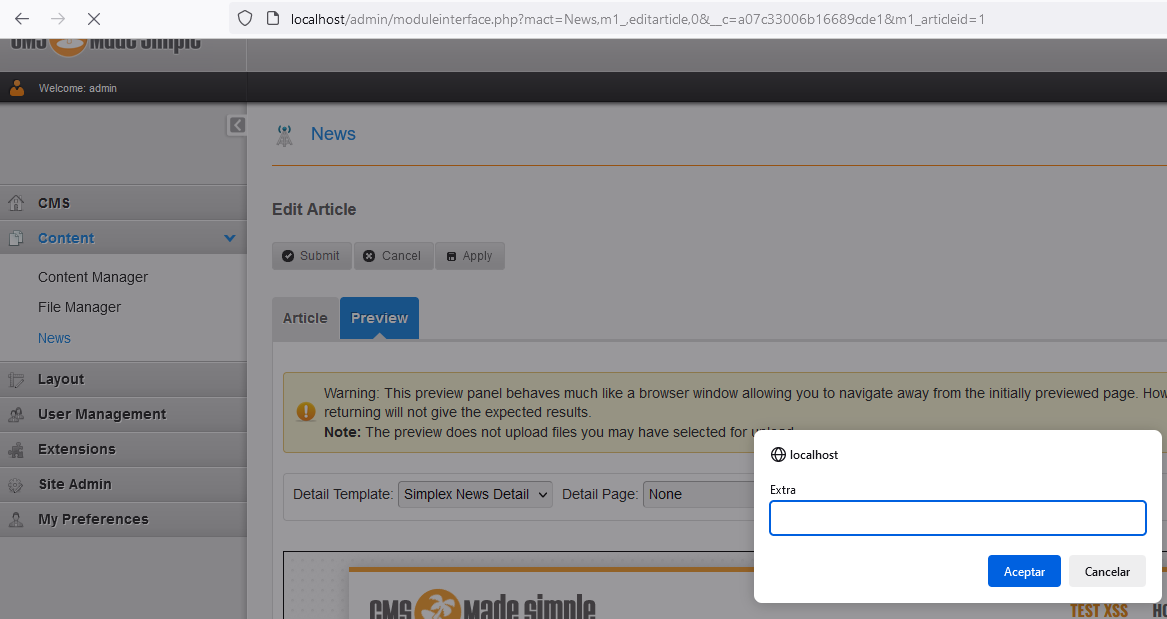 sromanhu/cve-2023-43353-cmsmadesimple-stored-xss---news---extra
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Extrain…
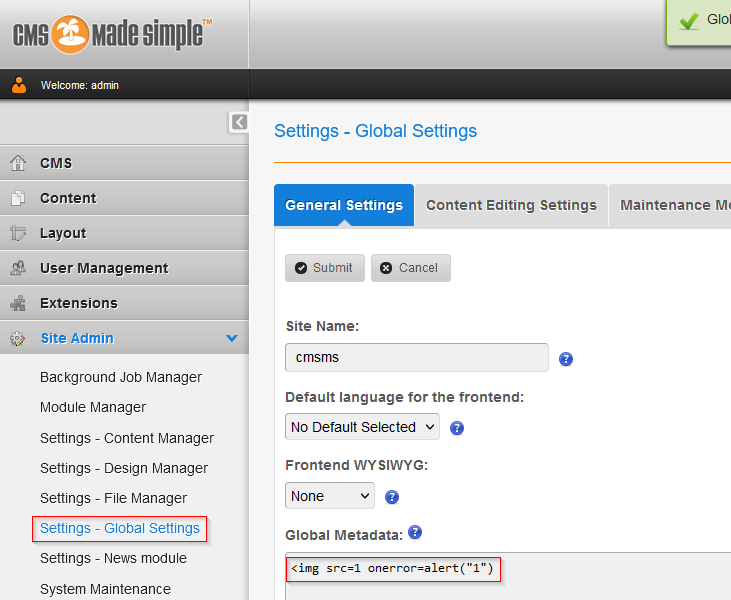 sromanhu/cve-2023-43356-cmsmadesimple-stored-xss---global-settings
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Global…
 sromanhu/cve-2023-43360-cmsmadesimple-stored-xss---file-picker-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Top…
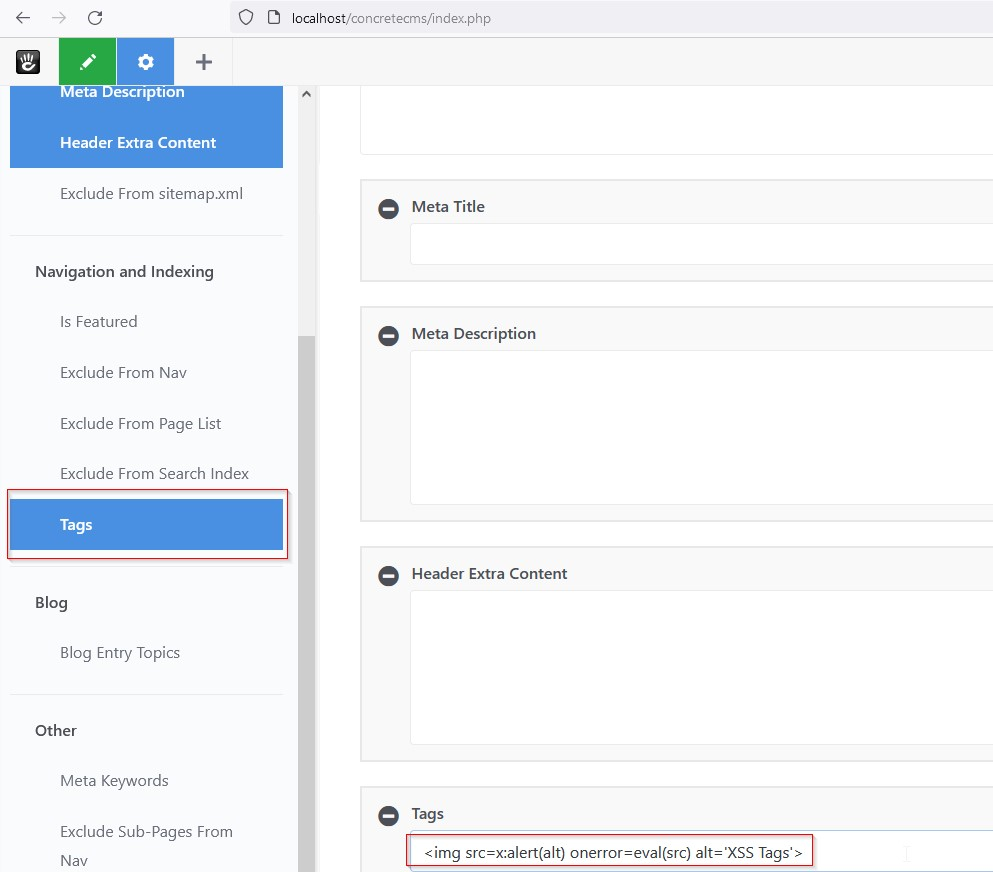 sromanhu/cve-2023-44762_concretecms-reflected-xss---tags
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Tags from…
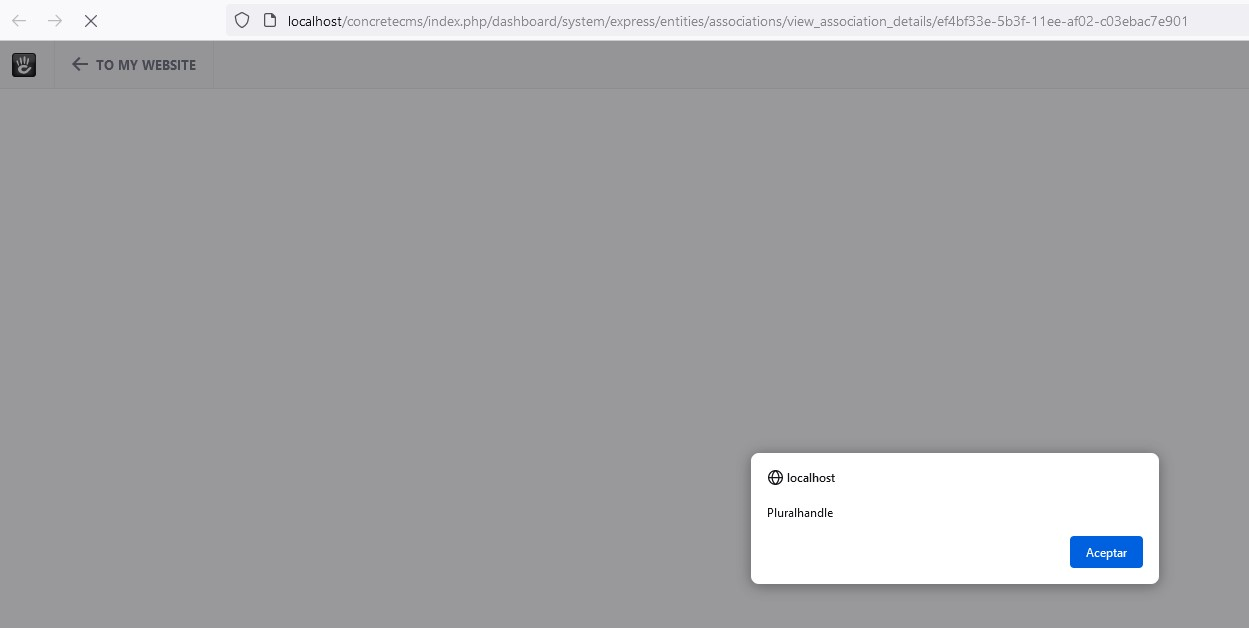 sromanhu/cve-2023-44765_concretecms-stored-xss---associations
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Plural Handle…
 kai-one001/wordpress-news-and-blog-designer-bundle-cve-2025-14502
WordPress的News and Blog Designer Bundle插件在1.1及之前所有版本中,存在通过template参数导致的本地文件包含漏洞。该漏洞使得未经身份验证的攻击者能够包含并执行服务器上的任意.php文件,从而运行这些文件中的任何PHP代码。在允许上传和包含.php文件类型…
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 cybercrowcc/cve-2024-48990
Technical analysis and proof-of-concept for CVE-2024-48990, a privilege escalation vulnerability in needrestart allowing local attackers to execute…
 randomrobbiebf/cve-2024-10516
Swift Performance Lite <= 2.3.7.1 - Unauthenticated Local PHP File Inclusion via 'ajaxify'
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 fr4nkxixi/cve-2021-26871_poc
Proof-of-concept exploit for CVE-2021-26871, a type confusion vulnerability in Windows WalletService's PROPVARIANT handling, enabling local privilege…