
o1js-scan
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
code-analysiscryptographydefensive-tools+5
3
auditinfra-io/o1js-scanDependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 mhtsec/cve-2026-84645
Jenkins PersistenceRoot Deserialization RCE (SECURITY-3972) — PoC & analysis. Requires Item/Configure; affects weekly <= 2.579 / LTS <= 2.568.2
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 grishinpv/cve-2026-31431-old-python
Provides a ctypes wrapper for the splice syscall to enable exploitation of CVE-2026-31431 on Python versions below 3.10, tested on Python 3.7.3.
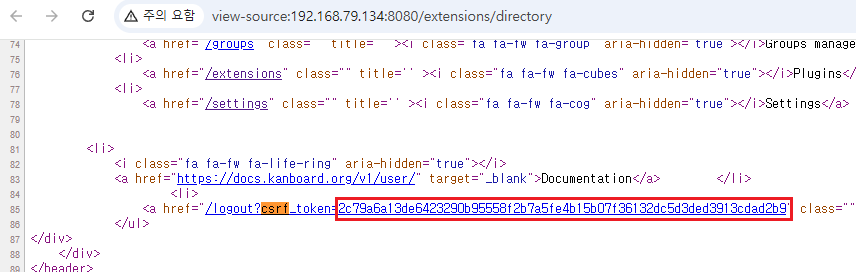 drkim-dev/cve-2026-25924
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…
 bilalclicksafe/cve-2025-60595
SPH Engineering UgCS 5.13.0 is vulnerable to Arbitary code execution. This is the public refrence to be used on CVE site
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…