

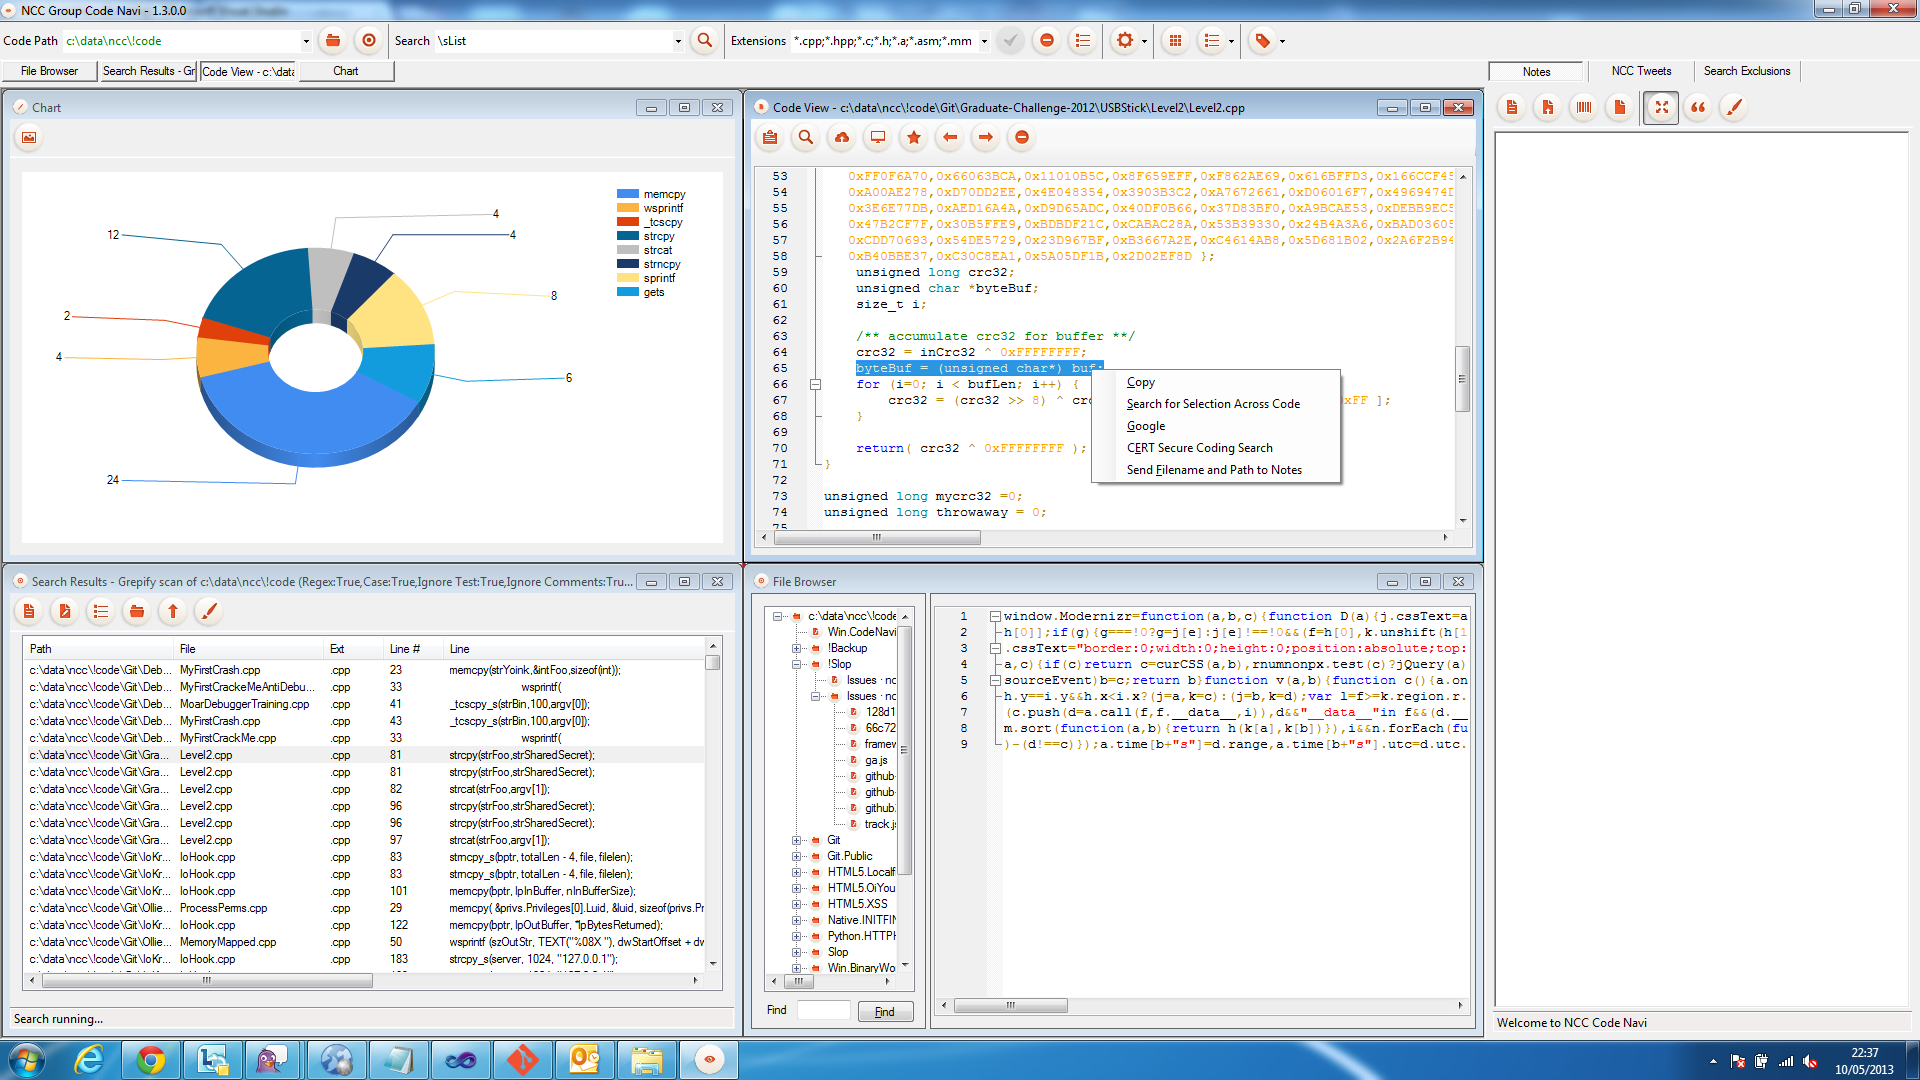
 nccgroup/ncccodenavi
NCC Code Navigator
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 learner202649/cve-2026-47102-poc
The code for personally reproducing the corresponding vulnerability
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
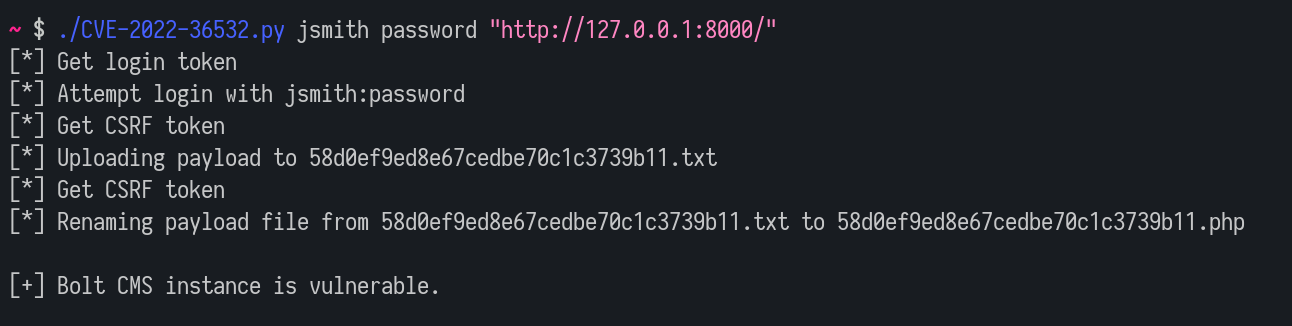 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 ptrstr/cve-2025-4524
CVE-2025-4524 - Unauthenticated madara-core Wordpress theme LFI
 open-flaw/cve-2025-12758
Detailed CVE-2025-12758 disclosure with PoC demonstrating Unicode variation selector bypass in validator.js isLength(), including root cause…
 morrisel/cve-2023-26136
This repository contains a solution for the CVE-2023-26136 vulnerability.
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 trickstersec/cve-2019-5420
Exploit for the Rails CVE-2019-5420
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
 razi-interactive/claude-project-scanner
Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 shoucheng3/apache__jspwiki_cve-2019-10078_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…
 d0n601/cve-2025-9216
StoreEngine – Powerful WordPress eCommerce Plugin for Payments, Memberships, Affiliates, Sales & More <= 1.4.0 - Authenticated (Subscriber+)…
 d0n601/cve-2025-12973
S2B AI Assistant – ChatBot, ChatGPT, OpenAI, Content & Image Generator <= 1.7.7 - Authenticated (Editor+) Arbitrary File Upload