
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
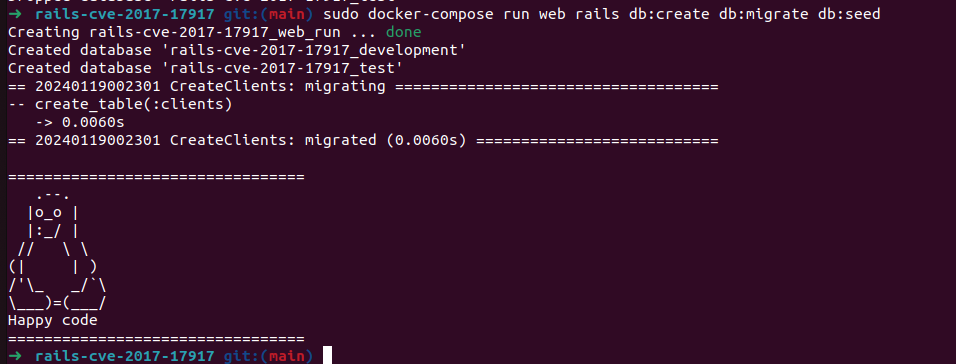 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 gui/legacy-rails-cve-2020-5267-patch
Patch CVE-2020-5267 for Rails 4 and Rails 3
 phusion/rails-cve-2012-5664-test
Demo app showing how the Rails CVE-2013-5664 vulnerability works.
 cyberdefenseinstitute/poc_cve-2016-2098_rails42
A PoC of CVE-2016-2098 (rails4.2.5.1 / view render)
 trickstersec/cve-2019-5420
Exploit for the Rails CVE-2019-5420
 ztgrace/cve-2019-5418-rails3
Rails 3 PoC of CVE-2019-5418
 danielhemmati/cve-2016-2098-my-first-exploit
This exploit is remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data
 debalinax64/cve-2016-2098
CVE-2016-2098 - POC of RCE Ruby on Rails: Improper Input Validation (CVE-2016-2098) in bash. Remote attackers can execute arbitrary Ruby code by…
 j4k0m/cve-2016-2098
Remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data.
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 3rg1s/cve-2016-2098
Proof-of-concept exploit for CVE-2016-2098, demonstrating remote Ruby code execution through Rails render method abuse; intended for security testing…
 0xeval/cve-2015-3224
Ruby on Rails Web Console (v2) Whitelist Bypass Code Execution implementation in Python
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
