
CVE-2026-33980
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
cloud-securitycode-analysisdatabase-security+3
romain-deperne/cve-2026-33980KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 romain-deperne/cve-2026-32247
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1
 toanln-cov/cve-2026-76564
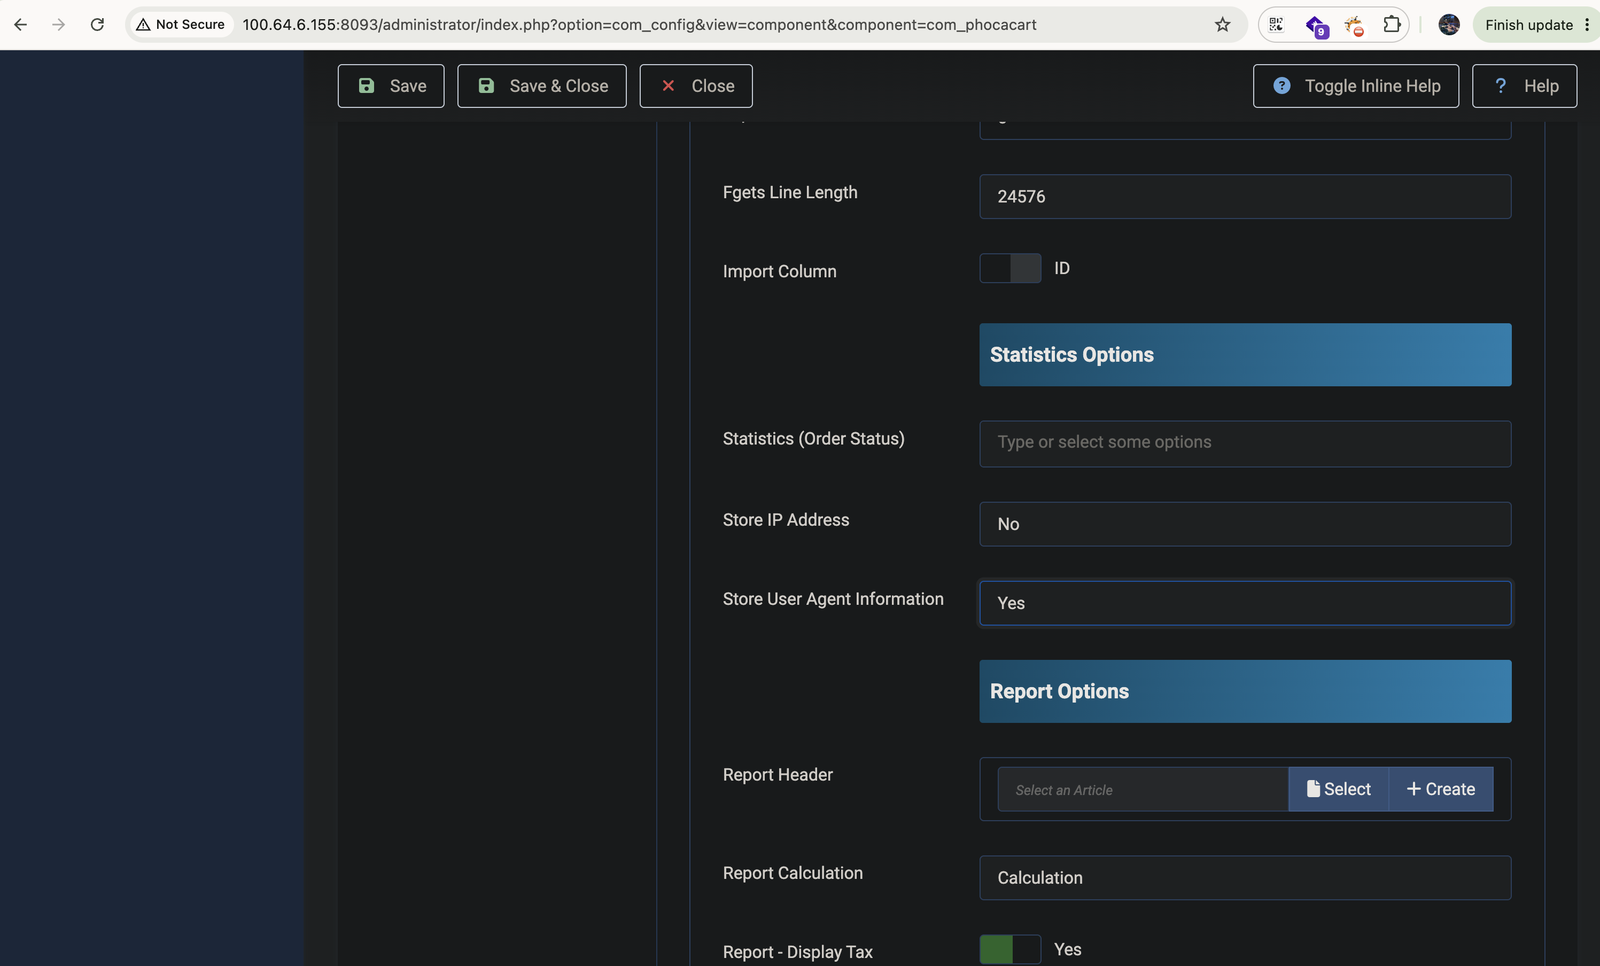
Stored XSS via User-Agent in Admin Order View in PhocaCart
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
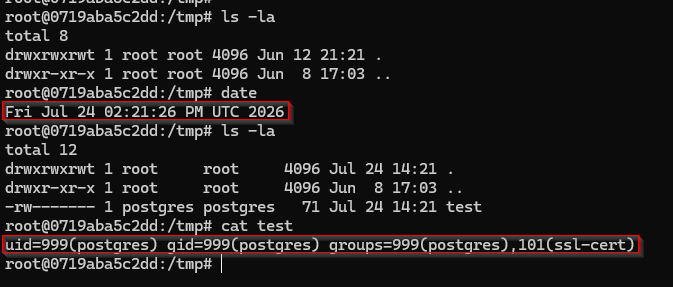 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 loic-houchi/django-faille-cve-2025-57833_test
Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
 shanika04/hibernate-orm
CVE-2019-14900
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d