TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Cloud native secrets management for developers - never leave your command line for secrets.

Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…

Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.

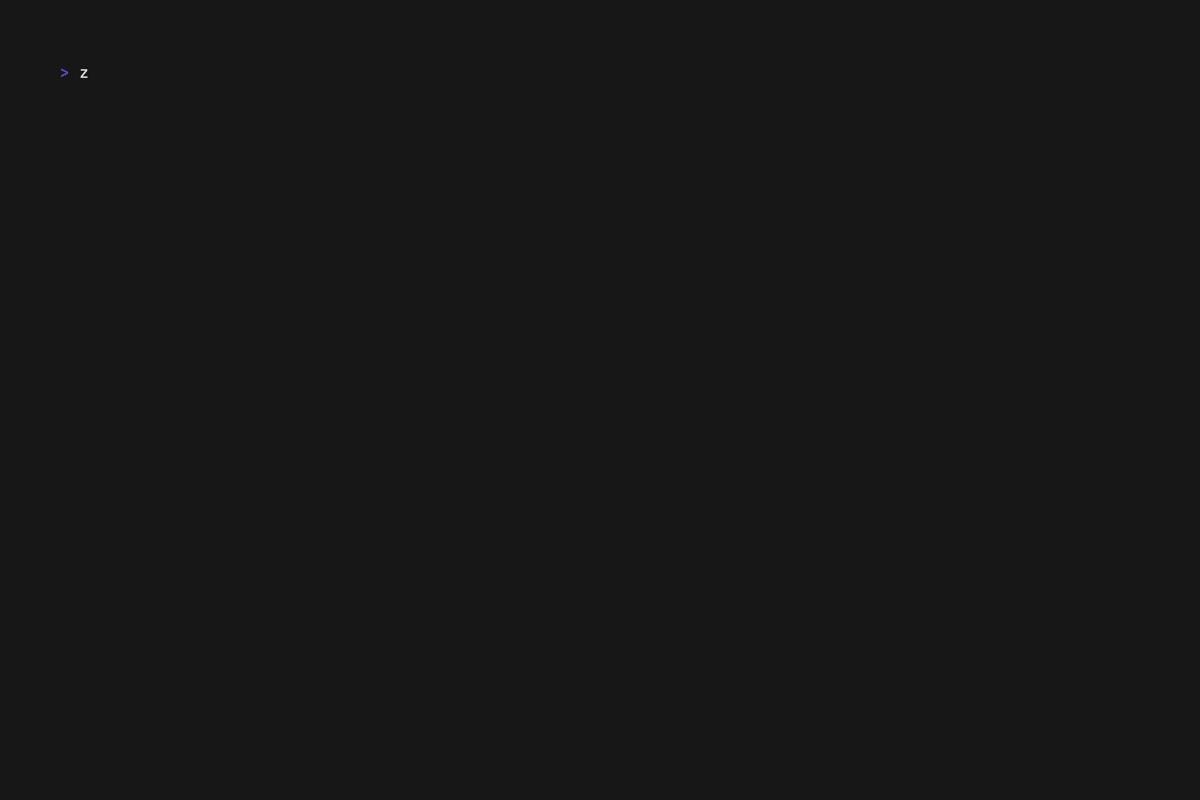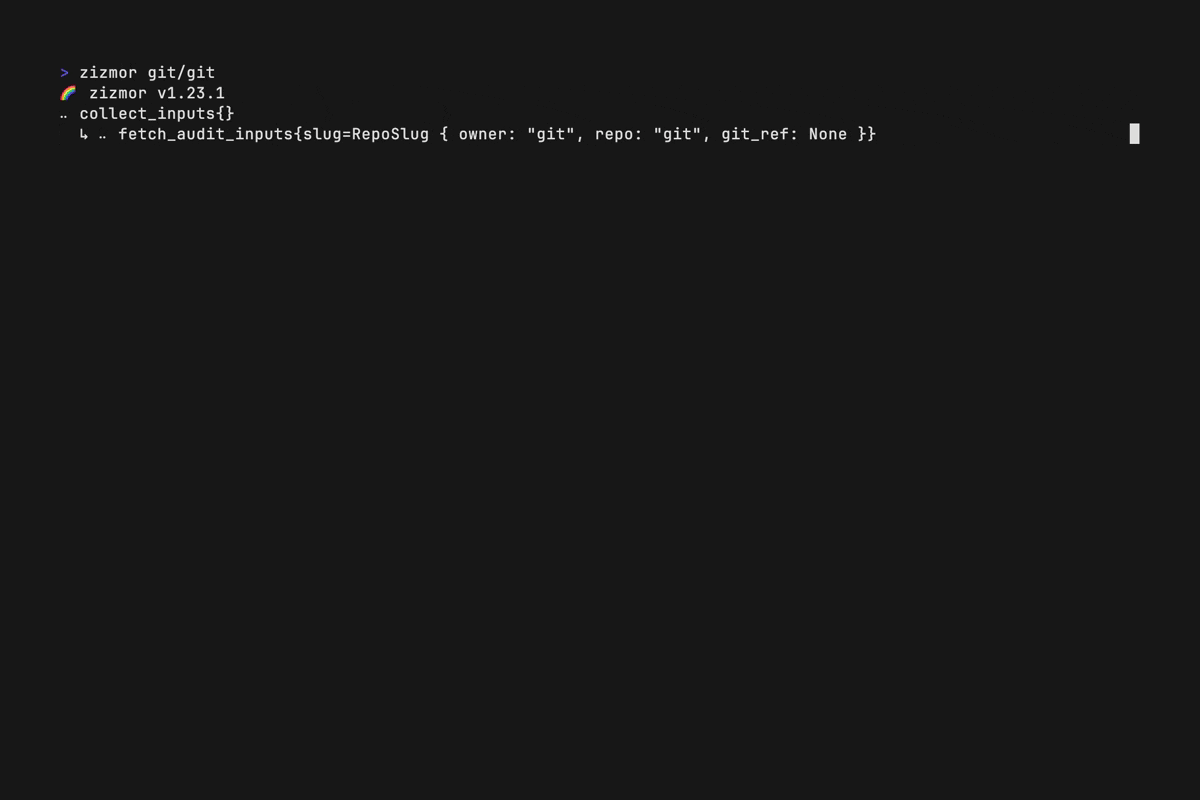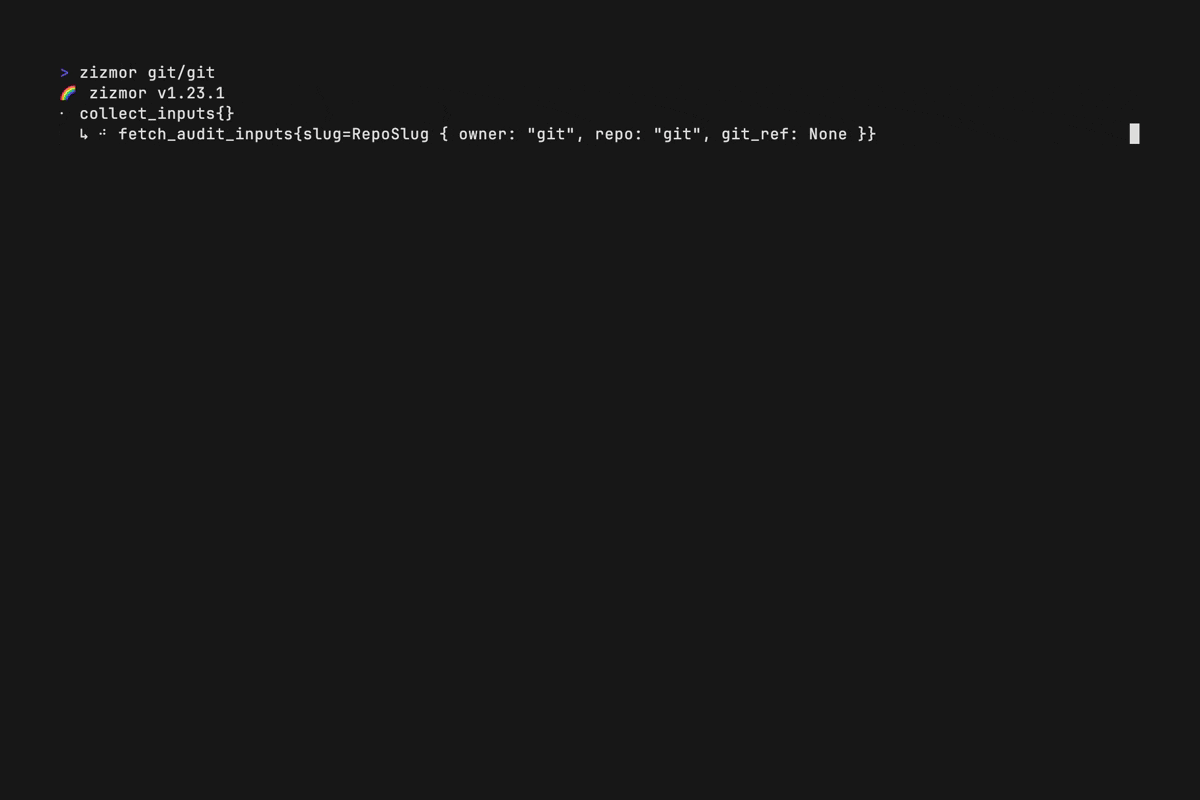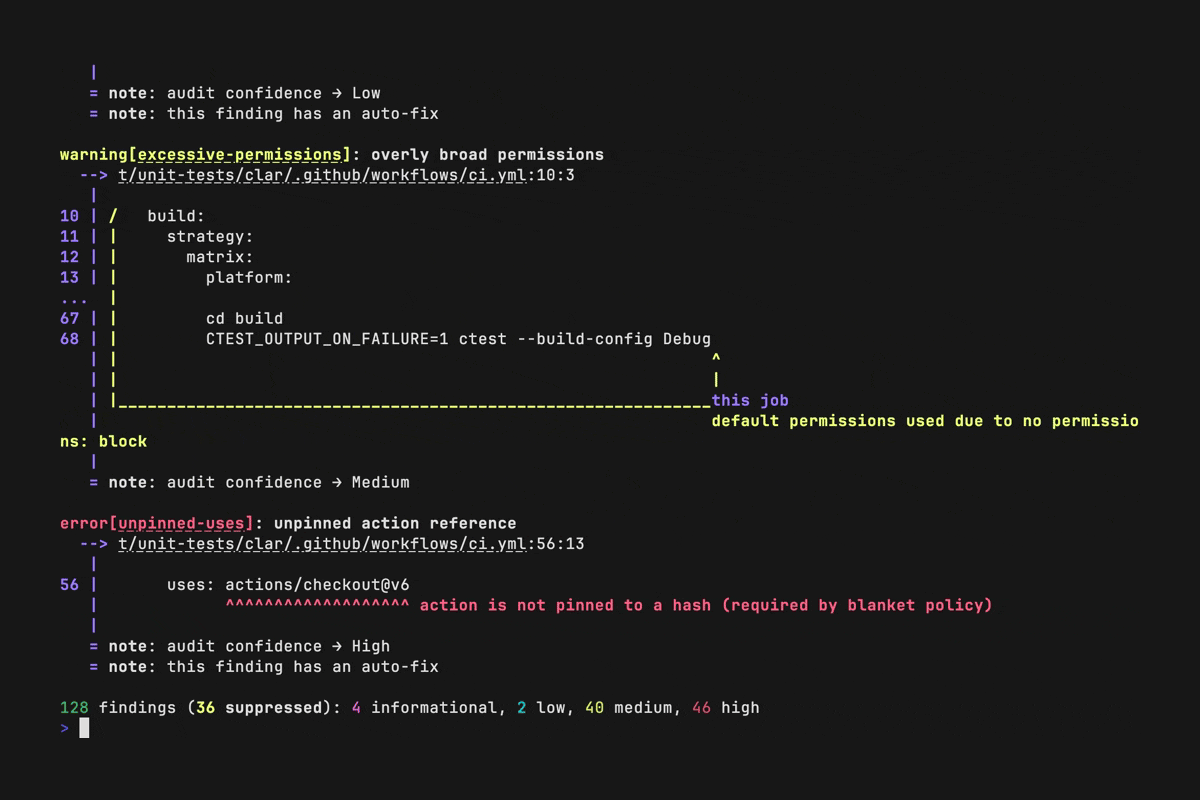
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…

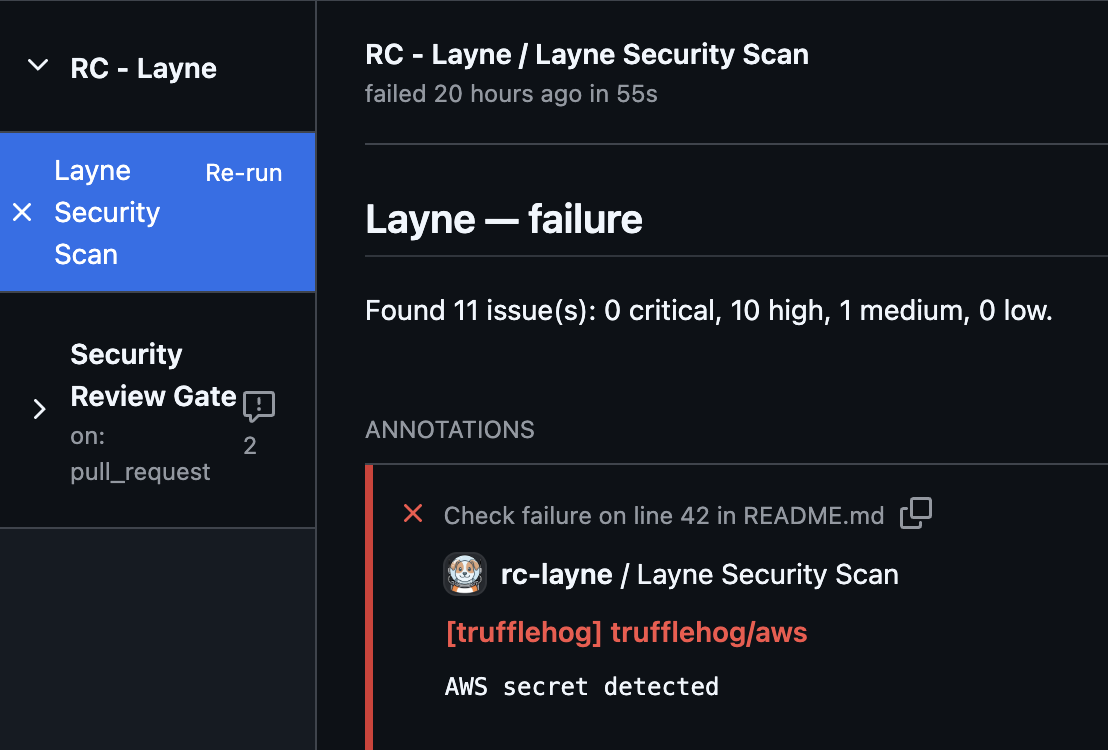
A doggo that helps look for security issues in your repositories.

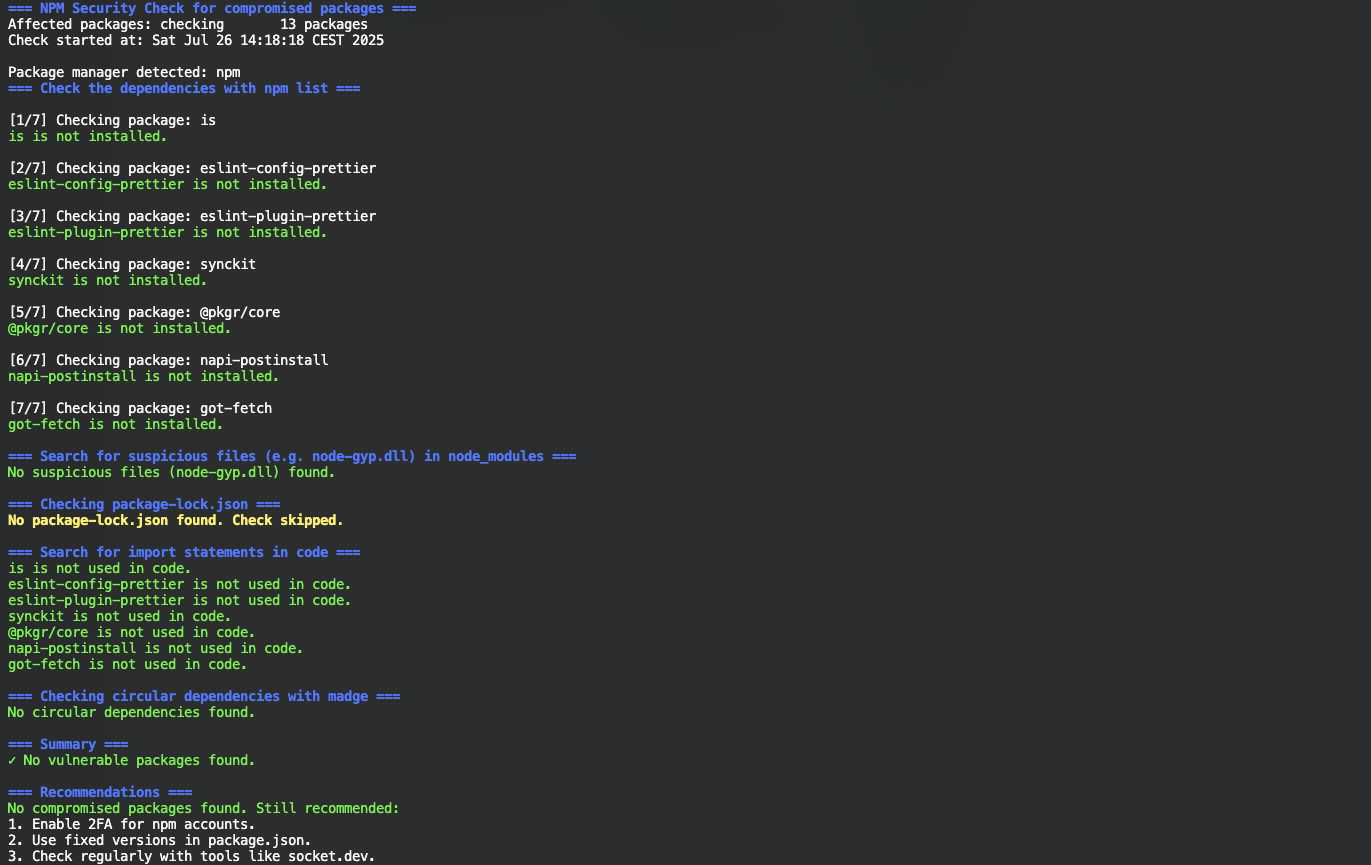
Checks projects for compromised packages, suspicious files, and import statements.

CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…

Static security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.

Open-source secret scanner in Rust

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…


safely install npm packages by auditing them pre-install stage

Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…

Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.

Bash script to detect CVE-2025-55182 (React2Shell) and credential exposure in Next.js projects. Zero dependencies.

CLI tool to scan codebases for quantum-vulnerable cryptography

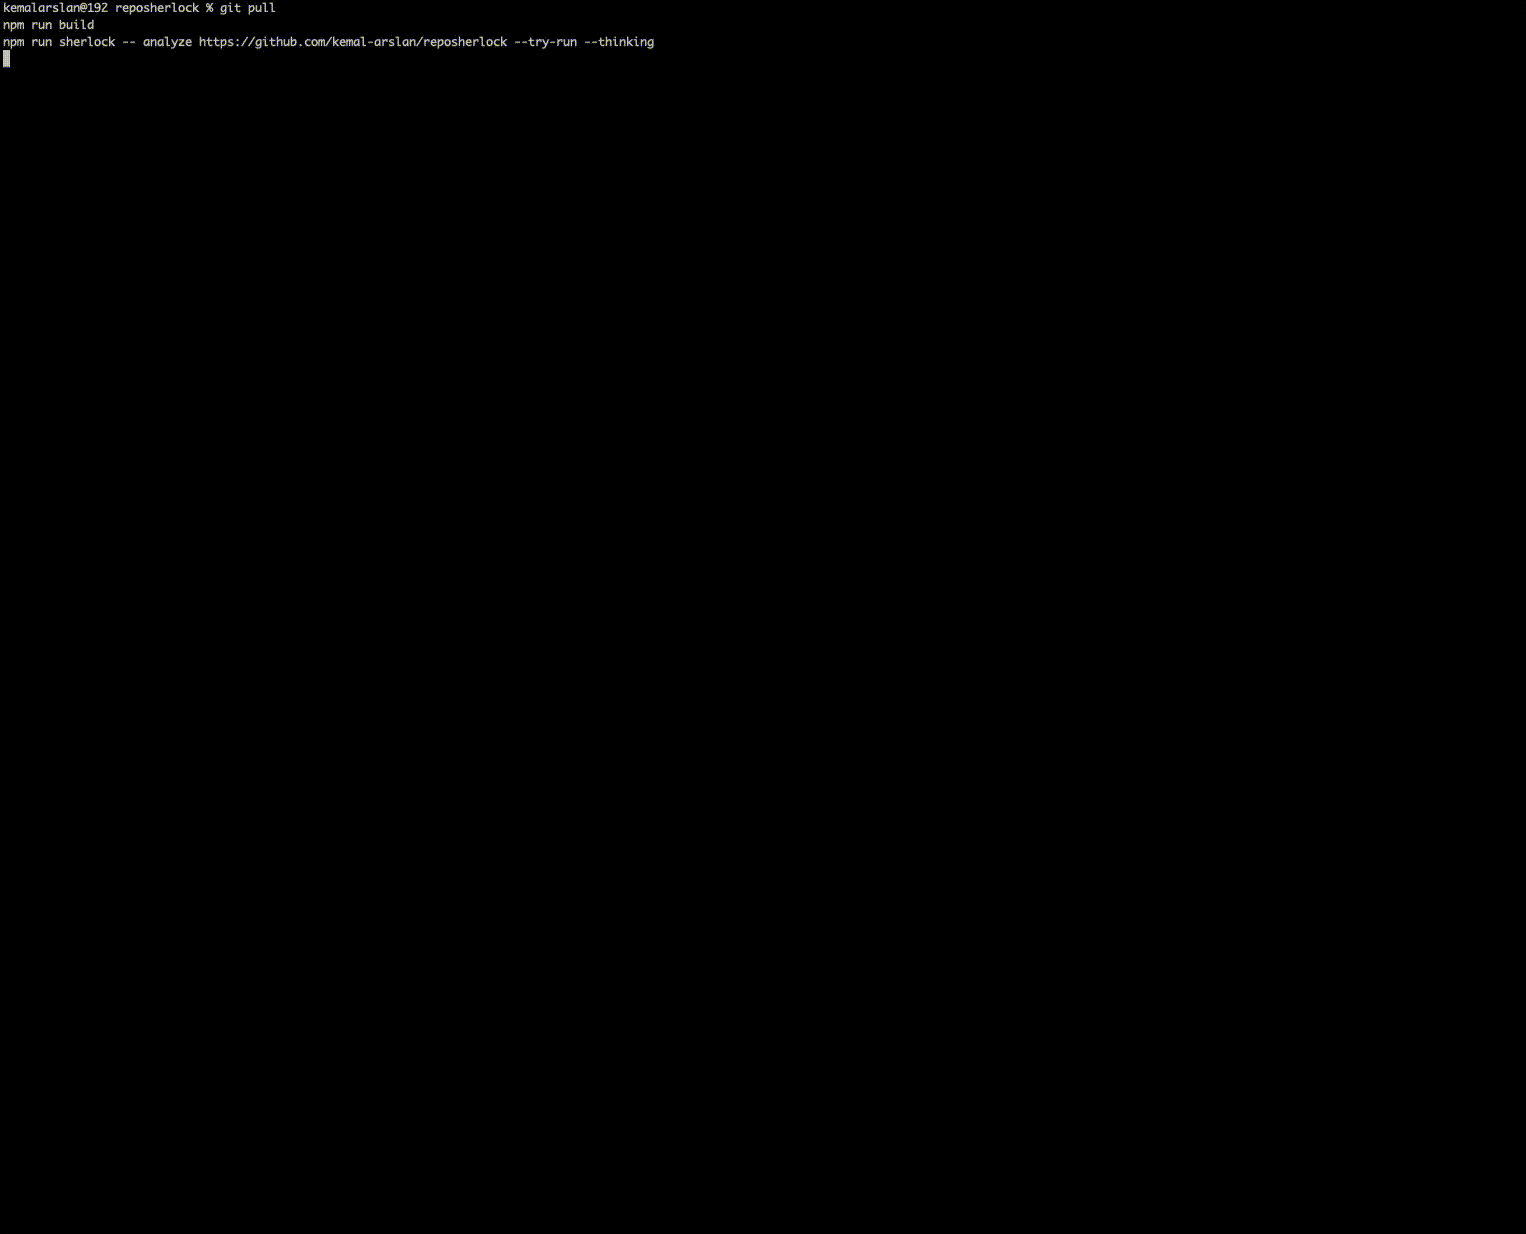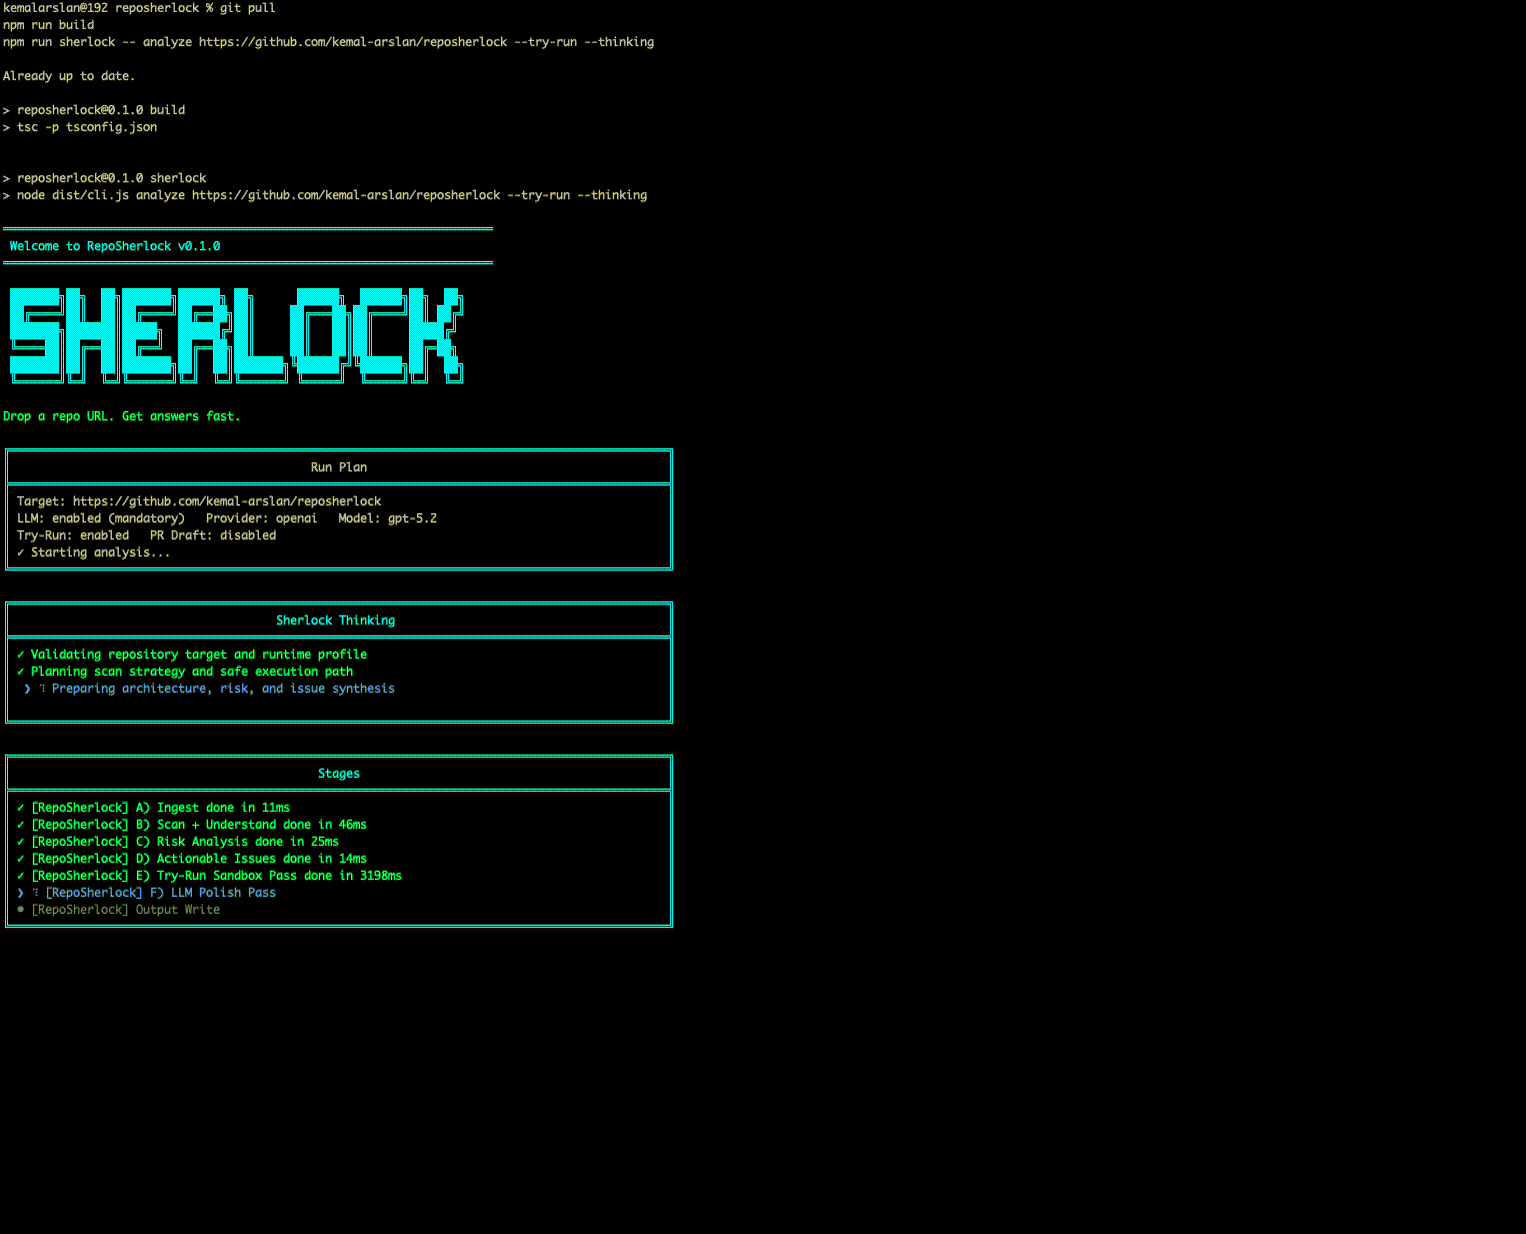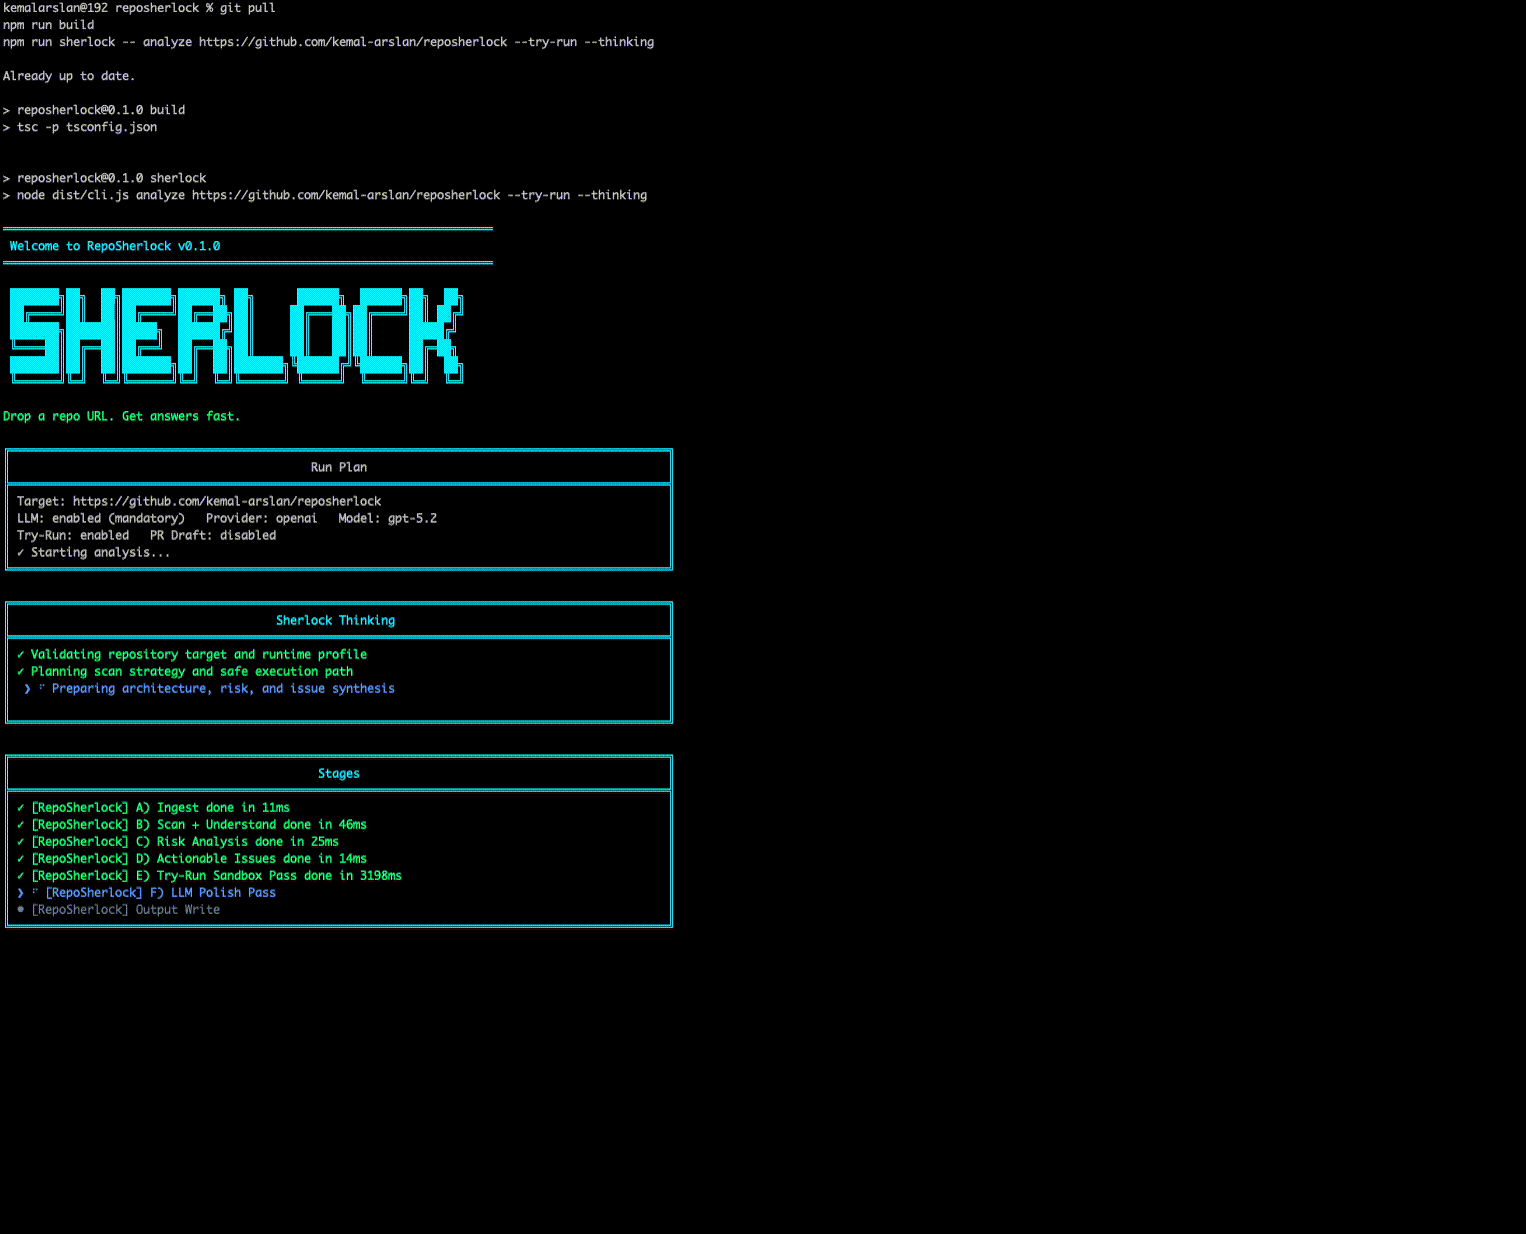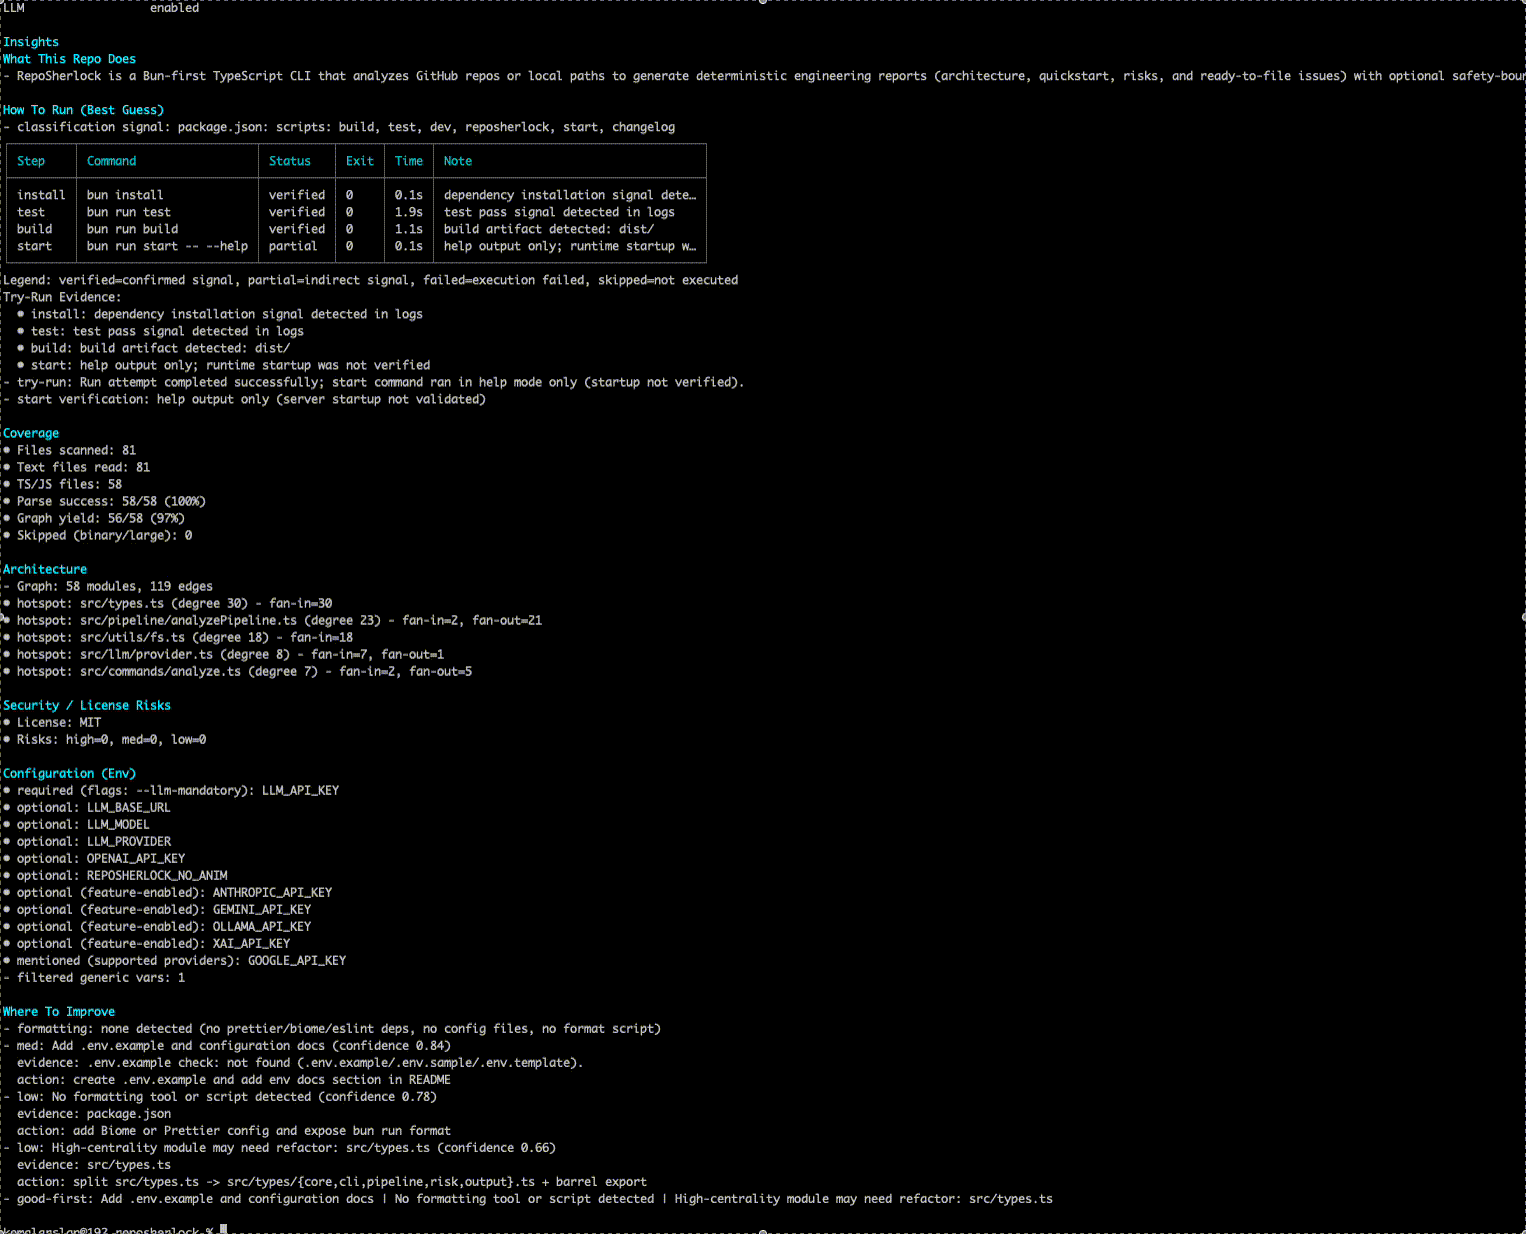
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.