php-5.4-cve-2026-php2shell-patch

Production-ready backported .patch for EOL PHP 5.4,.23 custom 5.x to fix the critical PHP2Shell (OOM) vulnerability (CVE-2026-109618 /…

Production-ready backported .patch for EOL PHP 5.4,.23 custom 5.x to fix the critical PHP2Shell (OOM) vulnerability (CVE-2026-109618 /…

Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…

Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…

Yet another llvm based obfuscator based on goron.

Adversarial image attacks on vision-language web agents, from visual grounding to browser execution

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…

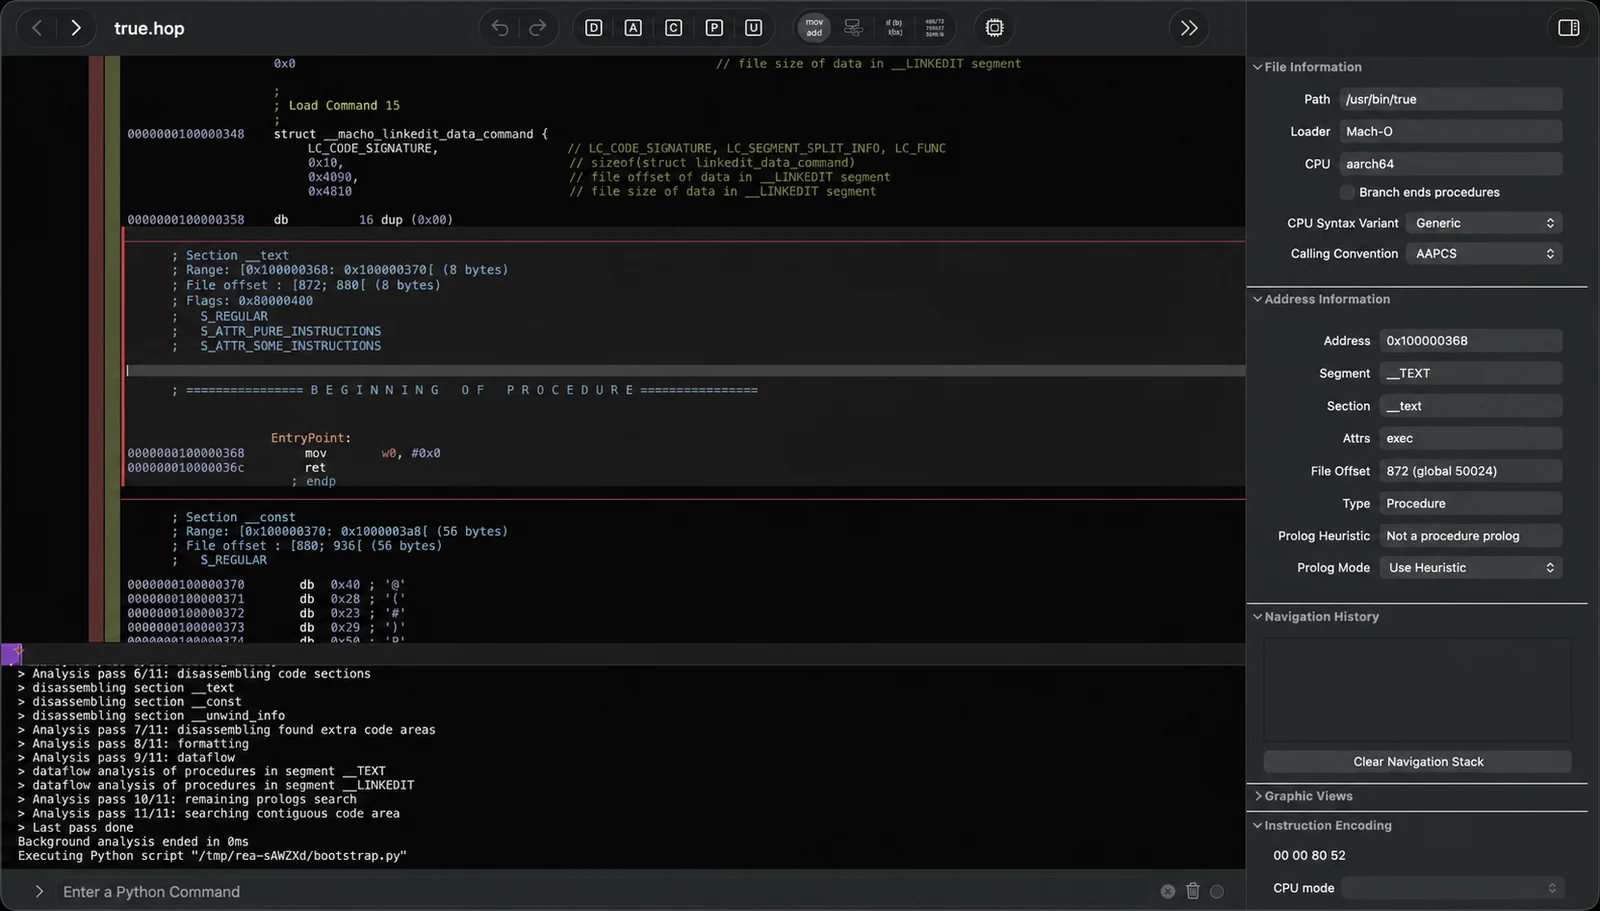
Reverse engineer anything with agents, from app behavior down to native binaries.

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

Pure-Go Java Decompiler and Serialization Operator

A native APK and DEX decompiler written in Rust

The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().

Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…

WooCommerce plugin: safe formula-based product pricing, closing CVE-2026-4001's eval()-based RCE

Provides a ctypes wrapper for the splice syscall to enable exploitation of CVE-2026-31431 on Python versions below 3.10, tested on Python 3.7.3.

Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…