
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
CVE-2026-38192 preview

CVE-2026-38192

GitHubming1700/cve-2026-38192

pluck-CMS-4.7.20-code-injection-vulnerability
code-analysisexploitationpenetration-testing+2
326 days ago
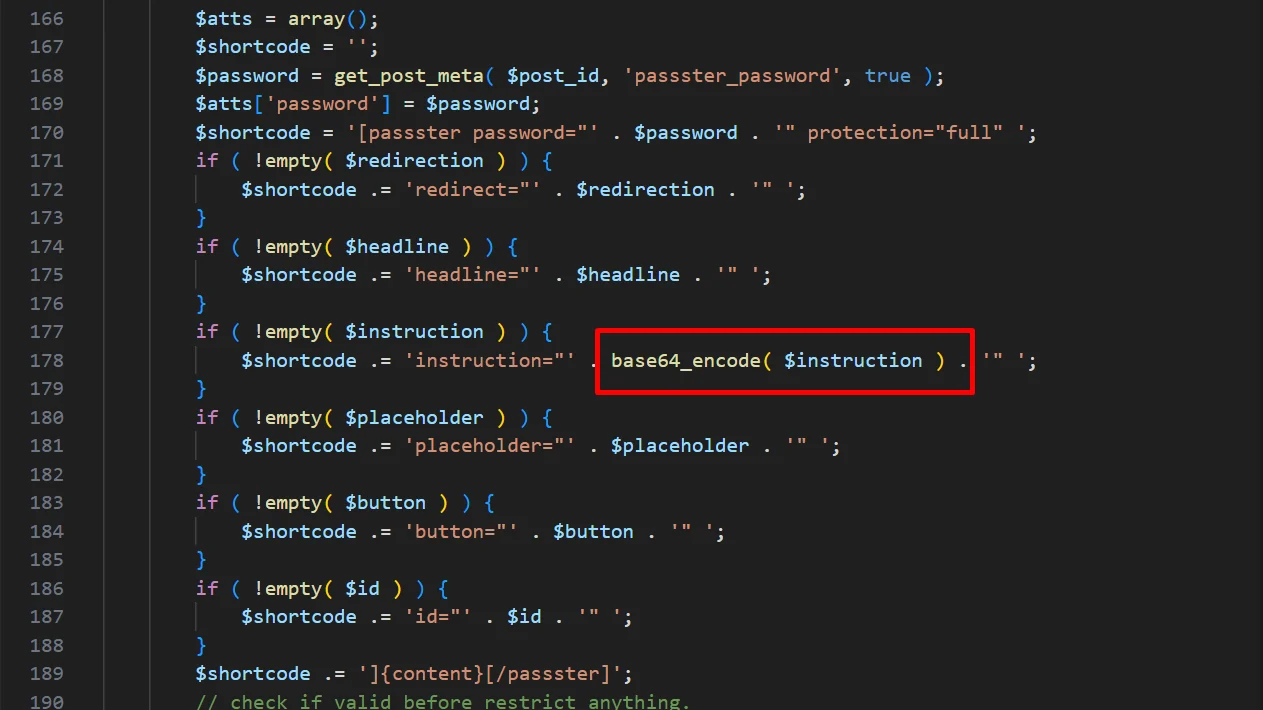
CVE-2025-57926 preview

CVE-2025-57926

GitHubquetuan03/cve-2025-57926

WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
code-analysisexploitationvulnerability-analysis+2
0 years ago
SoliditySecurity preview

SoliditySecurity

GitHubal1ex/soliditysecurity

Solidity Security

code-analysiscurated-resourceseducation+1
35 years ago
rustproofing-linux preview

rustproofing-linux

GitHubnccgroup/rustproofing-linux

Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
binary-exploitationcode-analysiscurated-resources+4
223 years ago
CVE-2026-52832-PoC-exploit-nuclio-dashboard preview

CVE-2026-52832-PoC-exploit-nuclio-dashboard

GitHubmdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard

Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…

code-analysiscontainer-securityexploitation+3
1 month ago
CVE-2024-4577 preview

CVE-2024-4577

GitHubianthinus/cve-2024-4577

Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.

code-analysisexploitationpayload-generation+3
1 year ago
CVE-2025-22710 preview

CVE-2025-22710

GitHubdottak/cve-2025-22710

PoC of CVE-2025-22710

code-analysisexploitationpenetration-testing+2
21 year ago
CVE-2024-5932 preview

CVE-2024-5932

GitHubeqstlab/cve-2024-5932

GiveWP PHP Object Injection exploit
code-analysiseducationexploitation+5
771 year ago
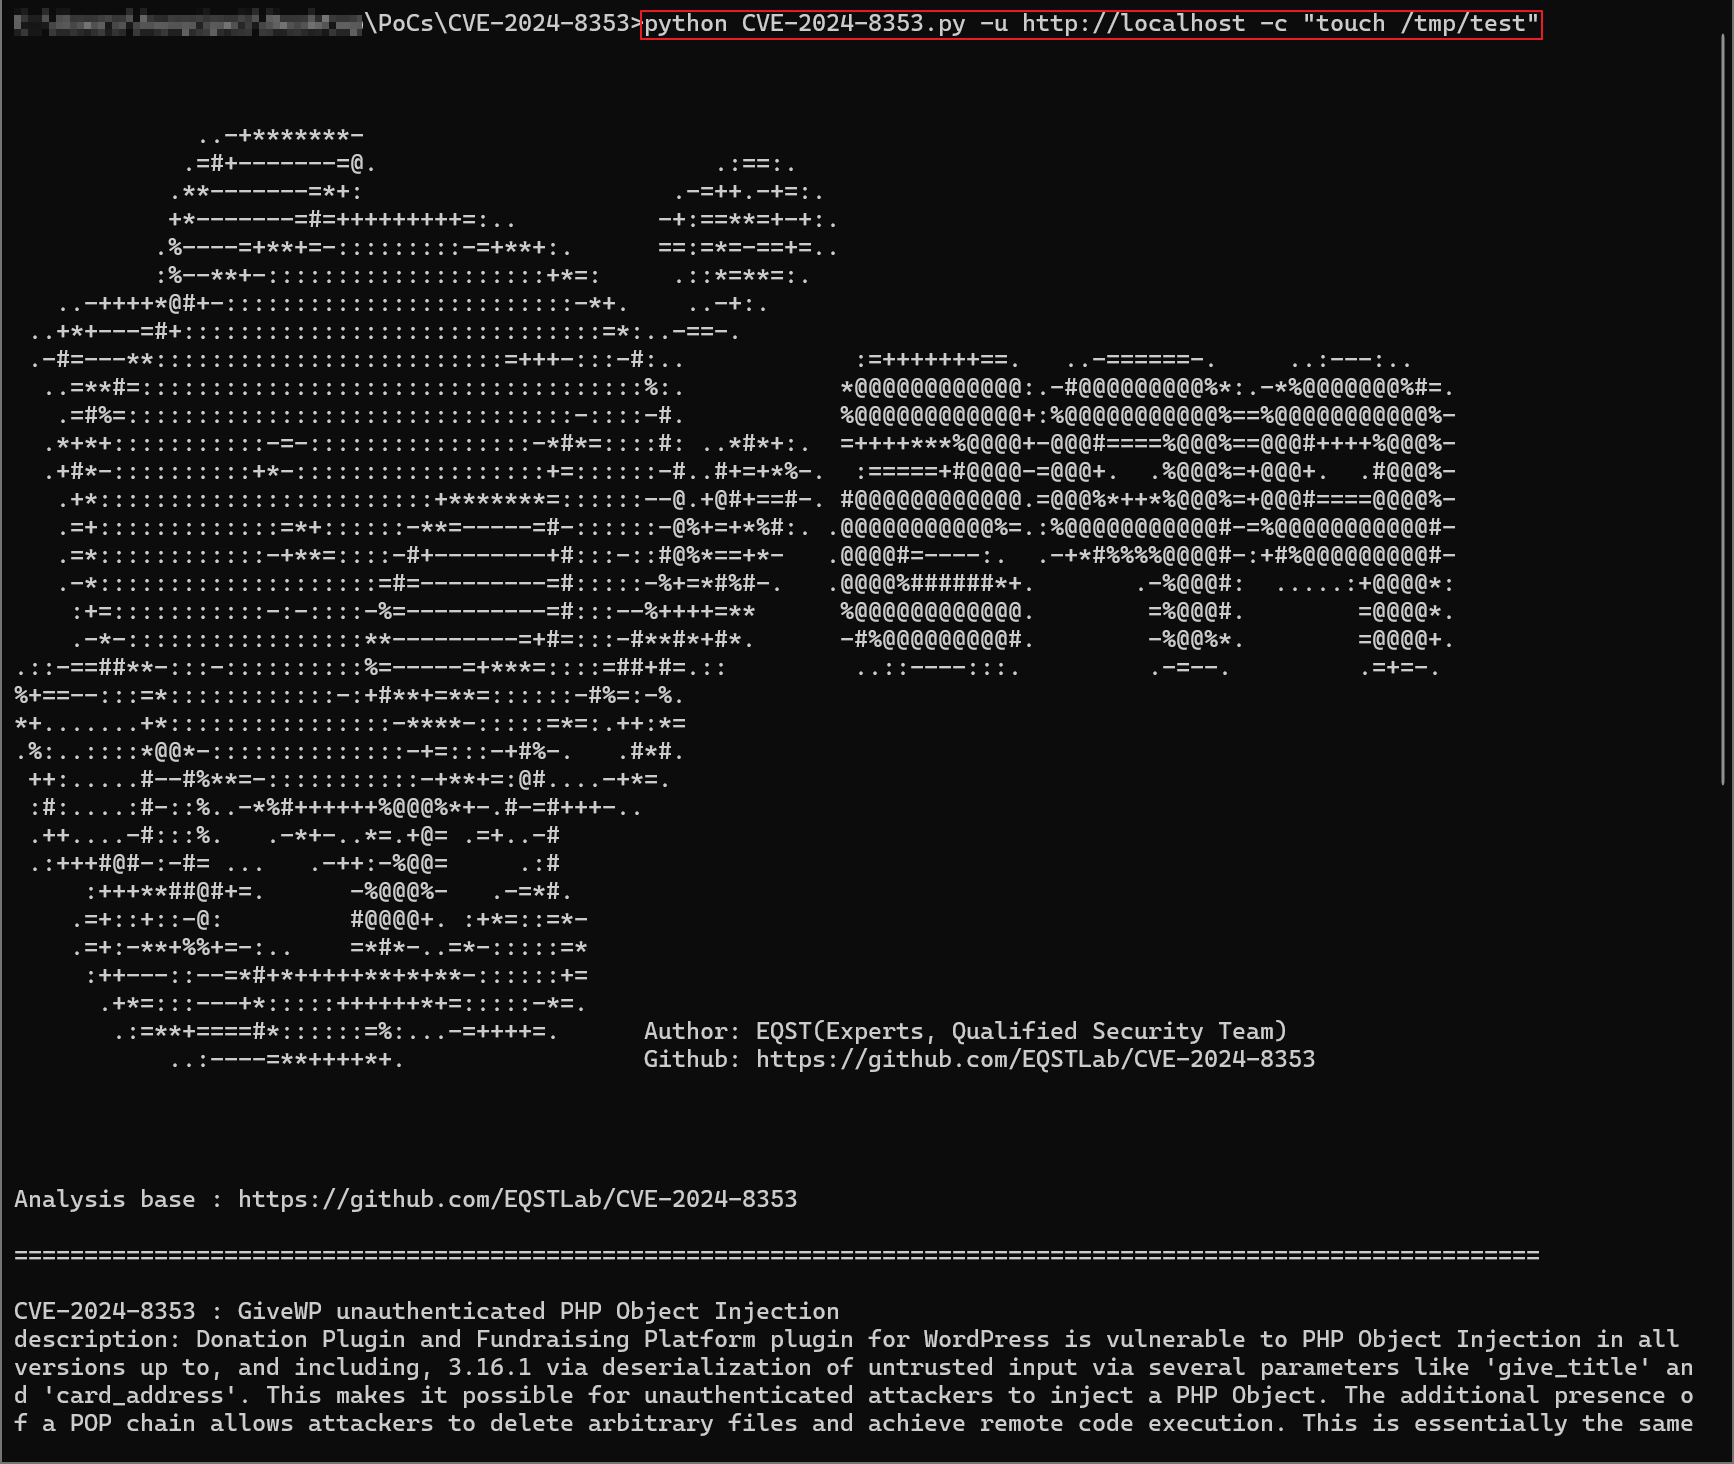
CVE-2024-8353 preview

CVE-2024-8353

GitHubeqstlab/cve-2024-8353

GiveWP PHP Object Injection exploit
code-analysisexploitationpayload-development+3
121 year ago
moodle-rce-calculatedquestions preview

moodle-rce-calculatedquestions

GitHubredteampentesting/moodle-rce-calculatedquestions

Scripts for Analysis of a RCE in Moodle Calculated Questions (CVE-2024-43425)
code-analysiseducationexploitation+3
192 years ago
Ghost-CMS-Code-Injection-Audit-CVE-2026-26980 preview

Ghost-CMS-Code-Injection-Audit-CVE-2026-26980

GitHubkulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980

Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
code-analysisdefensive-toolsincident-response+3
1 month ago
CVE-2026-40217-PoC preview

CVE-2026-40217-PoC

GitHublearner202649/cve-2026-40217-poc

The code for personally reproducing the corresponding vulnerability

code-analysiscontainer-securityeducation+4
4 months ago
CVE-2025-56815 preview

CVE-2025-56815

GitHubxiaoxiaoranxxx/cve-2025-56815

Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
code-analysisexploitationmisconfiguration+3
51 year ago
CVE-2025-4427-CVE-2025-4428 preview

CVE-2025-4427-CVE-2025-4428

GitHubrxerium/cve-2025-4427-cve-2025-4428

Detection for CVE-2025-4427 and CVE-2025-4428
code-analysisdynamic-analysis-sandboxingexploitation+3
11 months ago
CVE-2024-1247-PoC preview

CVE-2024-1247-PoC

GitHubnxploited/cve-2024-1247-poc

Post Saint <= 1.3.1 plugin for WordPress Arbitrary File Upload

code-analysiseducationexploitation+3
1 year ago
CVE-2024-5932 preview

CVE-2024-5932

GitHubnishant-kumar-5173/cve-2024-5932

Proof-of-concept exploit for CVE-2024-5932, a PHP object injection vulnerability in the GiveWP WordPress plugin, enabling unauthenticated remote code…
code-analysiseducationexploitation+5
4 months ago
CVE-2020-14295 preview

CVE-2020-14295

GitHubmrg3ntl3m4n/cve-2020-14295

Proof of Concept for CVE-2020-14295.
code-analysisexploitationpenetration-testing+2
5 years ago
wolfCOSE preview

wolfCOSE

GitHubwolfssl/wolfcose

A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.

code-analysiscryptographyembedded-systems-security+7
768 days ago
Previous12Next