

sast-scan-action
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
api-security-testingcloud-securitycode-analysis+4
offensive360/sast-scan-actionGitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
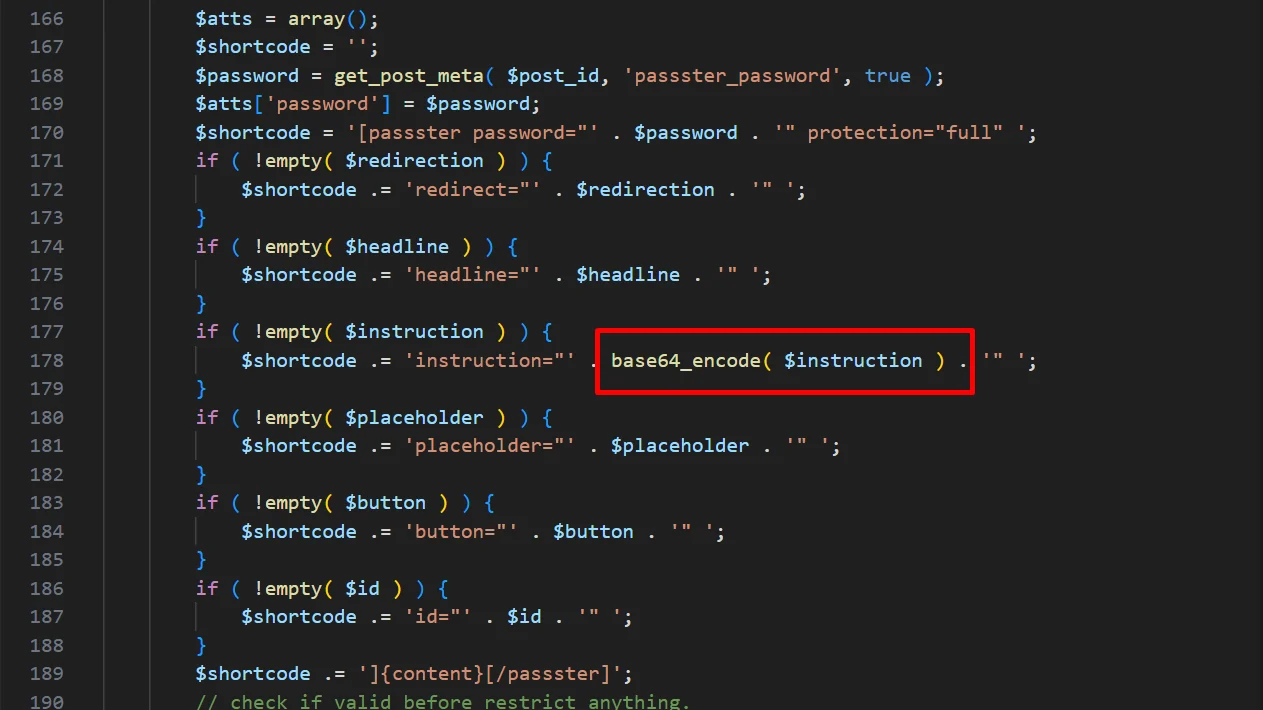 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
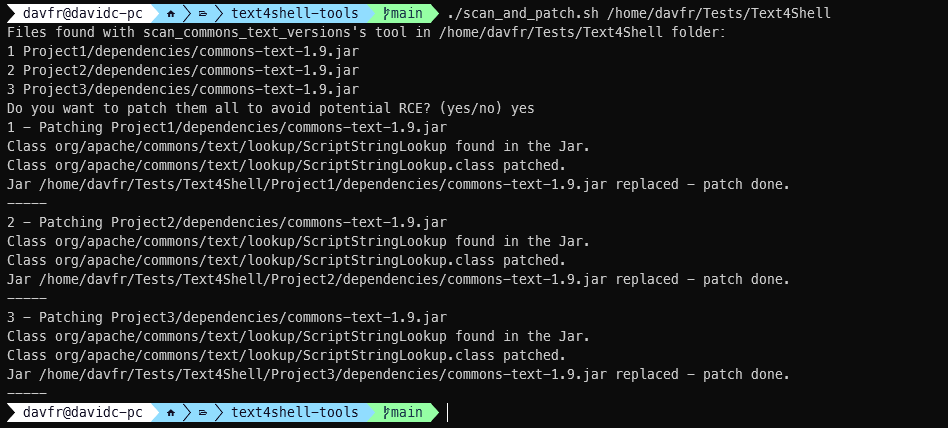 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 lysophavin18/cve-2026-3854-poc
GitHub RCE via X-Stat Push Option Injection
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 dottak/cve-2025-22710
PoC of CVE-2025-22710
 eqstlab/cve-2024-5932
GiveWP PHP Object Injection exploit
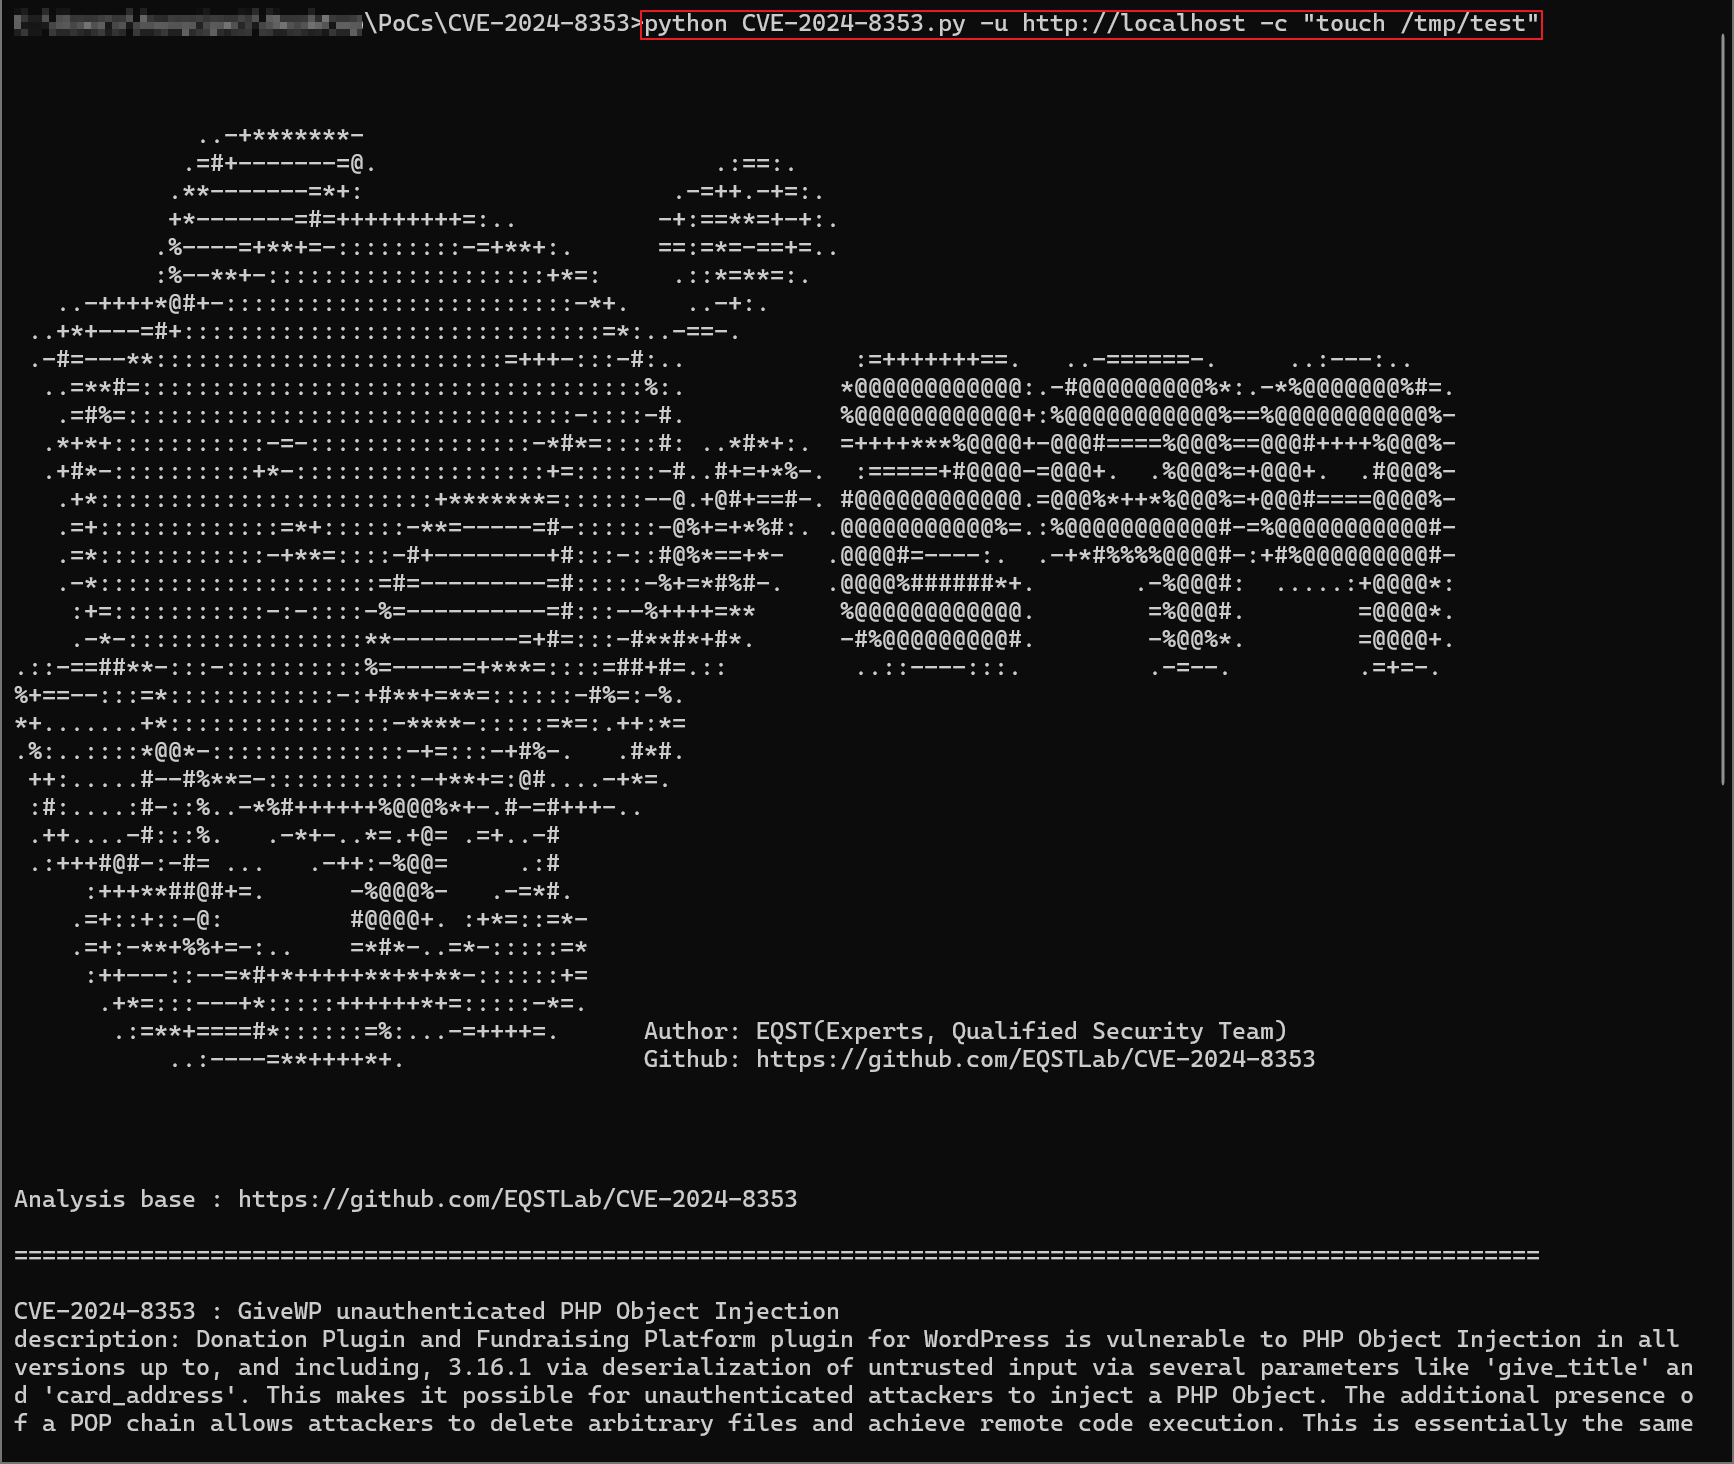 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit
 mooseloveti/vitepos-cve-report
Disclosure for CVE-2025-13156
 redteampentesting/moodle-rce-calculatedquestions
Scripts for Analysis of a RCE in Moodle Calculated Questions (CVE-2024-43425)
 kulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980
Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 rxerium/cve-2025-4427-cve-2025-4428
Detection for CVE-2025-4427 and CVE-2025-4428