

ShipProof
 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
cloud-securitycode-analysisconfiguration-auditing+6
divyanshukumar0014/shipproofSOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…

 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 hiteshgorana/susvibes-jupyter-server-cve-2026-35397
Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…
 synacktiv/weggli_rules_sstic2023
Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
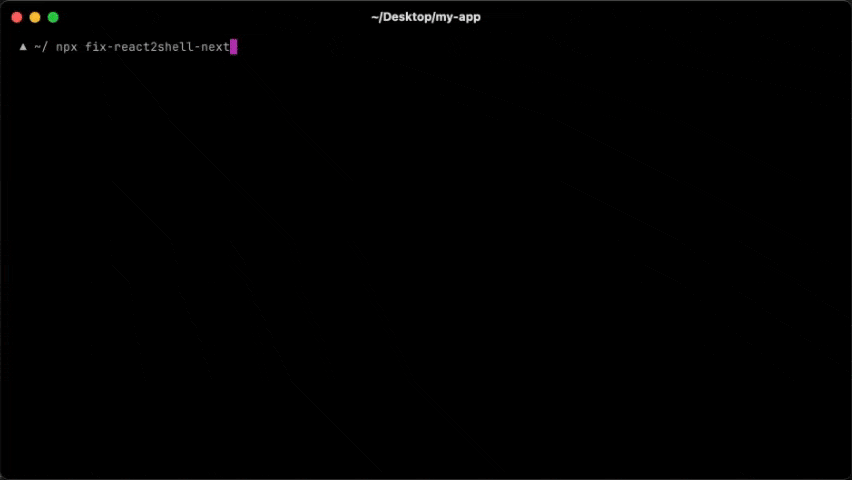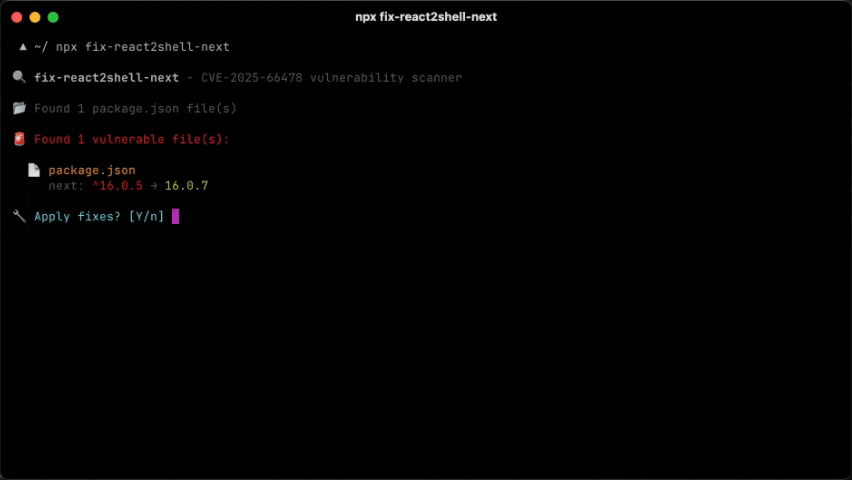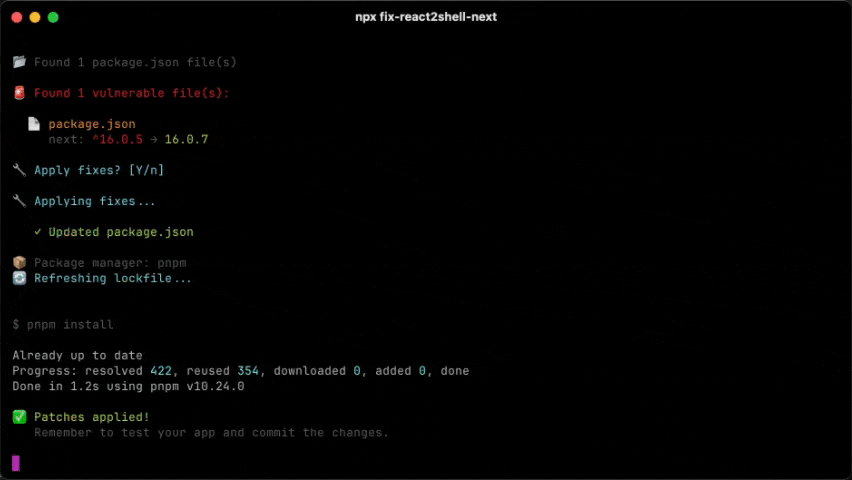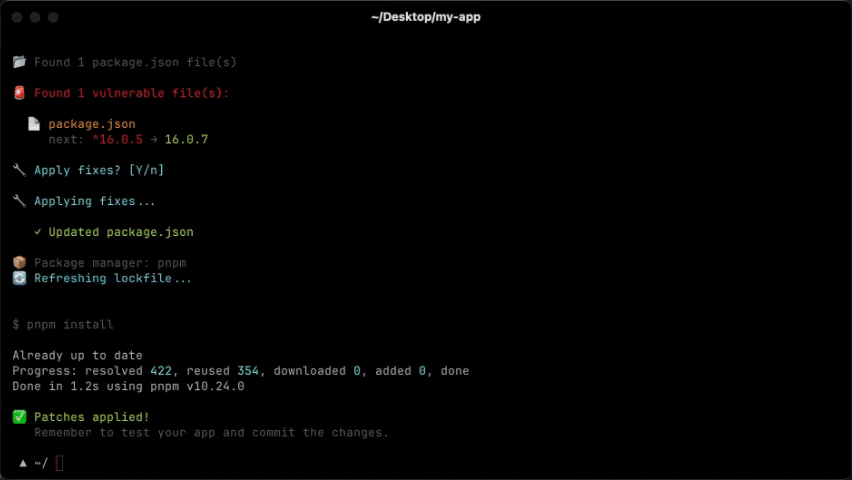 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.
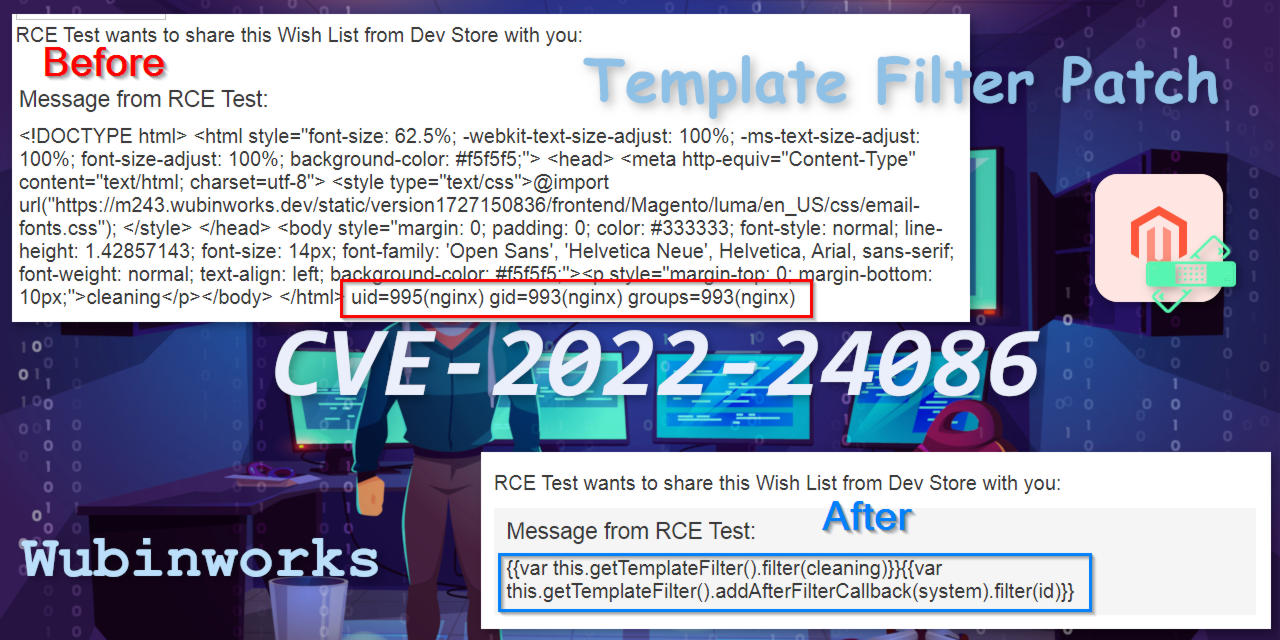 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 paolorabbito/internet-security-project---cve-2021-26814
Educational exploit demonstration for CVE-2021-26814 targeting Wazuh v4.0.3, with step-by-step exploitation and remediation code for university-level…
 oscerd/cve-2026-46590
Reproducer for CVE-2026-46590: Apache Camel camel-pqc key-lifecycle unsafe deserialization (FileBasedKeyLifecycleManager legacy .key migration via…
 oscerd/cve-2026-46457
Reproducer for CVE-2026-46457 — Apache Camel camel-nats inbound header injection (Camel control-header injection via a NATS publisher; CamelHttpUri…