
guardskill
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
ai-securitycode-analysisconfiguration-auditing+4
1
soemoescode/guardskillRead-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
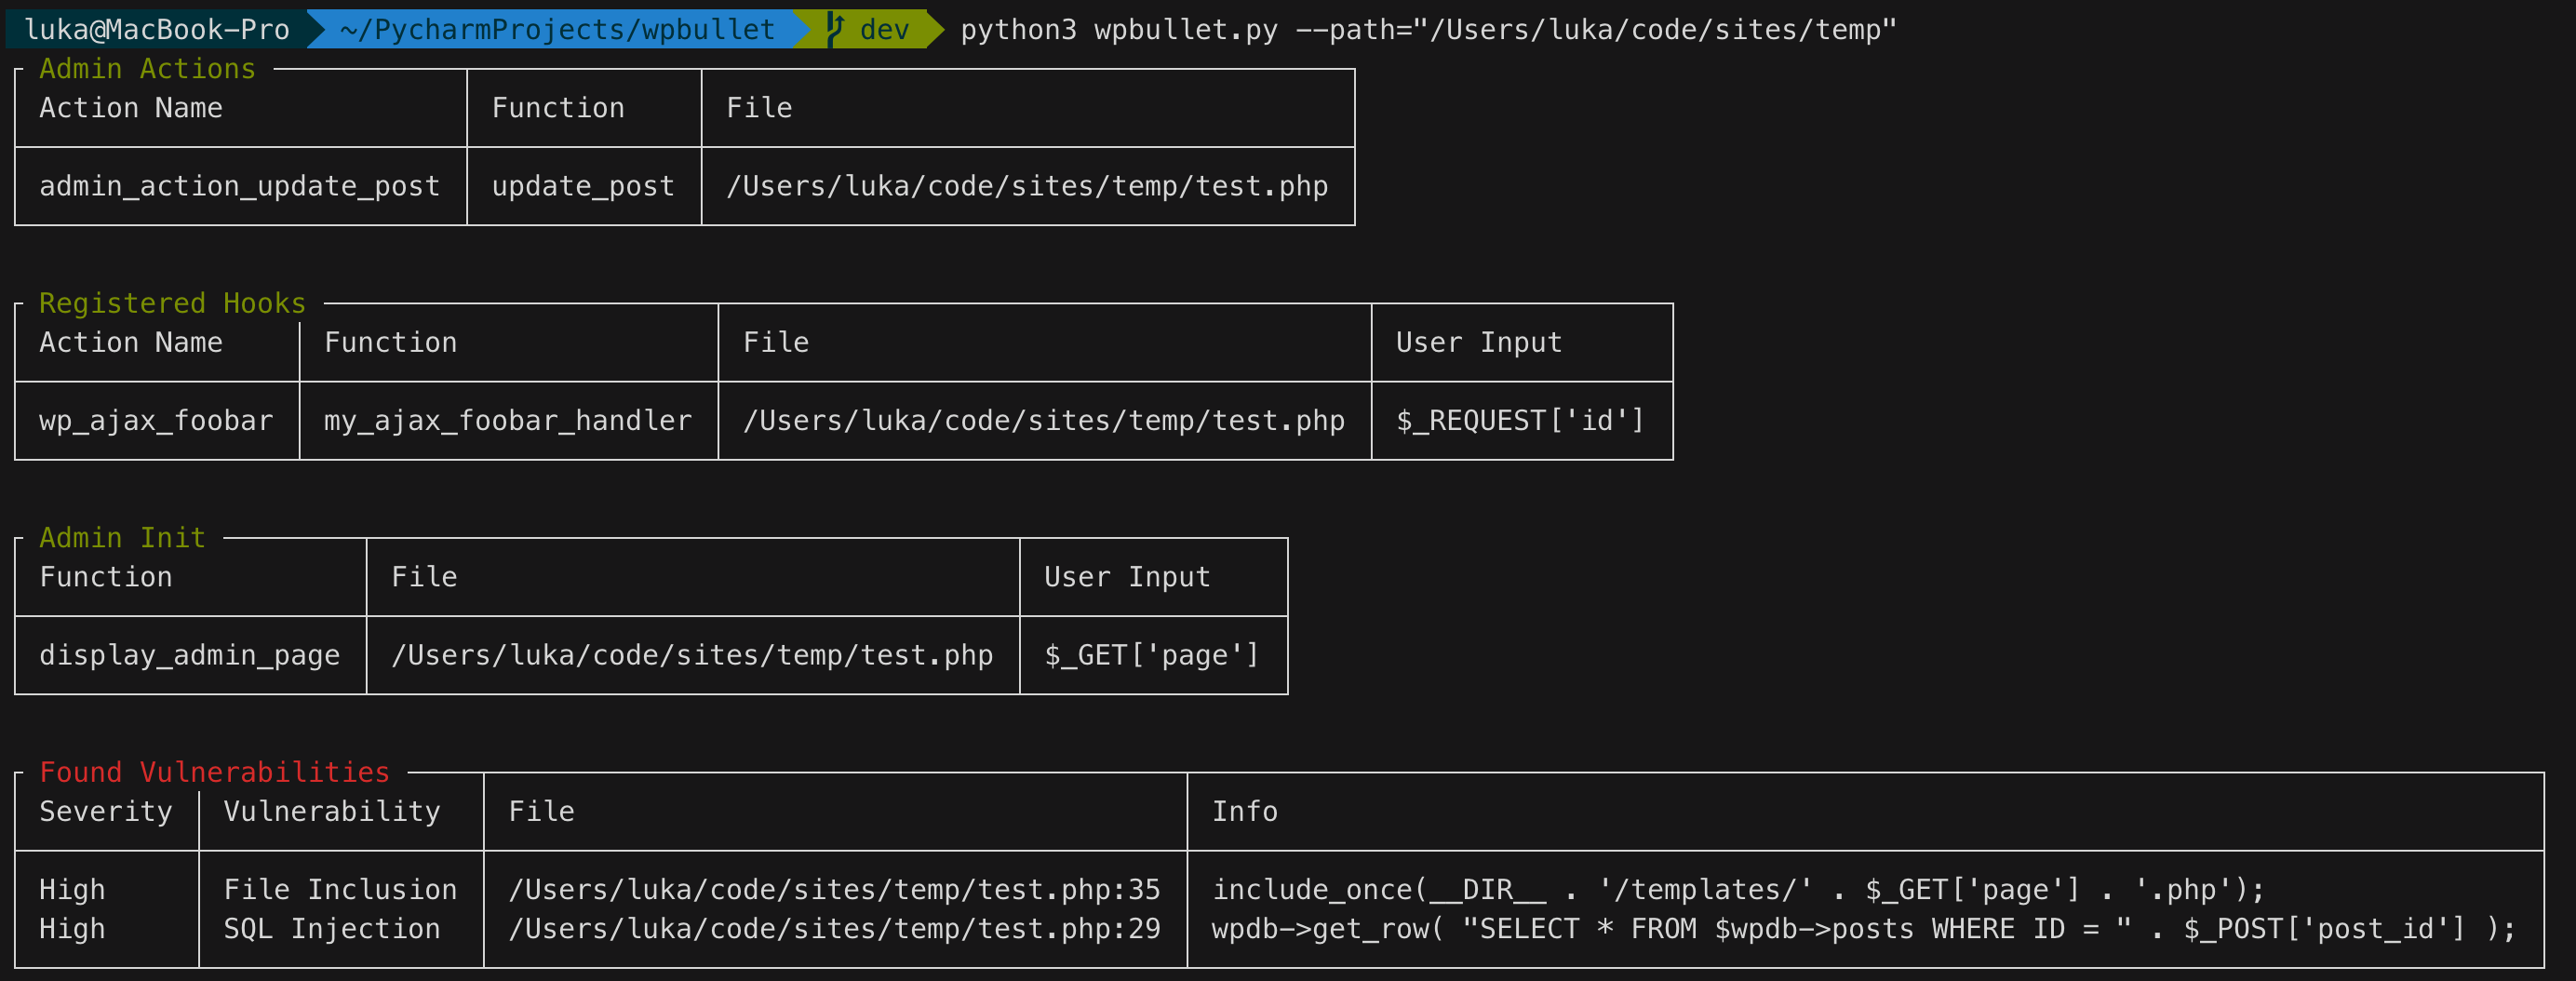 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 shoucheng3/jenkinsci__git-client-plugin_cve-2019-10392_2-8-4
Jenkins plugin providing Git APIs for automated repository operations including fetch, checkout, merge, and tag, with support for credential-based…
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 lirantal/cve-2024-21533-poc-ggit
Proof-of-concept exploit for CVE-2024-21533, an argument injection vulnerability in the ggit npm package that allows arbitrary command execution via…
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
 xelkomy/cve-2018-11235
Shell-based exploit for CVE-2018-11235, a remote code execution vulnerability in Git submodules. Enables testing and validation of the flaw in…
 nthuong95/cve-2018-11235
Proof-of-concept exploit for CVE-2018-11235, a remote code execution vulnerability in Git submodules. Demonstrates exploitation of malicious…
 thelastbyte/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a remote code execution vulnerability in git clients prior to v2.14.1, demonstrating recursive clone…
 jas502n/cve-2019-10392
Authenticated remote code execution exploit for Jenkins Git Client Plugin 2.8.2 via Jackson deserialization vulnerability (CVE-2019-10392).
 fishyyh/cve-2025-48384-poc
Proof-of-concept exploit for CVE-2025-48384, demonstrating remote code execution via a crafted git clone operation on vulnerable Git versions.
 knqyf263/cve-2018-11235
Proof-of-concept exploit for CVE-2018-11235, a remote code execution vulnerability in Git submodules. Includes Dockerfile for reproducible testing…
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 beishanxueyuan/cve-2025-48384-test
Reproduction of CVE-2025-48384 demonstrating a Git submodule path traversal vulnerability, with step-by-step commands to recreate the exploit.
 chenzhuo0618/test
Proof-of-concept exploit for CVE-2017-1000117, demonstrating a remote code execution vulnerability in Git.