
garble
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
anti-botbinary-analysiscode-analysis+4
5.8k
burrowers/garbleObfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
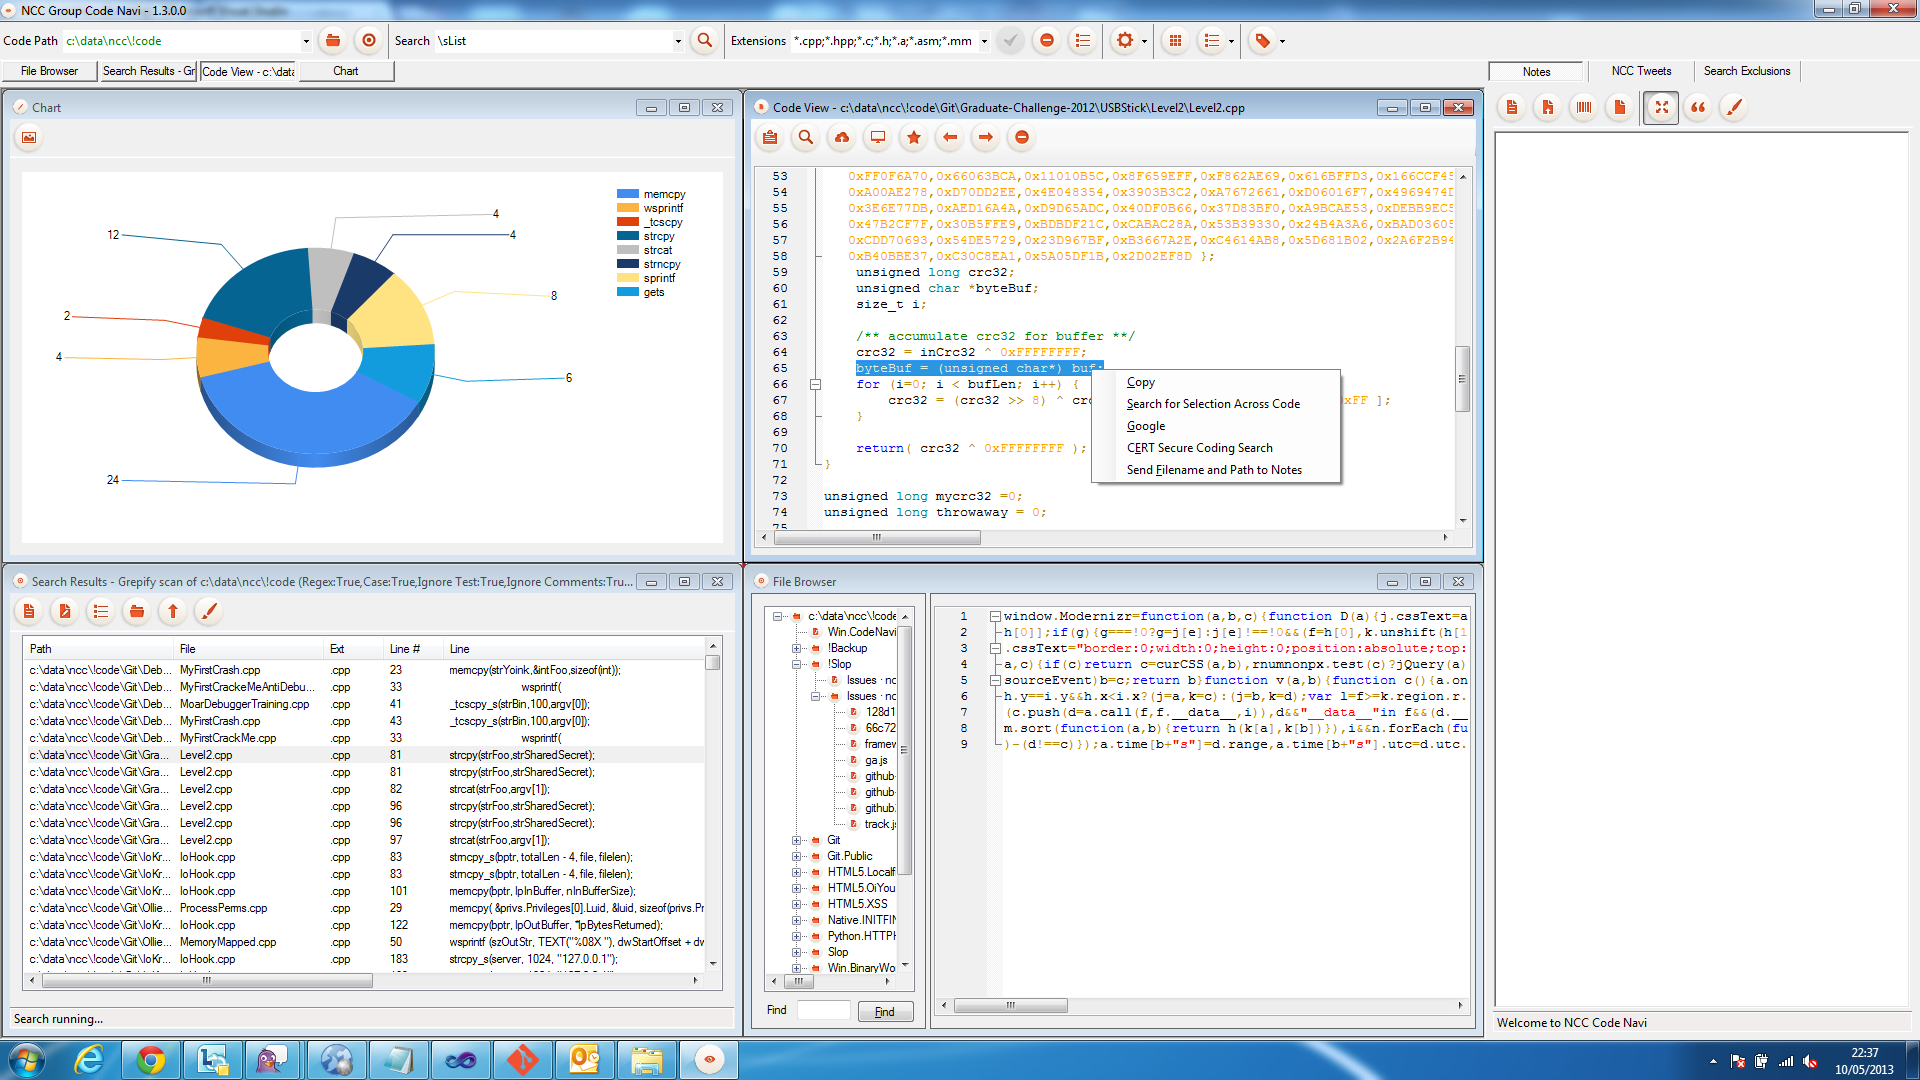 nccgroup/ncccodenavi
NCC Code Navigator
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 oscerd/cve-2026-49097
PoC reproducer for CVE-2026-49097 (Apache Camel camel-irc): the non-Camel-prefixed irc.sendTo header escapes the HTTP header filter and overrides the…
 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 gwroblew/detectxsslib
C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 zephrfish/wp2shell-scanner
CVE-2026-63030, CVE-2026-60137, wp2shell scanner
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…
 mooseloveti/hippoo-mobile-app-for-woocommerce-cve-report
Disclosure for CVE-2025-13339
 shoucheng3/dspace__dspace_cve-2022-31195_5-10
Patched version of DSpace repository addressing CVE-2022-31195, providing a secure digital asset management platform with enhanced vulnerability…