Instatic-Stored-XSS-CVE-2026-103931

Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…

Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…

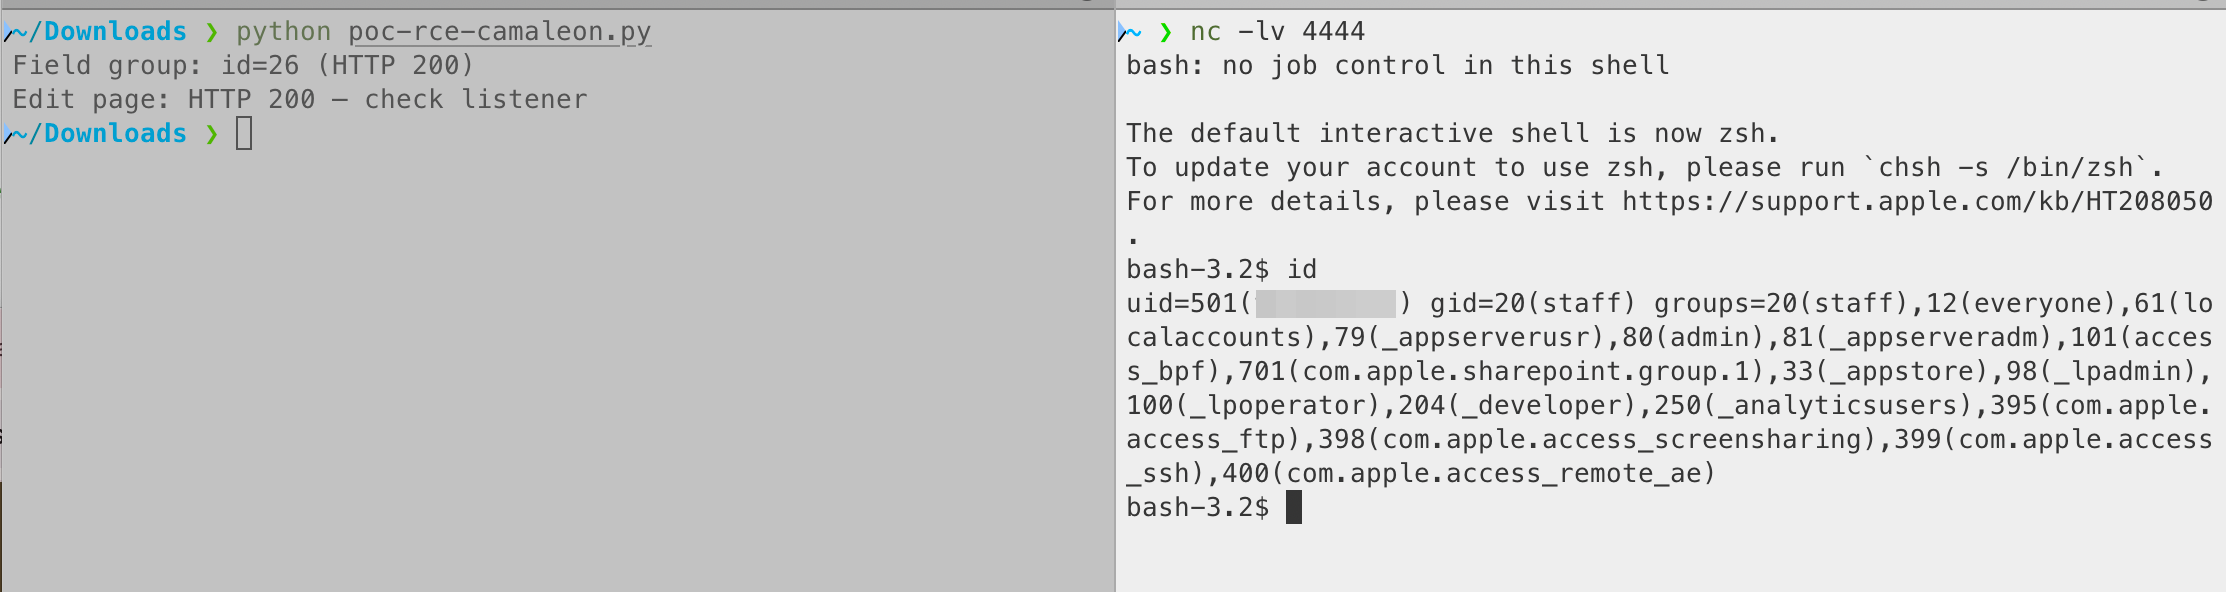
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field

PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.

Open-source secret scanner in Rust


Proof-of-concept exploit for CVE-2022-23614 demonstrating arbitrary code execution via Twig's sort filter sandbox bypass in PHP applications.

Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.

Report and PoC of Heap Buffer Overflow in Pepper Language before version 0.1.1, commit 961a5d9988c5986d563310275adad3fd181b2bb7

PoC: identify silent security patches before CVE

Python script to scan Git repos for interesting strings

Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.

Finding potential software vulnerabilities from git commit messages

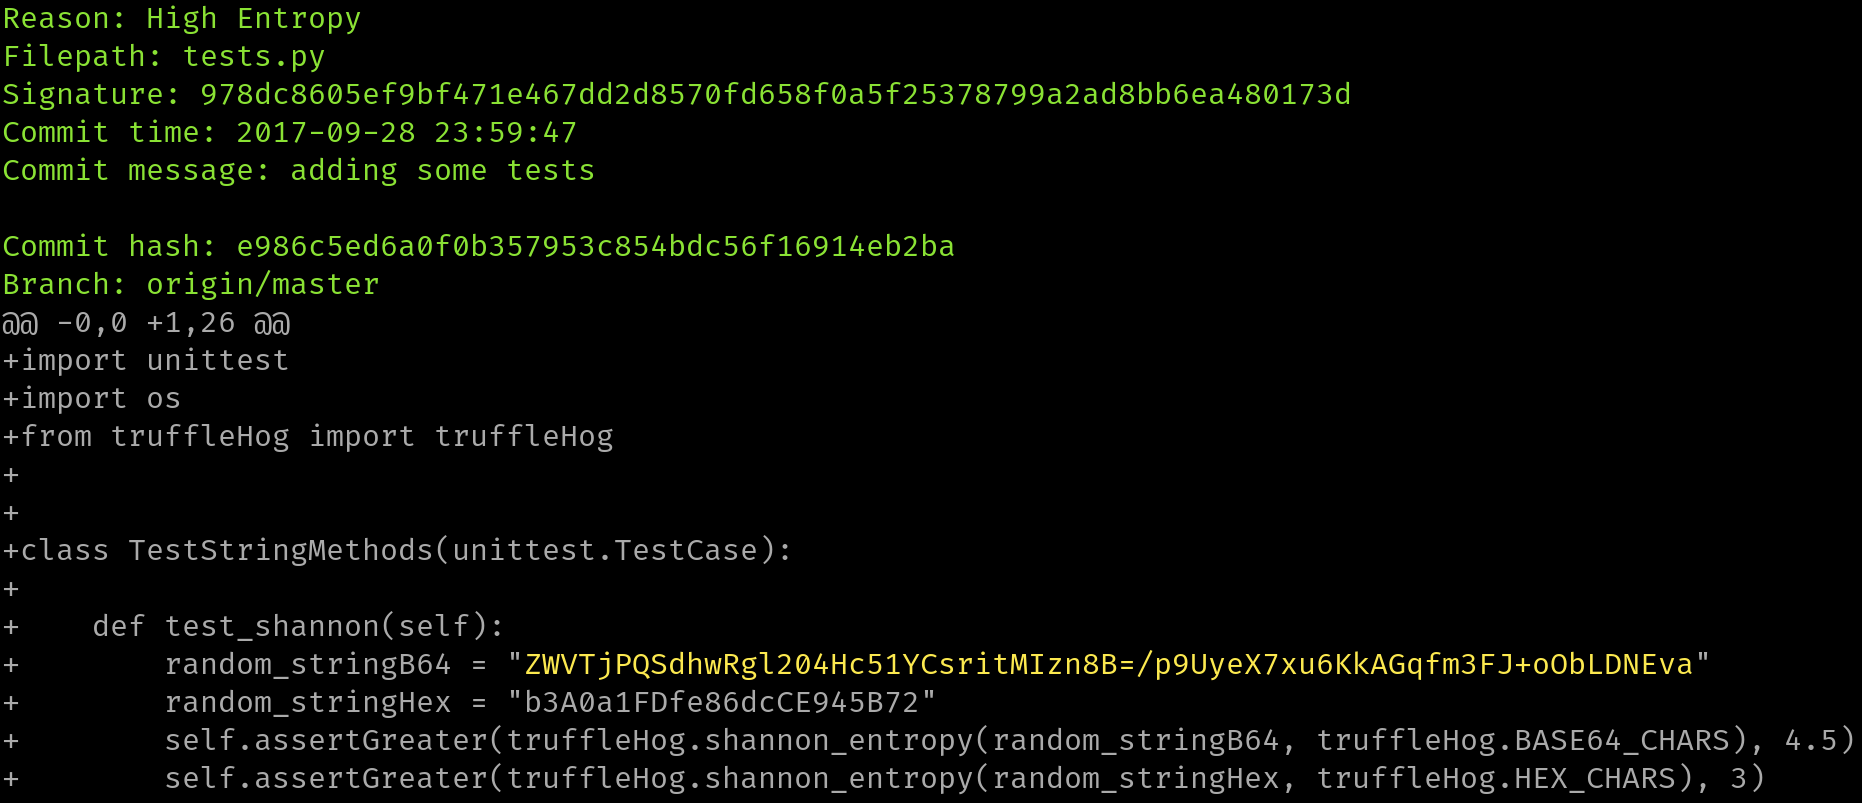
Searches through git repositories for high entropy strings and secrets, digging deep into commit history

Pluggable linting tool to prevent committing credential.