
FlowName
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
ai-assisted-reversingai-securitycode-analysis+3
123wwwa/flownameNext-generation JavaScript identifier recovery with LLMs.
 squeeze440/obsidian-note-toolbar-poc
PoC — frontmatter-driven arbitrary JavaScript execution in Note Toolbar for Obsidian (GHSA-q8cw-3m8c-5pf2, CVE-2026-87002, CVSS 7.0).
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

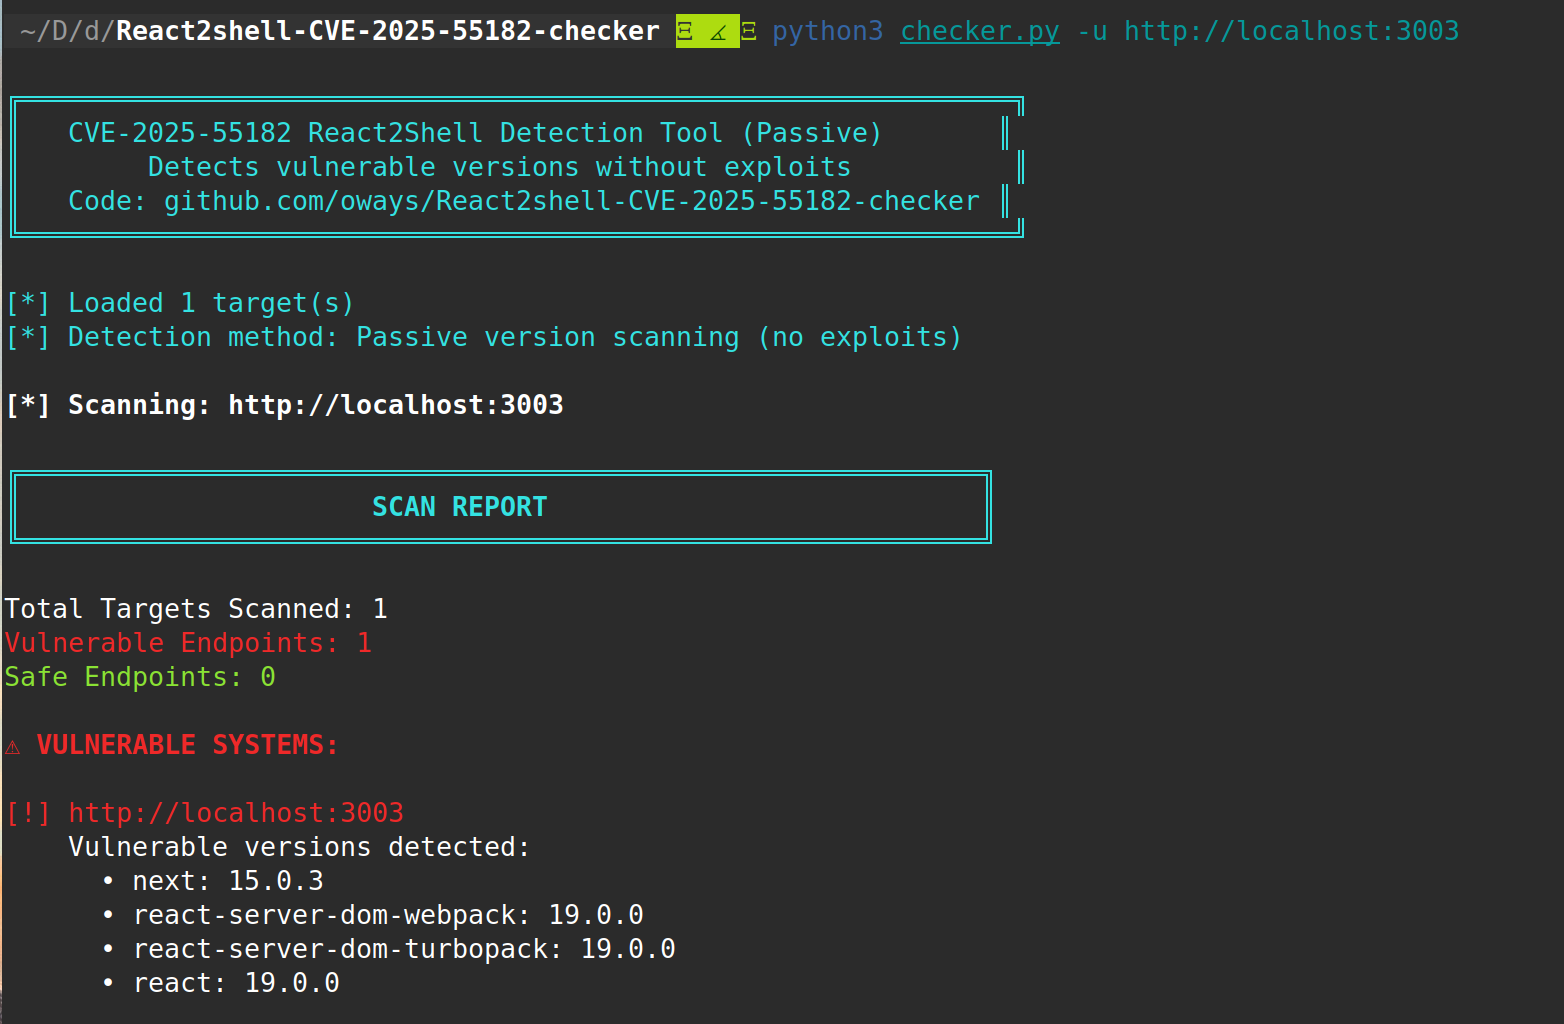 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 releaseown/analysis-and-poc-n8n-cve-2025-68613
Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…
 m-lito13/sealsecurity_exam
Fix prototype pollution vulnerability (CVE-2023-26136) for tough-cookie package
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 releaseown/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…