

sast
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
cloud-securitycode-analysisdefensive-tools+9
29 days ago
vulnz/sastFree offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
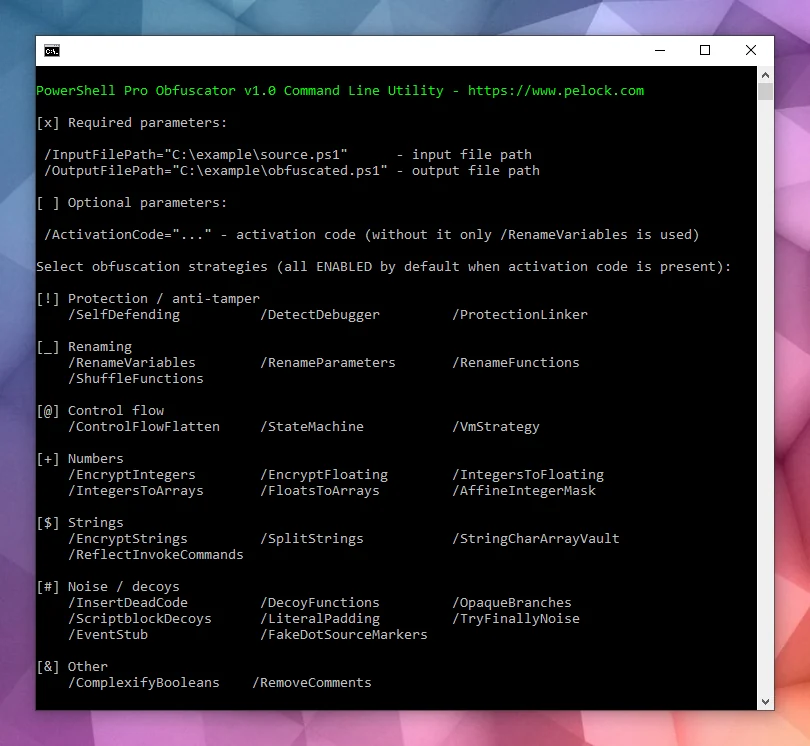 pelock/powershell-pro-obfuscator-python
Automate PowerShell script source code obfuscation & virtualization with a flexible Web API for Python (pip package).
 dxleryt/cve-2026-25731
Proof of Concept for a Server-Side Template Injection (SSTI) vulnerability in Calibre’s Templite engine (GHSA-xrh9-w7qx-3gcc). Demonstrates arbitrary…
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 califio/ngxray
ngxray — nginx config security scanner
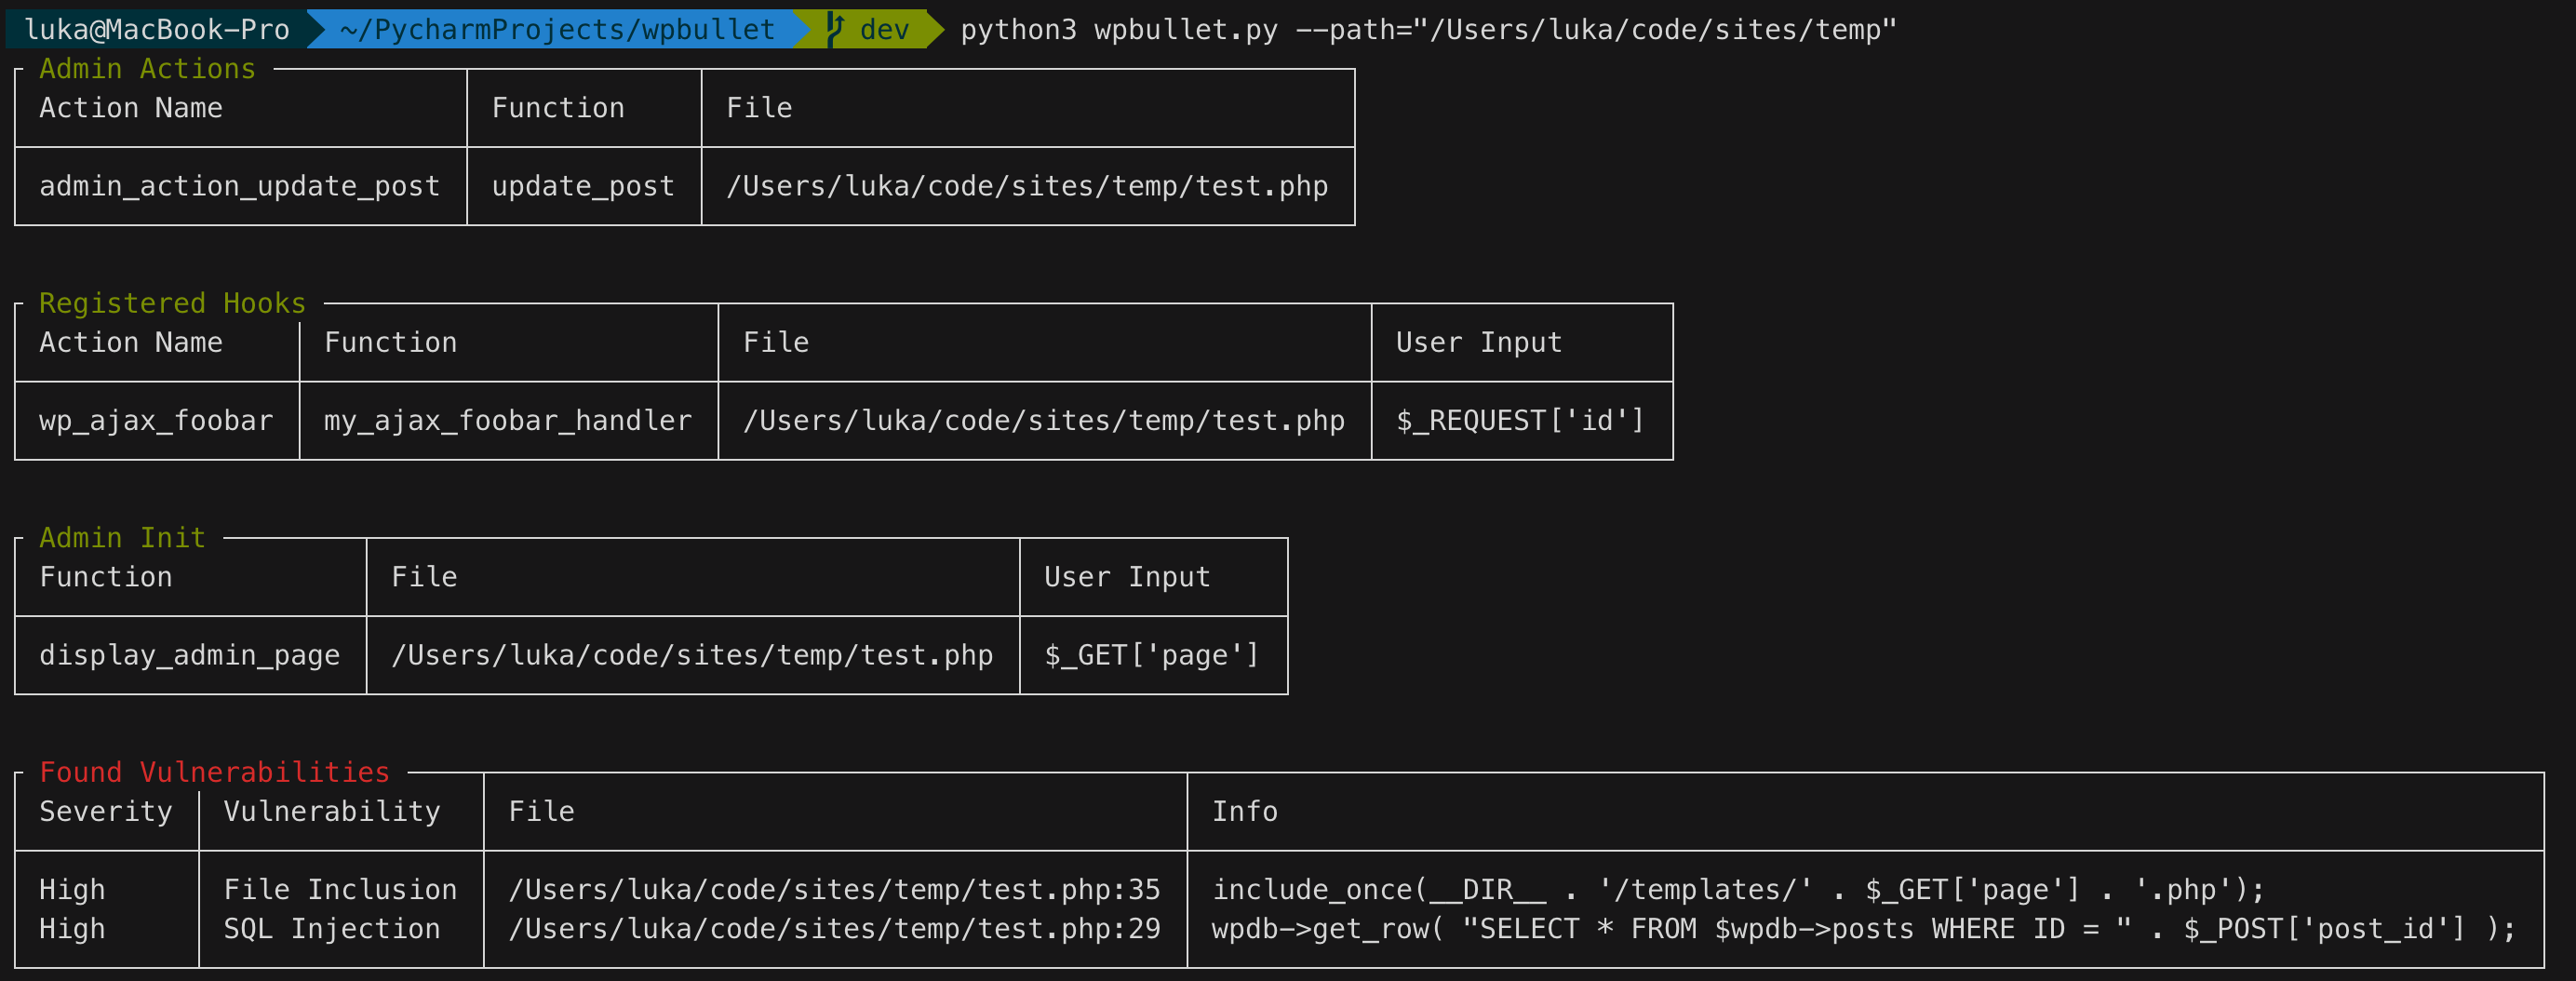 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
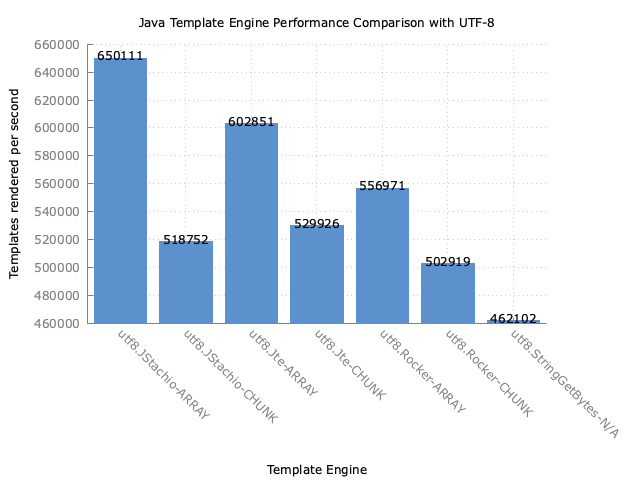 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-32070_14-5
Generic rendering system converting wiki syntax, HTML, and other formats into XHTML. Part of the XWiki platform, providing a flexible and extensible…
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…