
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
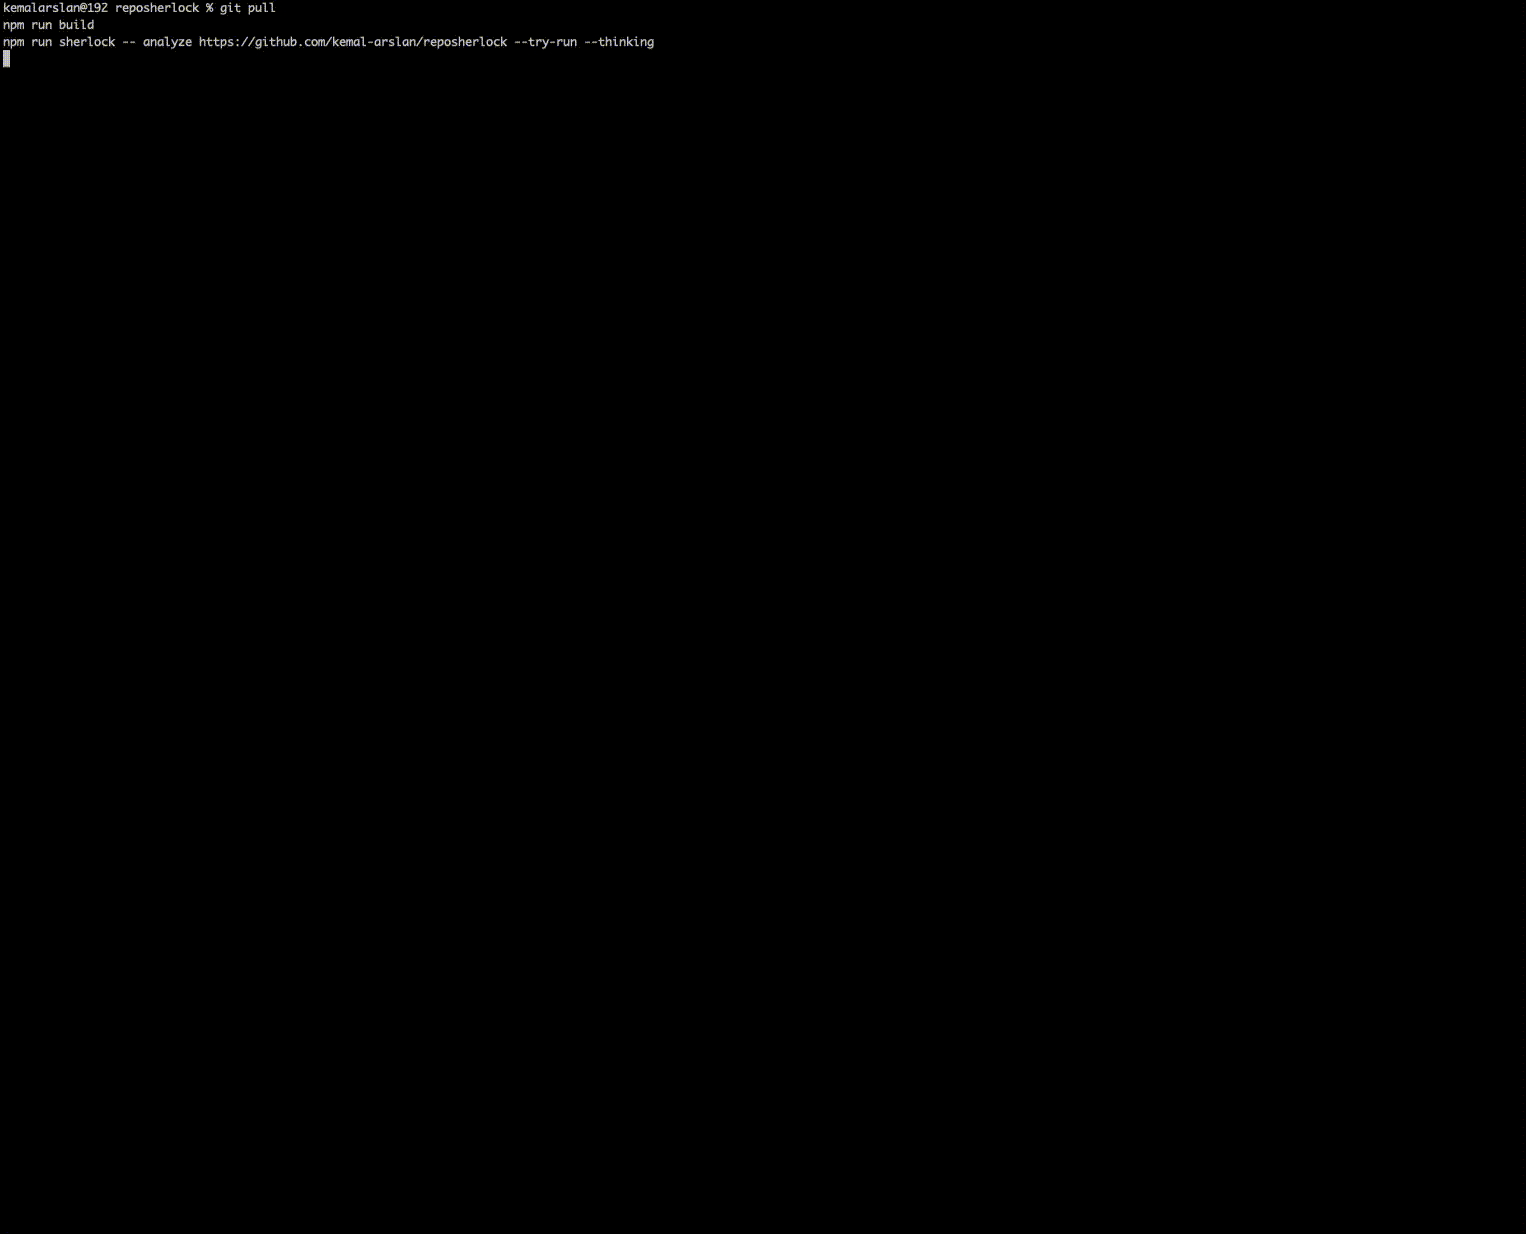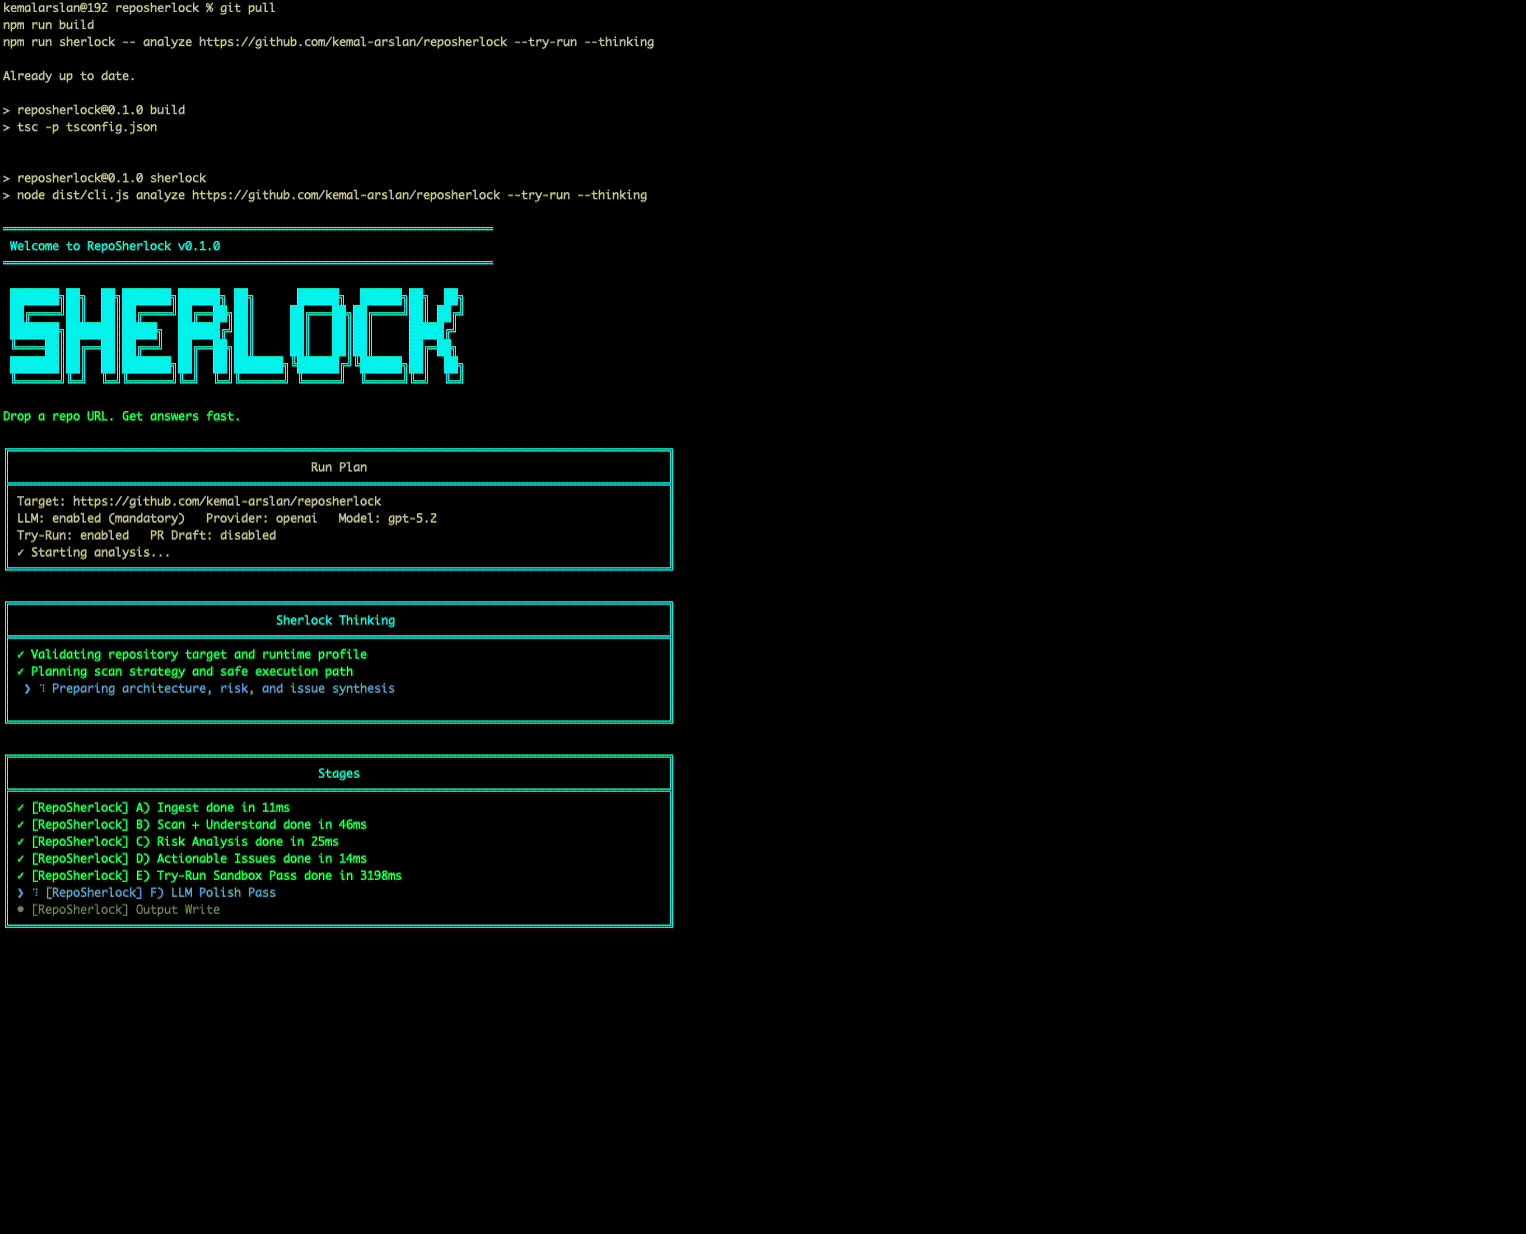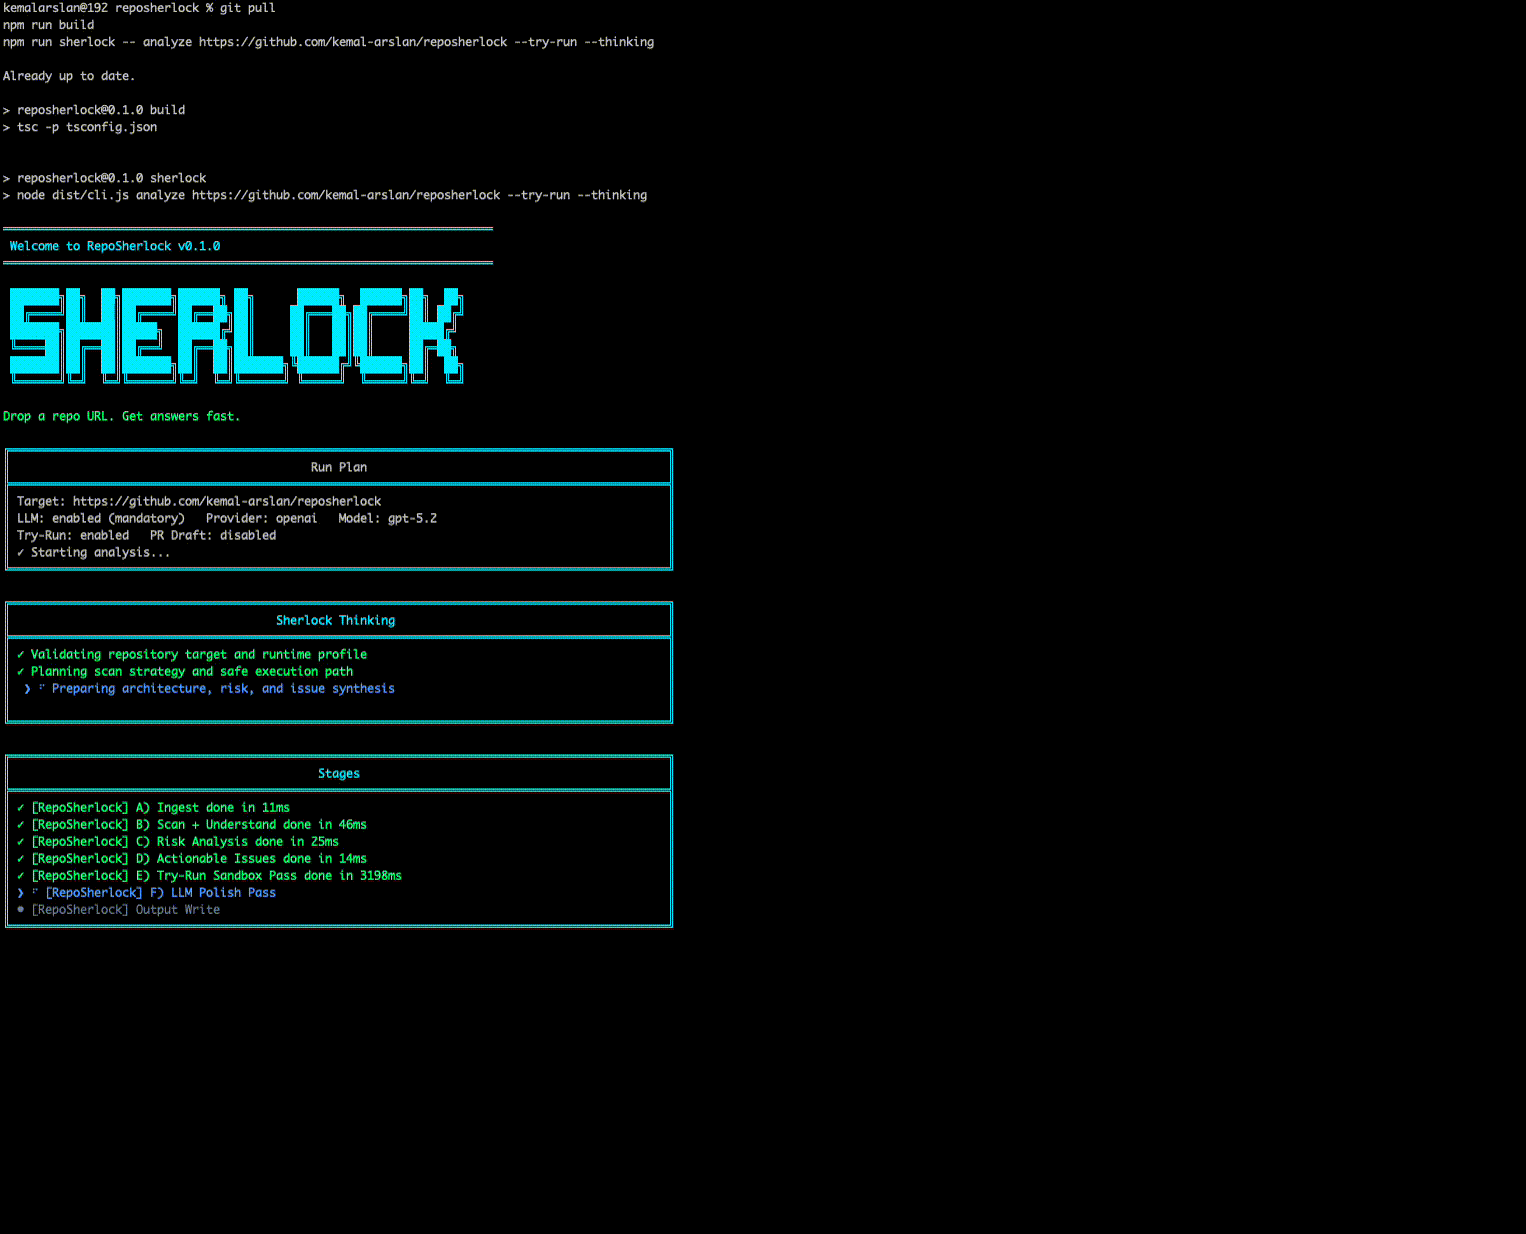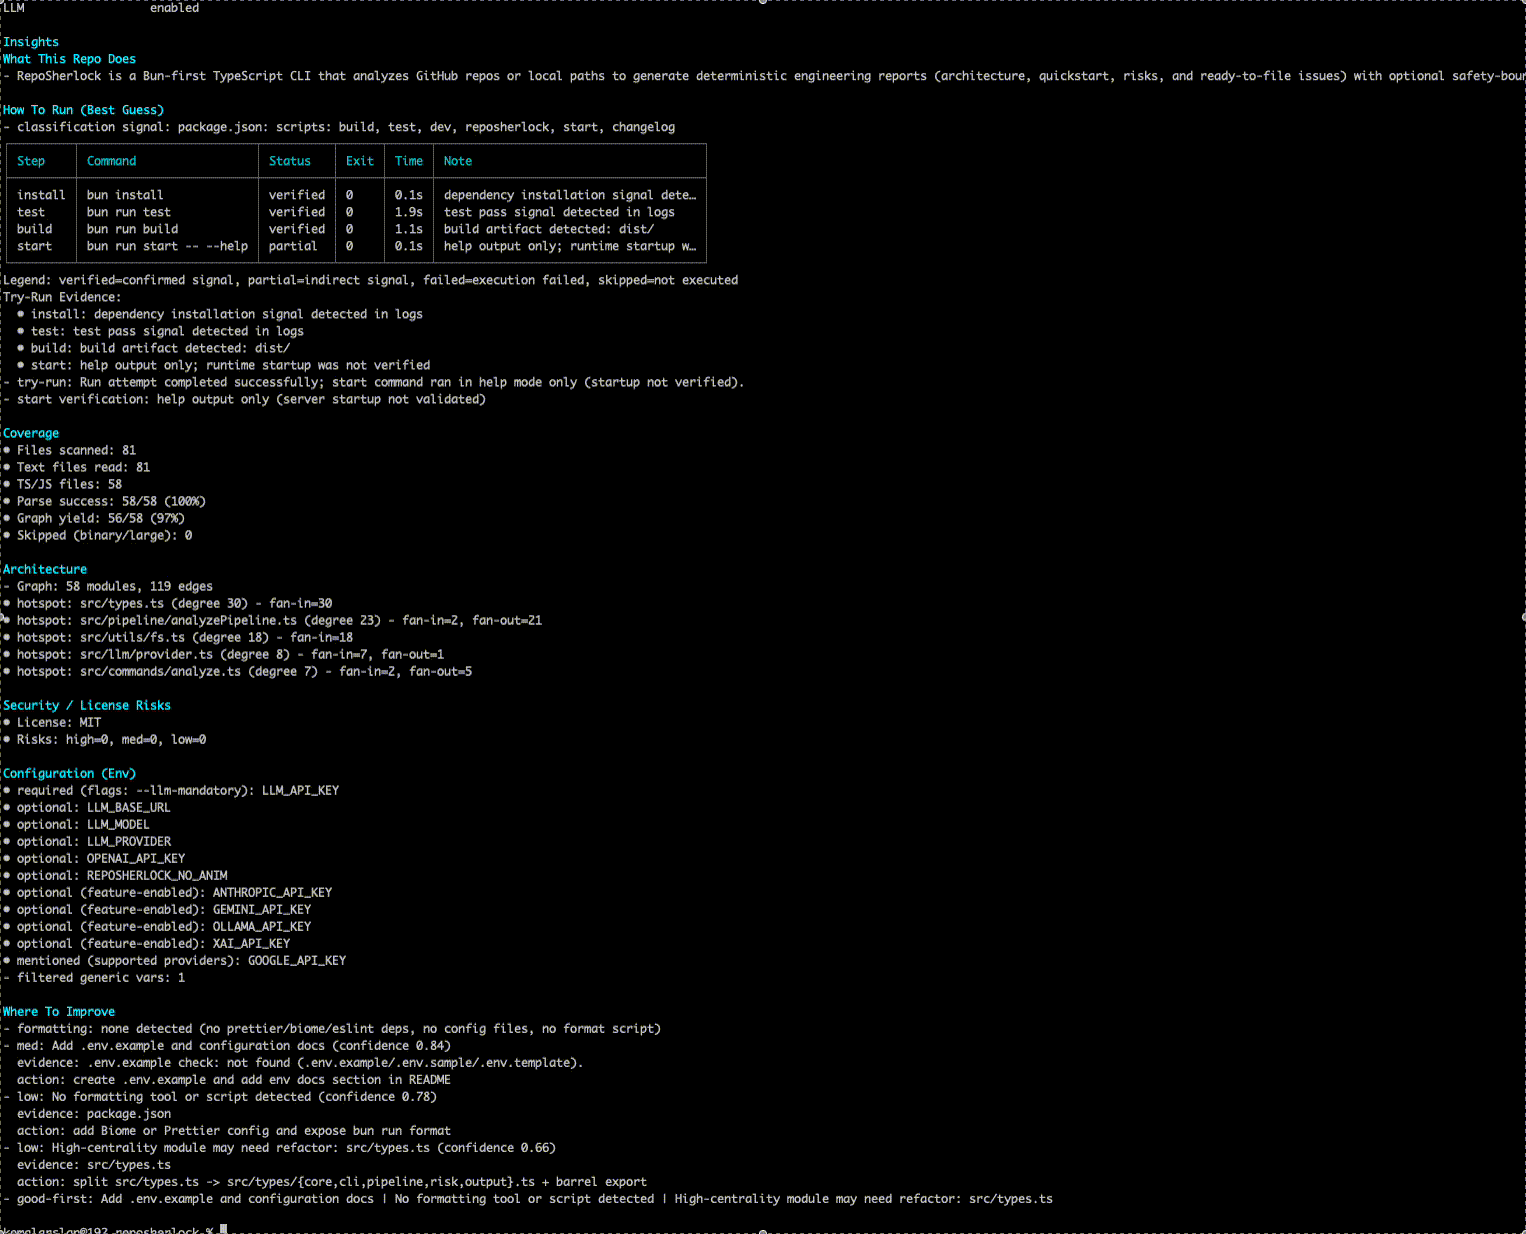 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
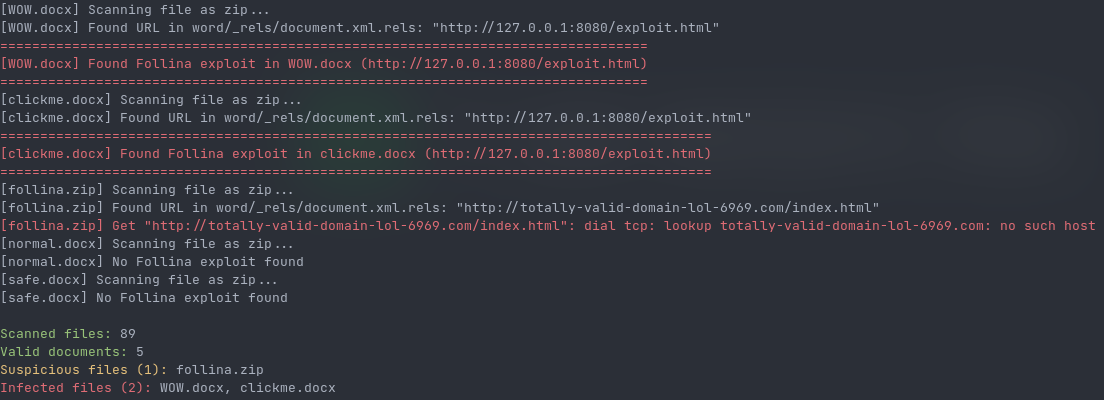 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 theopaid/cve-2026-67185-unauthenticated-path-traversal-allows-arbitrary-file-read-tinyweb-
Security Advisory: Unauthenticated Path Traversal Allows Arbitrary File Read (TinyWeb)
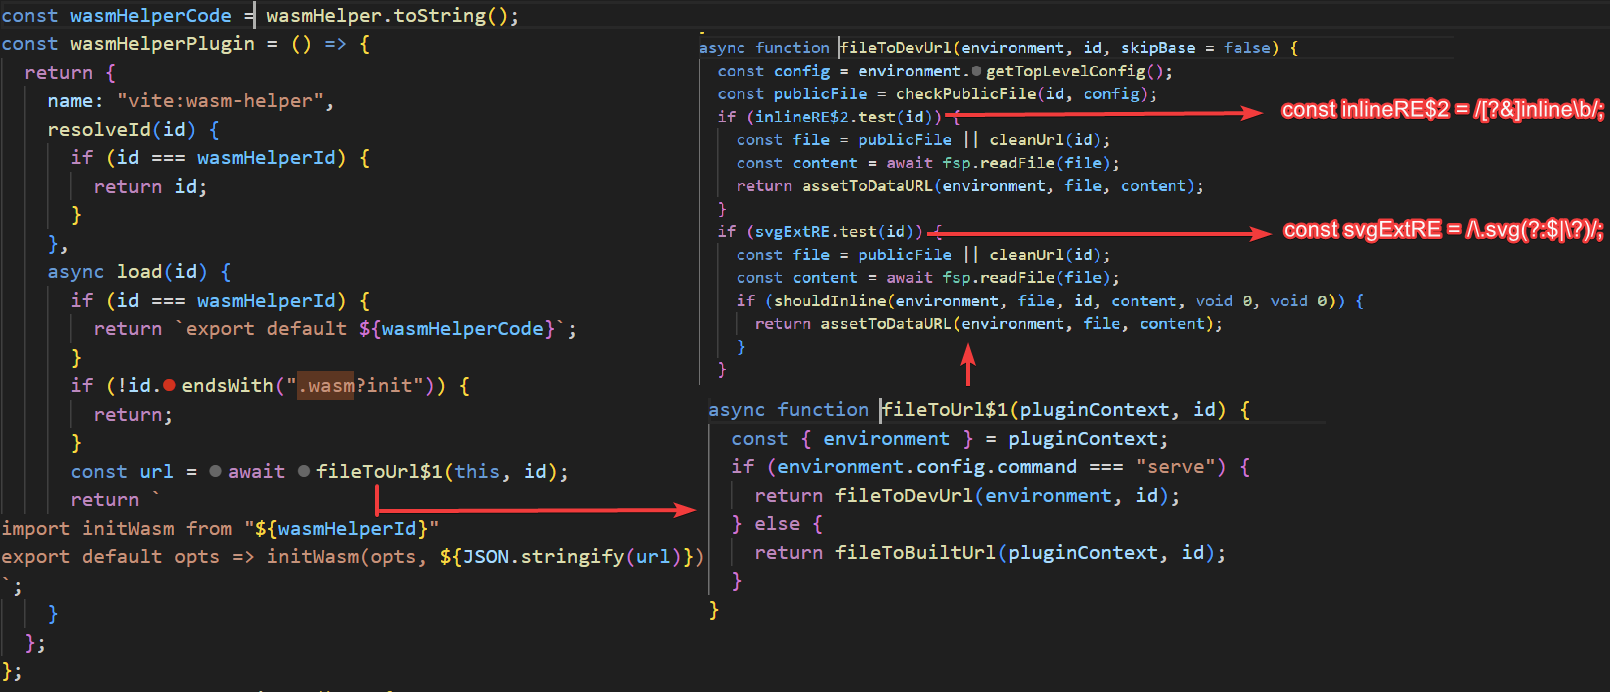 r0ngy40/cve-2025-30208-series
Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities
 fazilbaig1/cve-2021-23369
Python exploit script for CVE-2021-23369, a Remote Code Execution vulnerability in Handlebars template engine versions before 4.7.7. Accepts a target…
 mbadanoiu/cve-2023-34212
CVE-2023-34212: Java Deserialization via JNDI Components in Apache NiFi
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 cyberharsh/drupalcve-2018-7602
Exploit for Drupal CVE-2018-7602 remote code execution vulnerability via double URL encoding bypass of sanitize() filter. Includes Docker-based lab…
 ggfzx/cve-2024-36104
Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
 k8gege/cve-2019-11043
Proof-of-concept exploit module for CVE-2019-11043 (PHP-FPM remote code execution) with batch scanning capabilities for vulnerable Nginx…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 nyamort/cve-2024-50340
Proof-of-concept exploit for CVE-2024-50340 demonstrating Symfony ArgvInput environment variable injection via crafted URL query parameters, enabling…