

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 maximilianfeix/hexvero
Know what changed inside your app: inspect Electron apps and binaries, trace findings to file and line, compare releases. Locally, without executing…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 lauriewired/ghidramcp
MCP Server for Ghidra
 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 at190510-cuong/cve-2026-38165-ssti-
CVE-2026-38165 (SSTI)
 jack0we/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…
 killtr0/poc-cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574 targeting a Go web server vulnerability. Demonstrates remote code execution via crafted HTTP requests.
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 tranphuc2005/cve-2019-3396
Step-by-step analysis and exploitation guide for CVE-2019-3396, a critical SSTI vulnerability in Confluence Server & Data Center, including debugging…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
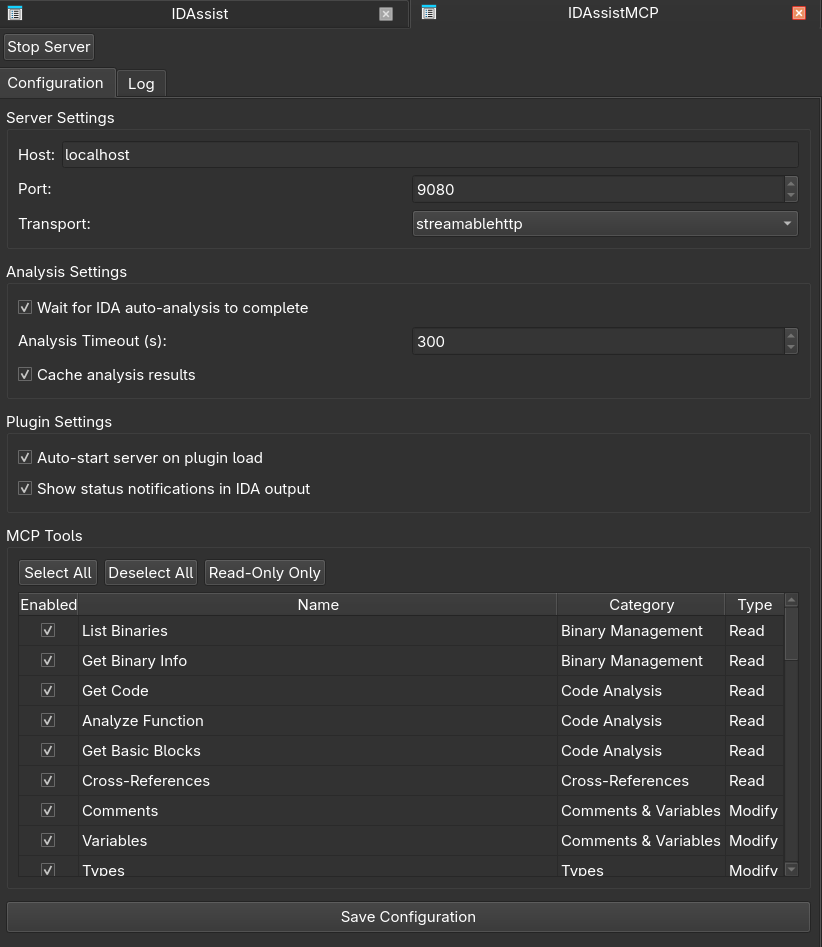 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 awslabs/threat-modeling-mcp-server
MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
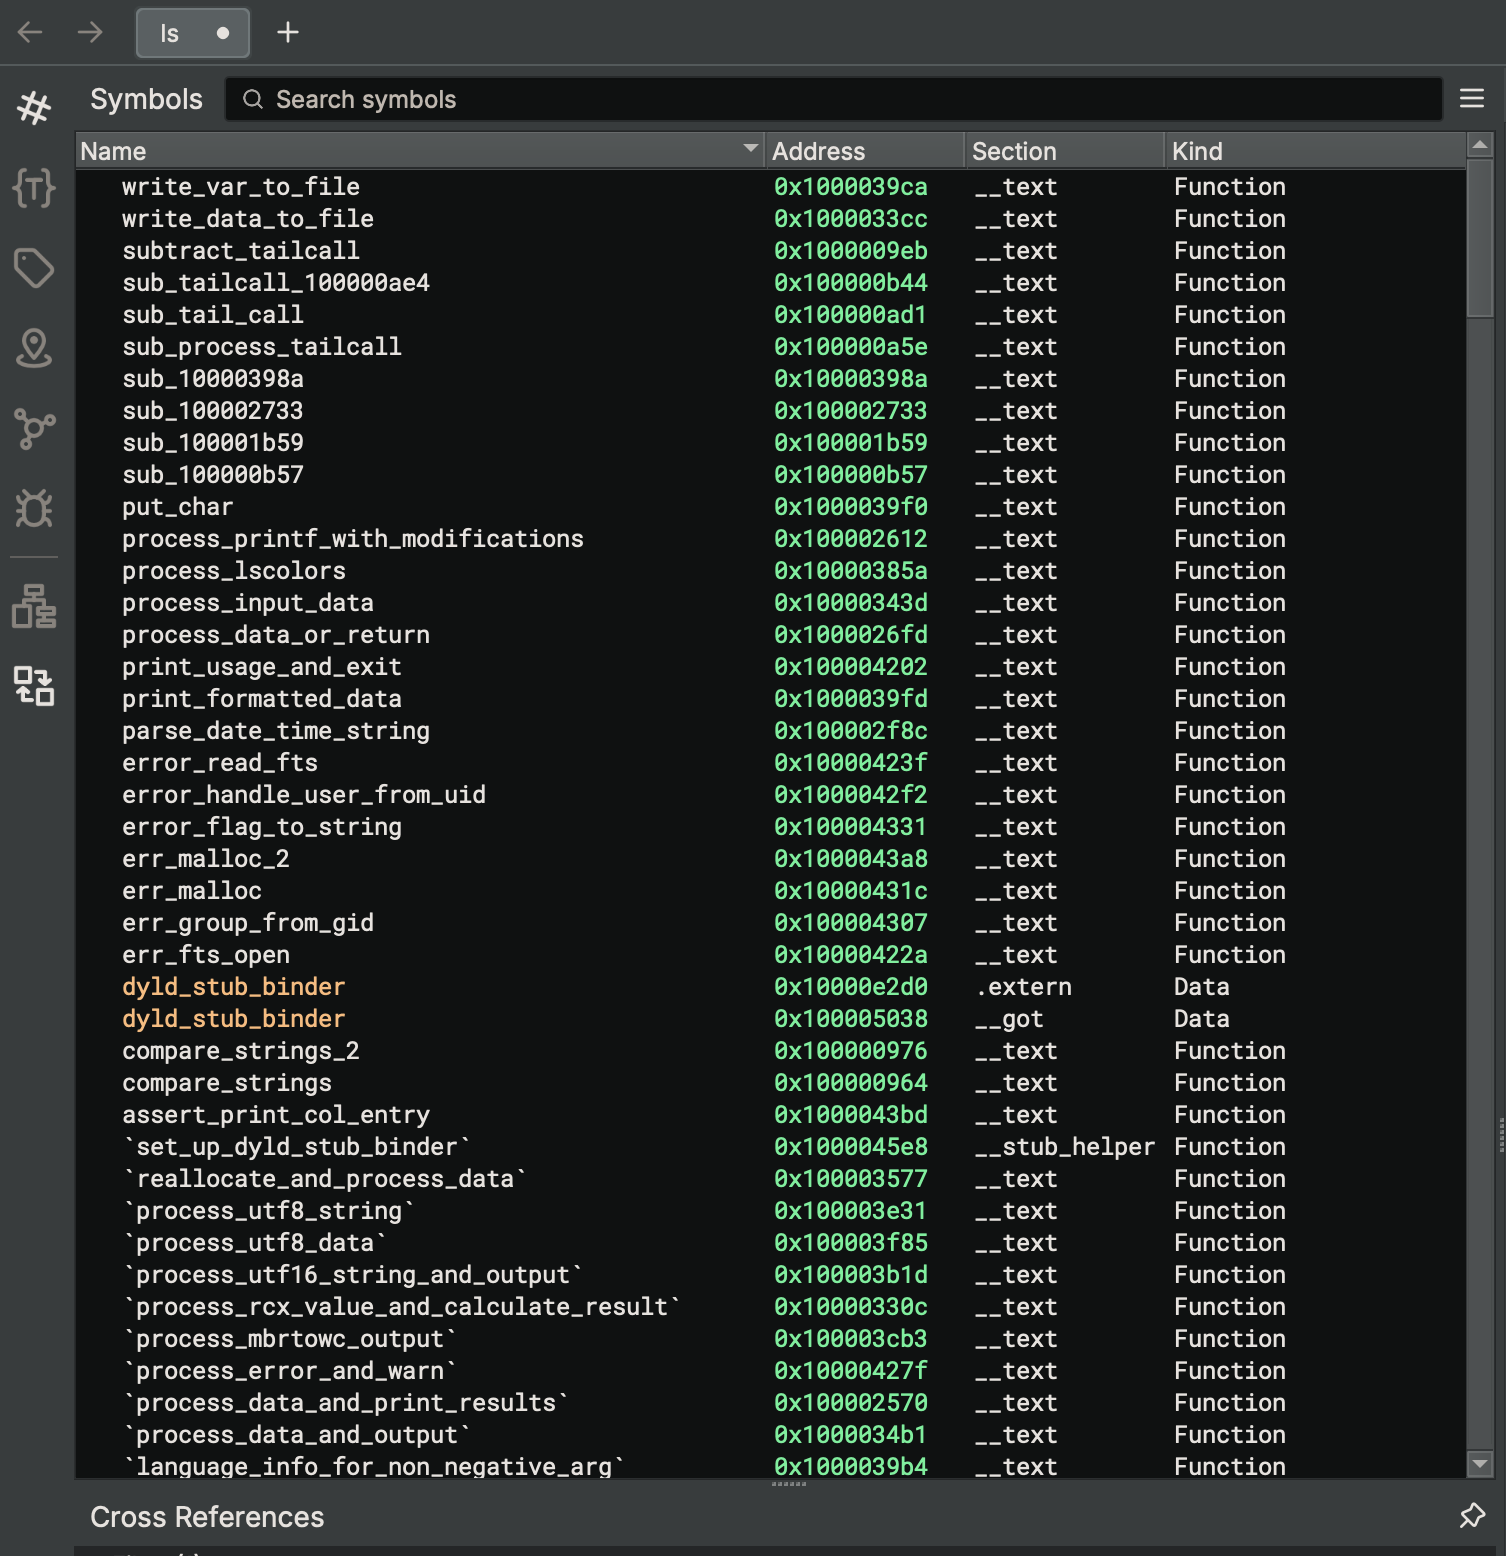 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…