

CVE-2017-8046
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
code-analysiseducationpenetration-testing+3
bkhablenko/cve-2017-8046Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 nxploited/cve-2024-1247-poc
Post Saint <= 1.3.1 plugin for WordPress Arbitrary File Upload
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 ajdumanhug/cve-2023-46818
CVE-2023-46818 Python3 Exploit for ISPConfig <= 3.2.11 (language_edit.php) PHP Code Injection Vulnerability
 ioncodes/curveball
PoC for CVE-2020-0601 - CryptoAPI exploit
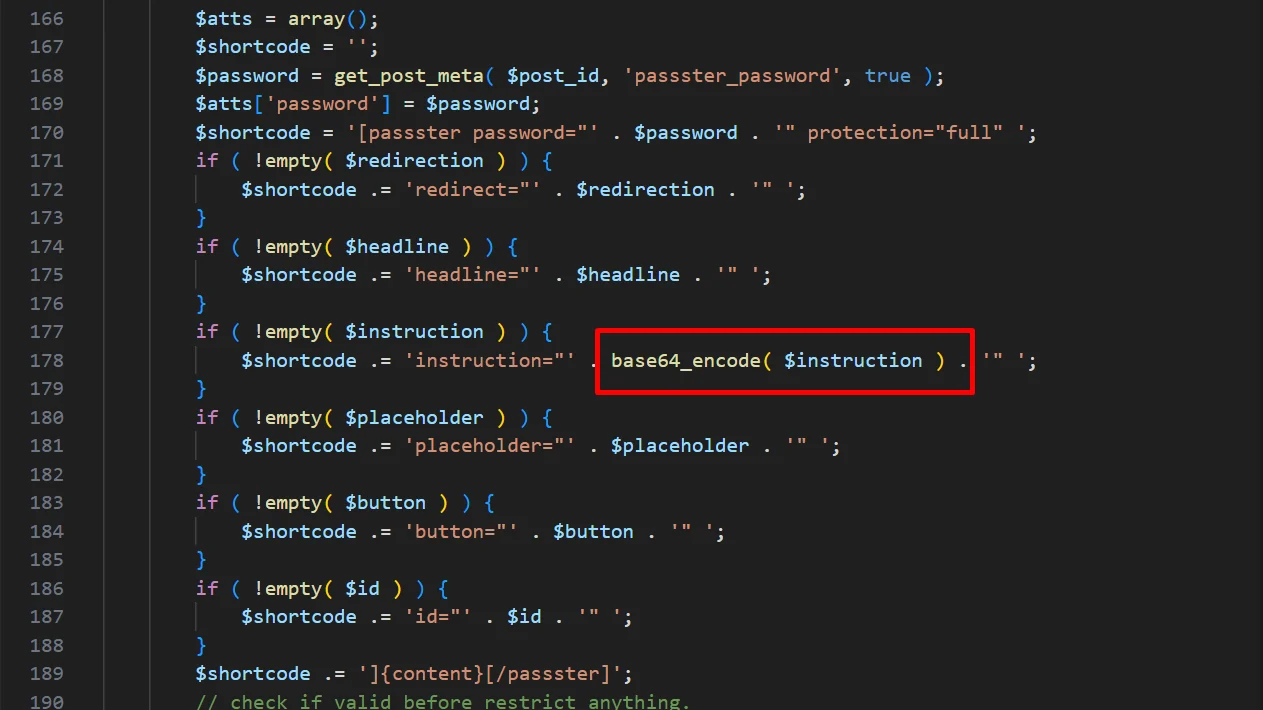 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 rxerium/cve-2025-4427-cve-2025-4428
Detection for CVE-2025-4427 and CVE-2025-4428
 eqstlab/cve-2024-5932
GiveWP PHP Object Injection exploit
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 kulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980
Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit