
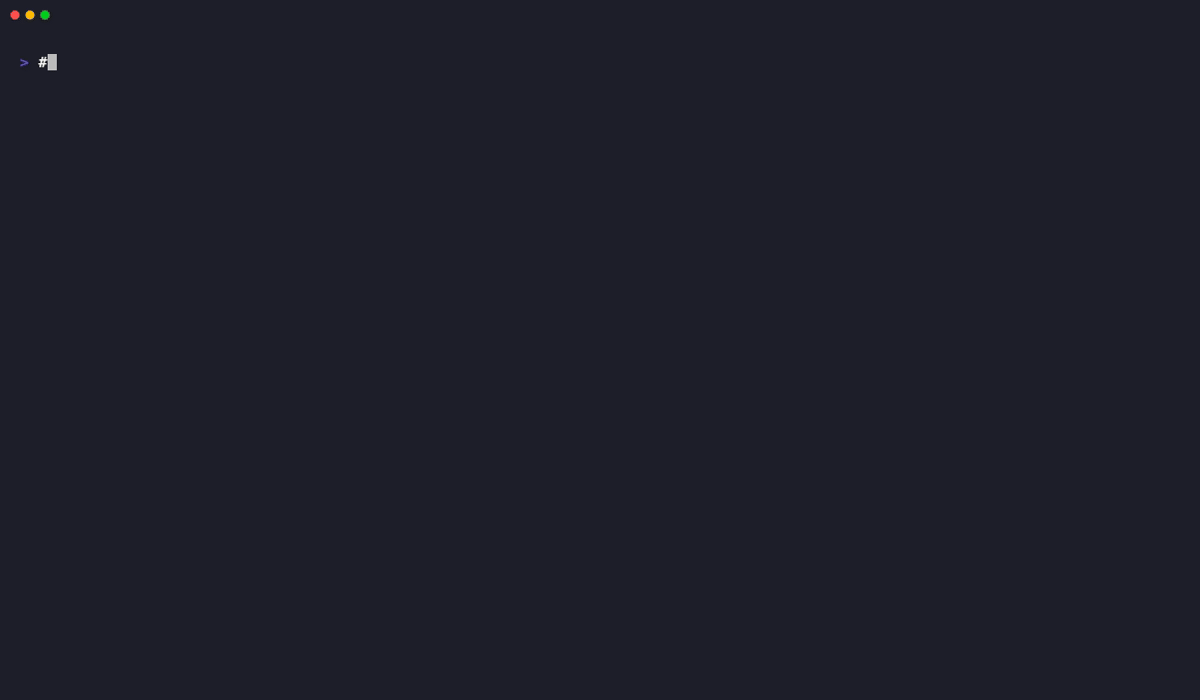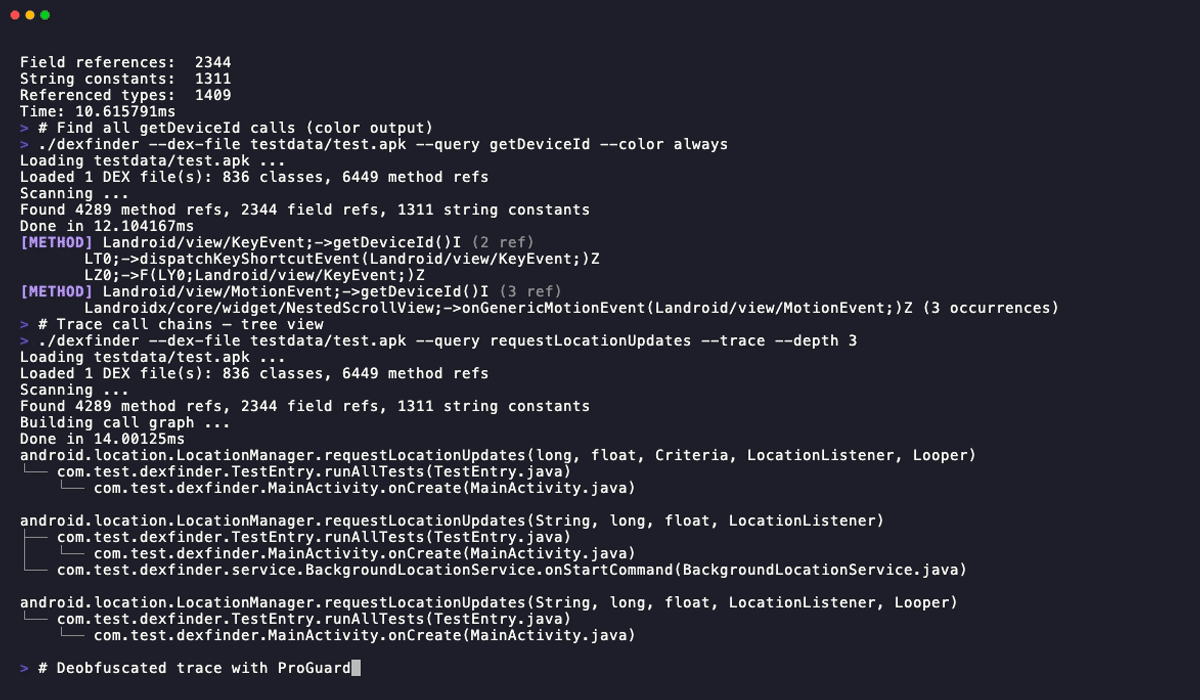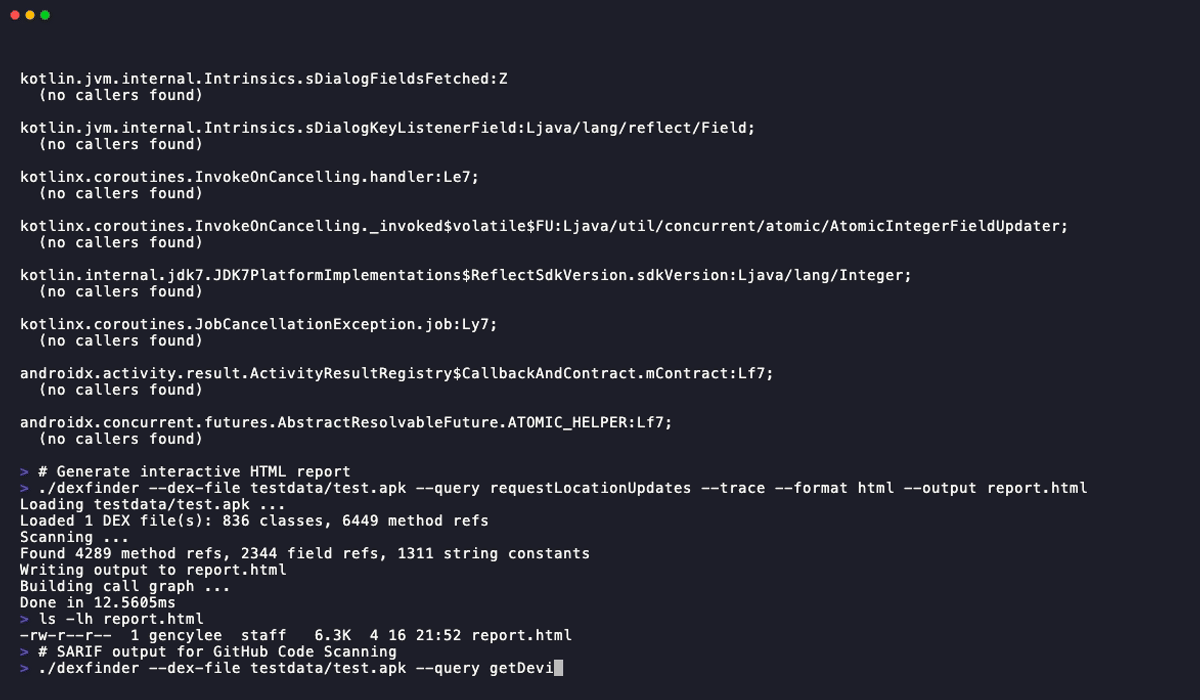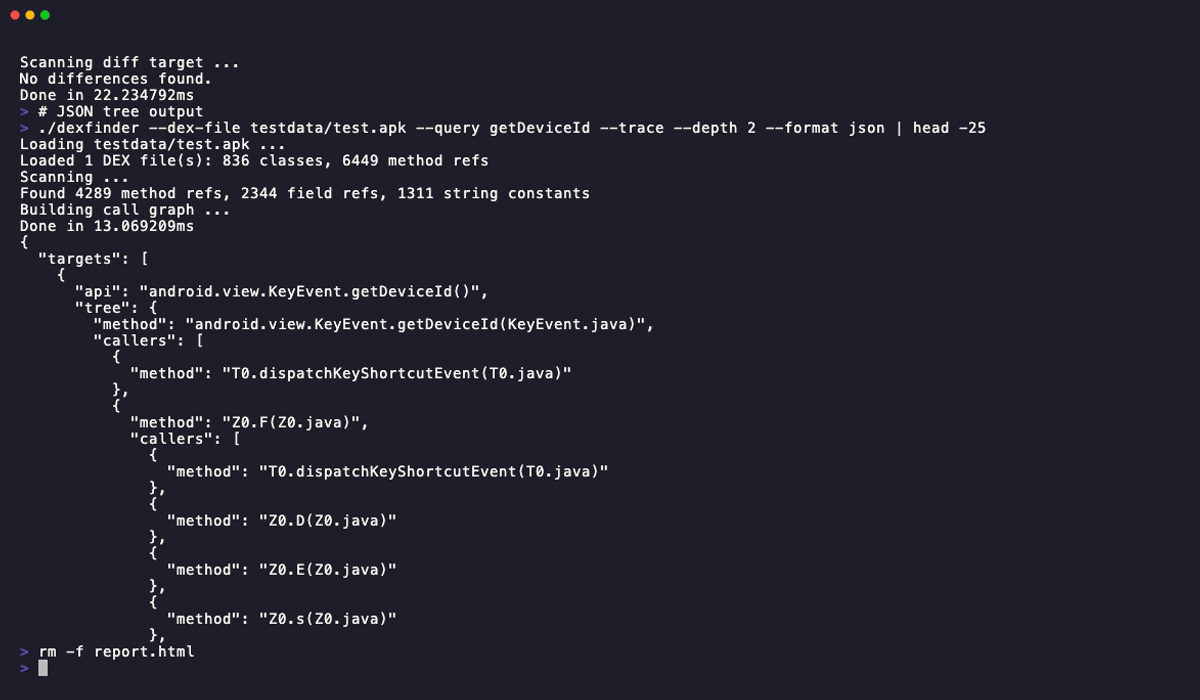
dexfinder
 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
android-securitybinary-analysiscode-analysis+6
108
junelegency/dexfinderCross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 trajanox/cve-2026-25541-fuel-analysis
CVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 learner202649/cve-2026-47102-poc
The code for personally reproducing the corresponding vulnerability
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 hax3xploit/cve-2021-41643
Remote Code Execution (RCE) vulnerability exists in Sourcecodester Church Management System 1.0 via the image upload field.
 kx00007/cve-2026-39938
Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 lukasz-rybak/cve-2026-22692
CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
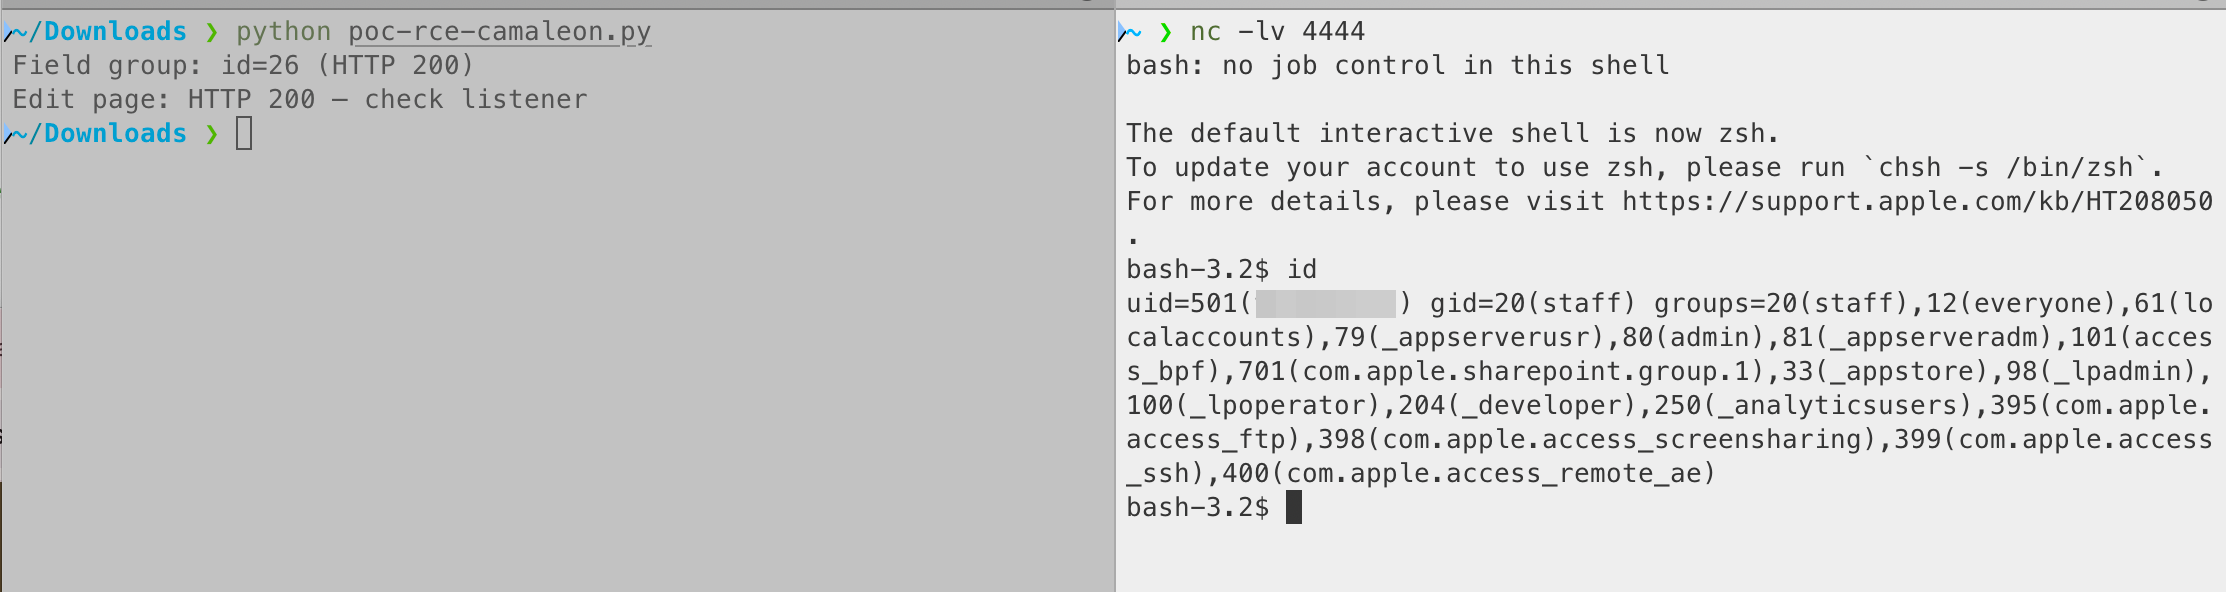 theopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 polosss/by-poloss..-..cve-2026-7515-poc
Unauthenticated Local File Inclusion
 muslimbek-0x/cve-2026-48030
Proof-of-concept exploit for CVE-2026-48030, a critical OS command injection in Pheditor 2.0.1-2.0.3. Includes vulnerable code analysis, PoC script,…
 kx00007/cve-2026-35196
Second CVE still Remote Code Execution
 hax3xploit/cve-2021-41645
Remote Code Execution (RCE) vulnerability exists in Sourcecodester Budget and Expense Tracker System 1.0 that allows a remote malicious user to…