

CVE-2025-24813
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
code-analysisexploitationpayload-generation+5
1
fatkz/cve-2025-24813Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 iamsanjay/cve-2022-42899
Proof-of-concept exploit for CVE-2022-42899, demonstrating remote code execution in Apache Commons Text 1.5-1.9 via StringSubstitutor interpolation…
 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 randomrobbiebf/cve-2024-9932
Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload
 ianxtianxt/cve-2019-11043
Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…
 crytic/slither
Static Analyzer for Solidity and Vyper
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
 ajdumanhug/cve-2023-46818
CVE-2023-46818 Python3 Exploit for ISPConfig <= 3.2.11 (language_edit.php) PHP Code Injection Vulnerability
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…

 0nion1/cve-2021-3129
CVE-2021-3129-Laravel Debug mode
 matesz44/cve-2025-64512
CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
 d0n601/cve-2025-12973
S2B AI Assistant – ChatBot, ChatGPT, OpenAI, Content & Image Generator <= 1.7.7 - Authenticated (Editor+) Arbitrary File Upload
 k3ystr0k3r/cve-2024-4577-exploit
A PoC exploit for CVE-2024-4577 - PHP CGI Argument Injection Remote Code Execution (RCE)
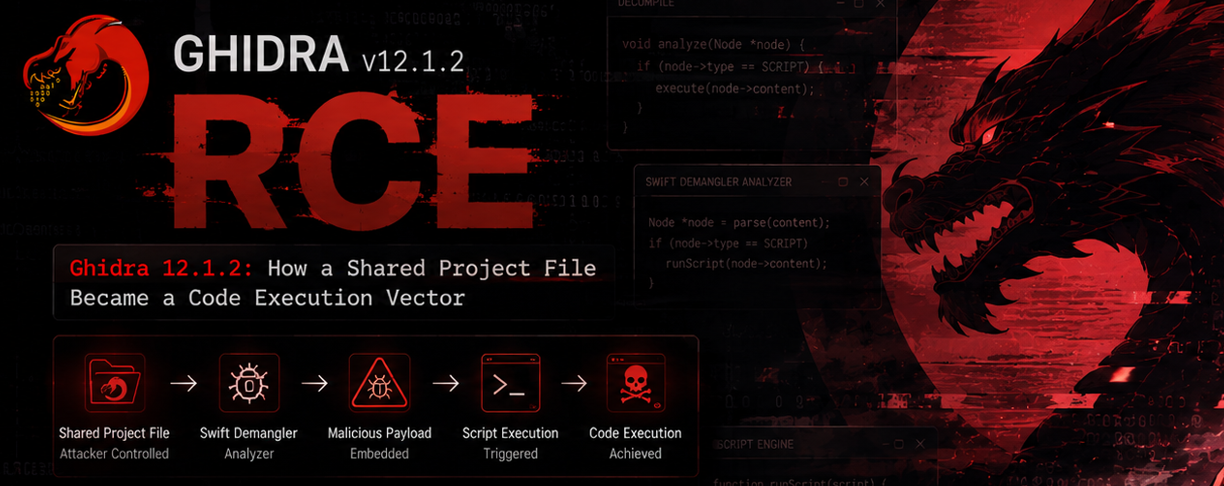 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector